
Android-Projector-C2-Malware
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
android-securitycommand-and-controldigital-forensics+9
23
kavan00/android-projector-c2-malwareBreakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 joshuaasmith/reproducer-okio-cve-2023-3635
Reproducer for CVE-2023-3635 in Okio 2.9.0, demonstrating how React Native's version catalog pins a vulnerable dependency, affecting Android apps.
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 saint0x/fzy
a systems programming language prioritizing verifiable correctness, determinism, and performance
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 psycho-prince/cve-2025-56513-nicehash-update-chain-compromise
Critical supply-chain vulnerability research on NiceHash QuickMiner update mechanism (CVE-2025-56513). Includes technical analysis, attack scenarios,…
 thomrgn/xzutils_backdoor_obfuscation
Script to obfuscate a payload the same way as it was done by the XZ utils attack (CVE-2024-3094)
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
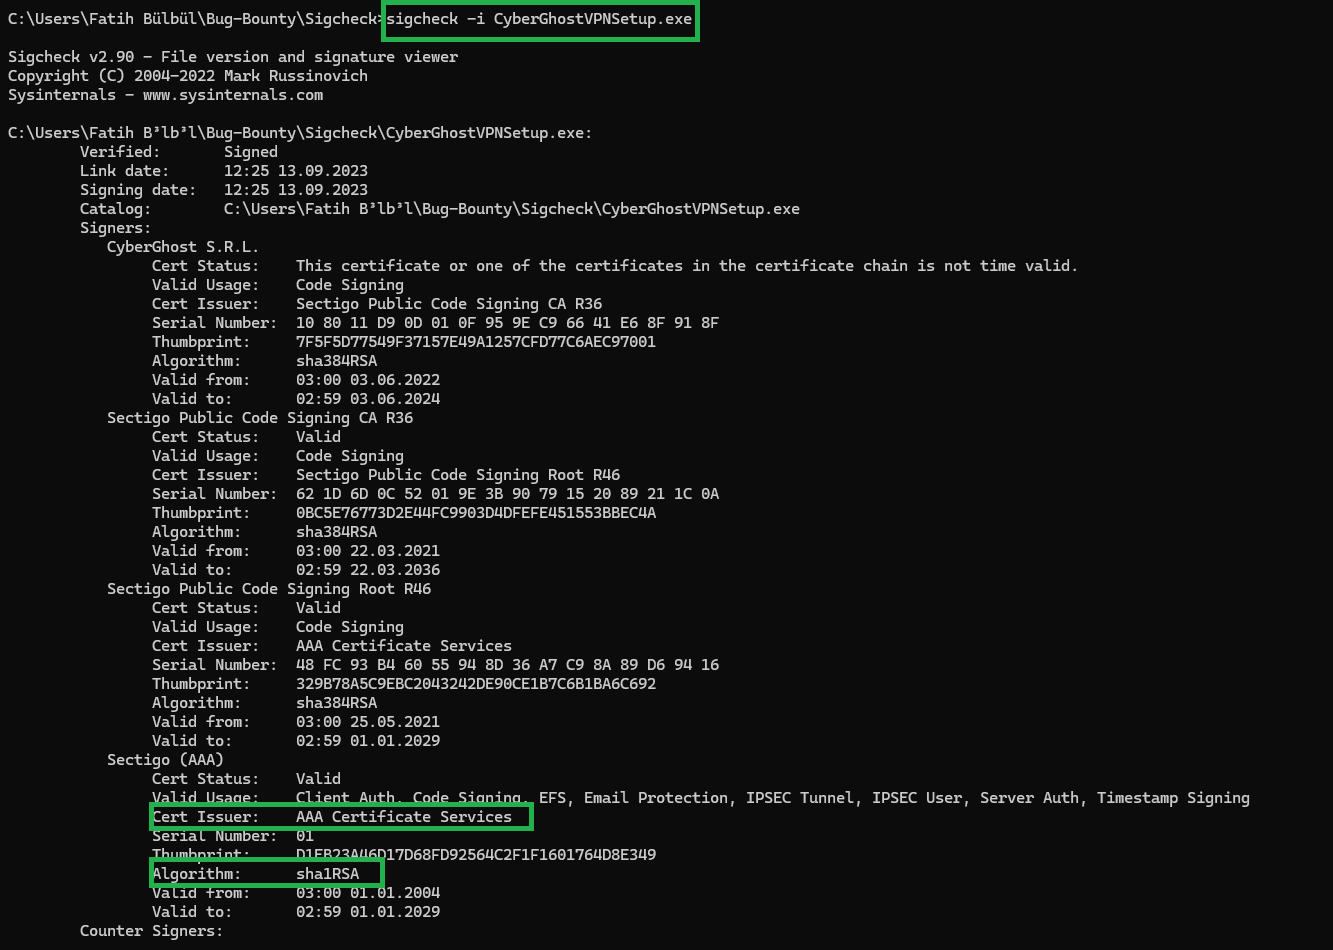 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability
 lucas-cauhe/cargo-perm
Cargo exploit from CVE-2023-38497