
kin
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
ai-securitycode-analysiscurated-resources+4
64
firelock-ai/kinSemantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 bkuan001/halo-record
Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
 8b-is/smart-tree
Smart Tree: not just a tree, a philosophy. A context-aware, AI-crafted replacement for 20+ tools with MEM8 quantum compression, semantic search,…
 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
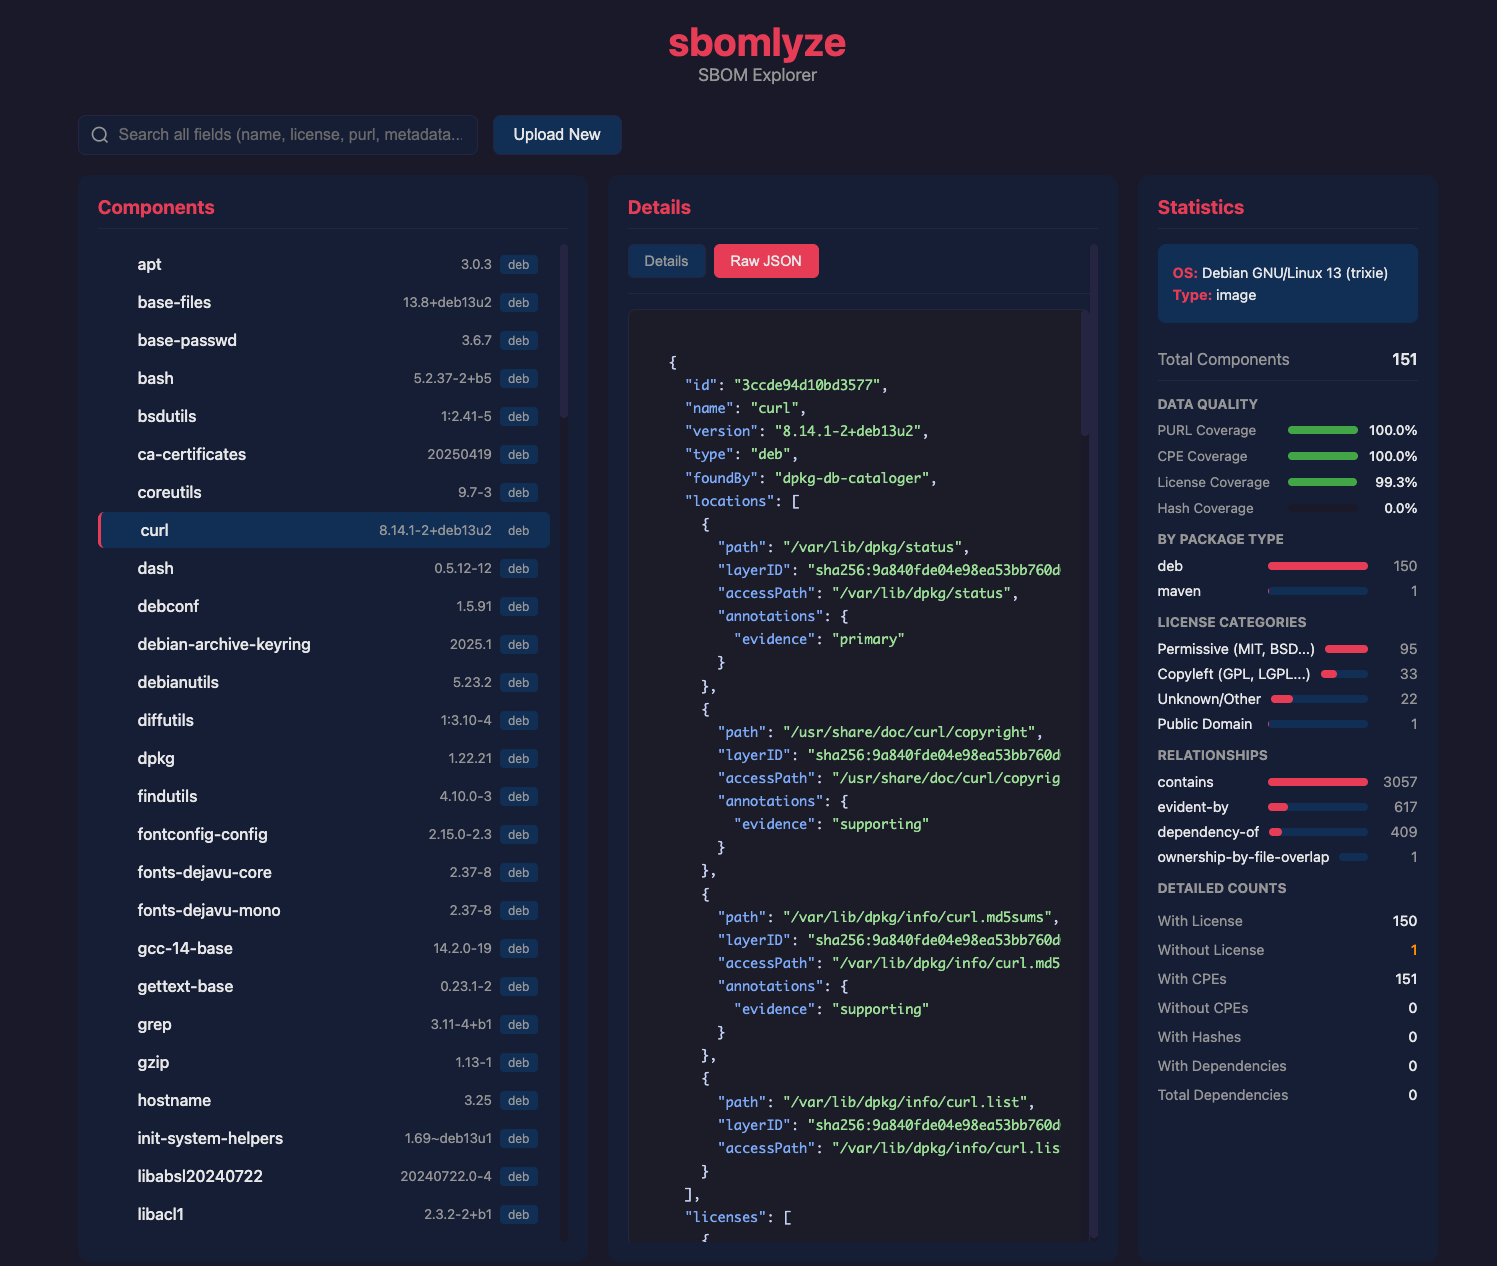 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
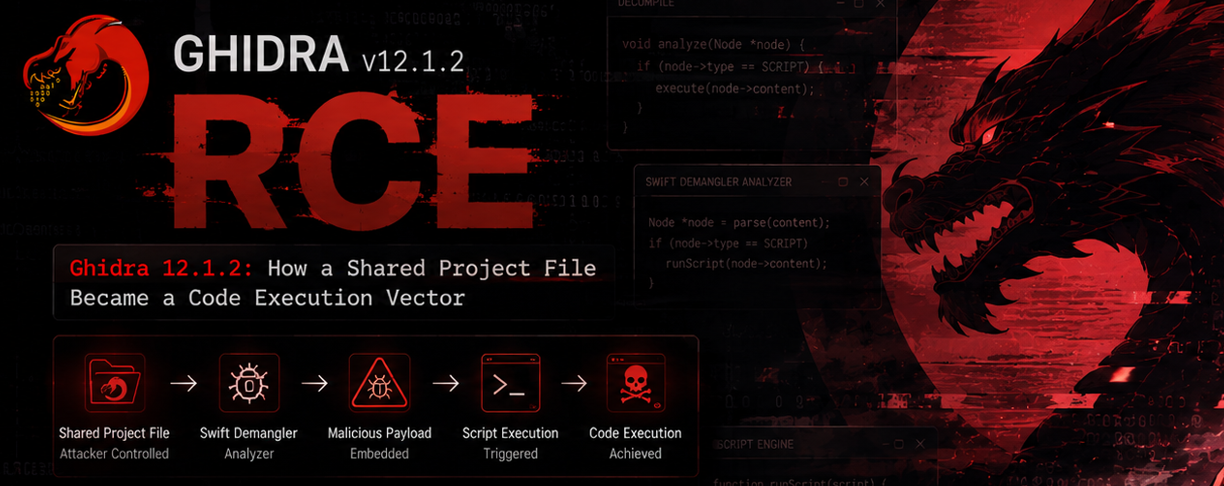 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 ridhinva/npm-tar-path-traversal-scanner
Scanner: CVE-2026-31802 npm tar path traversal — Python checker for arbitrary file write via npm pack
 x-cmd-build/xz
Portable binary distribution of xz-utils 5.8.3 with CVE-2024-3094 verification. Provides static builds for Linux, macOS, and Windows for compression…
 knqyf263/go-rpmdb
RPM DB bindings for go
 h3ck13r/cve-2026-35204
Proof-of-concept demonstrating a path traversal vulnerability (CVE-2026-35204) in Helm plugin installation, allowing arbitrary file write via crafted…
 chaitanyagarware/cve-2026-54520
Public advisory landing page documenting CVE-2026-54520, a high-severity path traversal vulnerability in ai-agent-automation's workflow executor,…
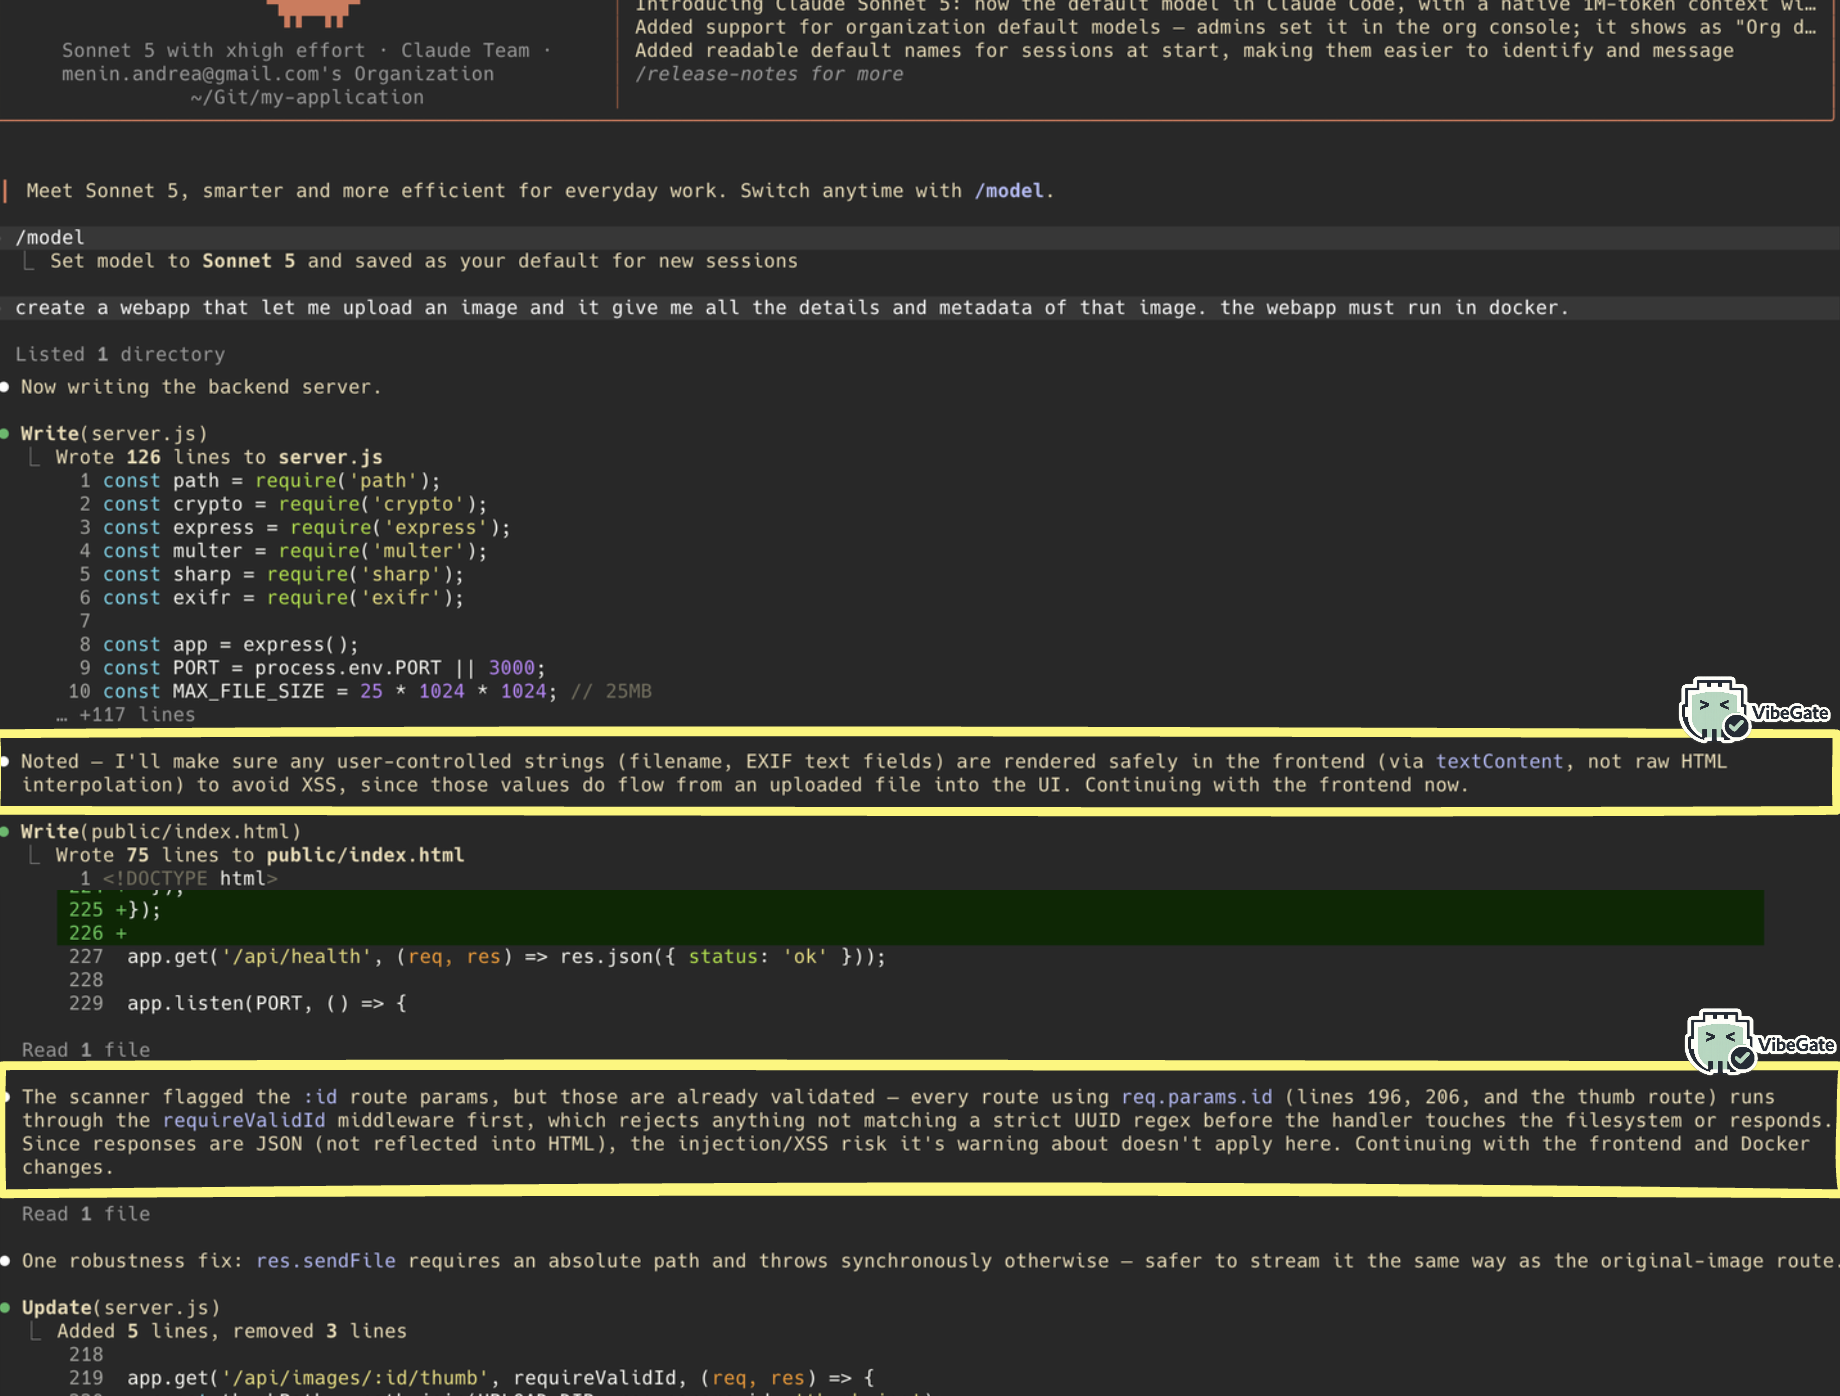 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…