
ai-ctf
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
ai-securityctfeducation+6
708 days ago
mubix/ai-ctfLocal AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 mubix/find-wsus
Helps defenders find their WSUS configurations in the wake of CVE-2025-59287
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
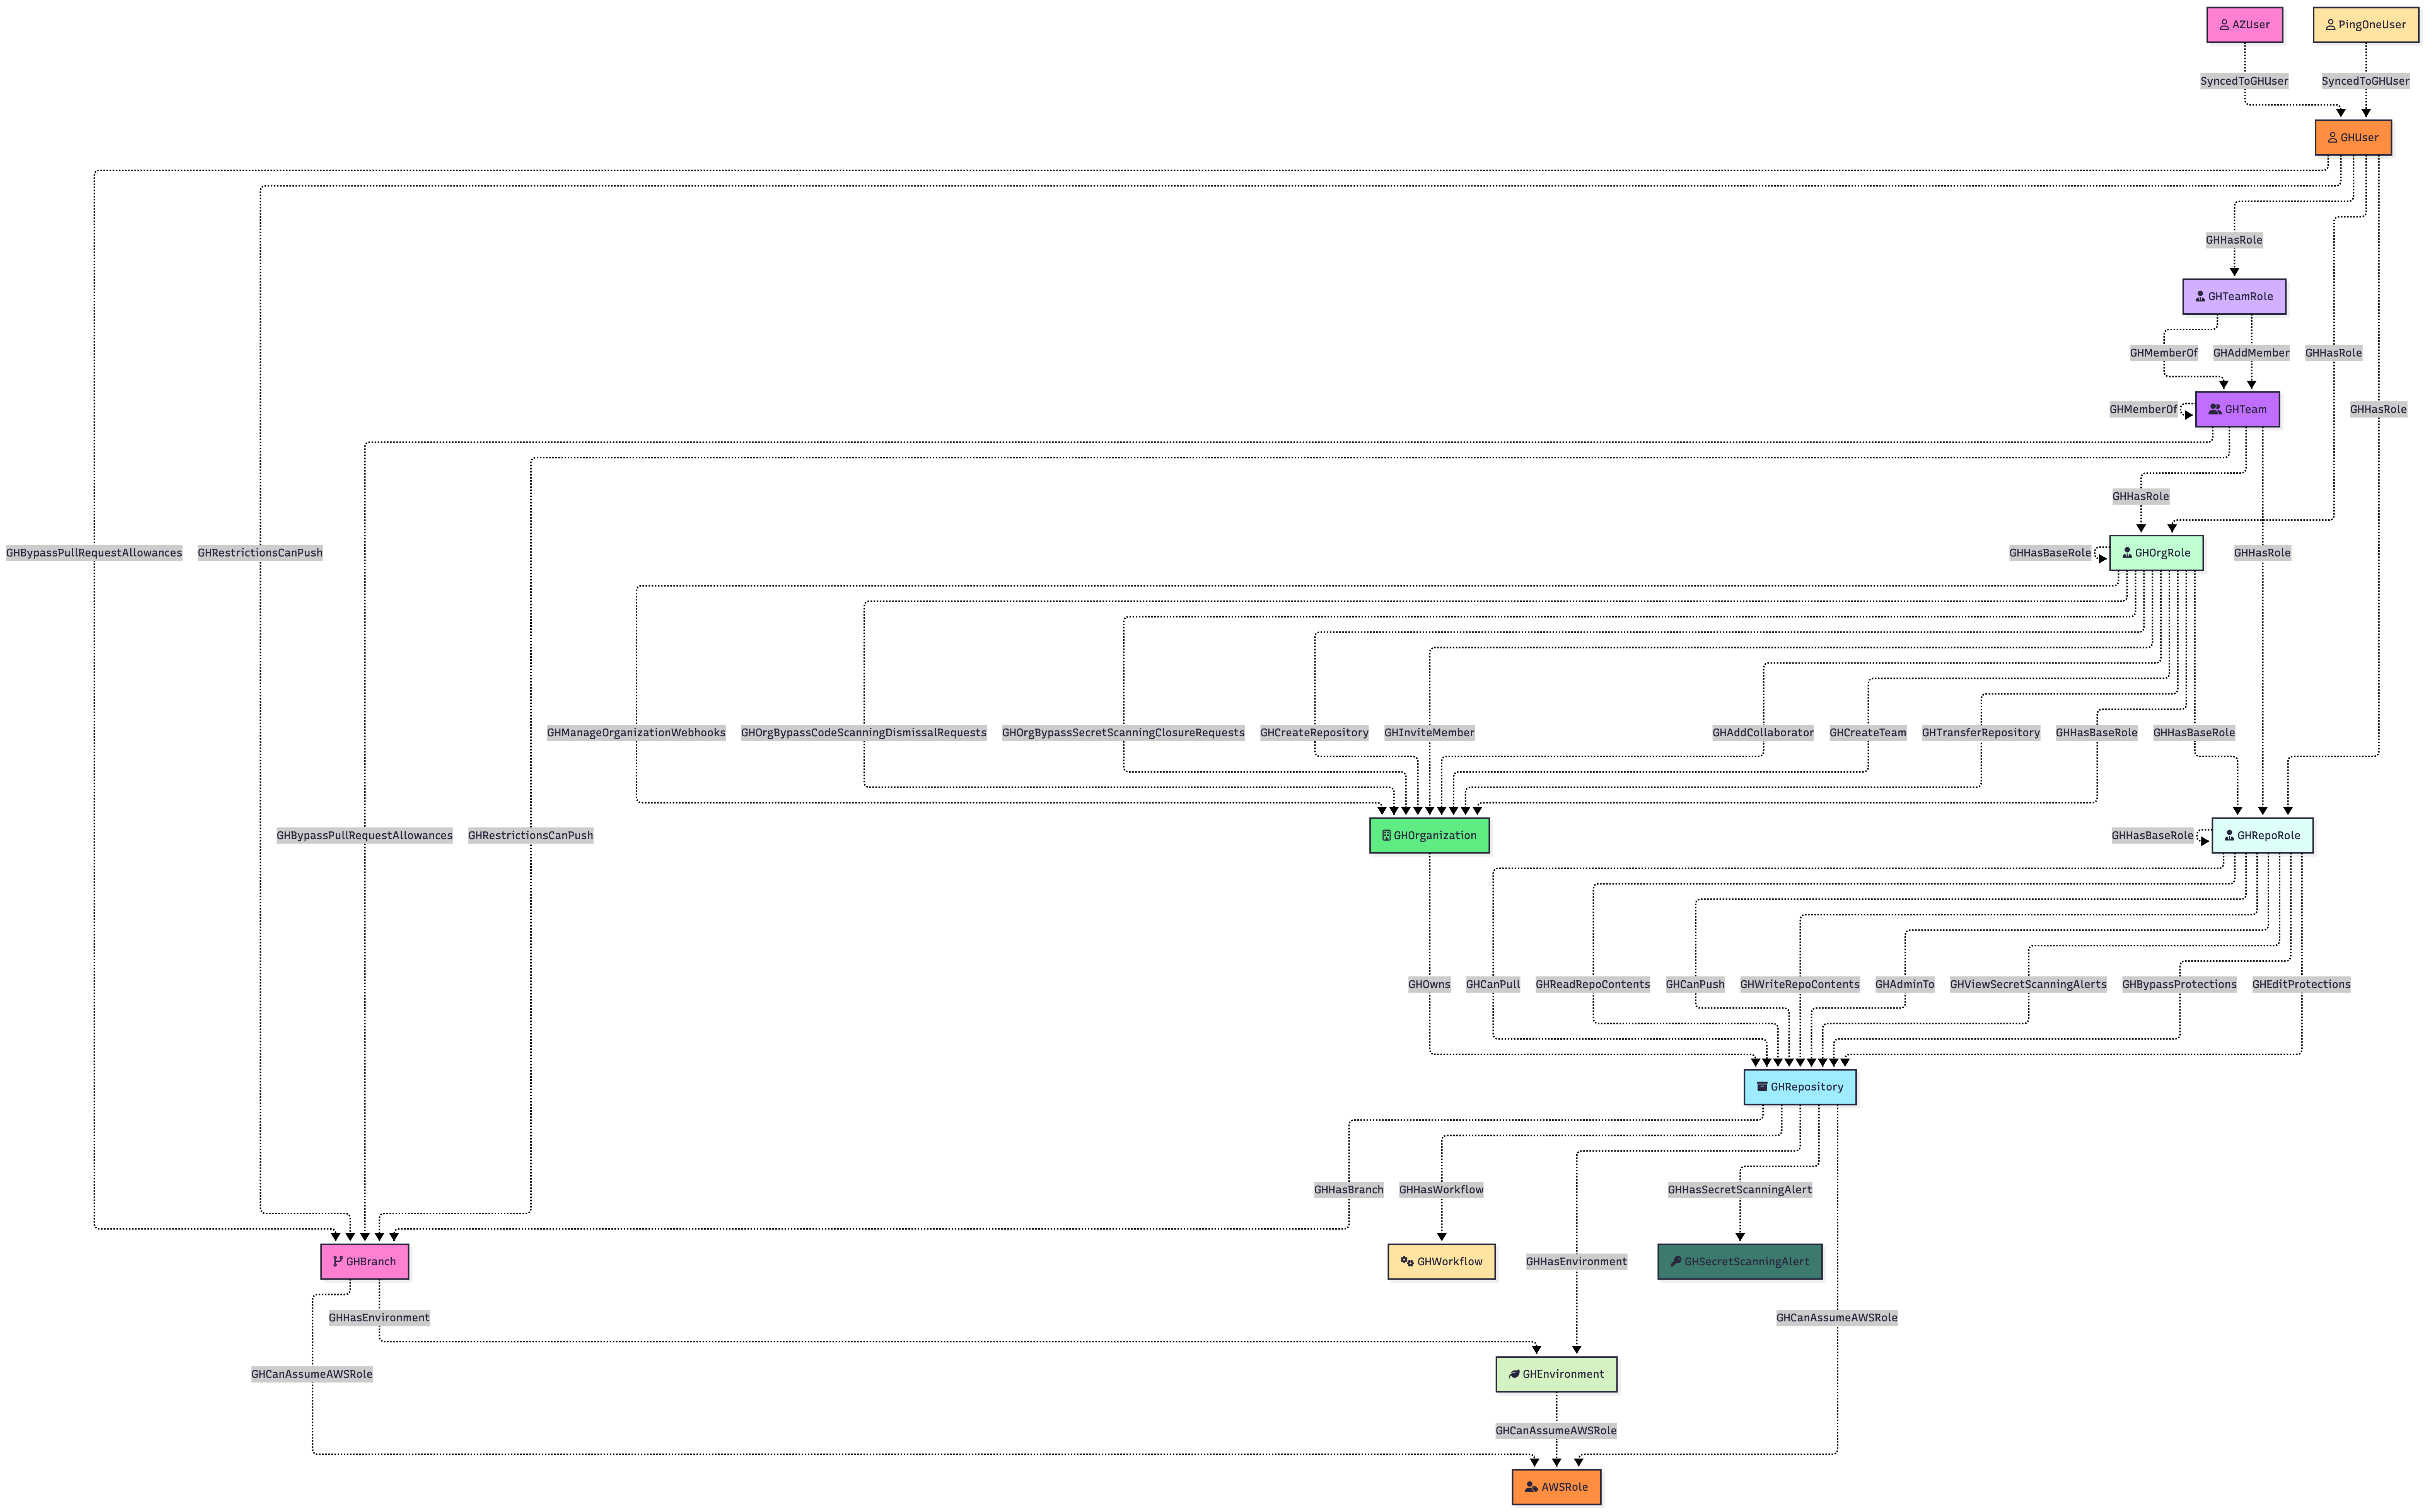 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
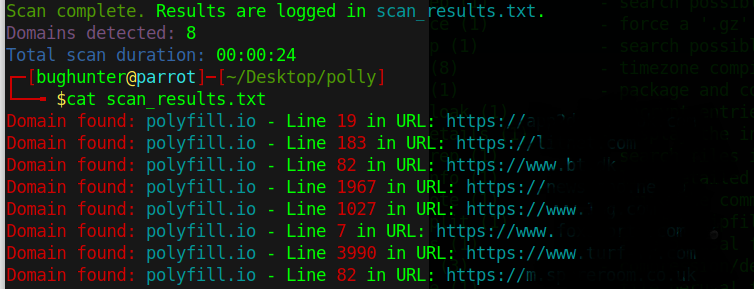 putget/cve-2024-38526
CVE-2024-38526 - Polyfill Scanner
 codesecurityteam/harbor
CVE-2022-46463 harbor公开镜像全自动下载脚本
 nurjaman2004/jspdf-bulk-detector-cve-2025-68428-
Asset-wide detection tool for identifying jsPDF usage related to CVE-2025-68428 Detection only — no exploitation
 perryflynn/find-log4j
Find log4j for CVE-2021-44228 on some places * Log4Shell
 mightysai1997/cve-2024-3094-info
Curated collection of resources and analysis documenting the CVE-2024-3094 supply-chain backdoor in XZ Utils, including security advisories,…