
log4j
 open-aims/log4j
Patched Log4j 1.2.17 library with the vulnerable JMSAppender class removed to mitigate CVE-2021-4104, intended as a drop-in replacement for affected…
devsecopssupply-chain-securityvulnerability-analysis
open-aims/log4jPatched Log4j 1.2.17 library with the vulnerable JMSAppender class removed to mitigate CVE-2021-4104, intended as a drop-in replacement for affected…
 scitotec/log4j-recognizer
A Java helper to identify log4j in the current classpath
 logpresso/cve-2021-44228-scanner
Vulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 municipalparkingservices/cve-2021-44228-scanner
Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…
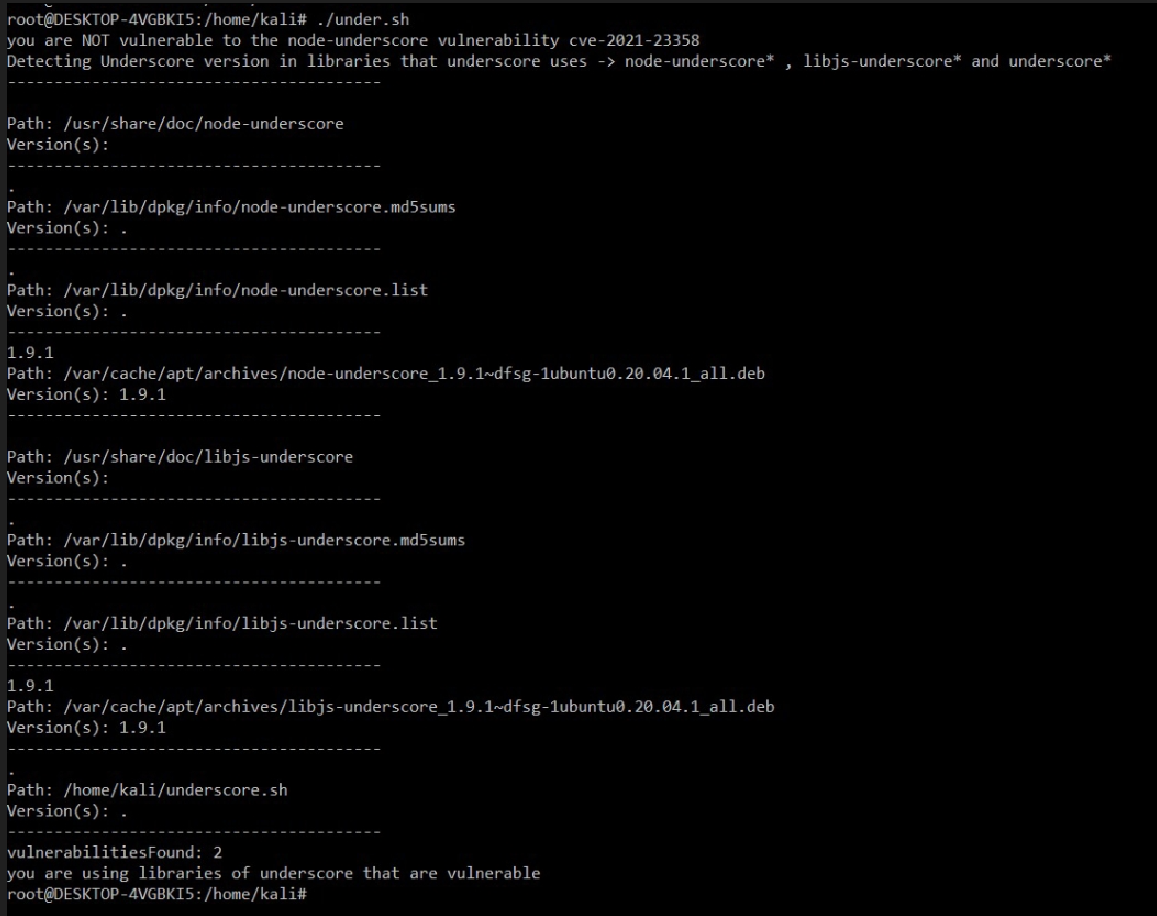 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 oopsiewoopsie/mc-log4j-patcher
CVE-2021-44228 server-side fix for minecraft servers.
 winnpixie/log4noshell
A Java Agent that disables Apache Log4J's JNDI Lookup to mitigate CVE-2021-44228 ("Log4Shell").
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 name/log4j-scanner
Discover Log4Shell vulnerability [CVE-2021-44832]
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]
 nccgroup/log4j-jndi-be-gone
A Byte Buddy Java agent-based fix for CVE-2021-44228, the log4j 2.x "JNDI LDAP" vulnerability.
 perryflynn/find-log4j
Find log4j for CVE-2021-44228 on some places * Log4Shell
 yamory/cve-2021-32804
Docker-based reproduction environment for CVE-2021-32804, a path traversal vulnerability in node-tar affecting npm, with step-by-step exploitation…
 izzyacademy/log4shell-mitigation
Mitigation for Log4Shell Security Vulnerability CVE-2021-44228
 icatalina/cve-2021-43616
Demonstration of CVE-2021-43616: npm `ci` command ignoring package-lock.json, causing unintended dependency version installation and supply-chain…