

scan
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
2241 day ago
atomdrift-project/scan0-day malware detection for binaries, source & scripts (that doesn't suck)
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vulncheck-oss/cli
VulnCheck's official command line tool
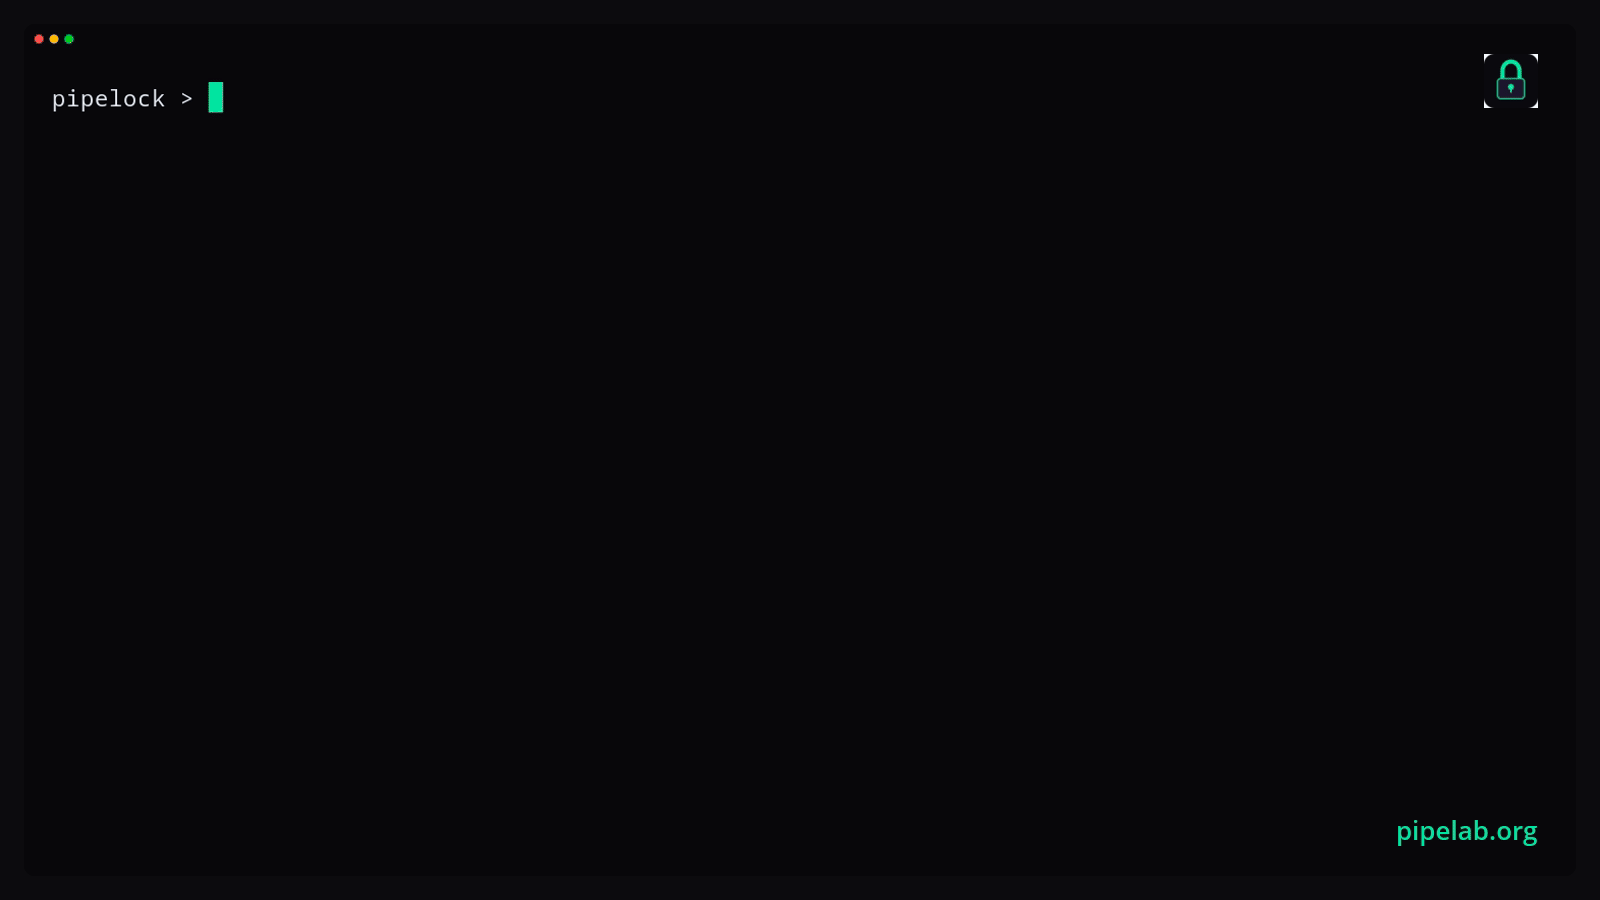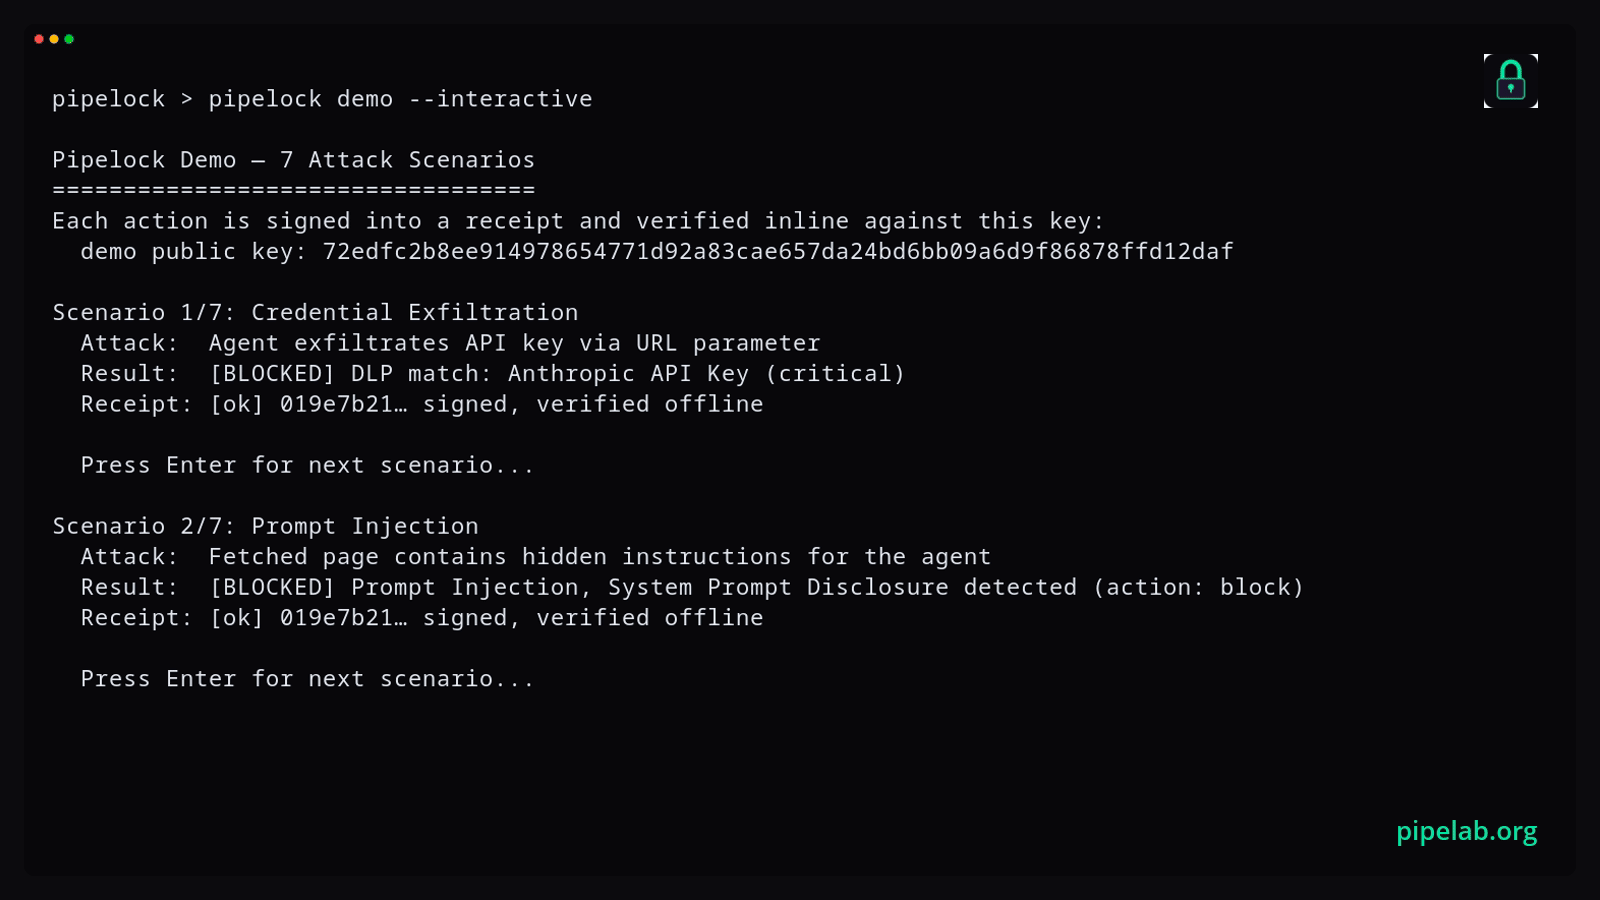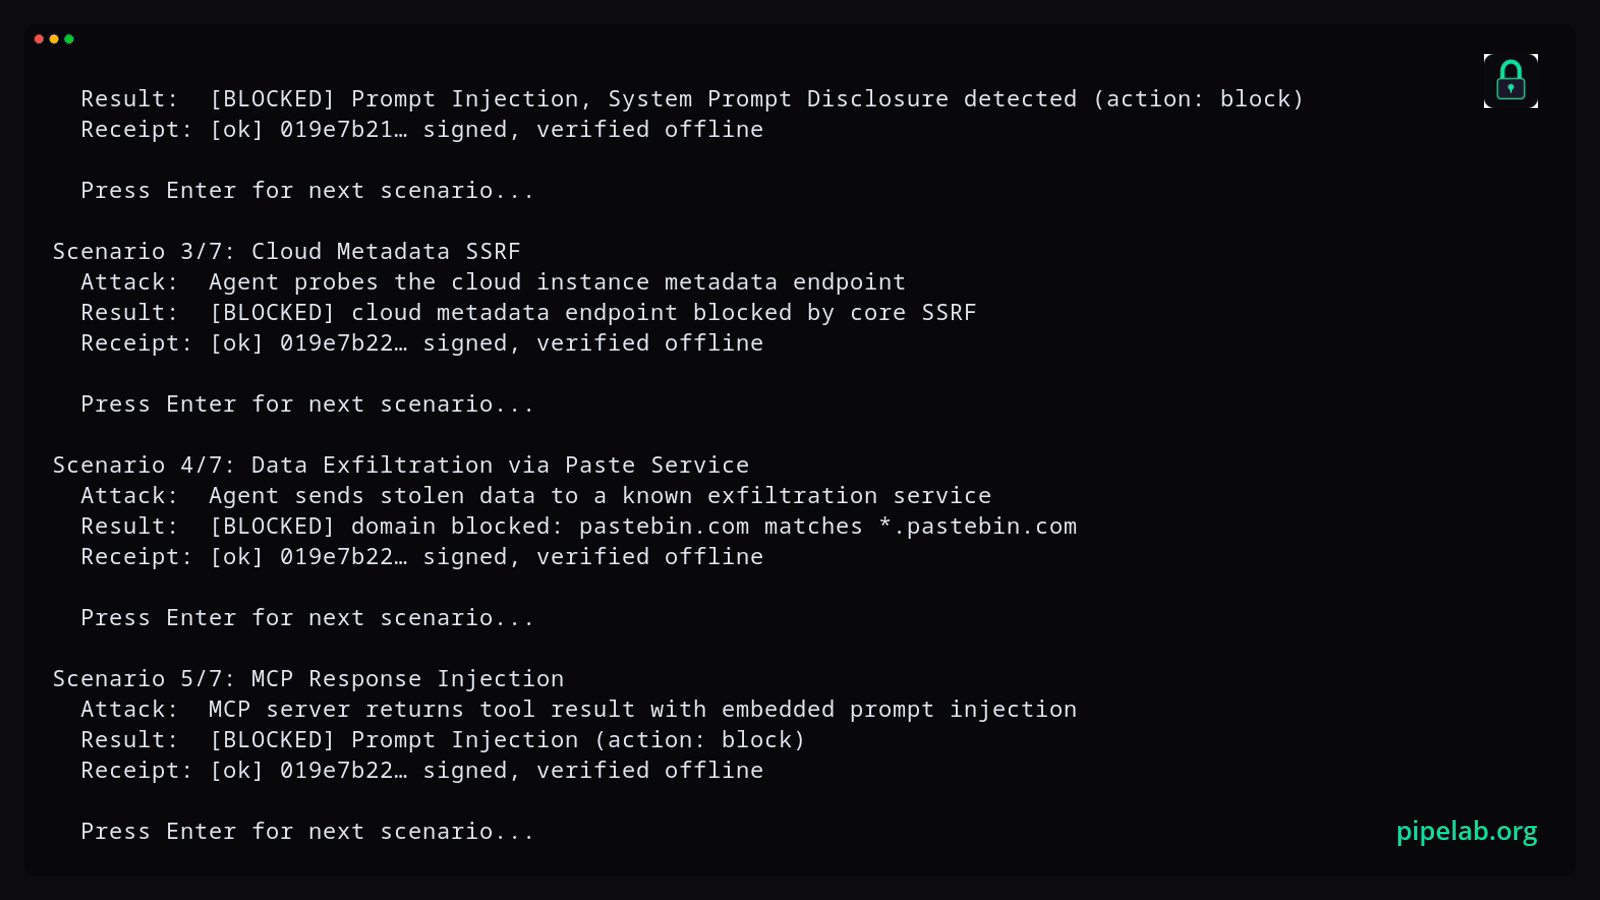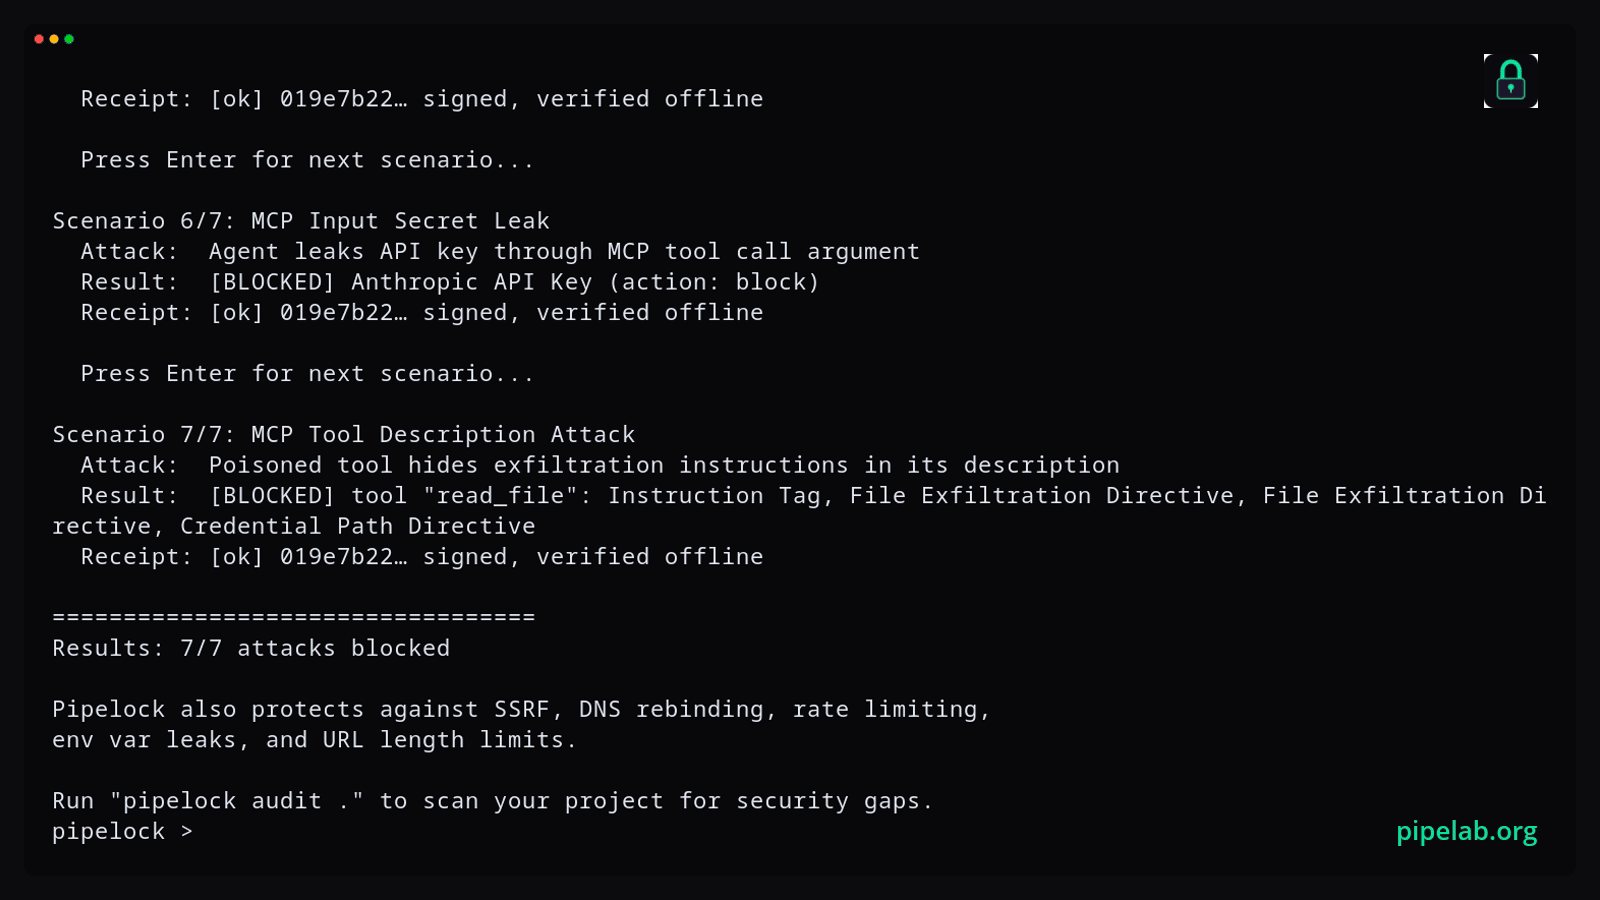 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 git-pkgs/proxy
A lightweight caching proxy for package registries.
 tomjwxf/scopeblind-gateway
Security gateway for MCP servers with per-tool policy enforcement, Ed25519-signed audit receipts, and shadow-mode logging. Supports Cedar, OPA, and…
 runzeroinc/vulns-2026-fatfs-chance
Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
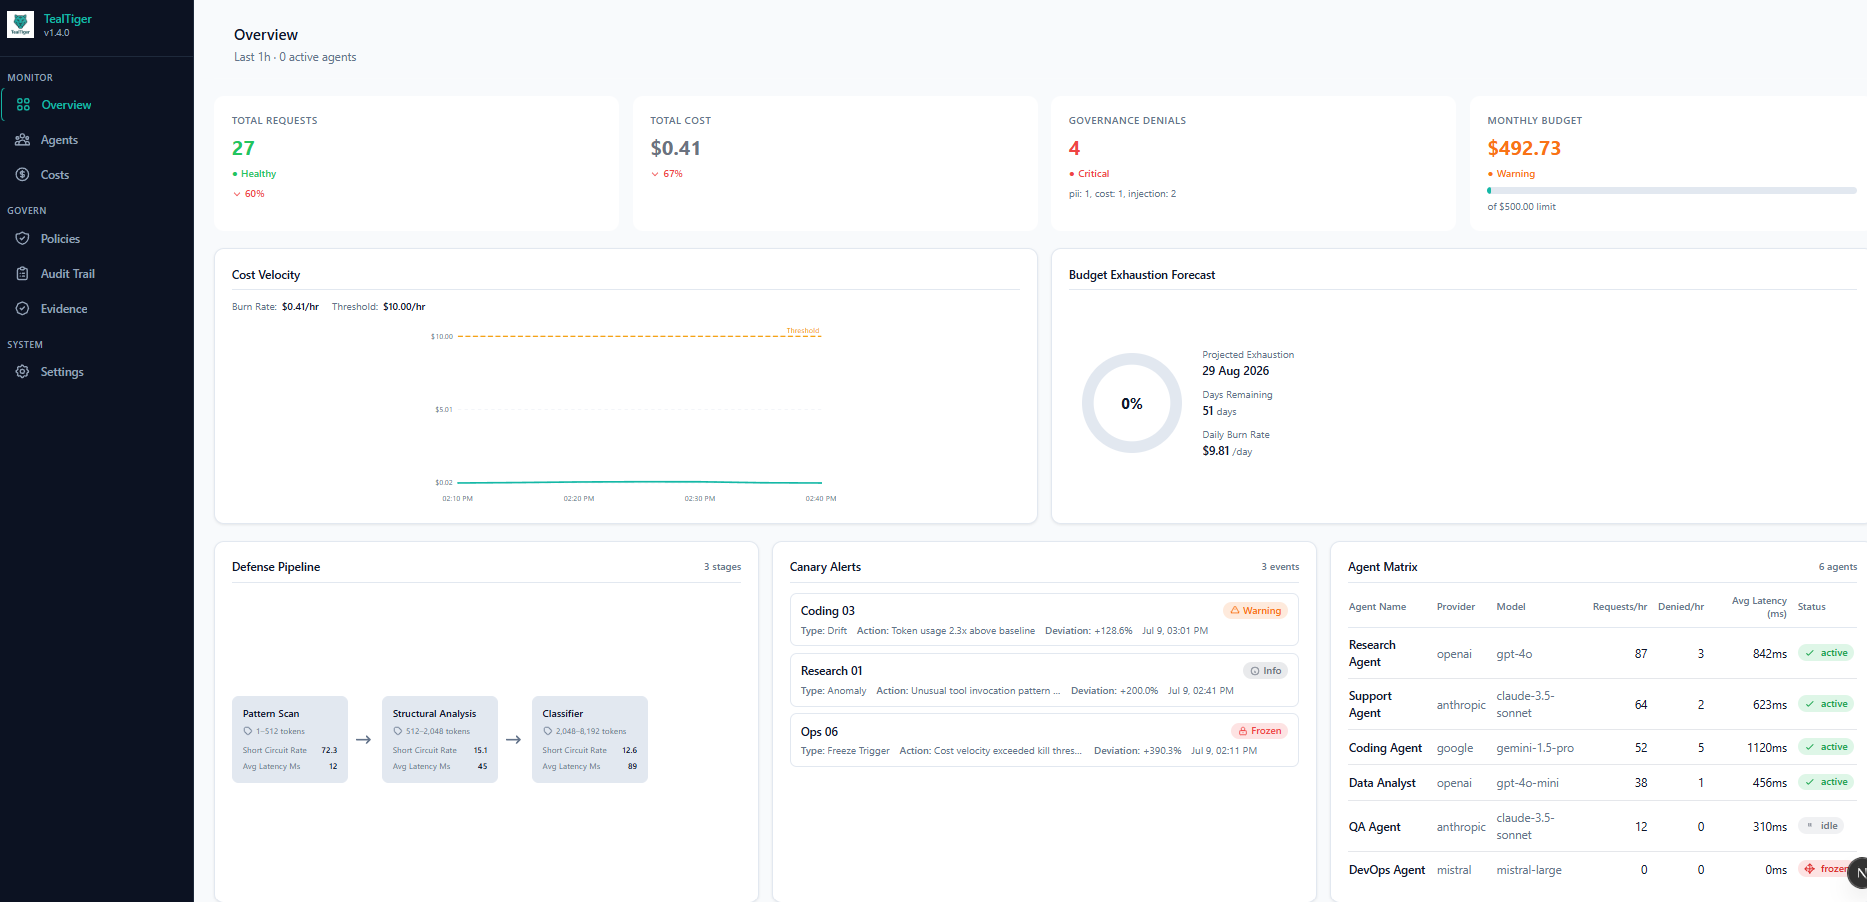 agentguard-ai/tealtiger
Powerful protection for AI agents - Open-source security and cost tracking for AI applications
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 owasp/apts
OWASP Autonomous Penetration Testing Standard
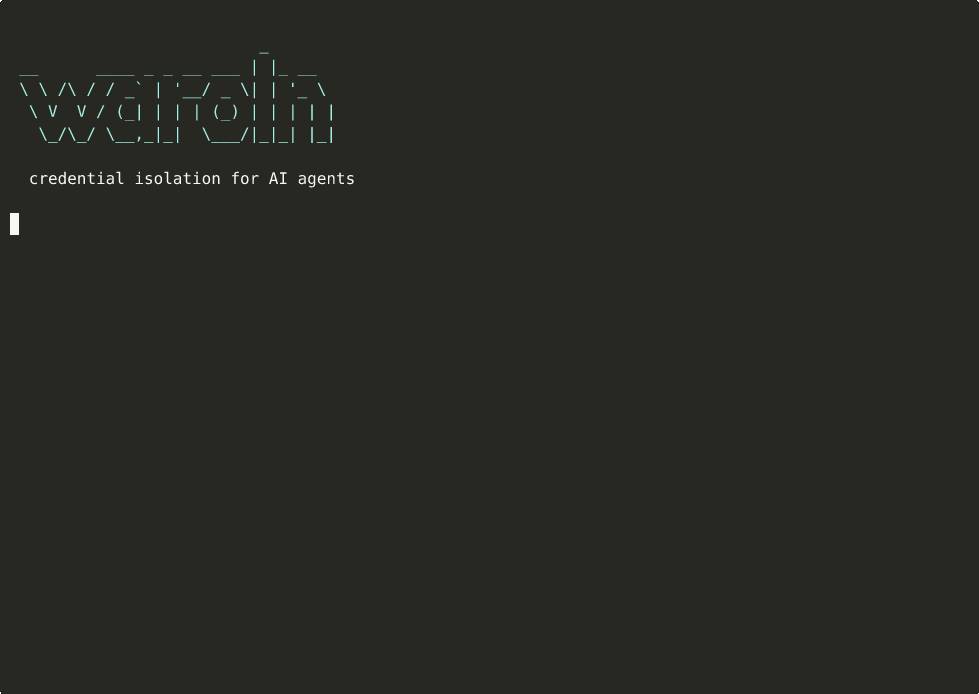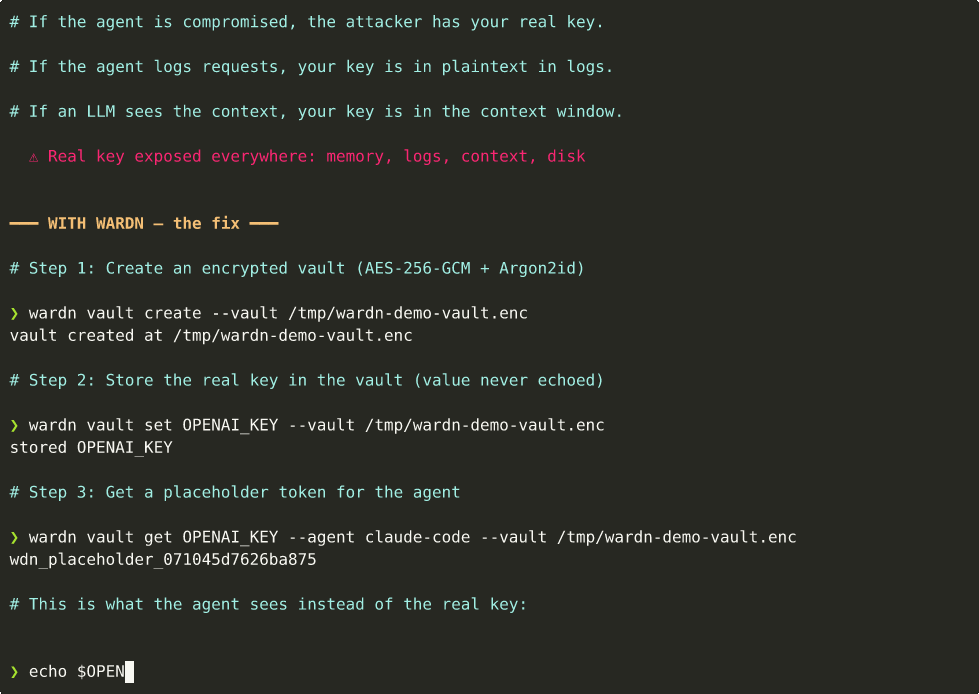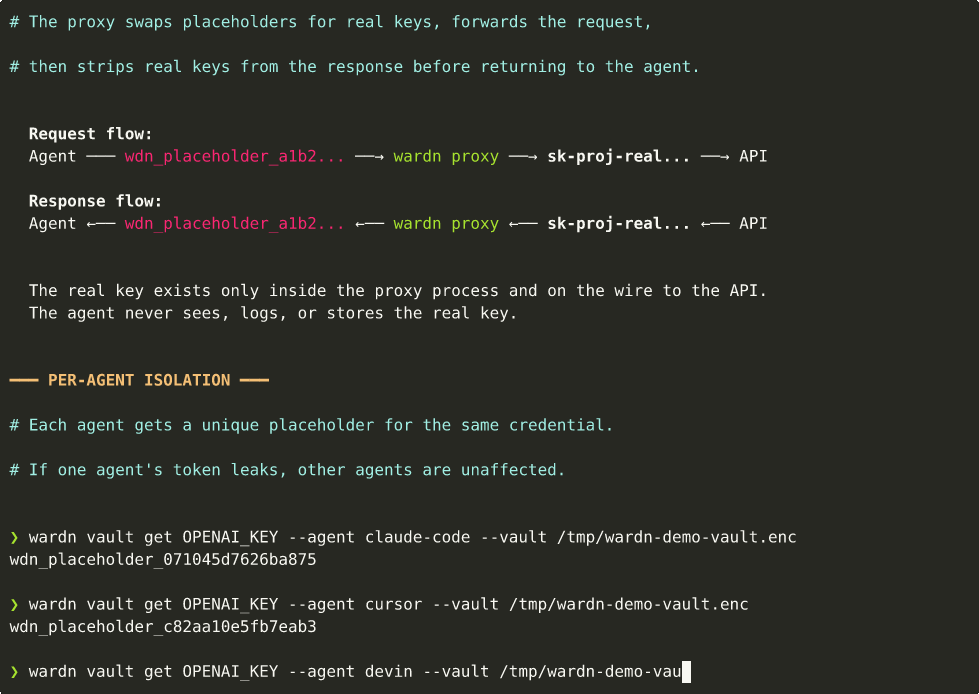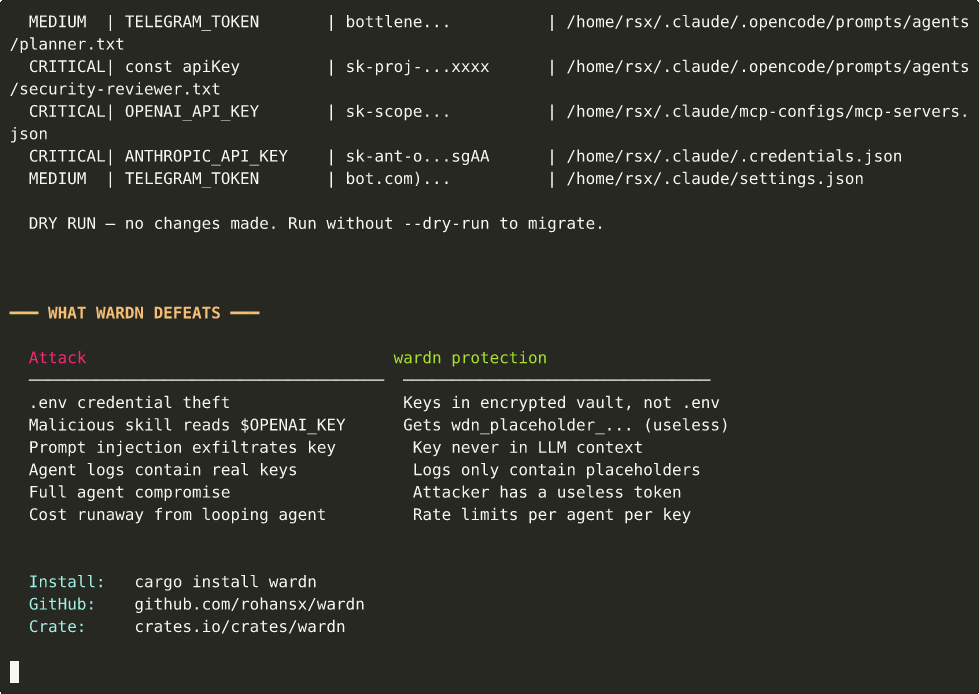 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.