
cli
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
cloud-infrastructure-securitycode-analysiscontainer-security+6
5.7k
snyk/cliSnyk CLI scans and monitors your projects for security vulnerabilities.
 mmiszczyk/cve-2021-33879
GameLoop update MITM
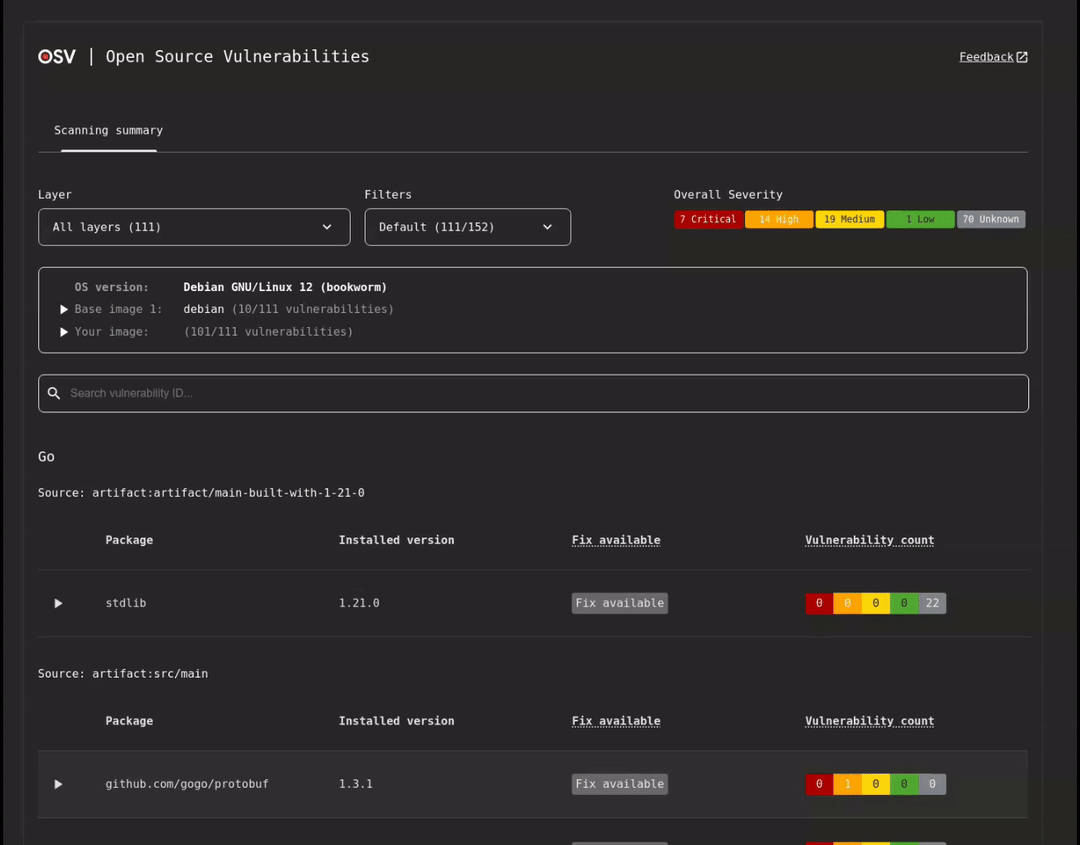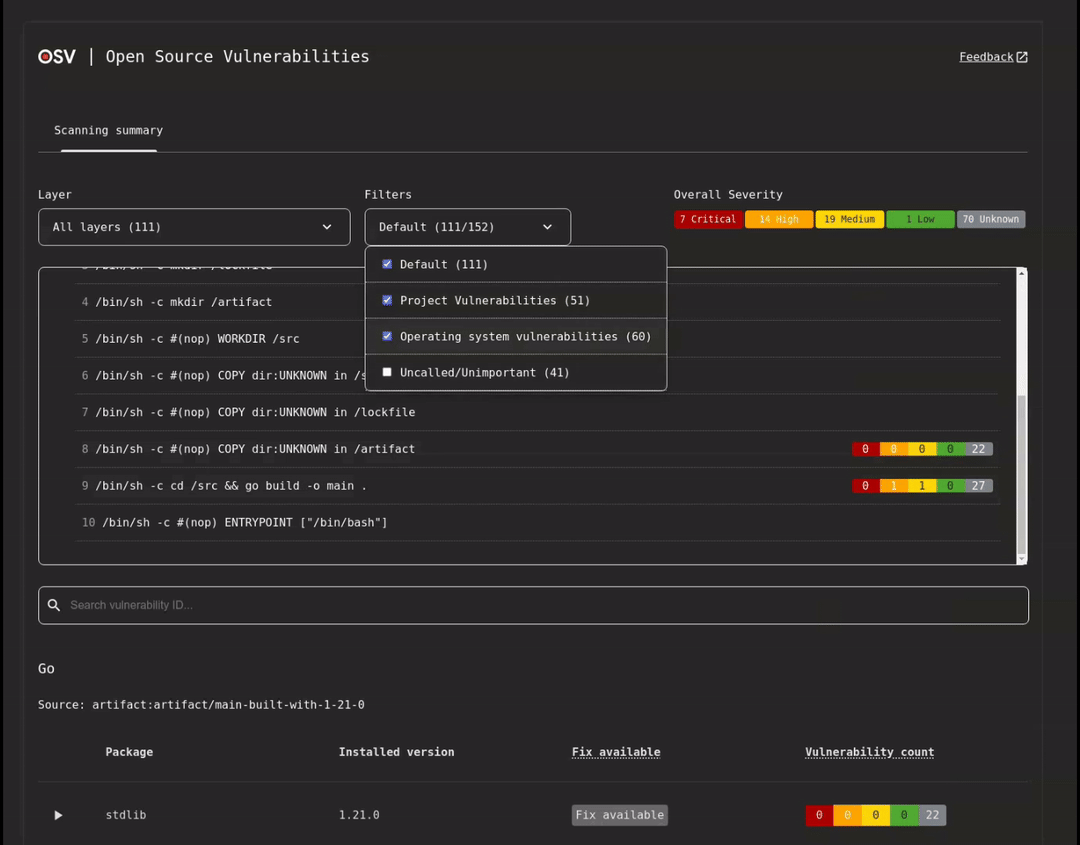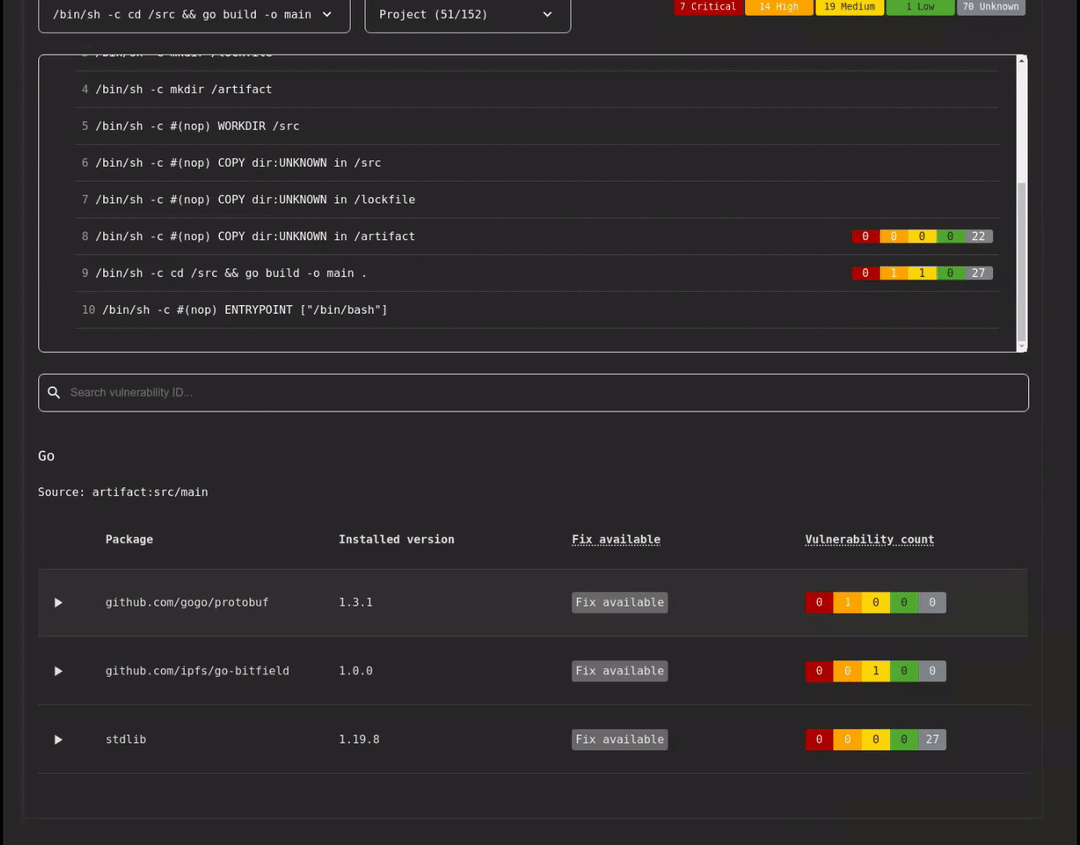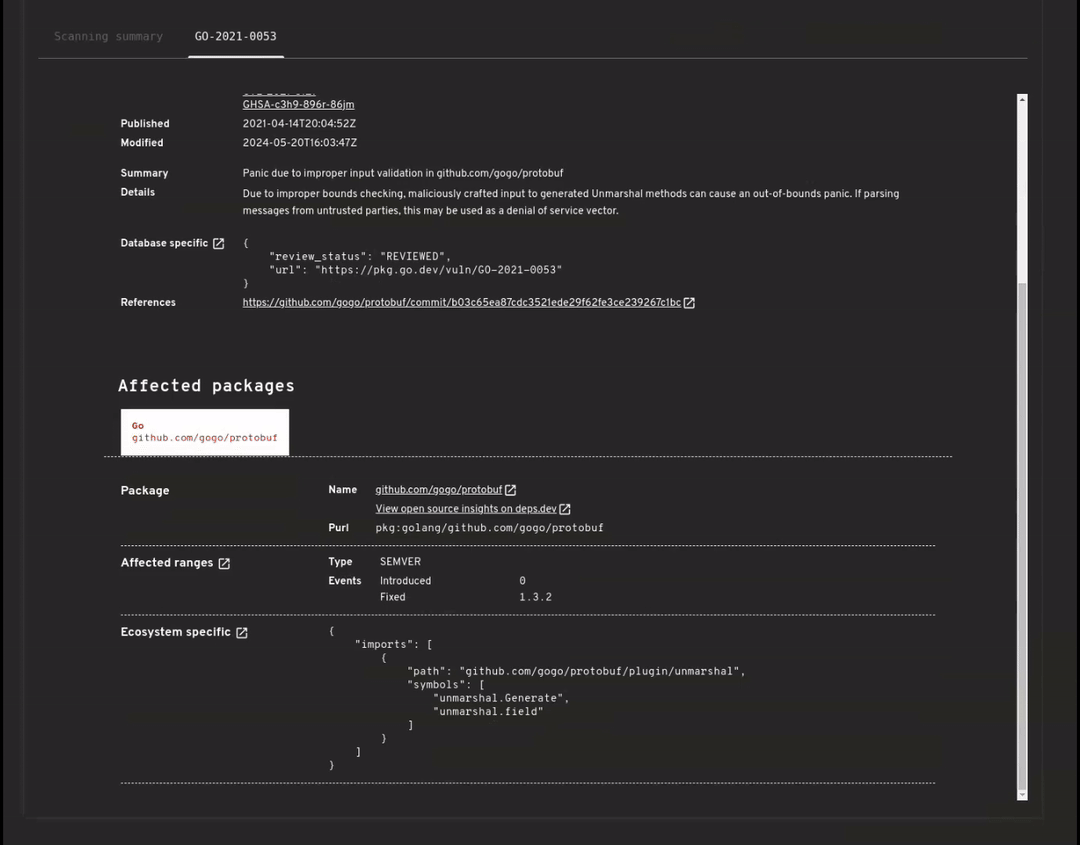 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 vinnimarcon/log4j-updater
Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
 cosai-oasis/ws4-secure-design-agentic-systems
Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
 bkuan001/halo-record
Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 owasp/owasp-top-10-ai-infrastructure-security-risks
A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…
 danielruf/snyk-js-jquery-174006
patches for SNYK-JS-JQUERY-174006, CVE-2019-11358, CVE-2019-5428
 aaravmaloo/revera
The credit score for npm packages. Analyze package reputation, maintenance, security, publisher trust, and ecosystem health before you install any…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
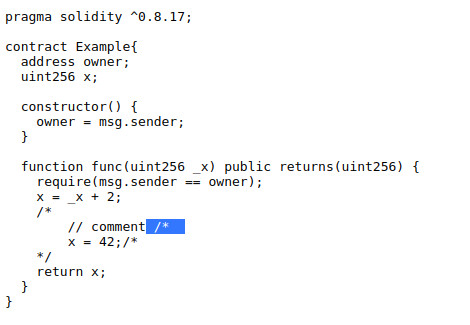 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler