dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…

Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…

A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

Source code for the Binaries of OWASP WrongSecrets

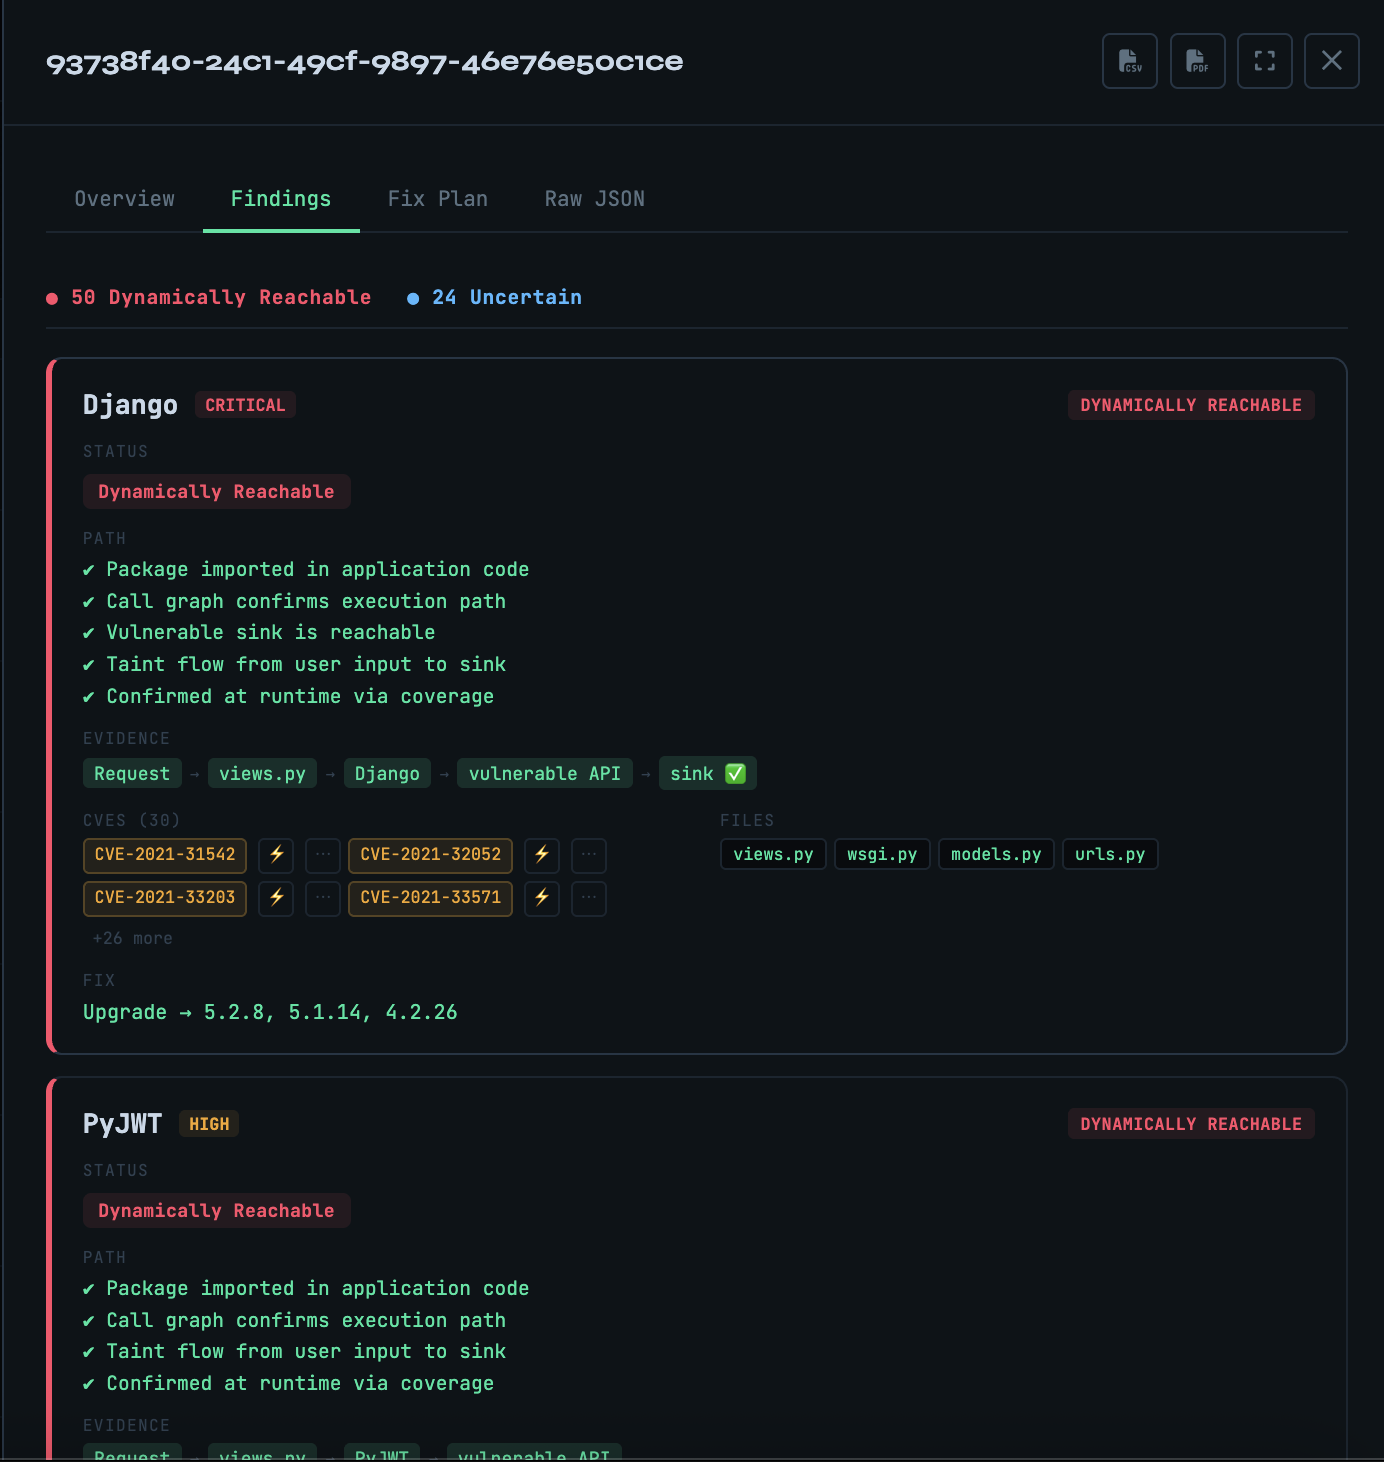
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.

Software Component Verification Standard (SCVS)

DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.

CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

A collection of awesome resources related AI security

OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.

Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…

The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists