

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.3k21h 19m ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 vulncheck-oss/cli
VulnCheck's official command line tool
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
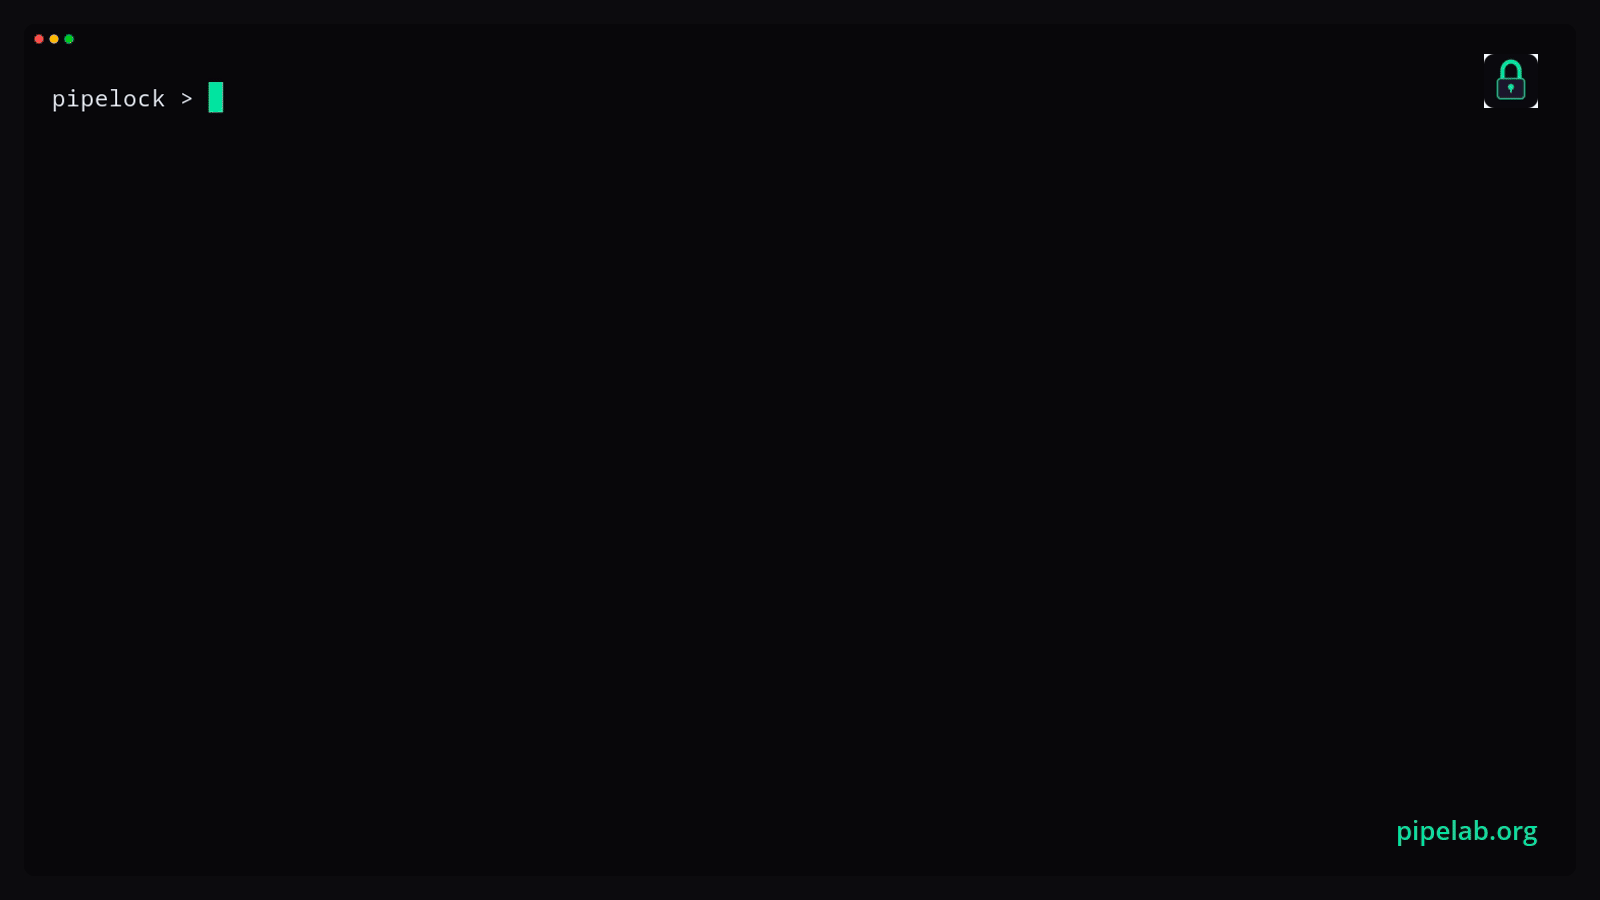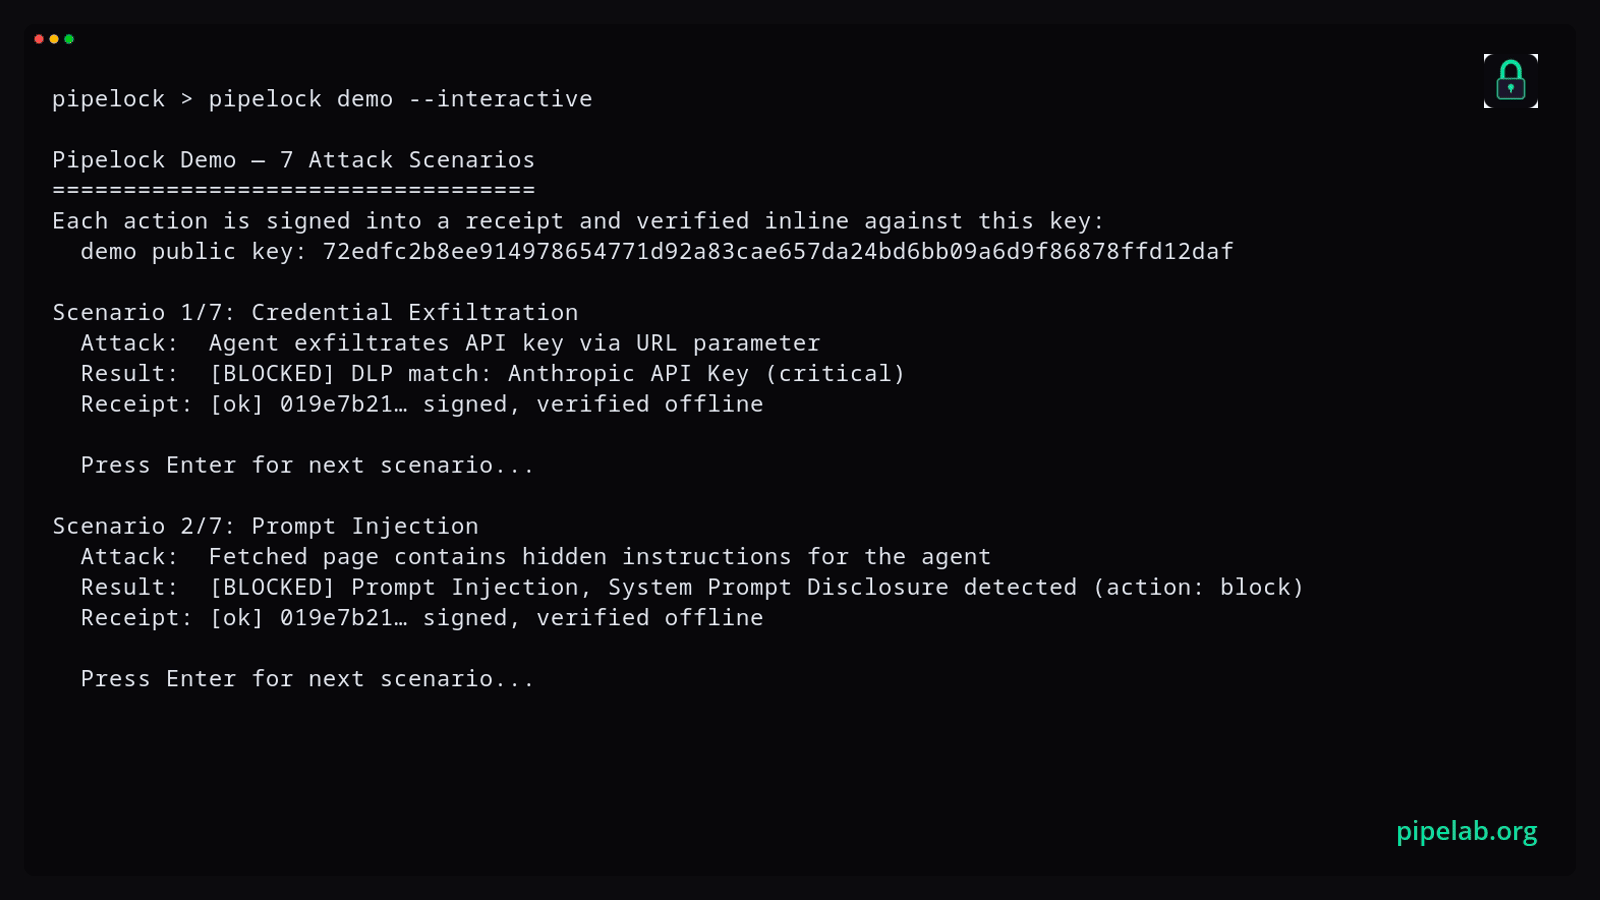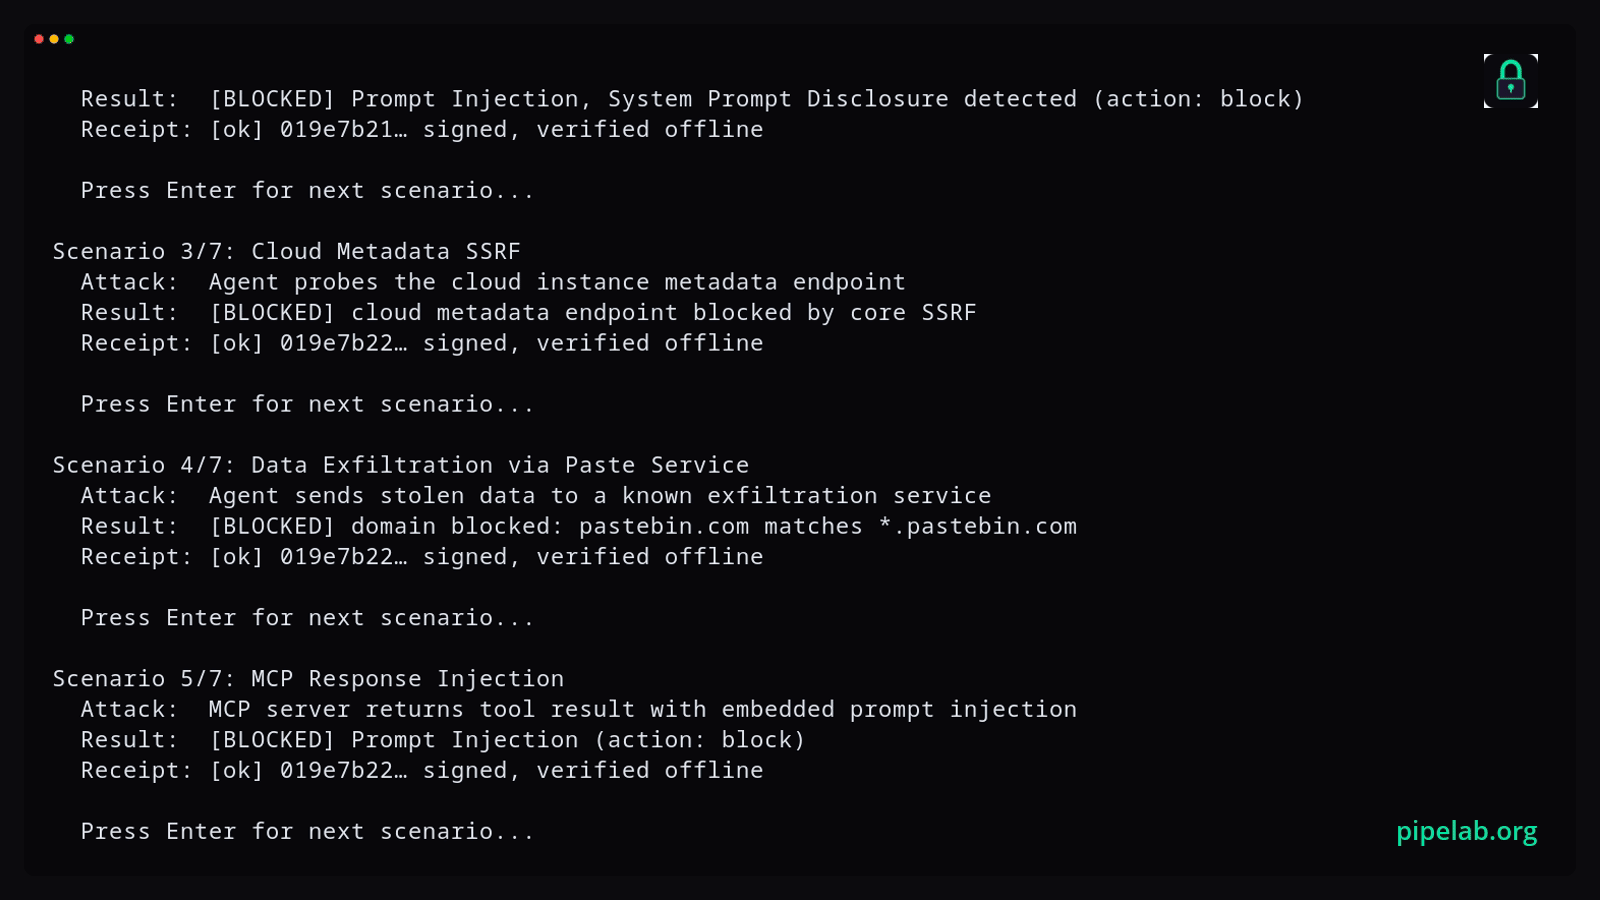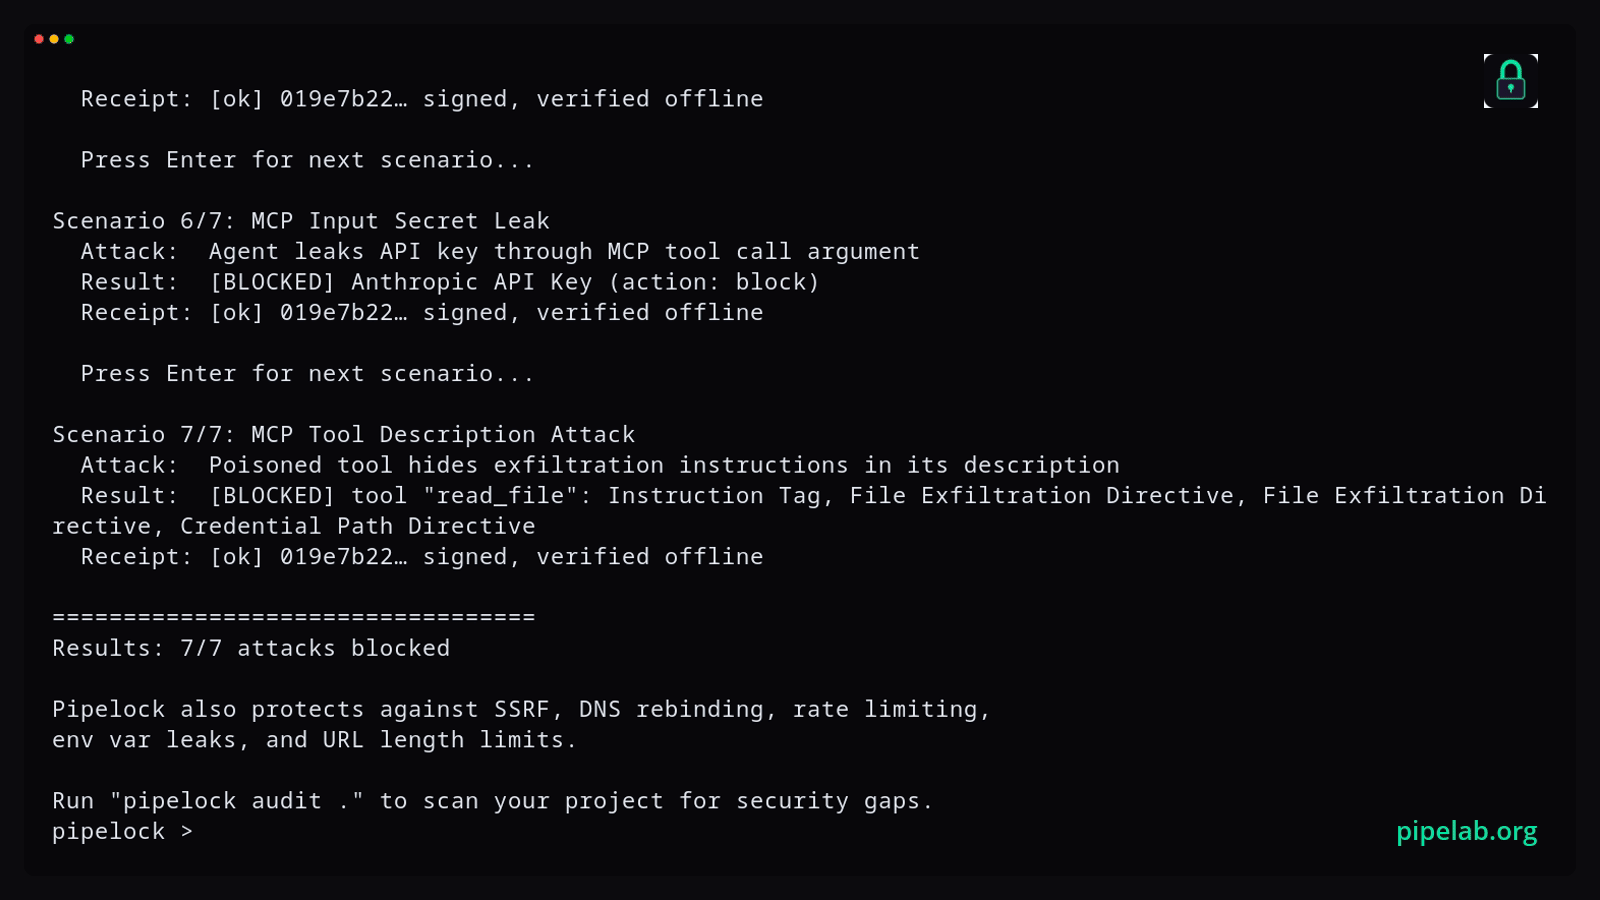 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…