
halo-record
 bkuan001/halo-record
Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
ai-securityforensicsincident-response+1
80
bkuan001/halo-recordTamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 harekrishnarai/xz-utils-vuln-checker
Checker for CVE-2024-3094 where malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. Through a series of…
 davidholiday/cve-2007-4559
Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
 agwa/git-crypt
Transparent file encryption in git
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
 sionnx/cve-2003-0282
Portable zipfile extraction utility with broad OS support, decryption, and security fixes for path traversal and symlink vulnerabilities.
 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector

 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
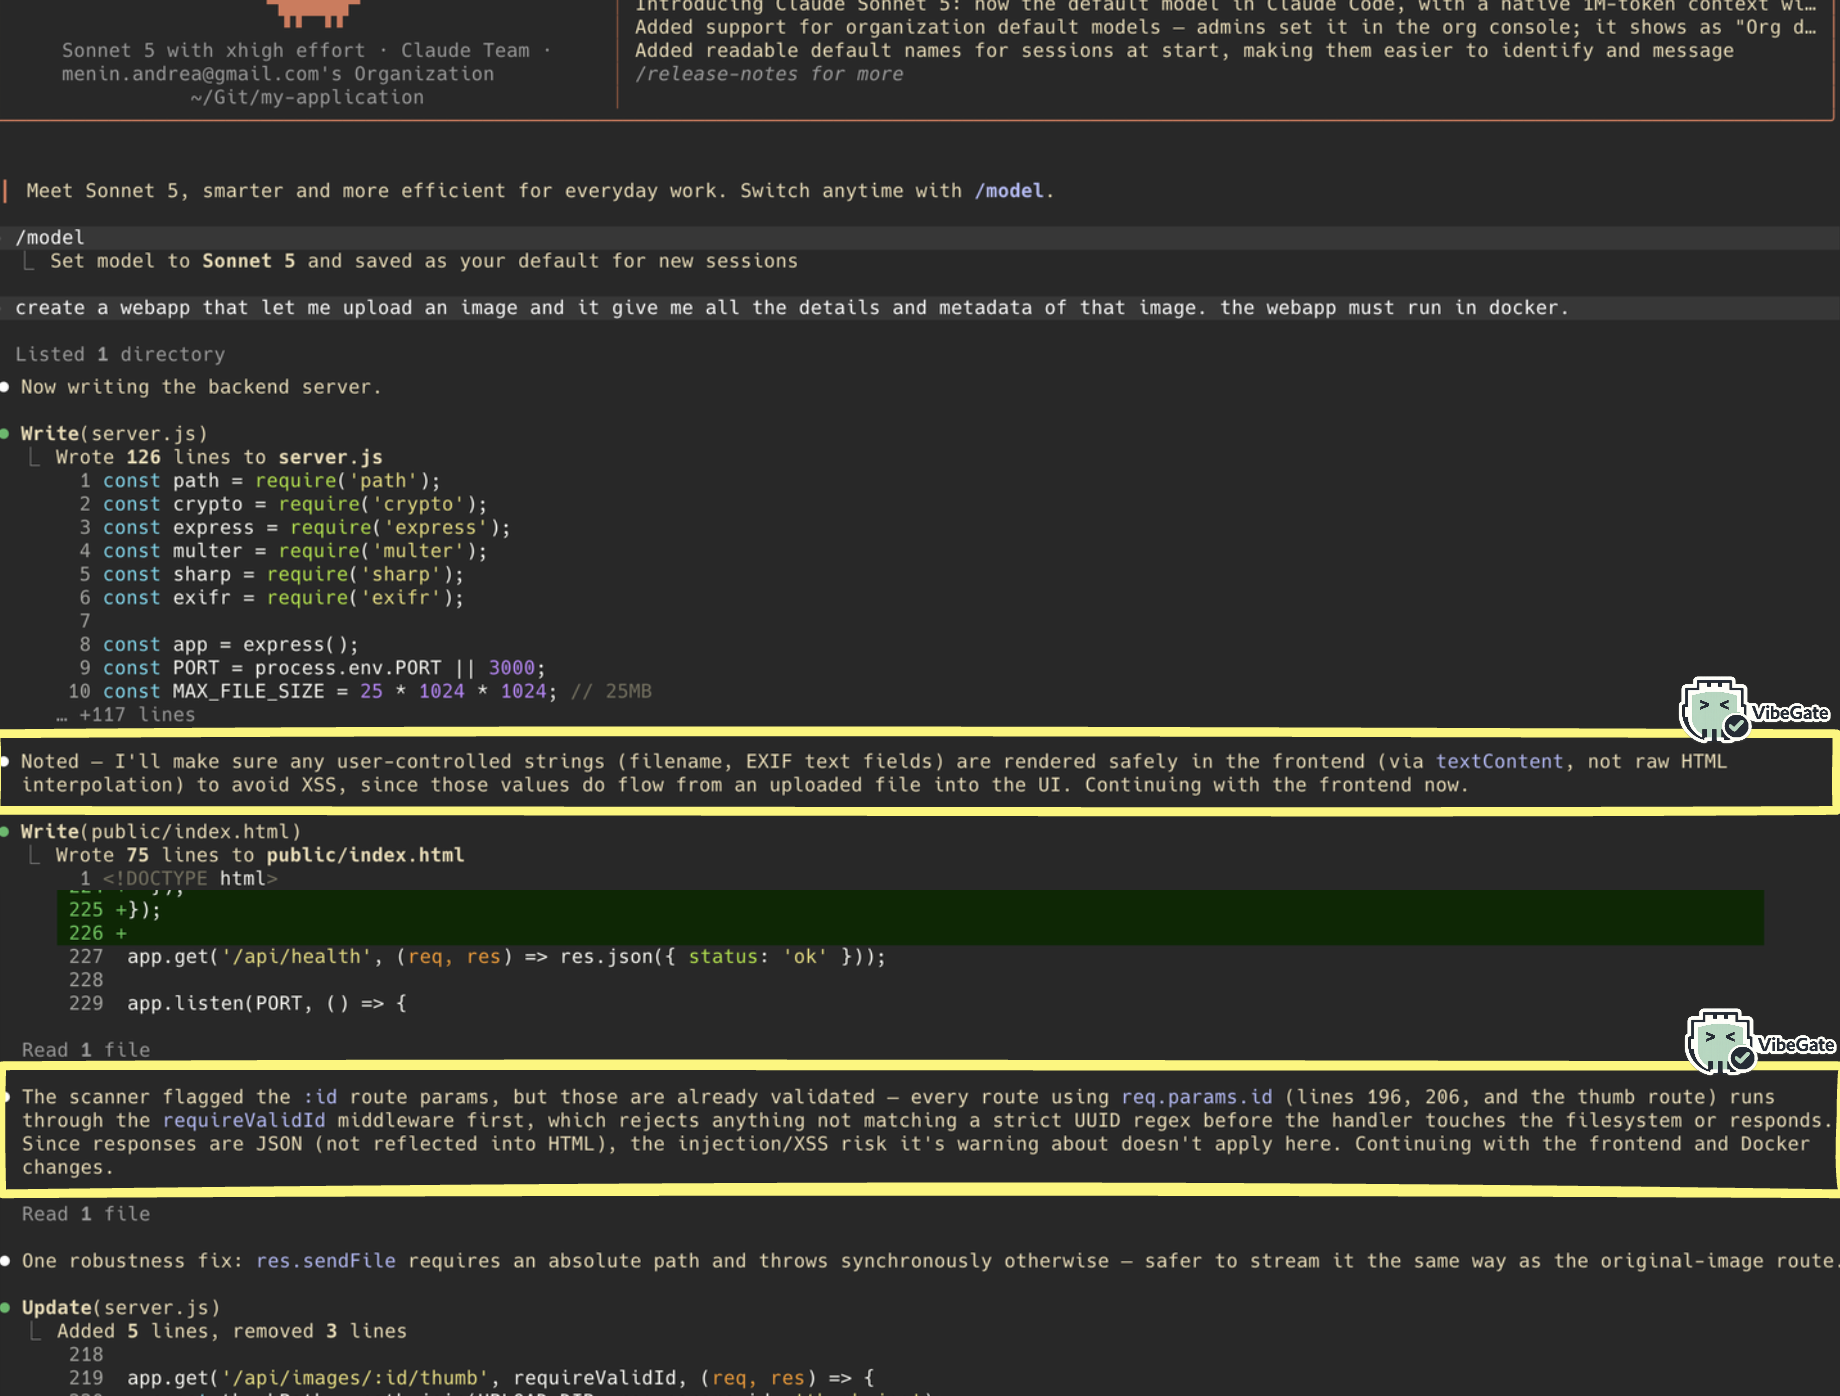 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
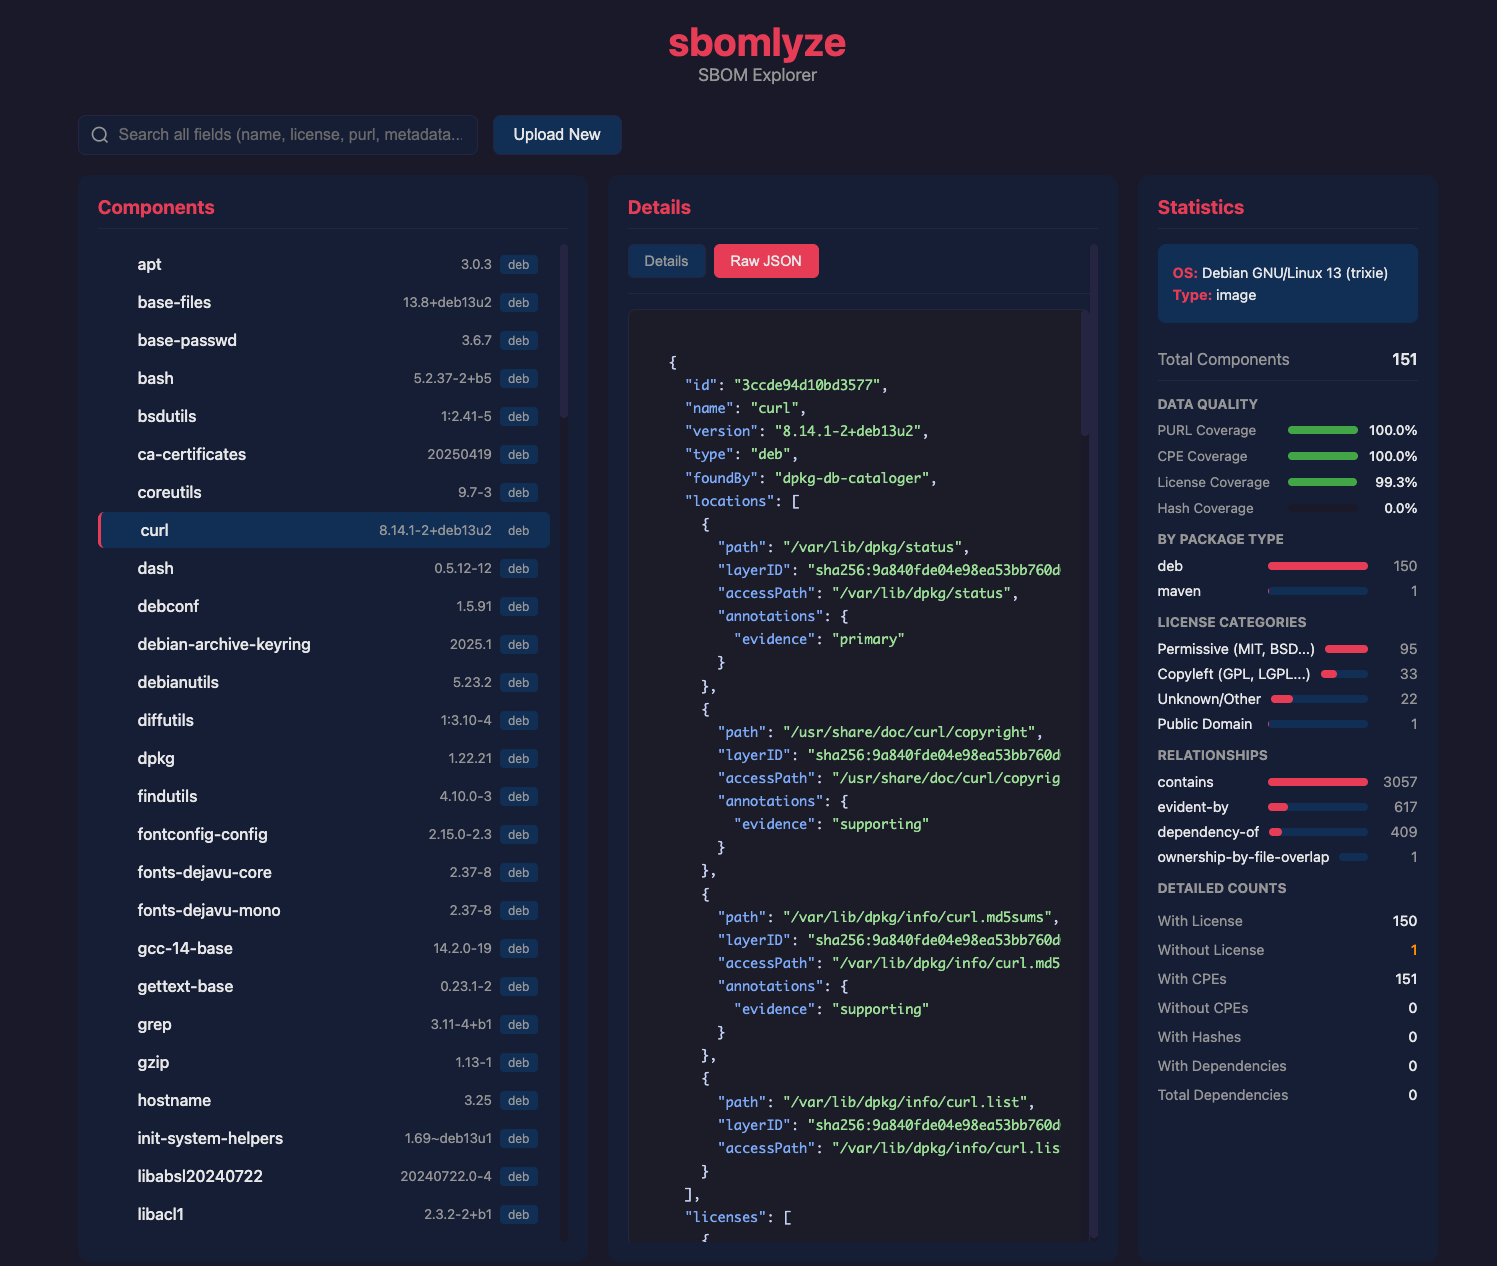 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter