
nGixshell
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
command-and-controlexploit-frameworkspayload-development+8
25
mateusverass/ngixshellnginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
 h4r5h1t/webcopilot
An automation tool that enumerates subdomains then filters out xss, sqli, open redirect, lfi, ssrf and rce parameters and then scans for…
 security-phoenix-demo/react2shell-scanner-cve-2025-55182
React2shell-web-scanner
 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
 toritoio/torito-r2s
Torito React2Shell Scanner & Exploit Tool (CVE-2025-55182 / 66478)
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 jan0x190/cve-2025-55182-simple-scanner-main
Multi-language scanner for CVE-2025-55182 RCE in Next.js React Server Components, with single/mass scanning modes and integrated bug bounty…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities
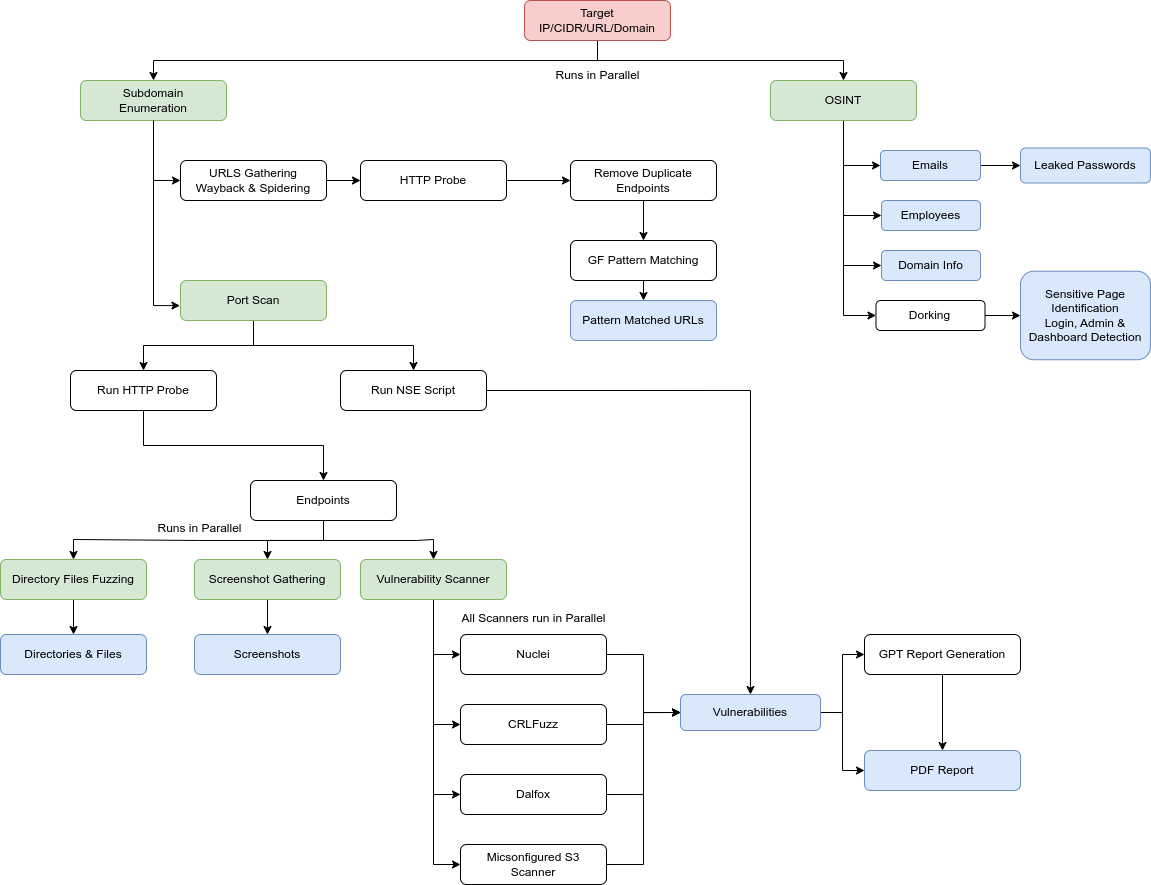 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 skavngr/rapidscan
:new: The Multi-Tool Web Vulnerability Scanner.
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 anmolksachan/thetimemachine
Weaponizing WaybackUrls for Recon, BugBounties , OSINT, Sensitive Endpoints and what not
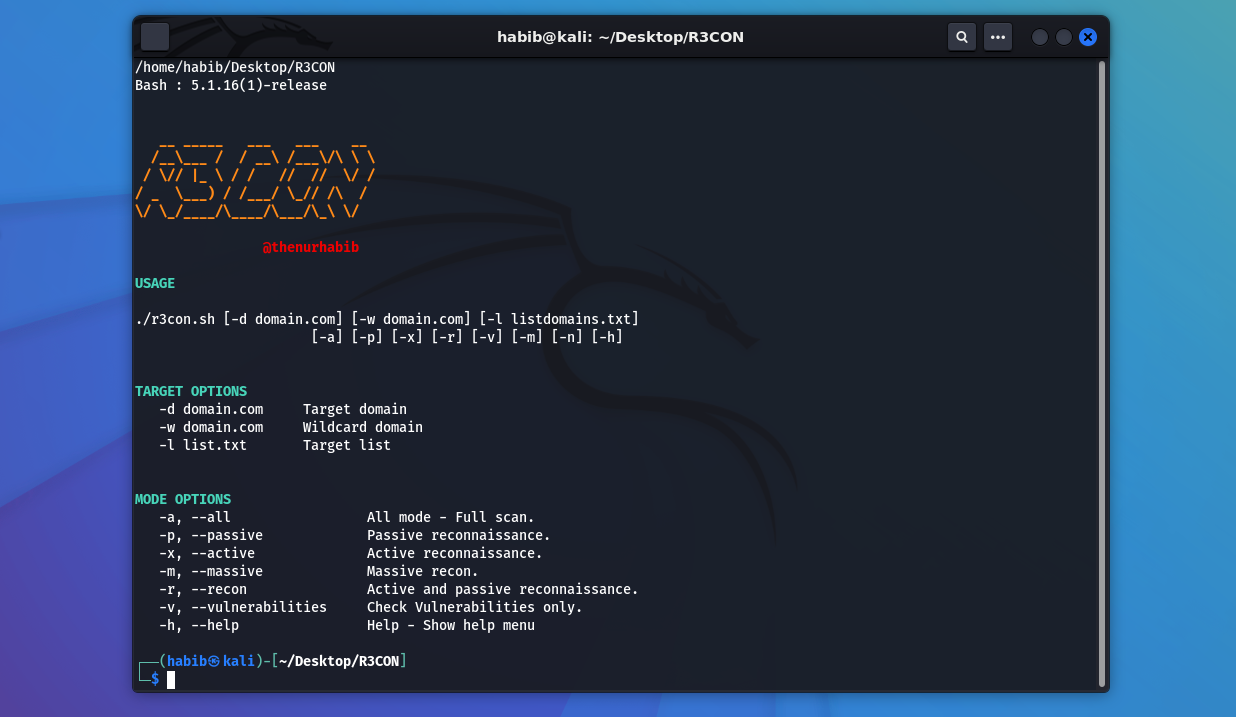 thenurhabib/r3con
Multi-functional Web Recon & Vulnerability Scanner Tool
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…