
RED_HAWK
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
crawlerdns-analysisinformation-gathering+5
3.8k
tuhinshubhra/red_hawkAll in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
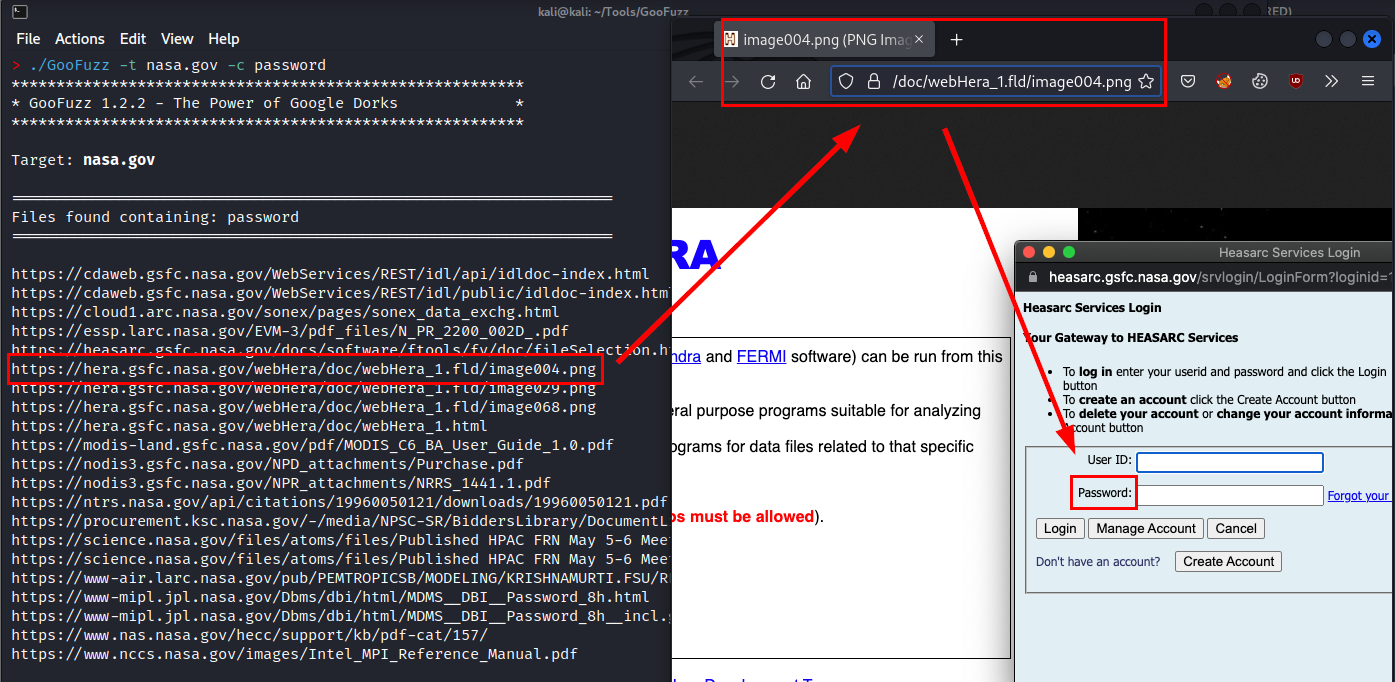 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
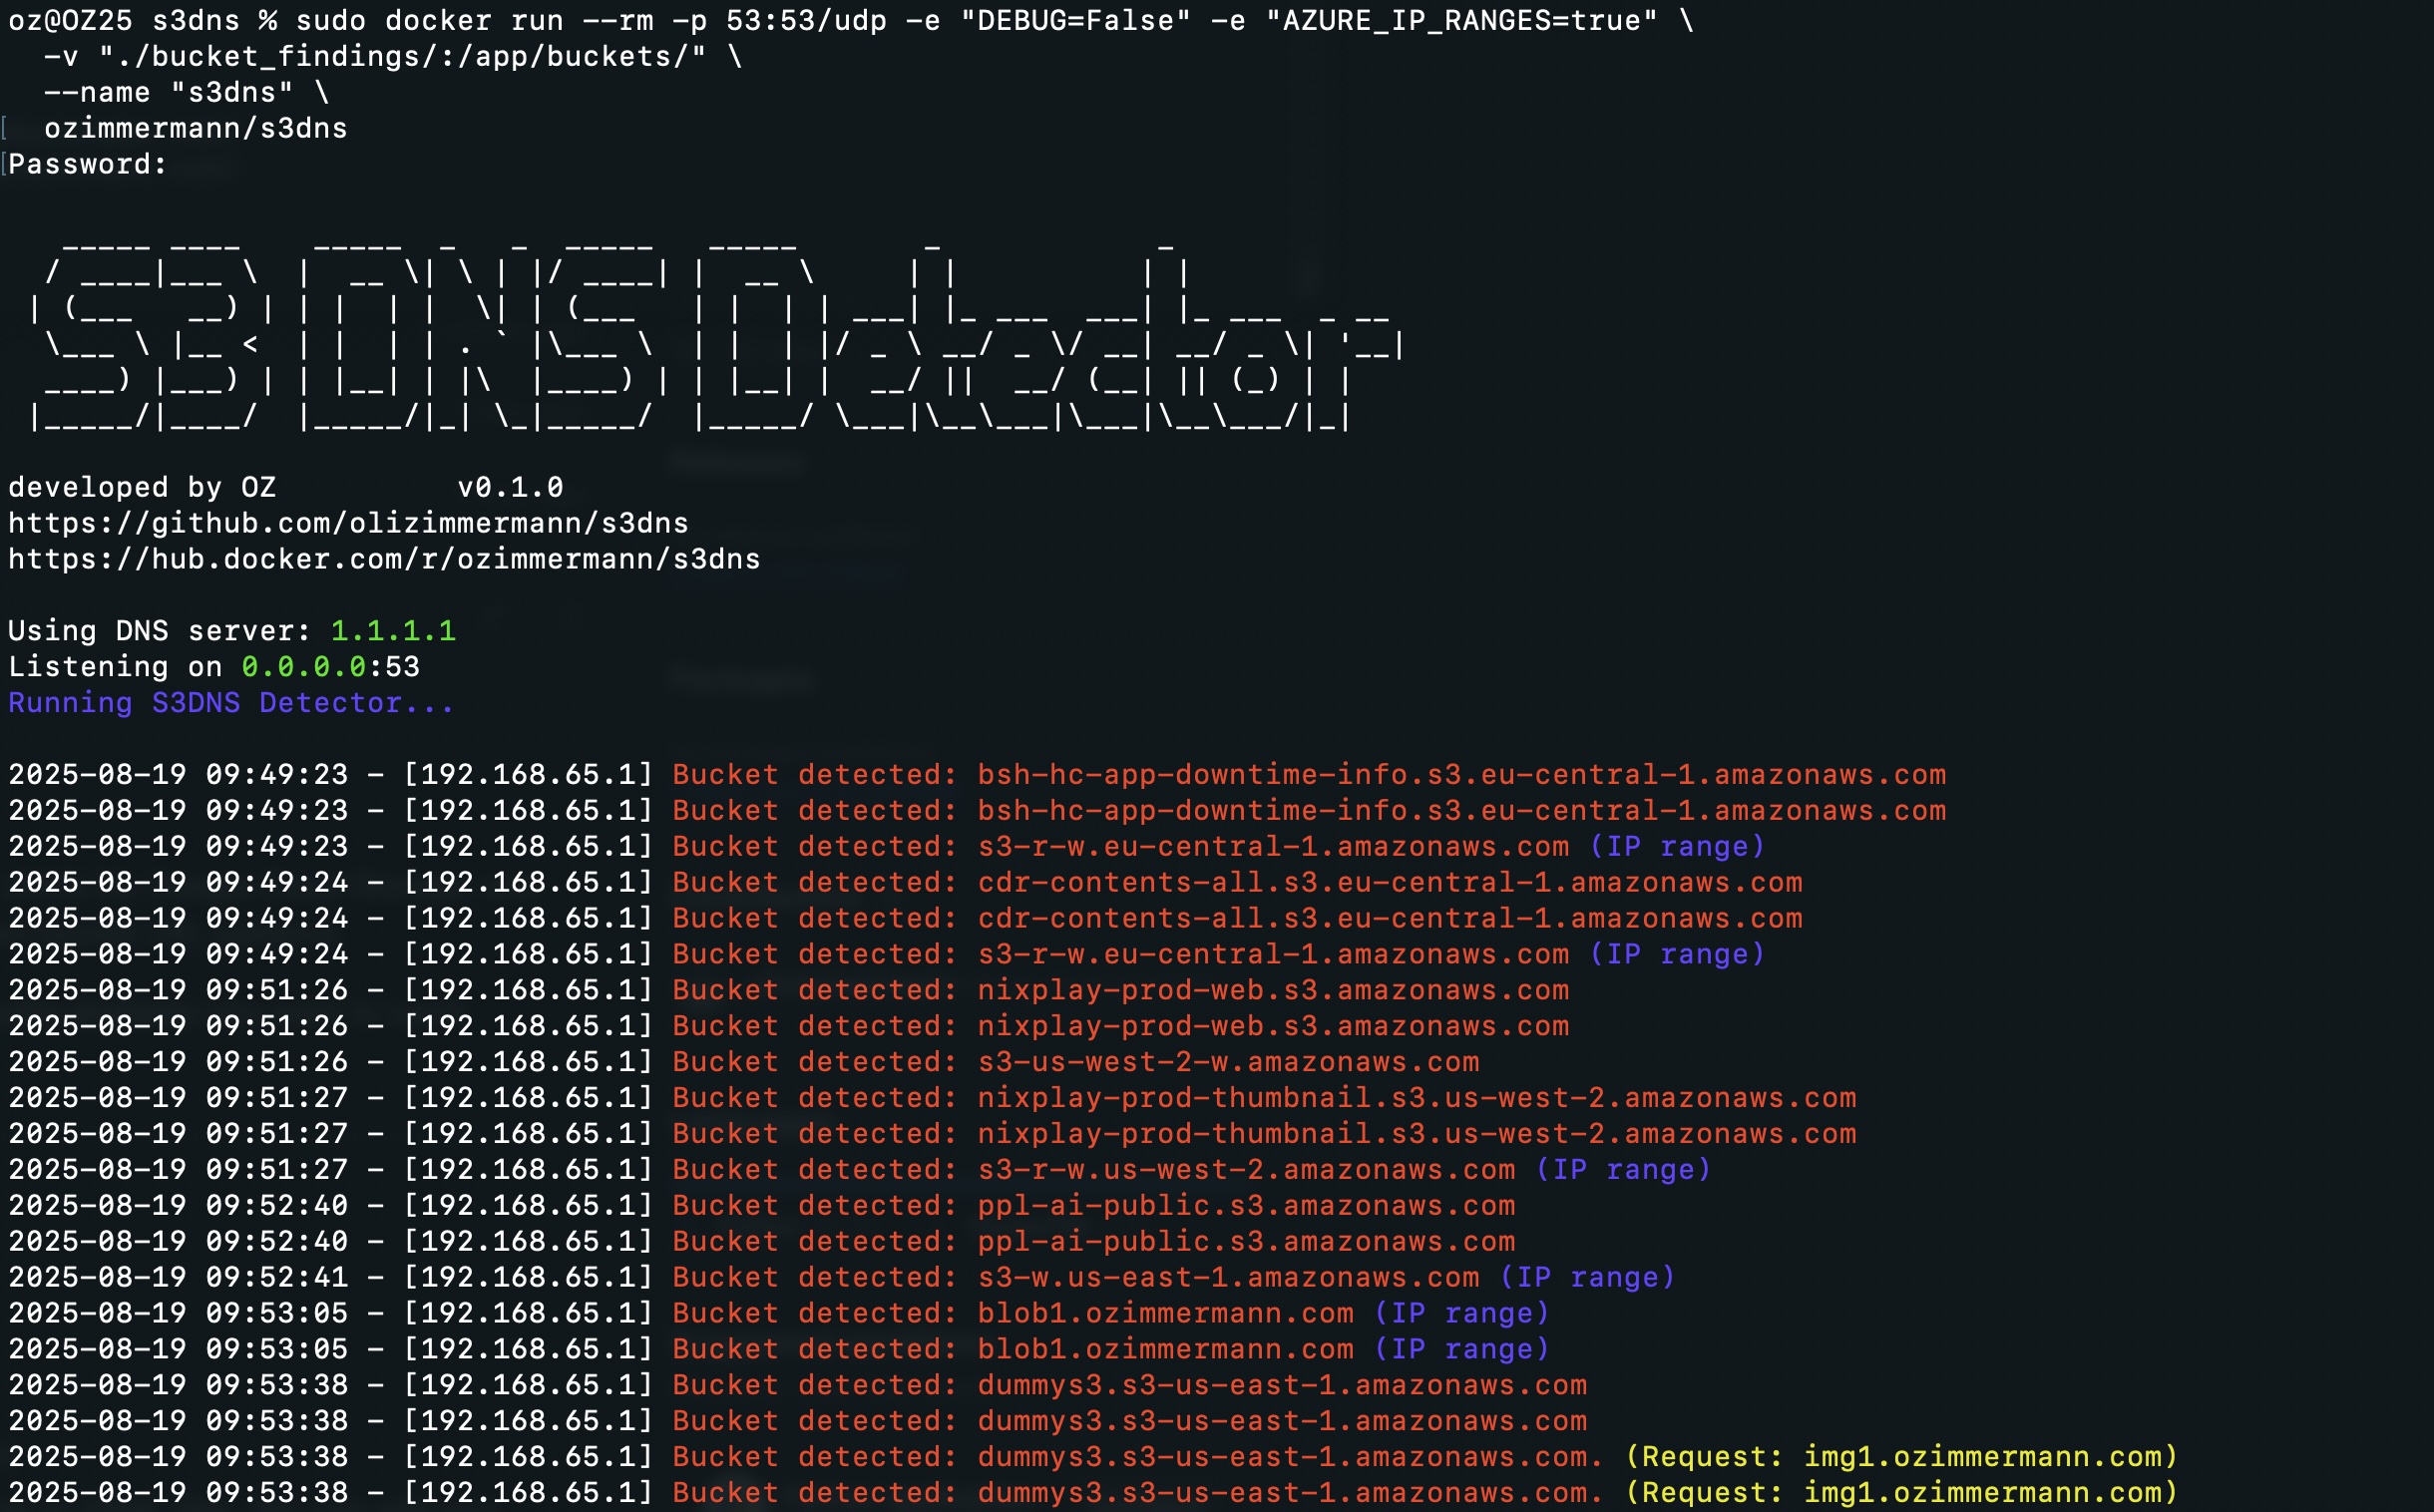 olizimmermann/s3dns
Passive DNS server that detects exposed cloud storage buckets (AWS S3, GCP, Azure) by resolving DNS requests, tracing CNAME chains, and flagging…
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 jan0x190/cve-2025-55182-simple-scanner-main
Multi-language scanner for CVE-2025-55182 RCE in Next.js React Server Components, with single/mass scanning modes and integrated bug bounty…
 josekutty-k/frontpage-server-extensions-vulnerability-scanner
Python script to scan for CVE-2000-0114 vulnerability in Frontpage Server Extensions. Automates subdomain enumeration and vulnerability scanning…
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
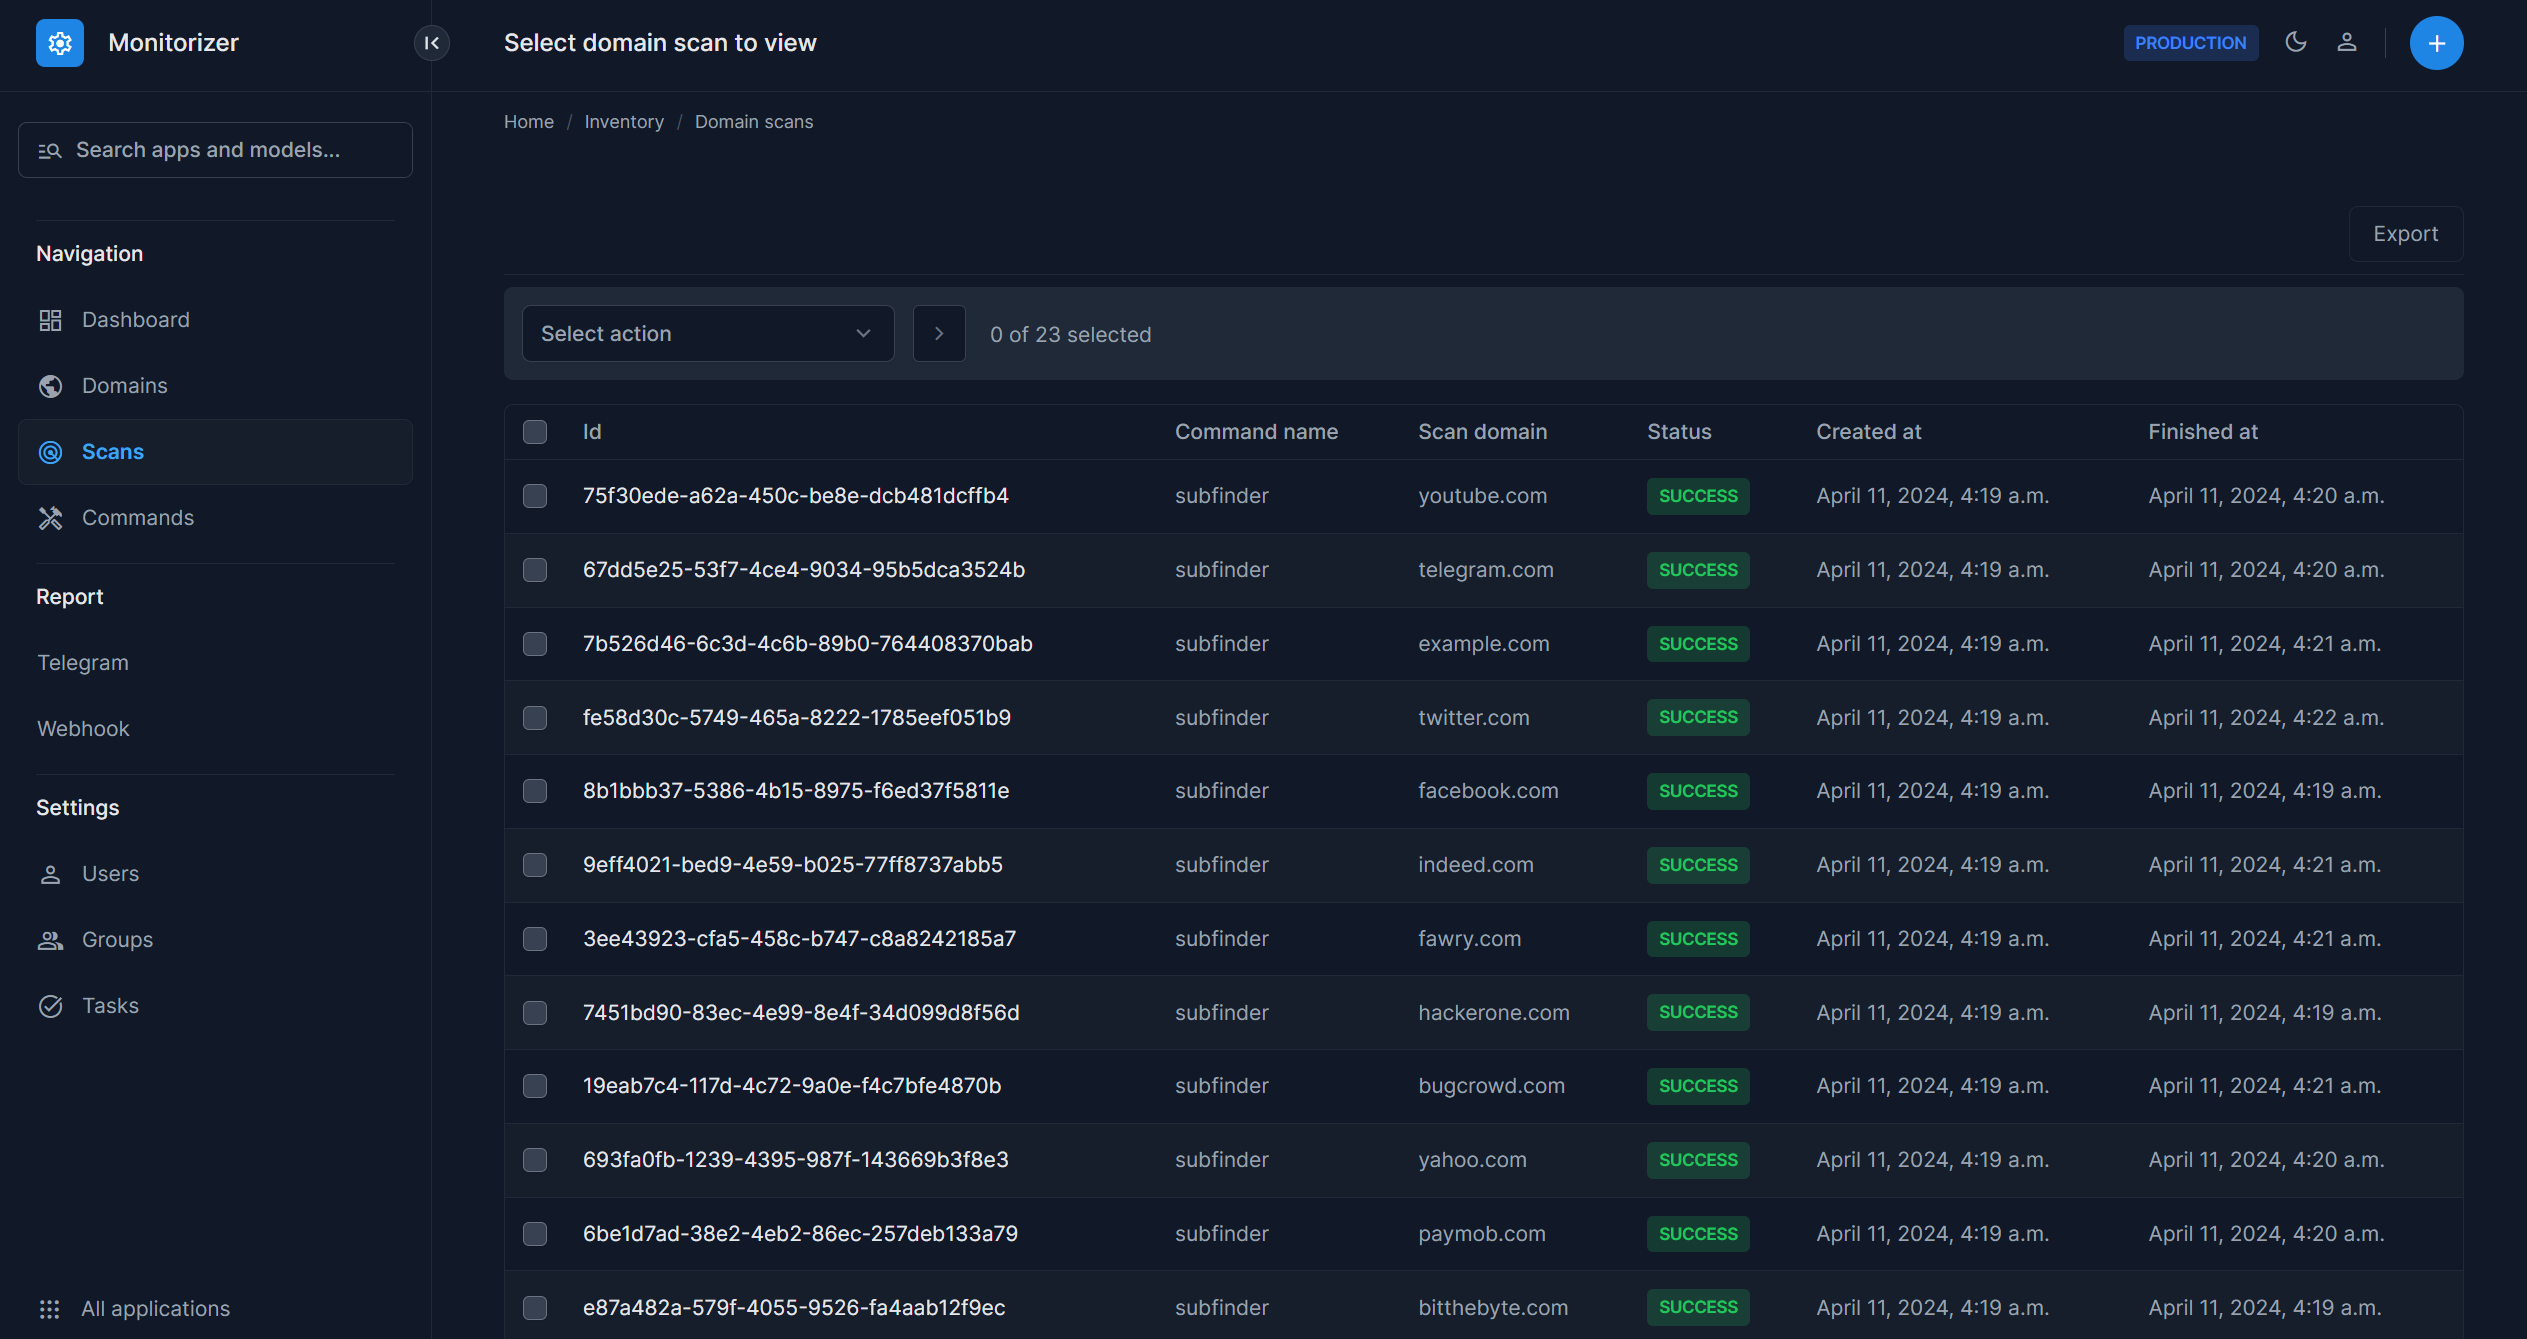 bitthebyte/monitorizer
Monitoring framework to detect and report newly found subdomains on a specific target using various scanning tools
 security-phoenix-demo/react2shell-scanner-cve-2025-55182
React2shell-web-scanner
 rapticore/ore_react2shell_scanner
CVE-2025-55182 (React2Shell) Scanner
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…