

dddd
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
fingerprint-spoofinginformation-gatheringnetwork-mapping+9
1.9k
sleepingbag945/ddddBatch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
 twelvesec/gasmask
Information gathering tool - OSINT
 superhedgy/attacksurfacemapper
AttackSurfaceMapper is a tool that aims to automate the reconnaissance process.
 h4r5h1t/webcopilot
An automation tool that enumerates subdomains then filters out xss, sqli, open redirect, lfi, ssrf and rce parameters and then scans for…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
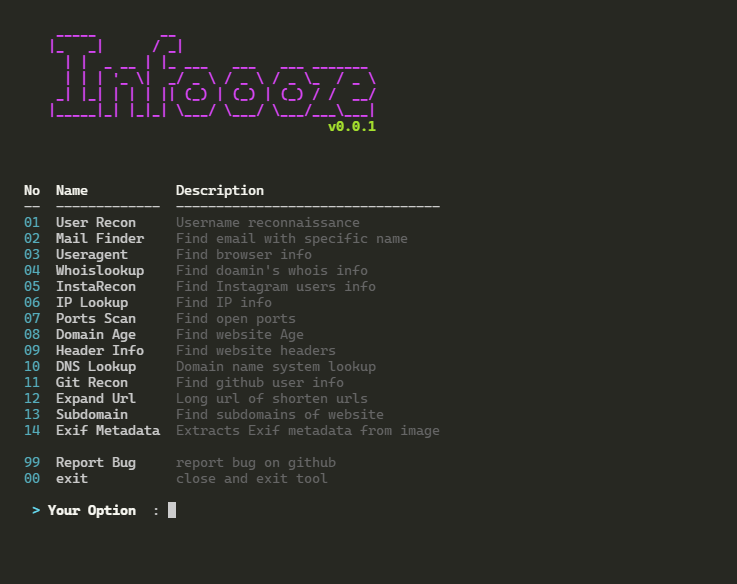 devxprite/infoooze
A OSINT tool which helps you to quickly find information effectively. All you need is to input and it will take take care of rest.
 iamthefrogy/frogy2.0
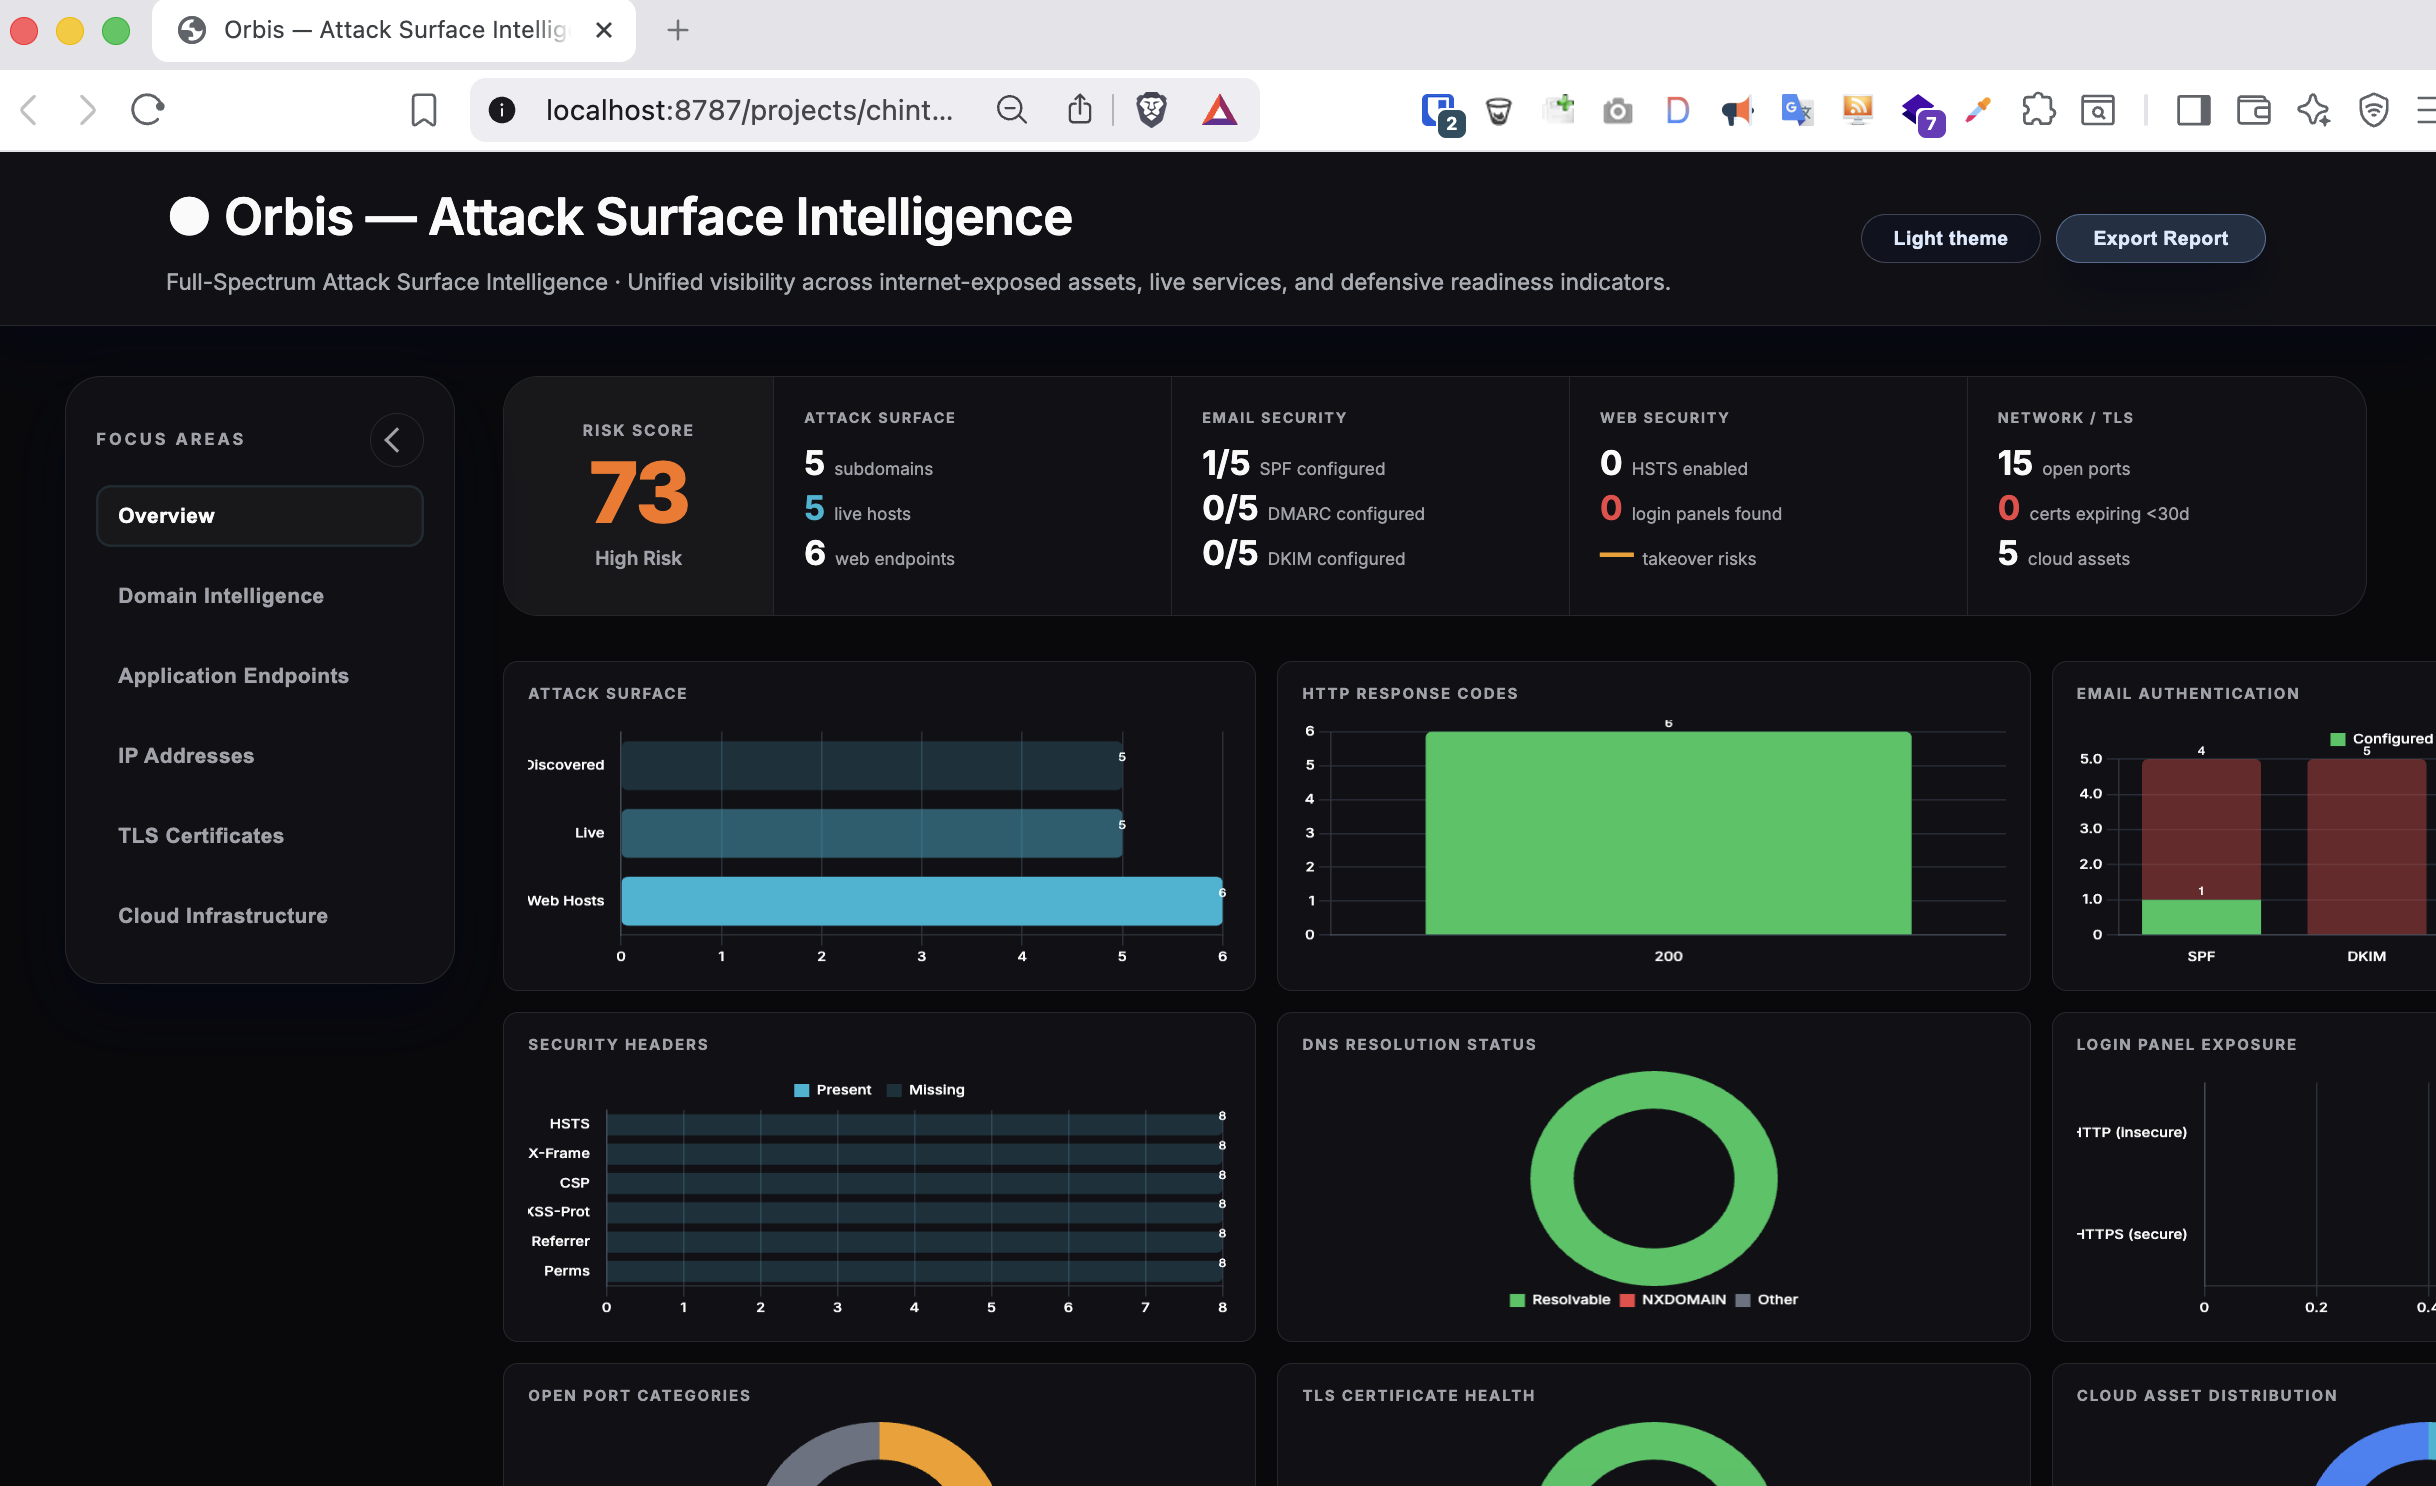
Orbis is an full spectrum automated external attack surface intelligent toolkit.
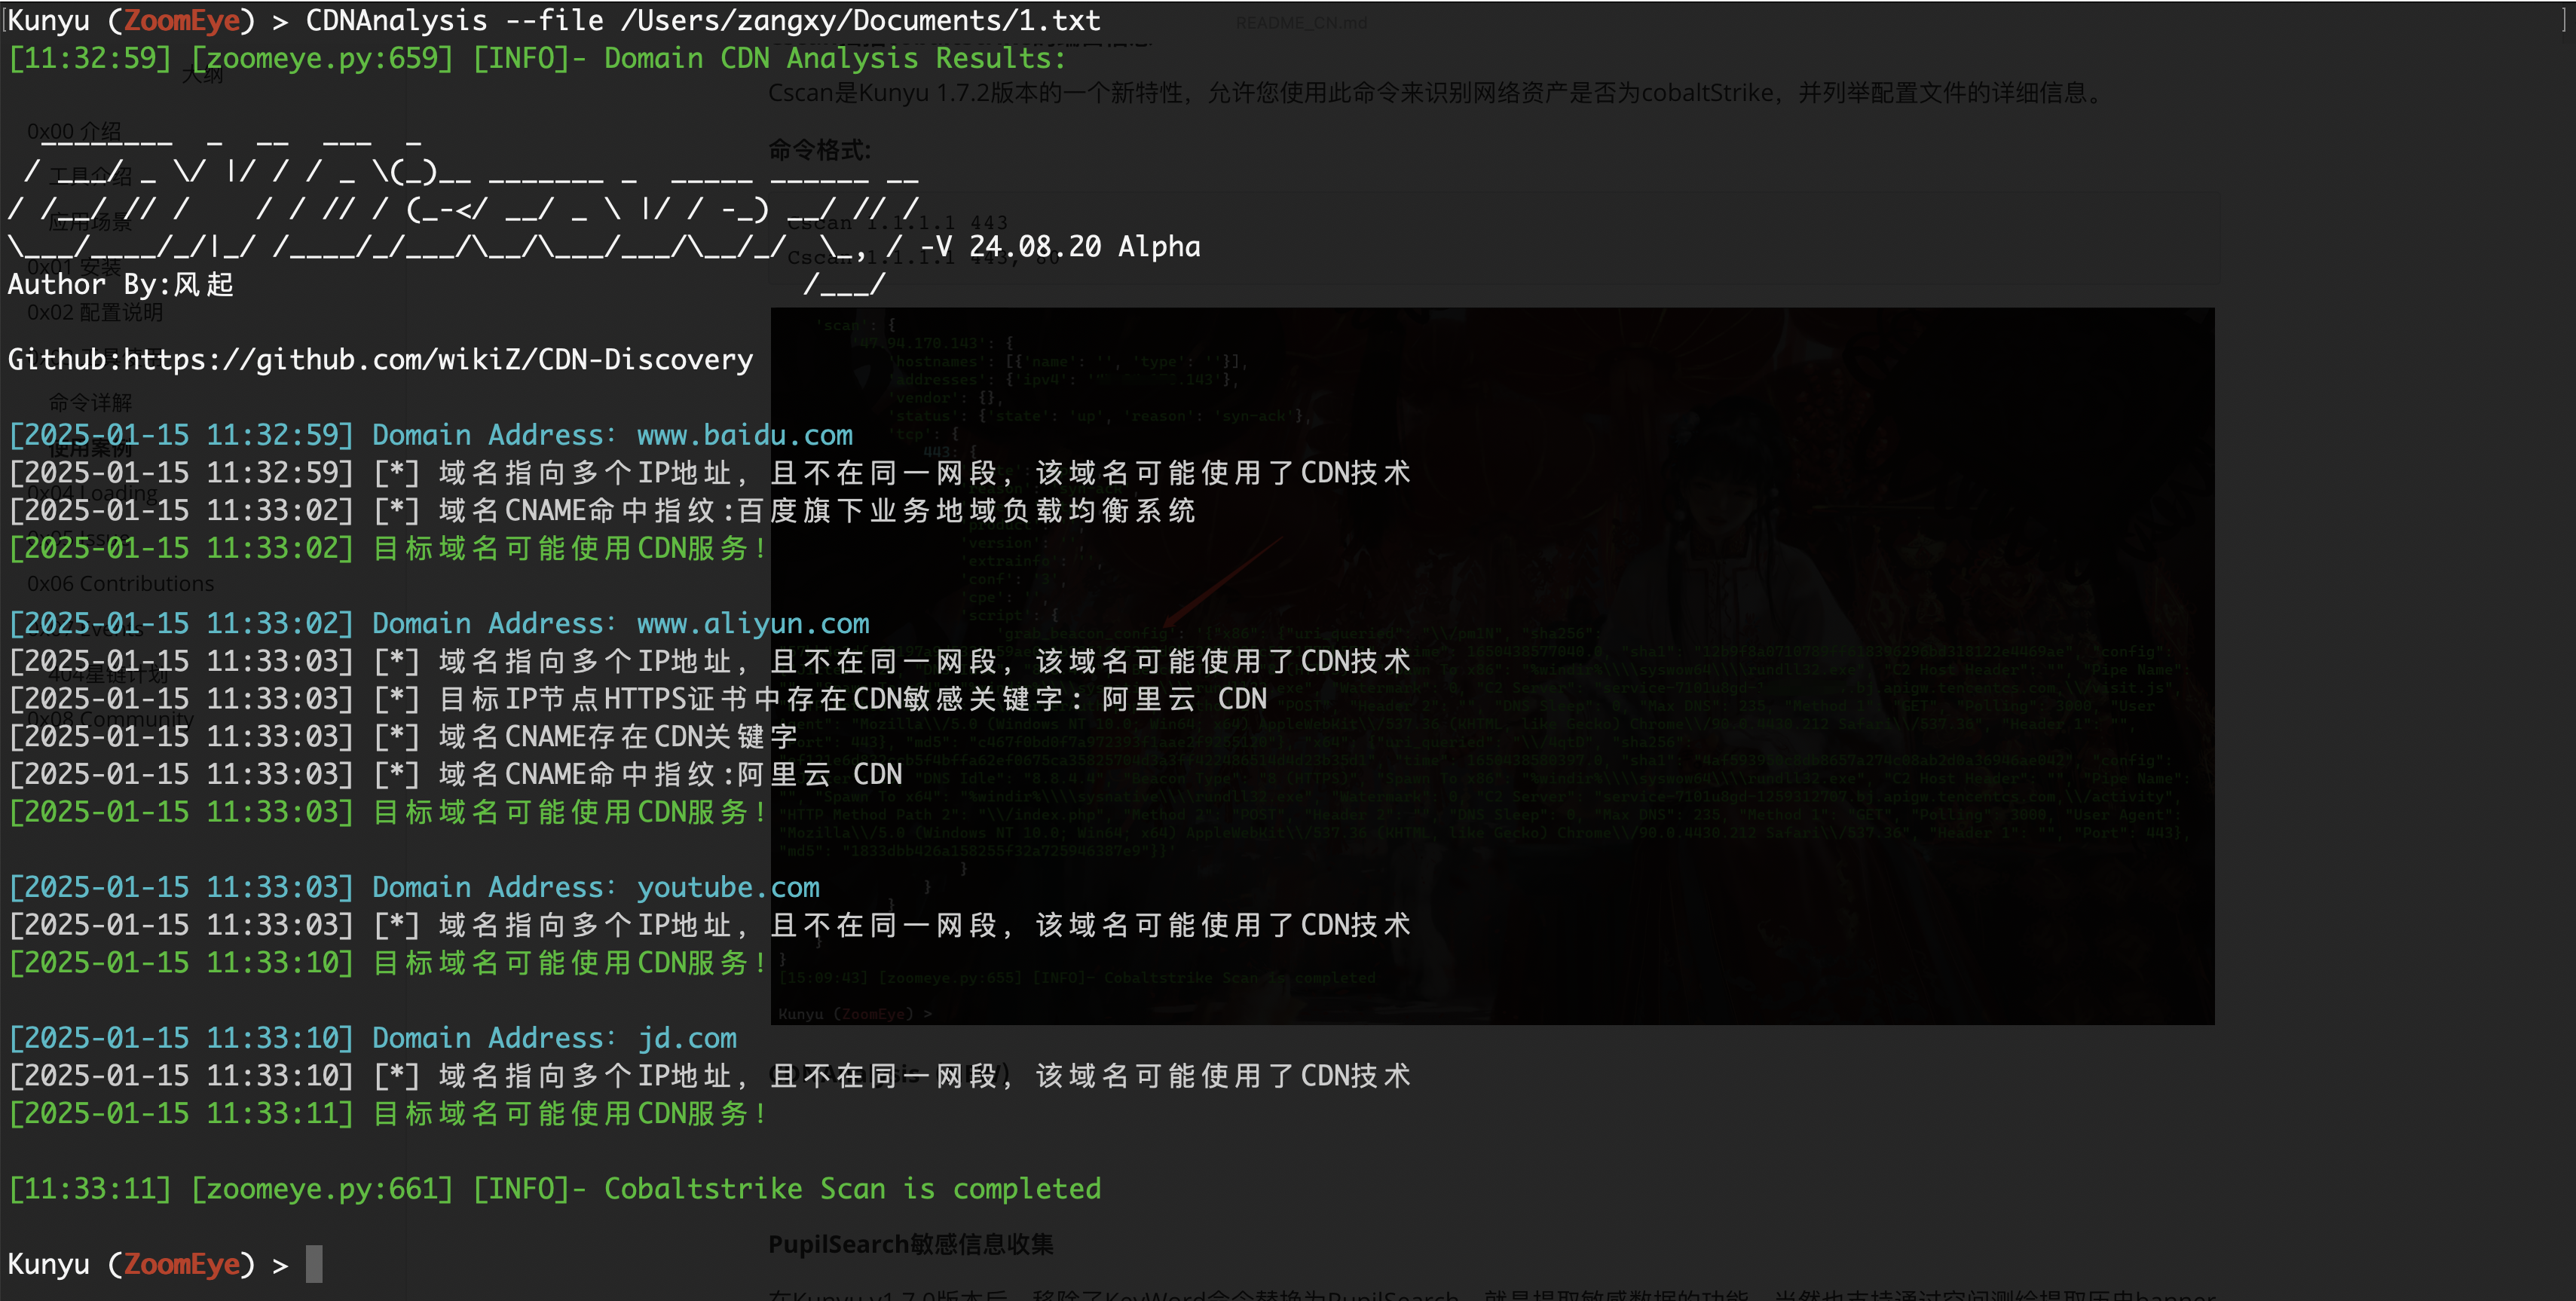 knownsec/kunyu
Kunyu, more efficient corporate asset collection
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
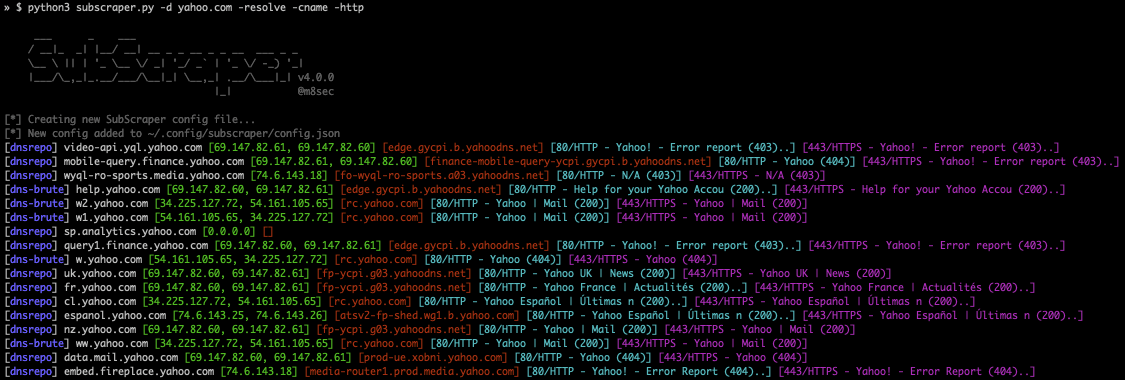 m8sec/subscraper
Subdomain and target enumeration tool built for offensive security testing
 chris408/ct-exposer
An OSINT tool that discovers sub-domains by searching Certificate Transparency logs
 bywalks/darkangel
Automated white-hat vulnerability scanner that monitors HackerOne and Bugcrowd assets, performs subdomain enumeration, crawling, fingerprinting, and…
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
 x1mdev/reconpi
ReconPi - A lightweight recon tool that performs extensive scanning with the latest tools.
 spyboy-productions/omnisci3nt
Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…