

Archived
GraphCrawler
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
api-security-testinginformation-gatheringreconnaissance+3
gsmith257-cyber/graphcrawlerGraphQL automated security testing toolkit
 edoverflow/megplus
Automated reconnaissance wrapper — TomNomNom's meg on steroids. [DEPRECATED]

 cyberdev-tools/nsec3-x
The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…
 eslam3kl/3klcon
Automation Recon tool which works with Large & Medium scopes. It performs a lot of tasks and gets back all the results in separated files.
 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites
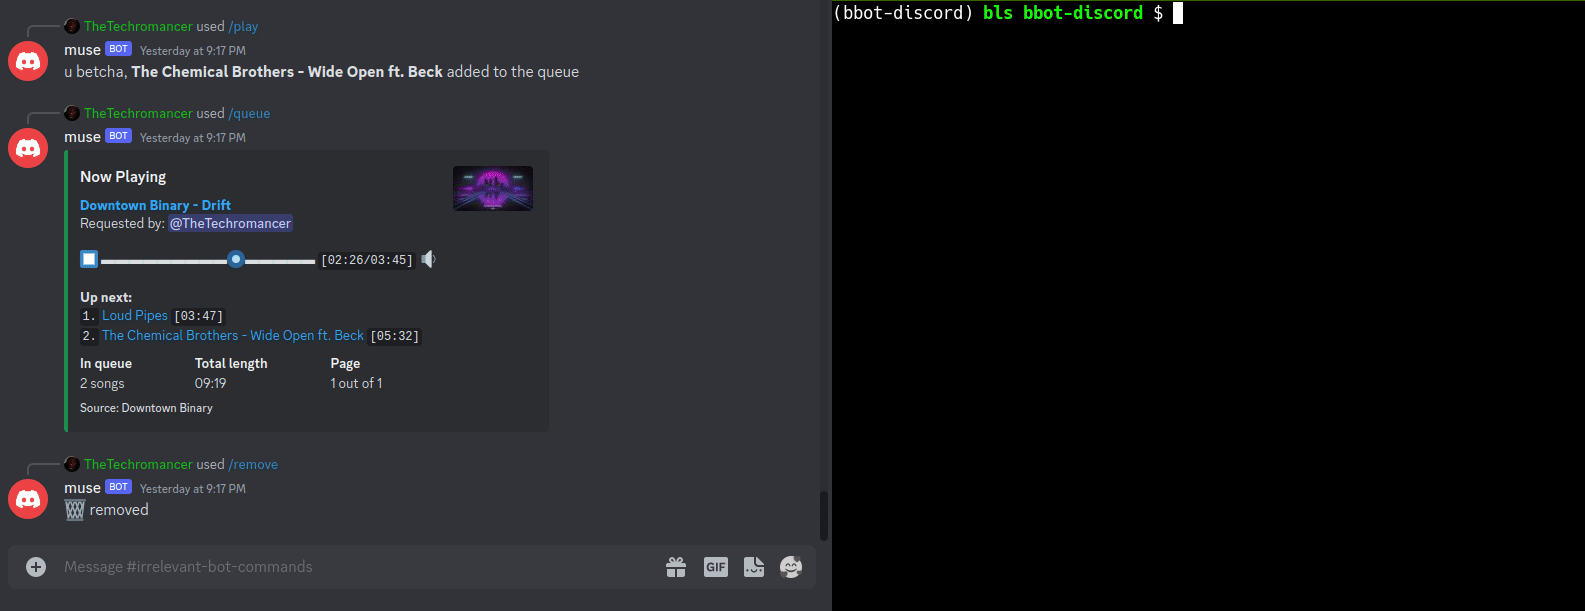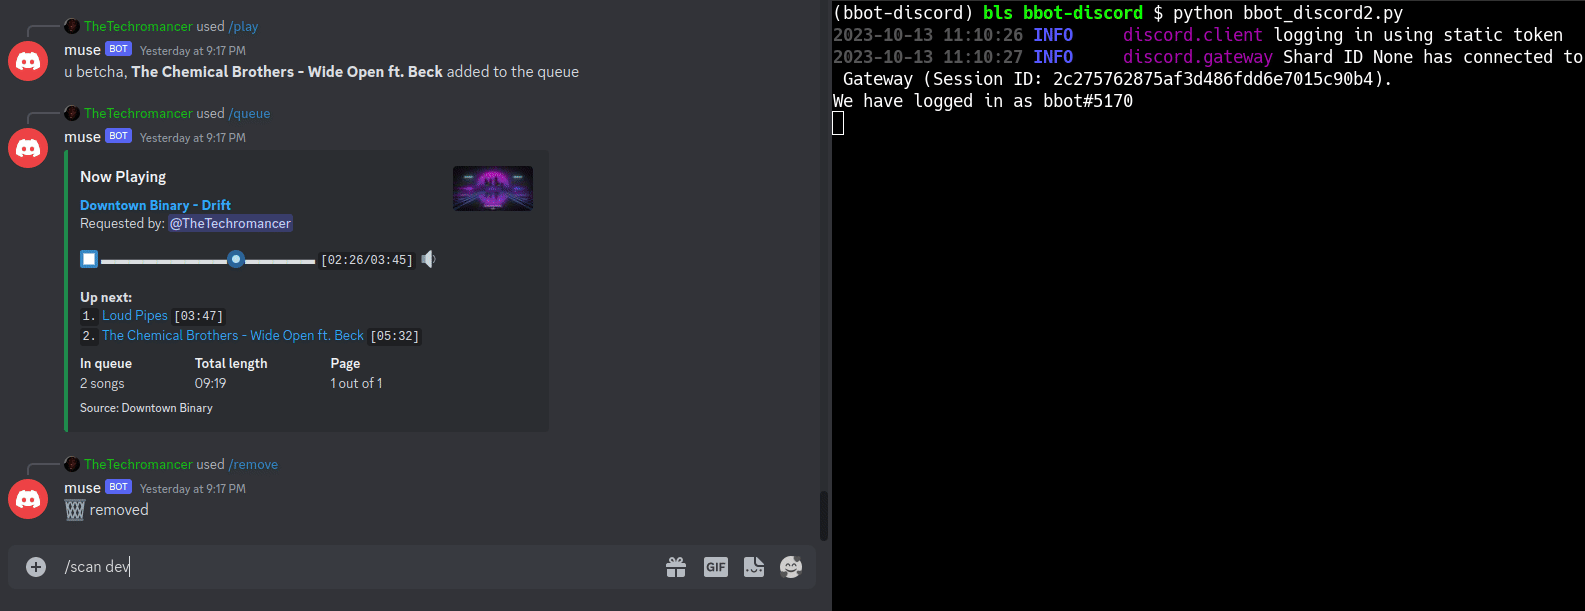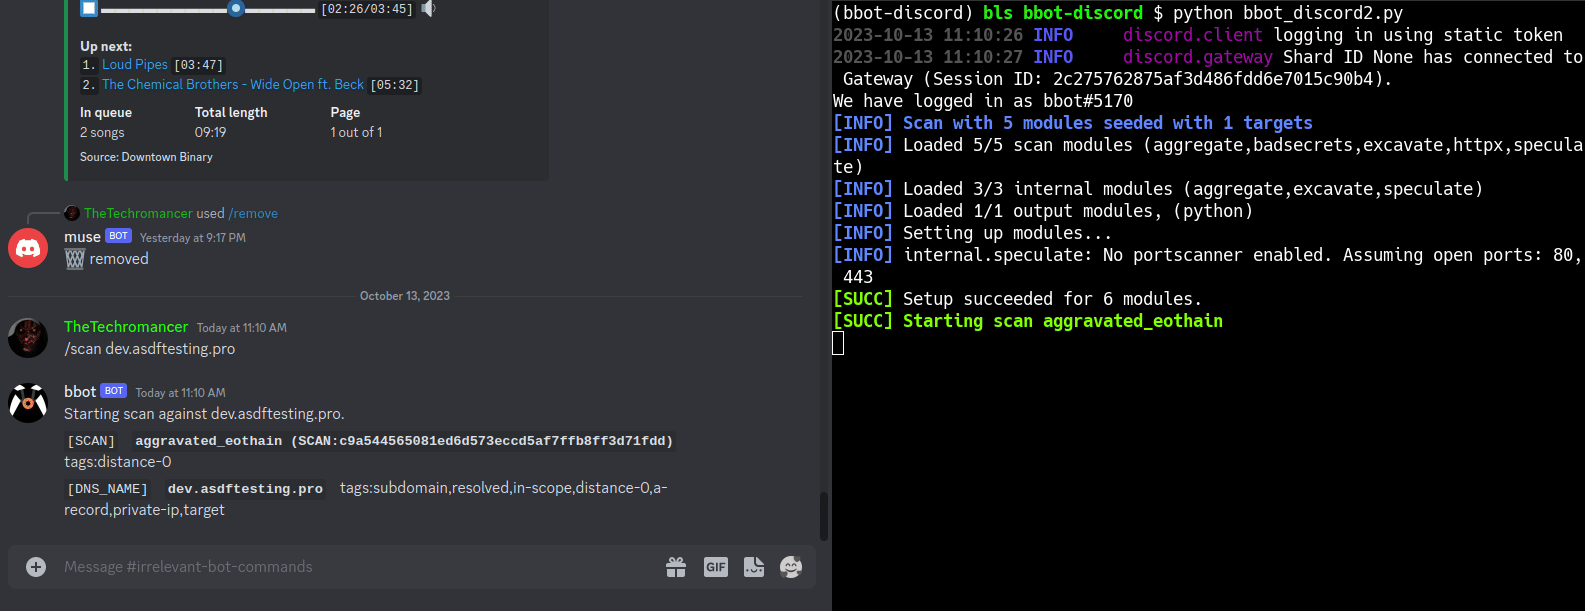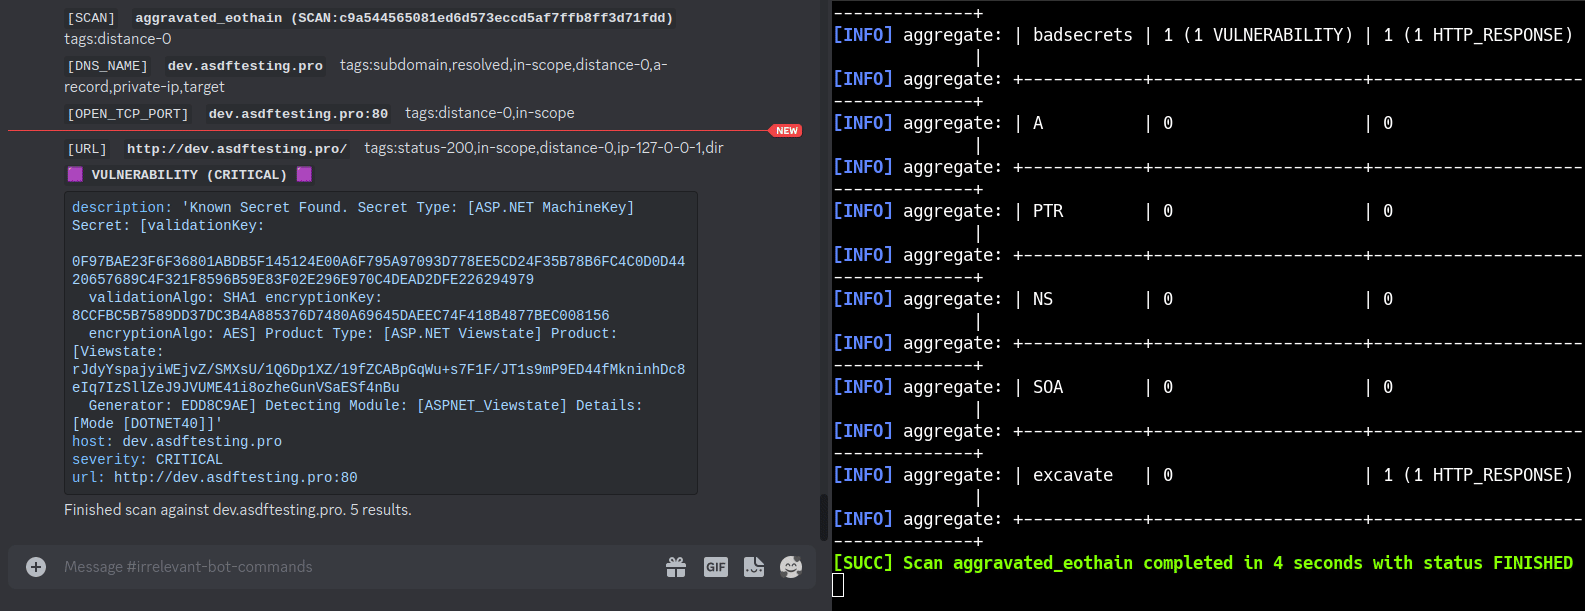 blacklanternsecurity/bbot
The recursive internet scanner for hackers. 🧡
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
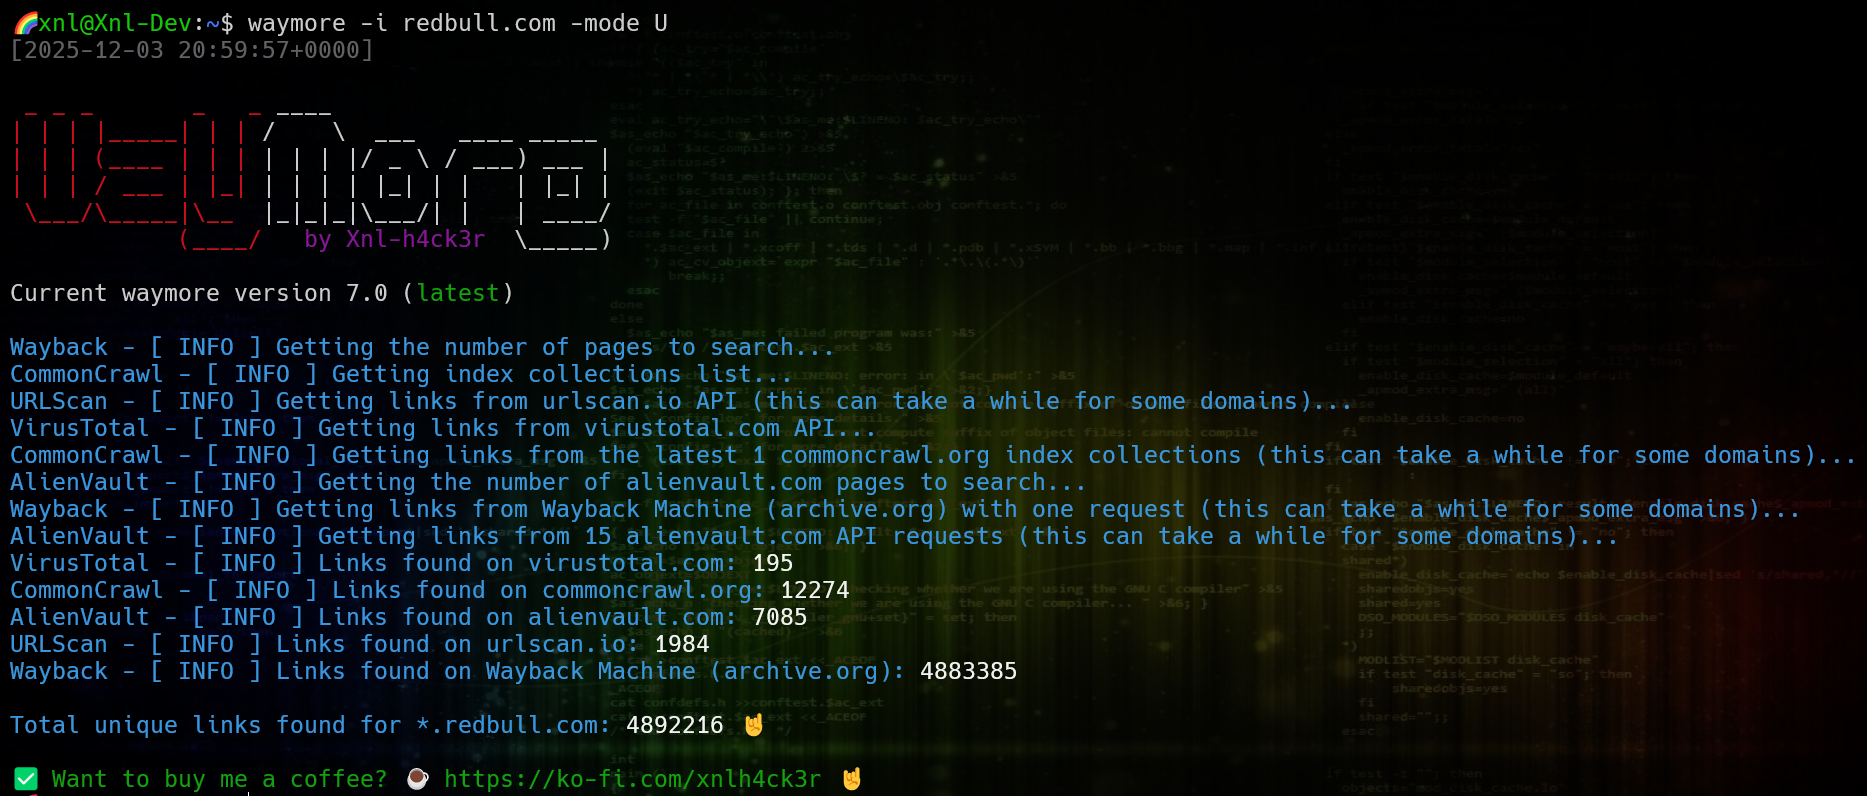 xnl-h4ck3r/waymore
Find way more from the Wayback Machine, Common Crawl, Alien Vault OTX, URLScan, VirusTotal, GhostArchive & Intelligence X!
 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.

 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 mhmdiaa/second-order
Crawls web applications to detect second-order subdomain takeover vulnerabilities by collecting URLs and matching configurable rules for non-200…
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…