

wordlists
 trickest/wordlists
Real-world infosec wordlists, updated regularly
curated-resourcesinformation-gatheringpenetration-testing+3
trickest/wordlistsReal-world infosec wordlists, updated regularly
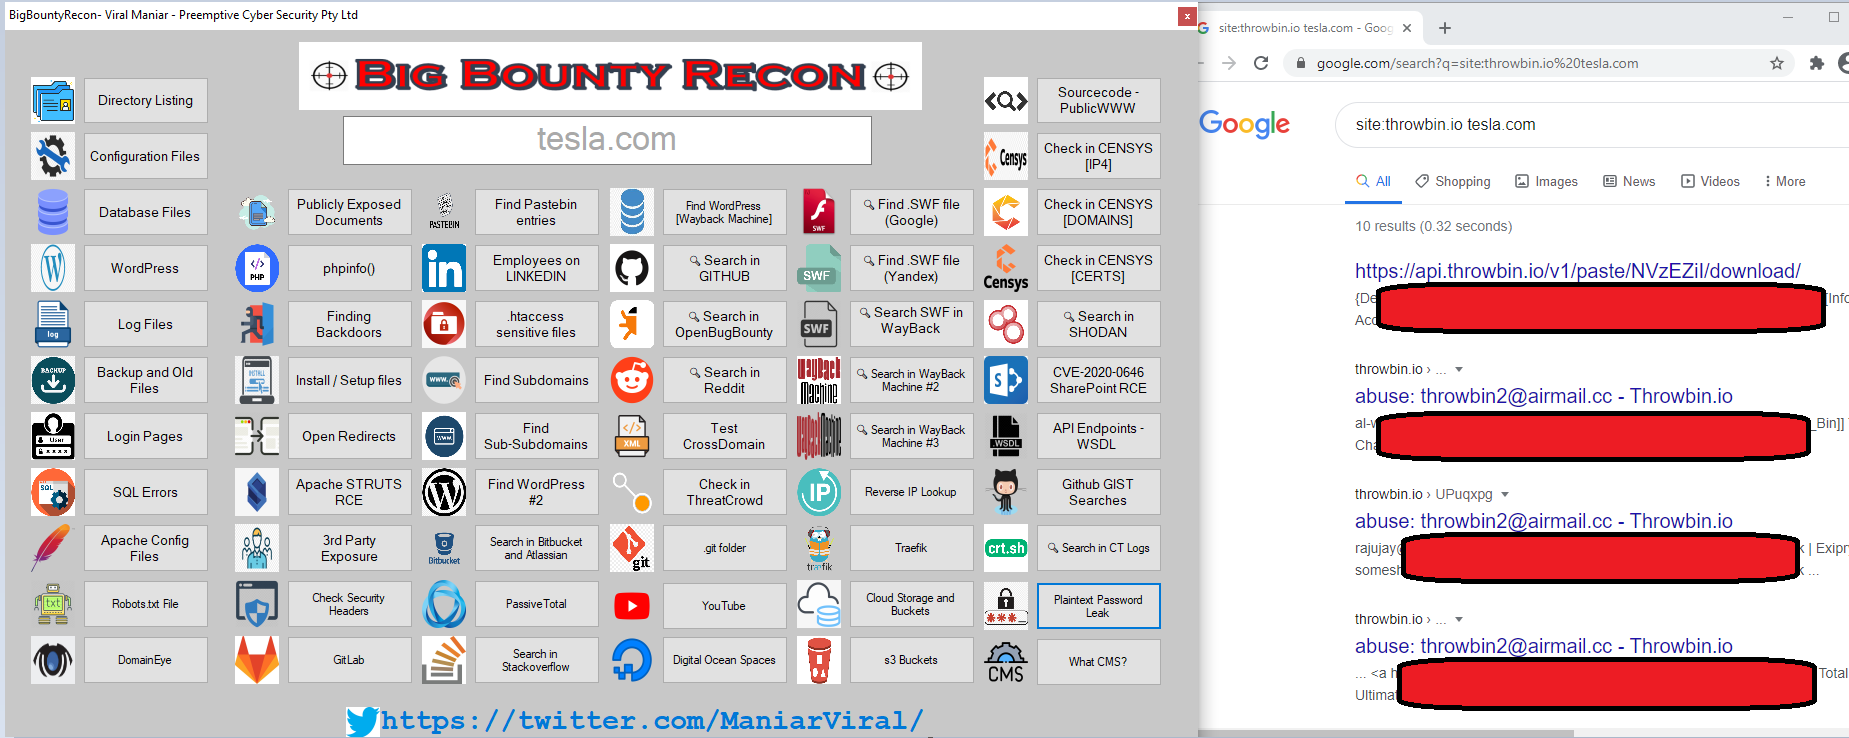 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 ice3man543/subover
A Powerful Subdomain Takeover Tool
 christophetd/censys-subdomain-finder
⚡ Perform subdomain enumeration using the certificate transparency logs from Censys.
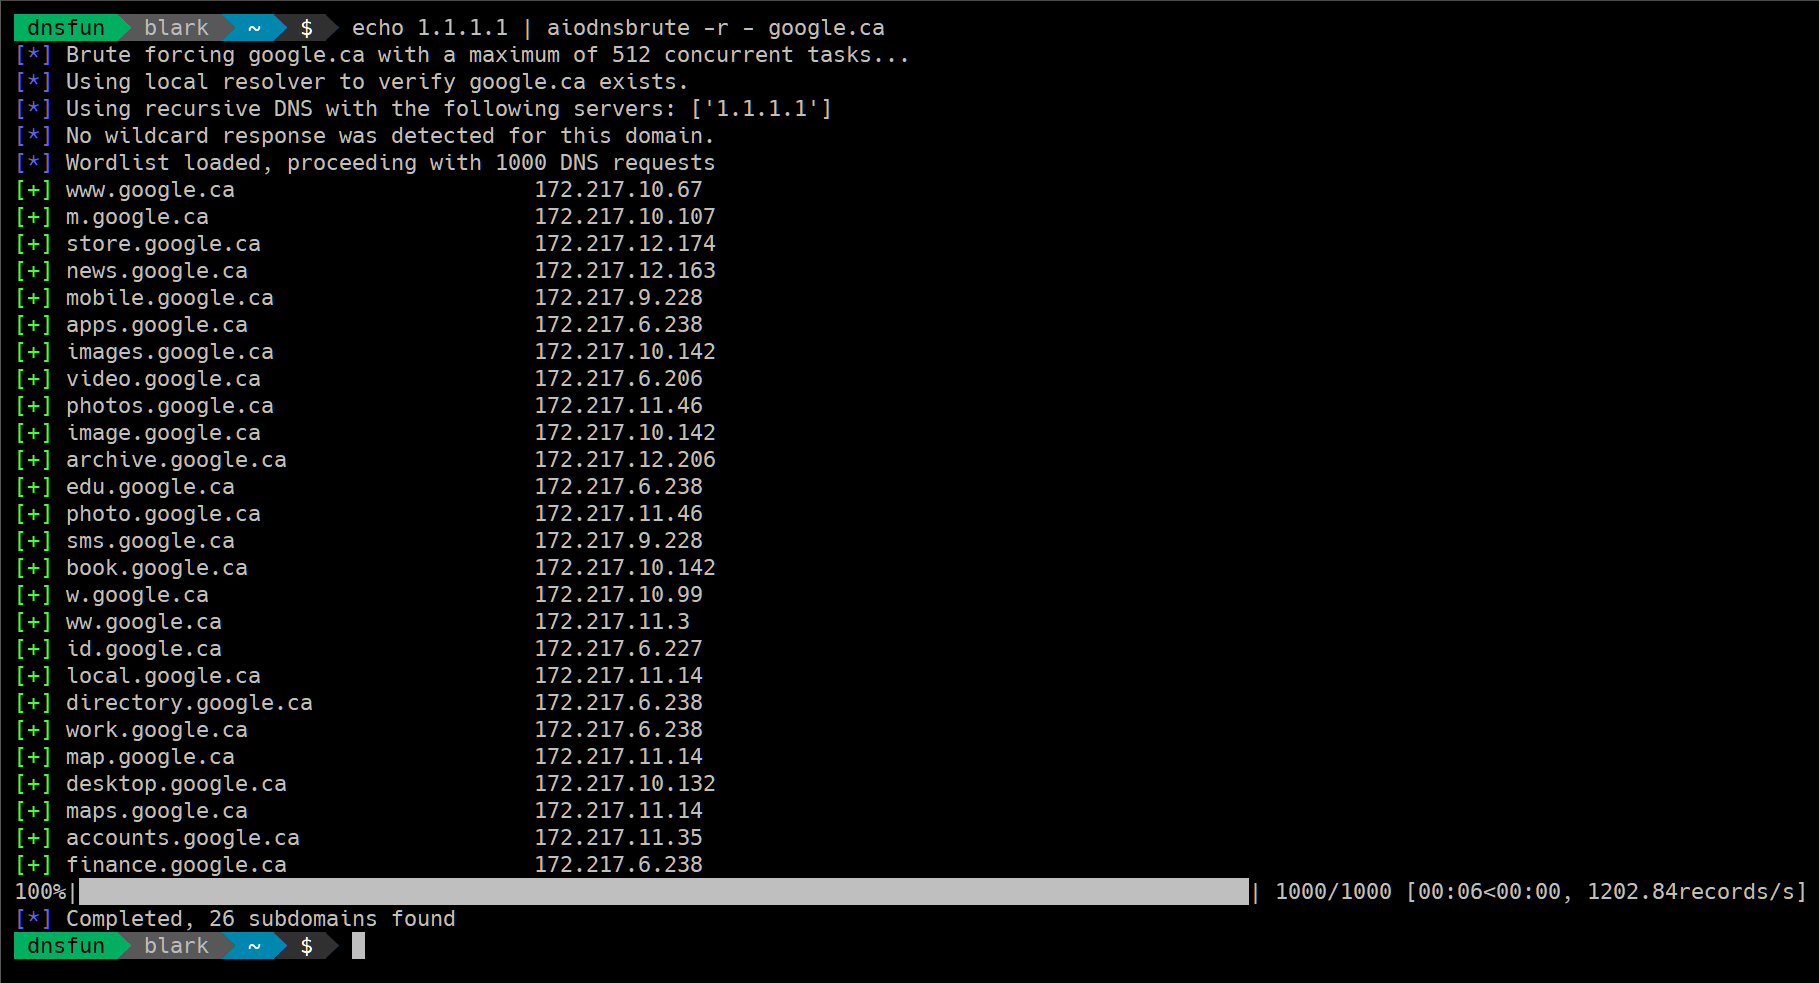 blark/aiodnsbrute
Python 3.5+ DNS asynchronous brute force utility
 umutcamliyurt/subhunter
Fast subdomain takeover scanner that checks DNS CNAME records against known fingerprints to detect vulnerable subdomains. Built in Go with…
 r3curs1v3-pr0xy/sub404
A python tool to check subdomain takeover vulnerability
 j3ssie/osmedeus
A Modern Orchestration Engine for Security
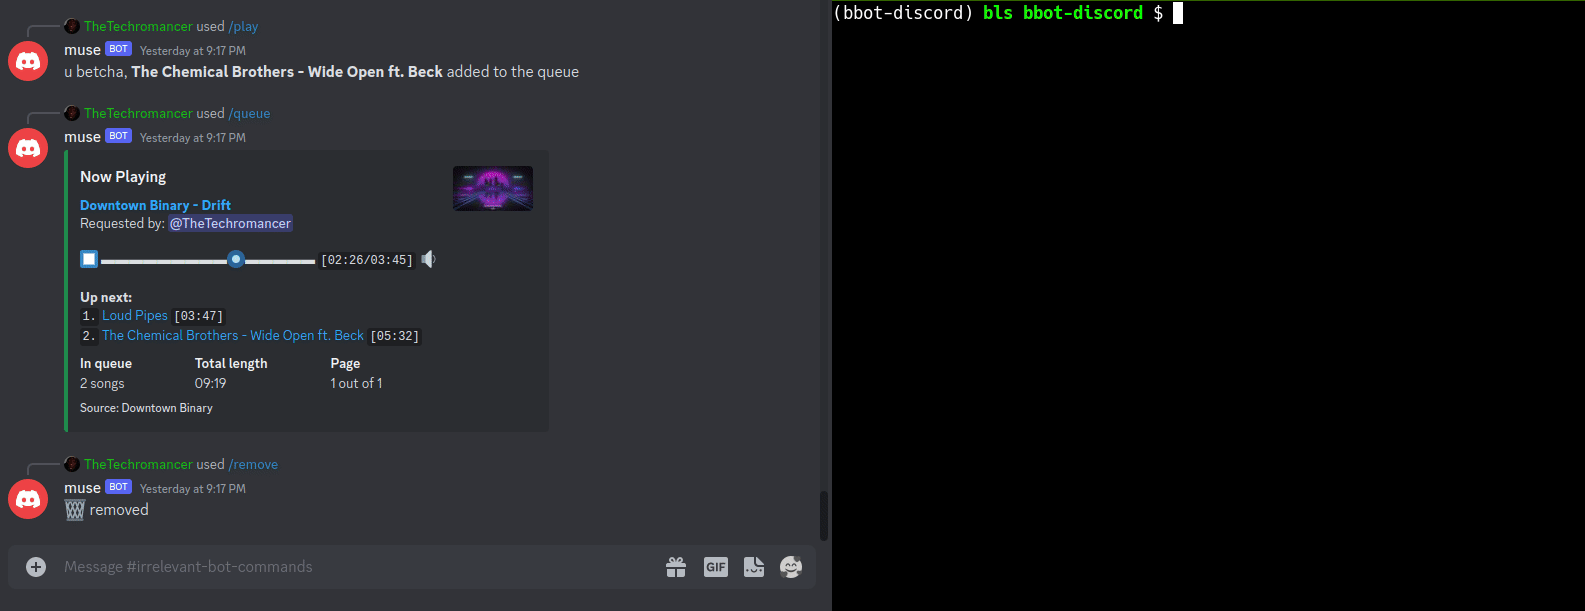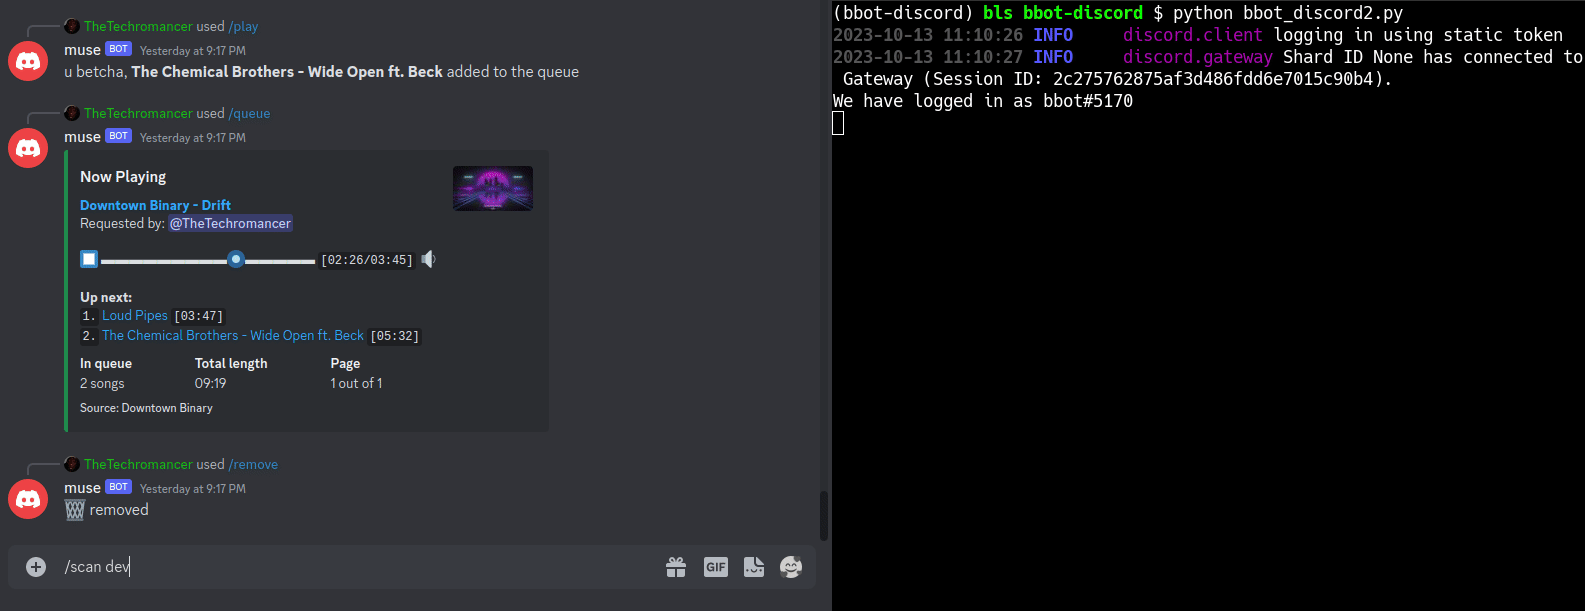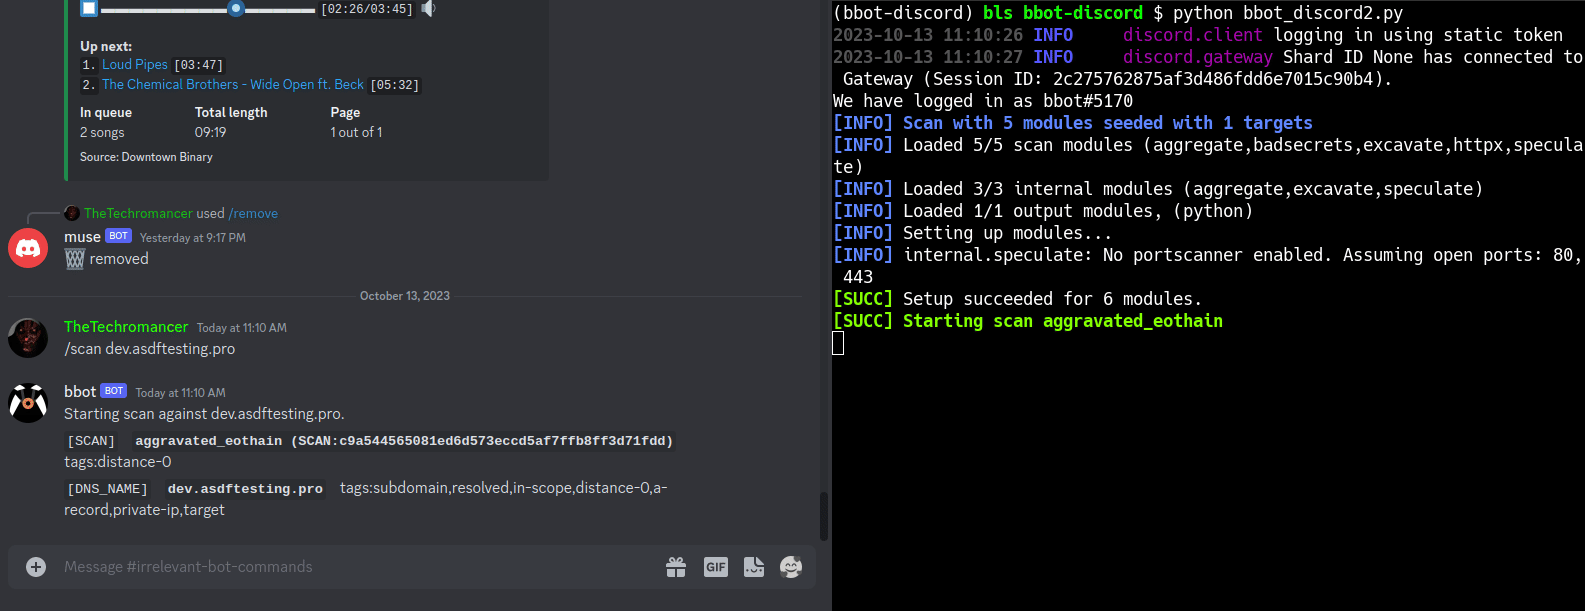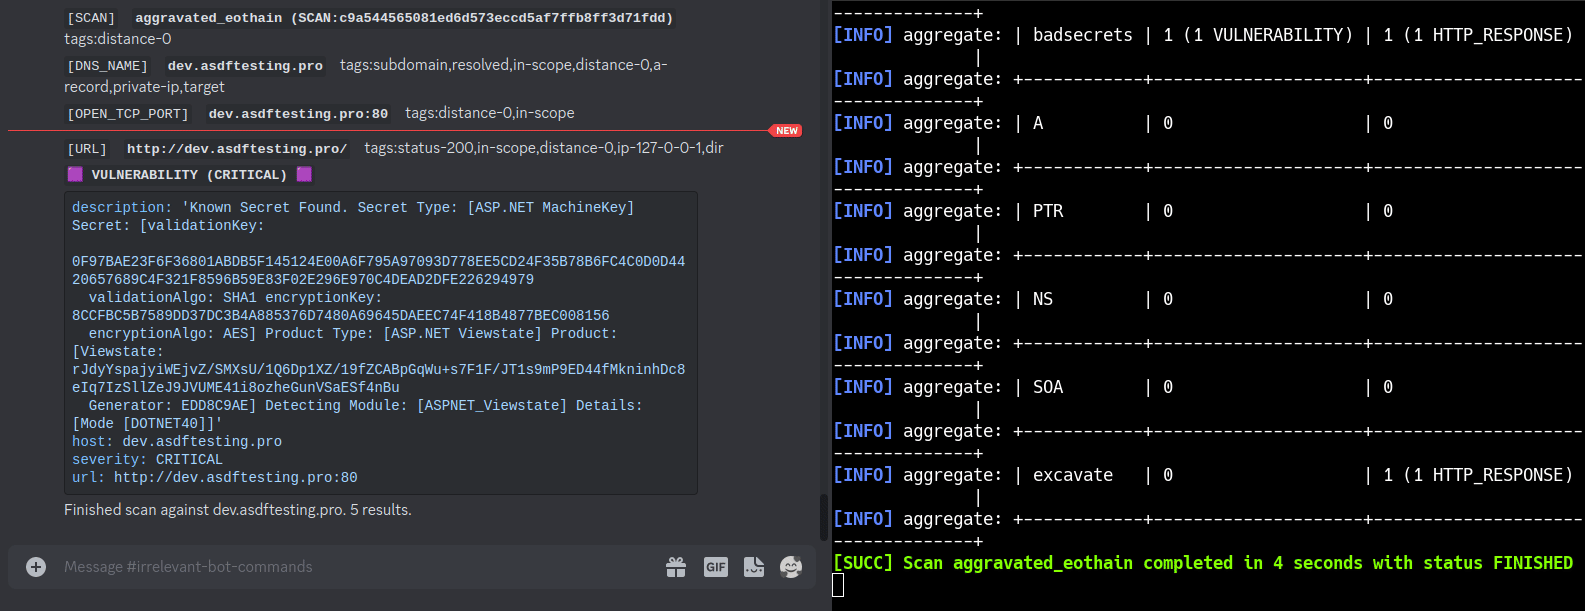 blacklanternsecurity/bbot
The recursive internet scanner for hackers. 🧡
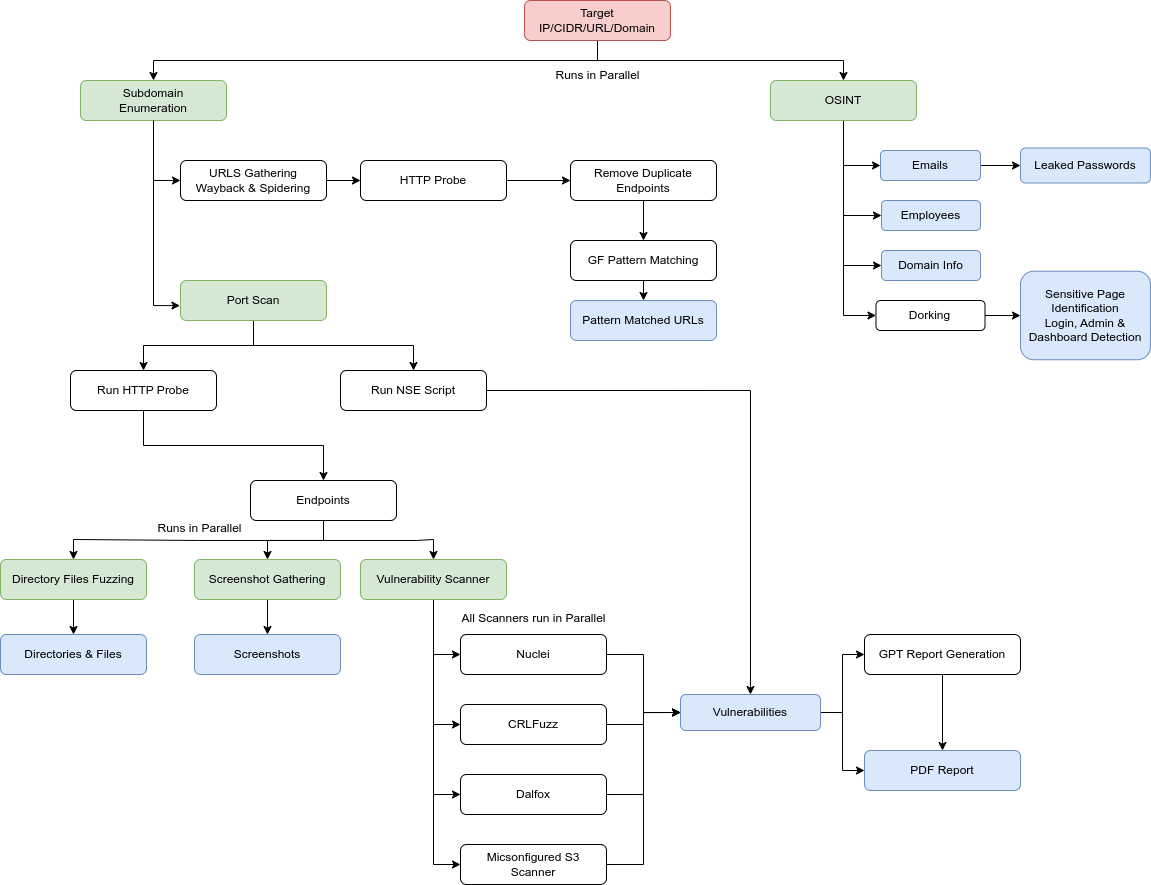 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
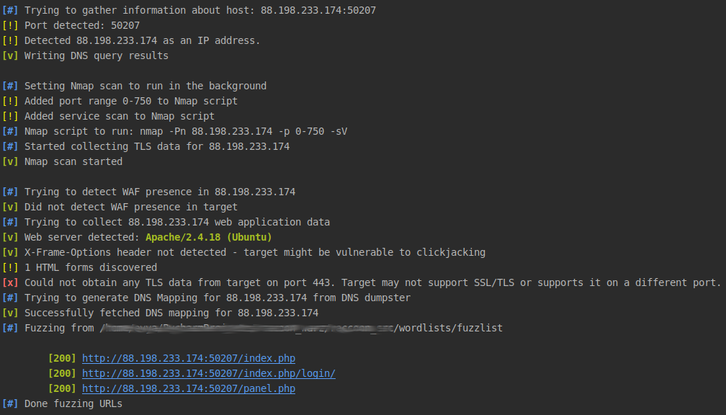 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
 skynet0x01/tugarecon
TugaRecon is an advanced subdomain reconnaissance and intelligence framework built for security researchers, penetration testers and OSINT…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
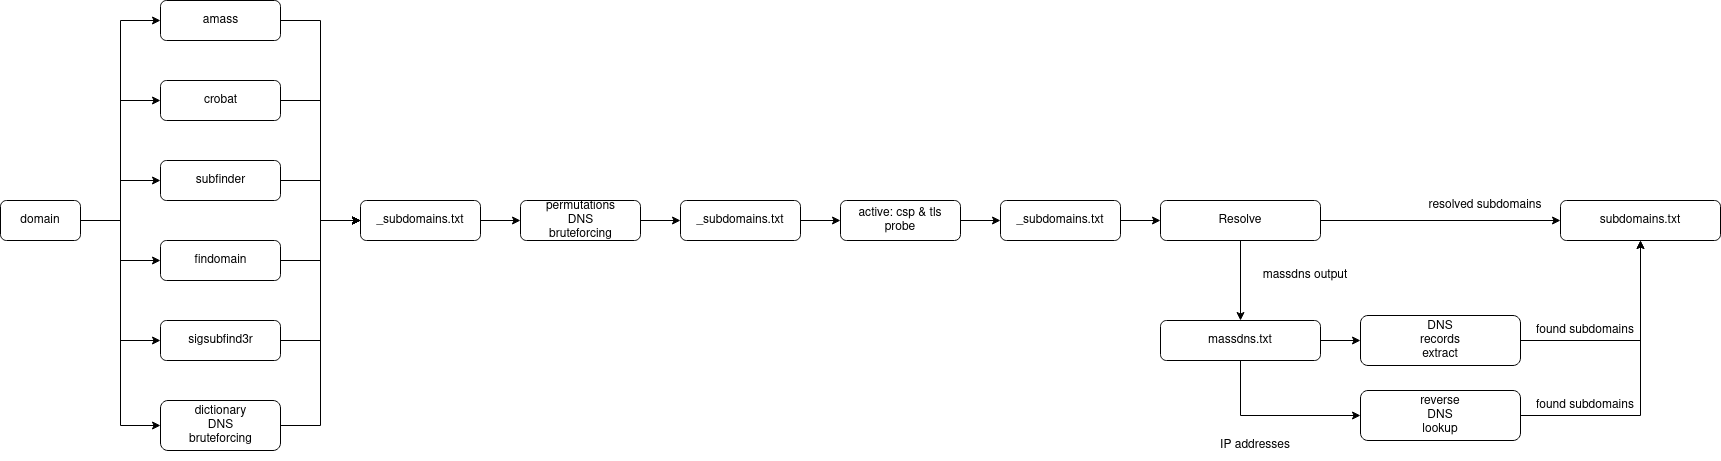 enenumxela/subdomains.sh
A wrapper around tools used for subdomain enumeration, to automate the workflow, on a given domain, written in bash.
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…