
submonitor
 xpl0ited1/submonitor
Subdomain monitor with reporting capabilities to Slack, Discord and Telegram
dns-subdomain-enumerationinformation-gatheringosint+2
143 years ago
xpl0ited1/submonitorSubdomain monitor with reporting capabilities to Slack, Discord and Telegram
 shifa123/cve-2020-13942-poc-
CVE-2020-13942 POC + Automation Script
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
 abaykan/getsubdomain
Get subdomain list and check whether they are active or not by each response code. Using API by c99.nl
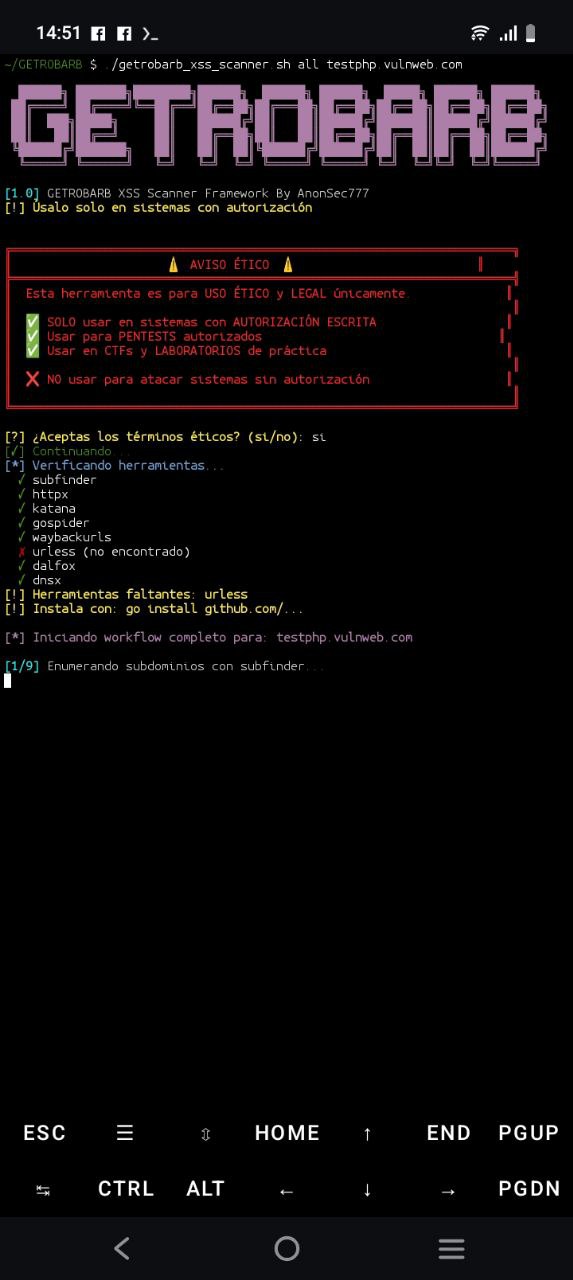 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
 cyberblackhole/domain-to-webapp
Bash script that enumerates subdomains via Subfinder, resolves IPs, and identifies live web applications hosted on a domain for reconnaissance and…
 a3h1nt/sububy
Modular subdomain enumeration suite with certificate transparency, DNS brute-force, and API-based discovery. Includes post-enumeration modules for…
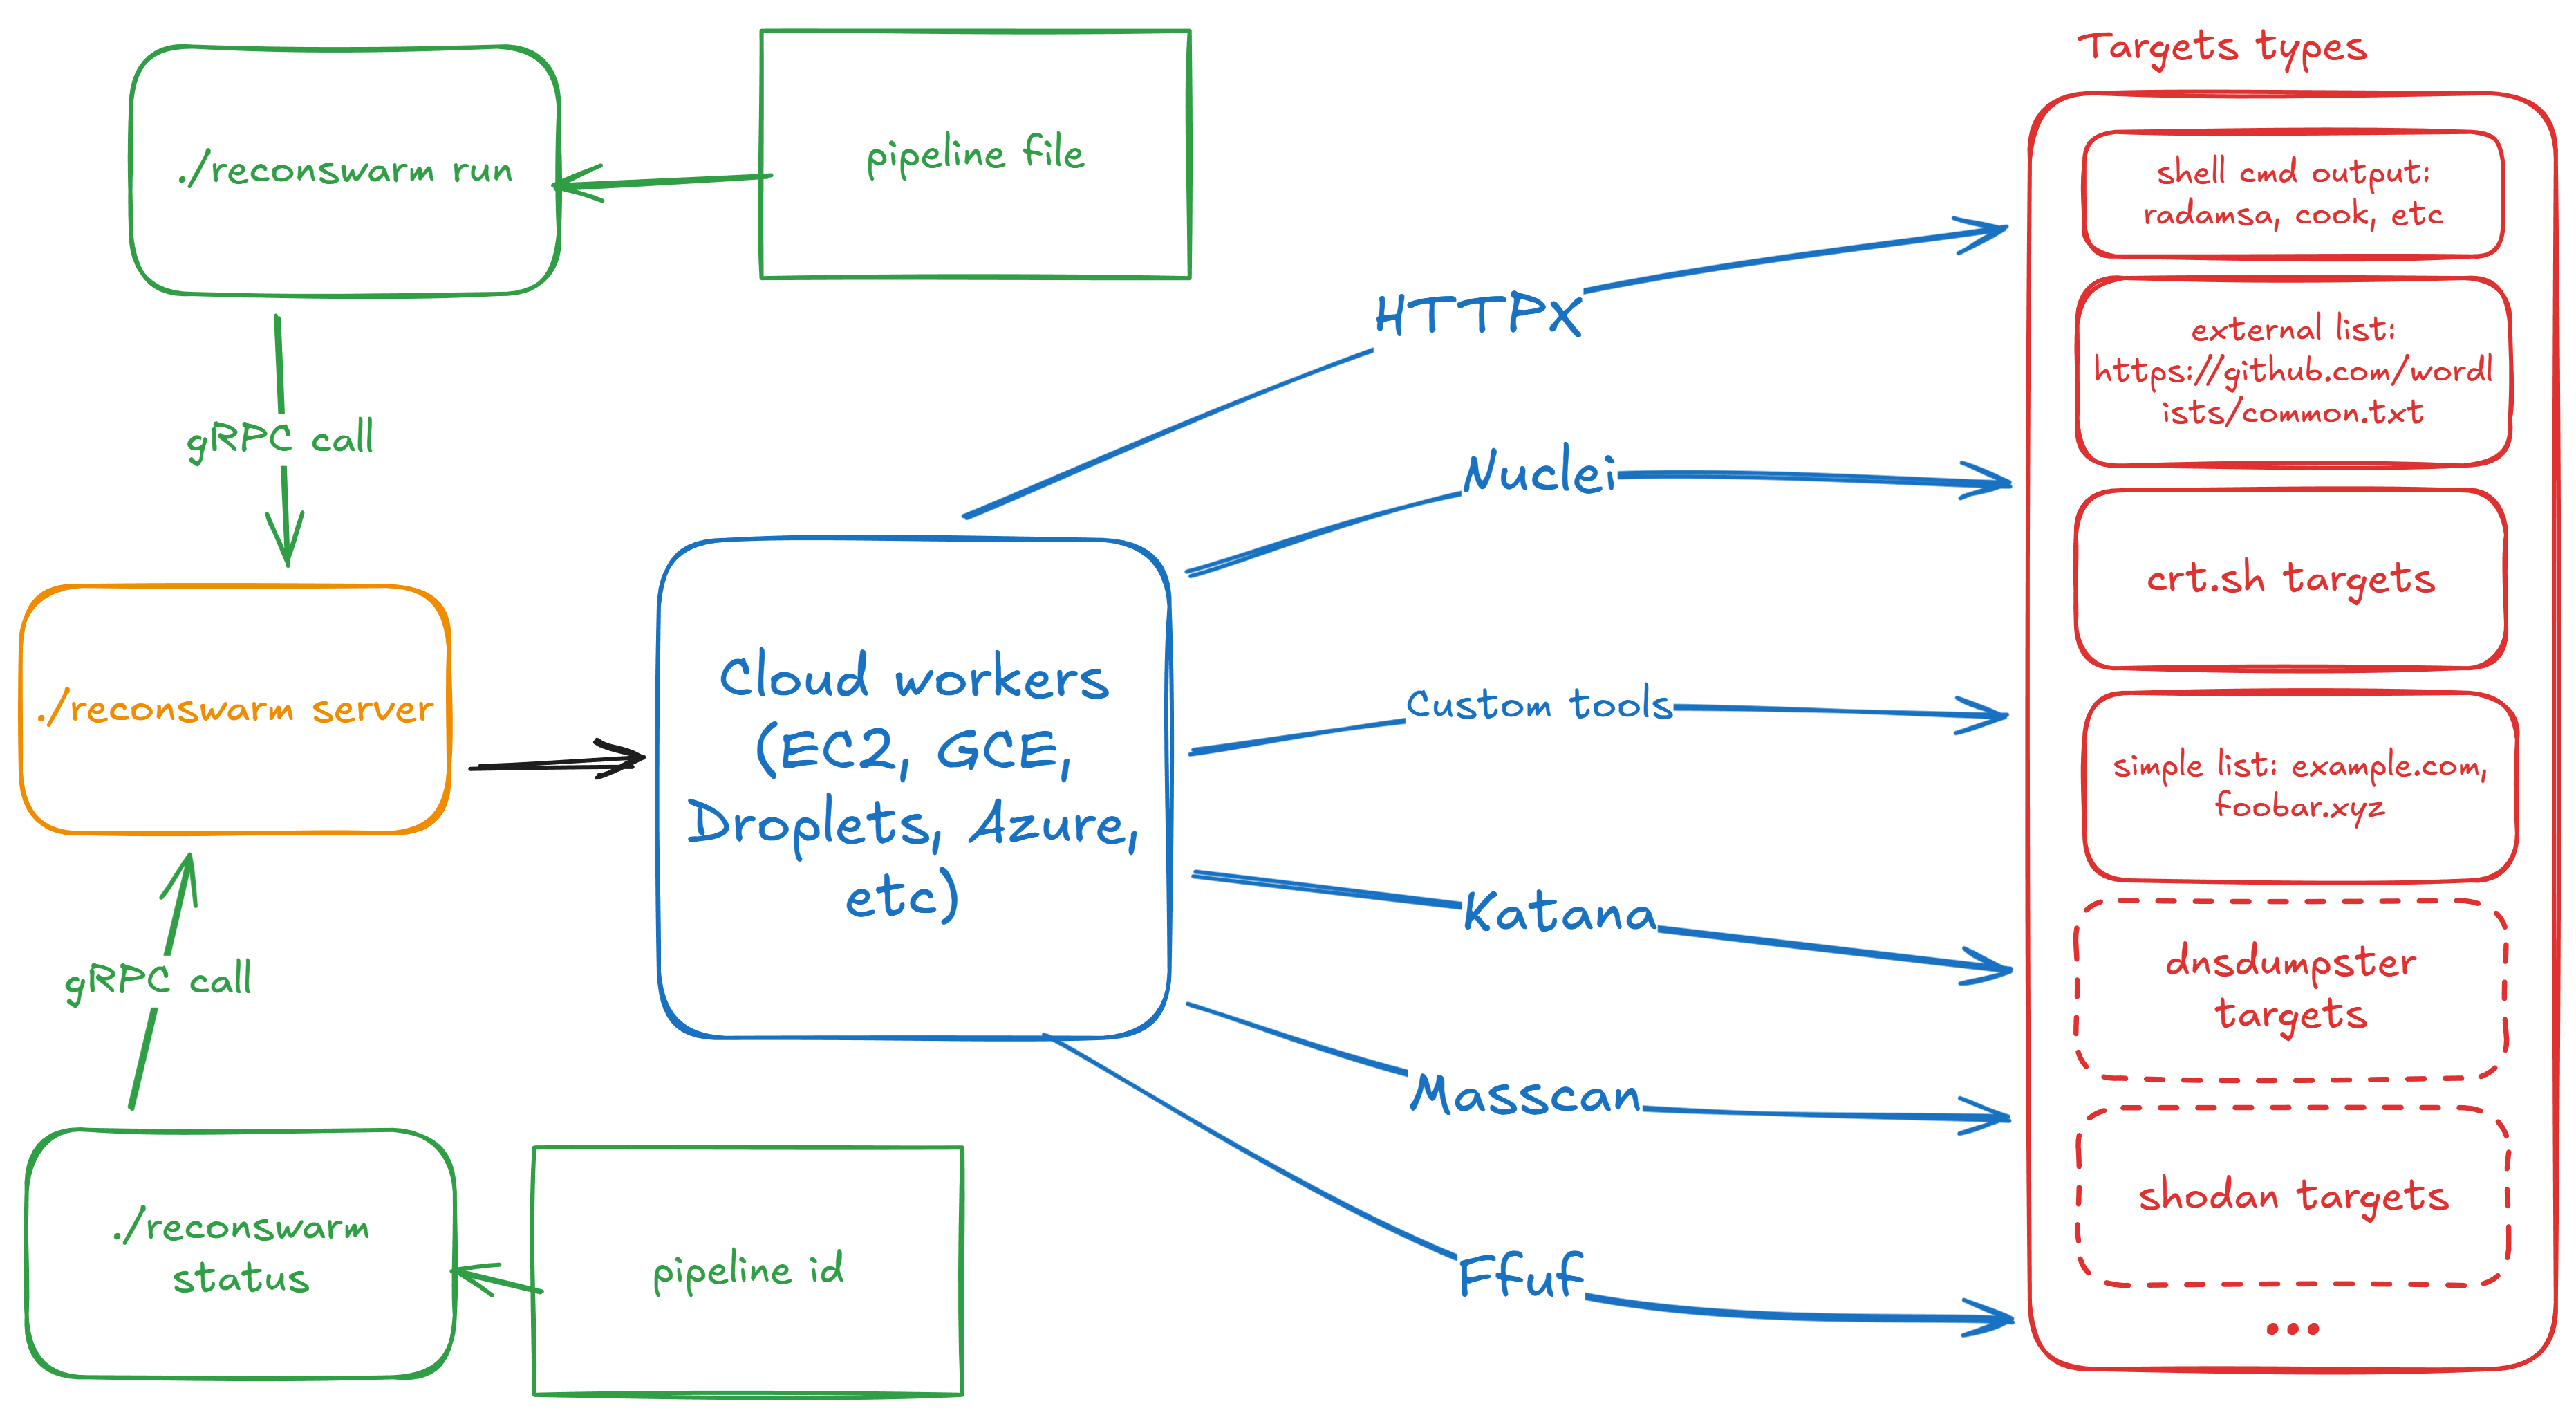 renatus-cartesius/reconswarm
Extend your recon with cloud power
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 sec-dan/wp2shell-scanner
Read-only CLI to check whether a WordPress site is exposed to WP2Shell (CVE-2026-63030 / CVE-2026-60137)
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 yashas-13/pentx-vapt-skill
Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
 k3ystr0k3r/dnsplit
Fast subdomain enumeration tool written in python.
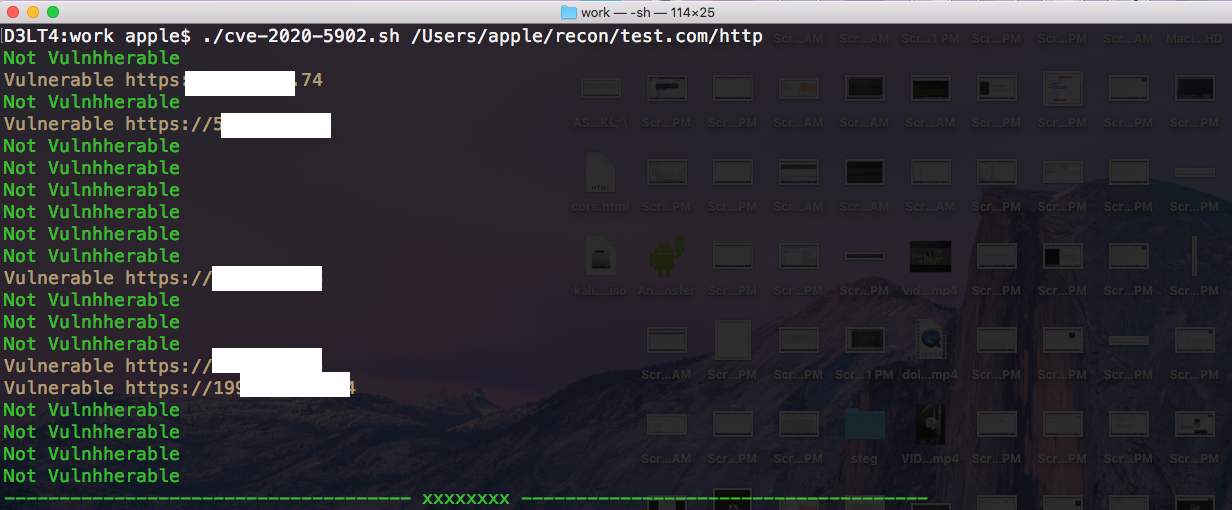 govindpalakkal/evilrip
It is a small script to fetch out the subdomains/ip vulnerable to CVE-2020-5902 written in bash
 shamo0/cve-2021-44228
log4shell (CVE-2021-44228) scanning tool
 toritoio/torito-r2s
Torito React2Shell Scanner & Exploit Tool (CVE-2025-55182 / 66478)
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.