

qyvora-anansi
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
exploitationinformation-gatheringnetwork-mapping+8
4
qyvora/qyvora-anansiTerminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.

 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
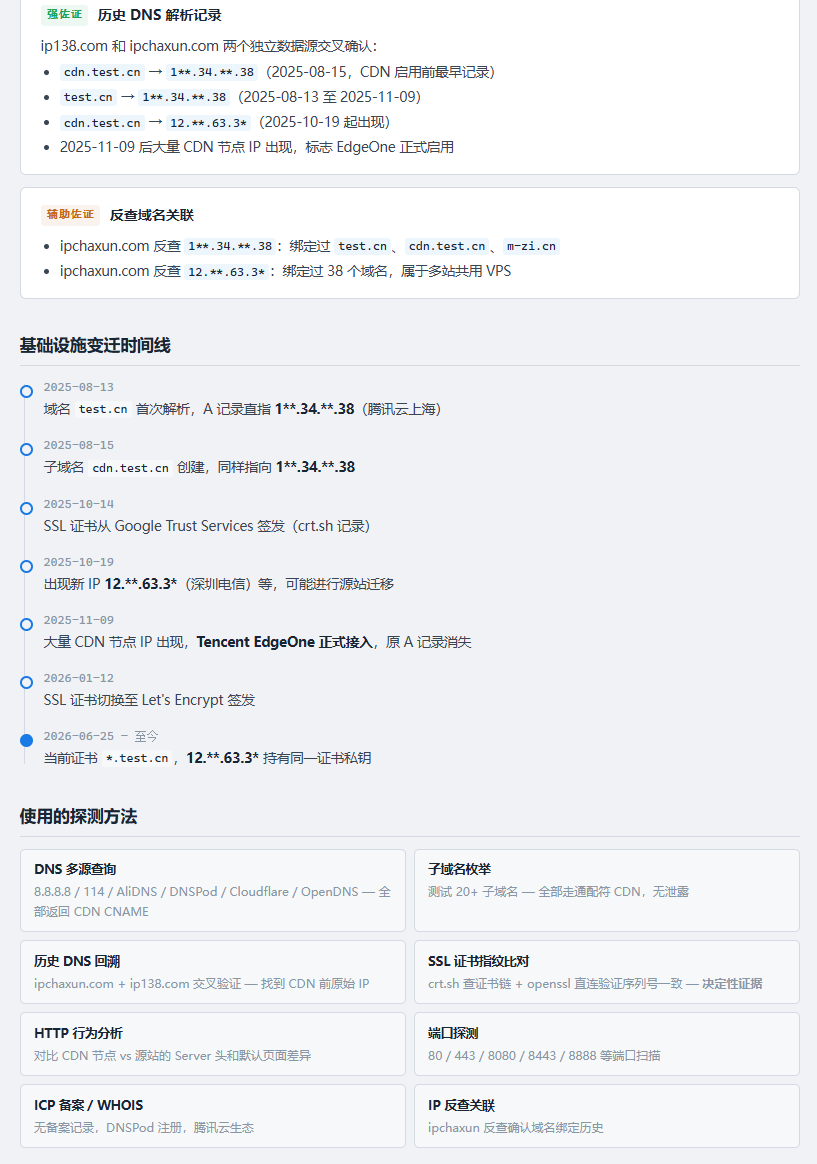 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 gmh5225/domain-enumeration-sicarius
Another tool for subdomain enumeration with some magics 🧙🏻♂️
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 sec-dan/wp2shell-scanner
Read-only CLI to check whether a WordPress site is exposed to WP2Shell (CVE-2026-63030 / CVE-2026-60137)
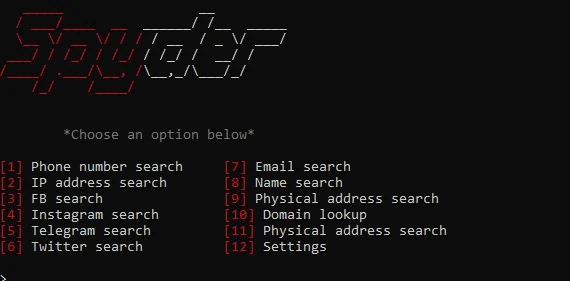 tq17oa7/spyder-osint
Open-source intelligence (OSINT) tool for gathering information from phone numbers, IP addresses, social media, emails, usernames, domains, and…
 yashas-13/pentx-vapt-skill
Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
 randomrobbiebf/subdomain-tko
Detects subdomain takeover vulnerabilities by analyzing DNS records and HTTP responses. Automatically identifies takeover-prone subdomains for…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 wattocyber/bug-bounty-library
Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…