
bug-bounty-library
 wattocyber/bug-bounty-library
Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…
curated-resourceseducationfuzzing+6
wattocyber/bug-bounty-libraryCurated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…
 nocomp/cve-2025-29927-scanner
python script for evaluate if you are vulnerable or not to next.js CVE-2025-29927
 rodney-o-c-melby/dns-zone-transfer-test
Automates Domain Name System (DNS) zone transfer testing. Checks for CVE-1999-0532 by automatically finding a given domains nameservers, and tests…
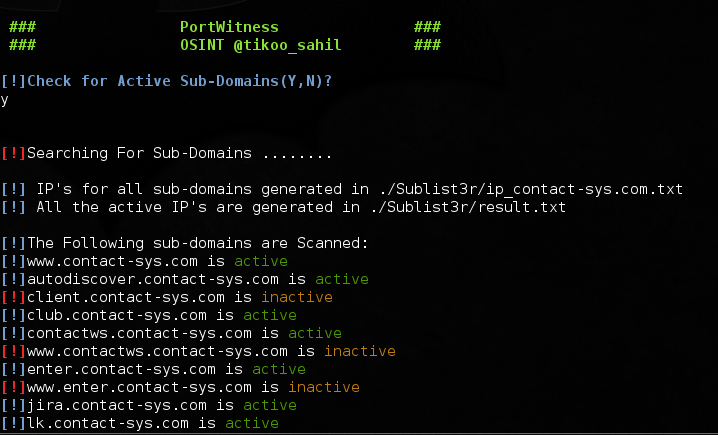 viperbluff/portwitness
Tool for checking Whether a domain or its multiple sub-domains are up and running.
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 kingofbugbounty/kingofbugbountytips
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…
 ascr0b/pcwt
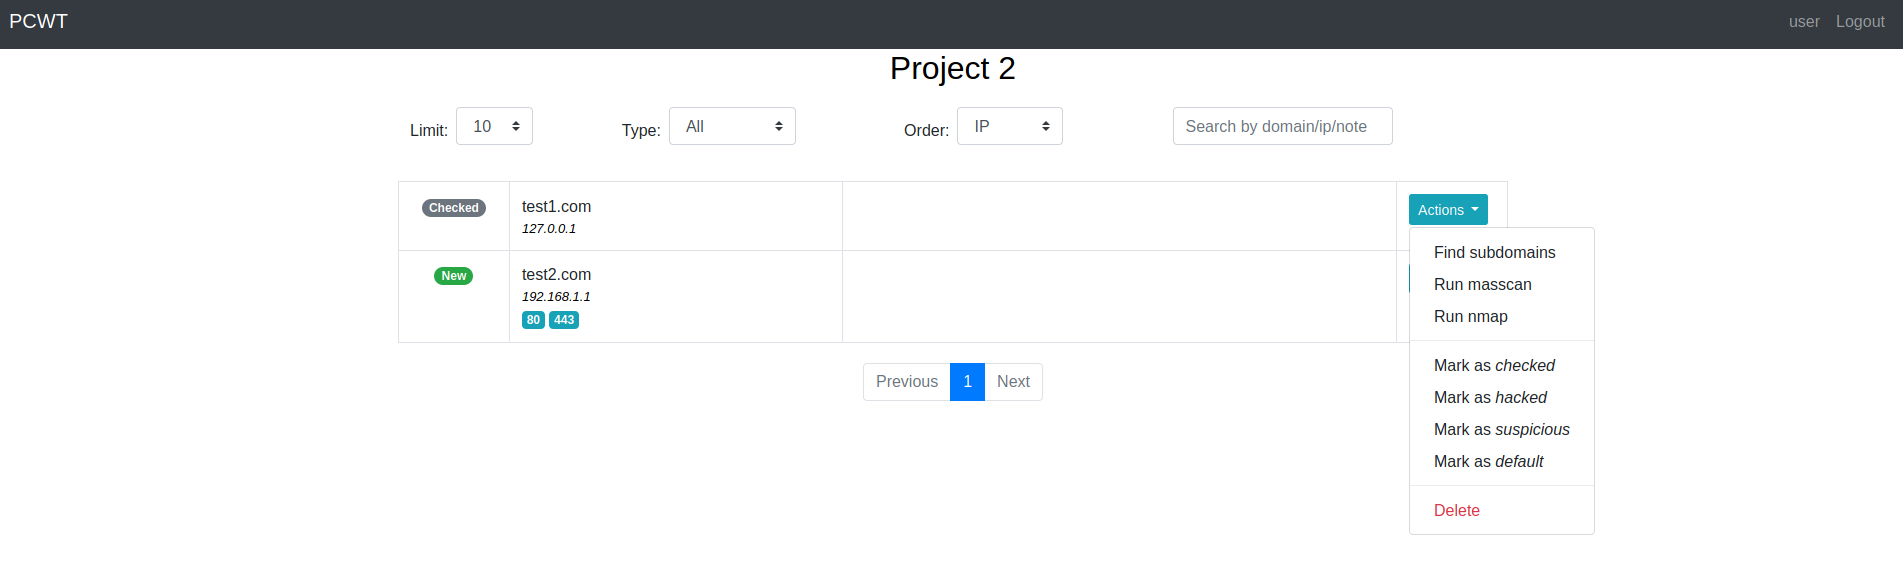
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 bitthebyte/monitorizer
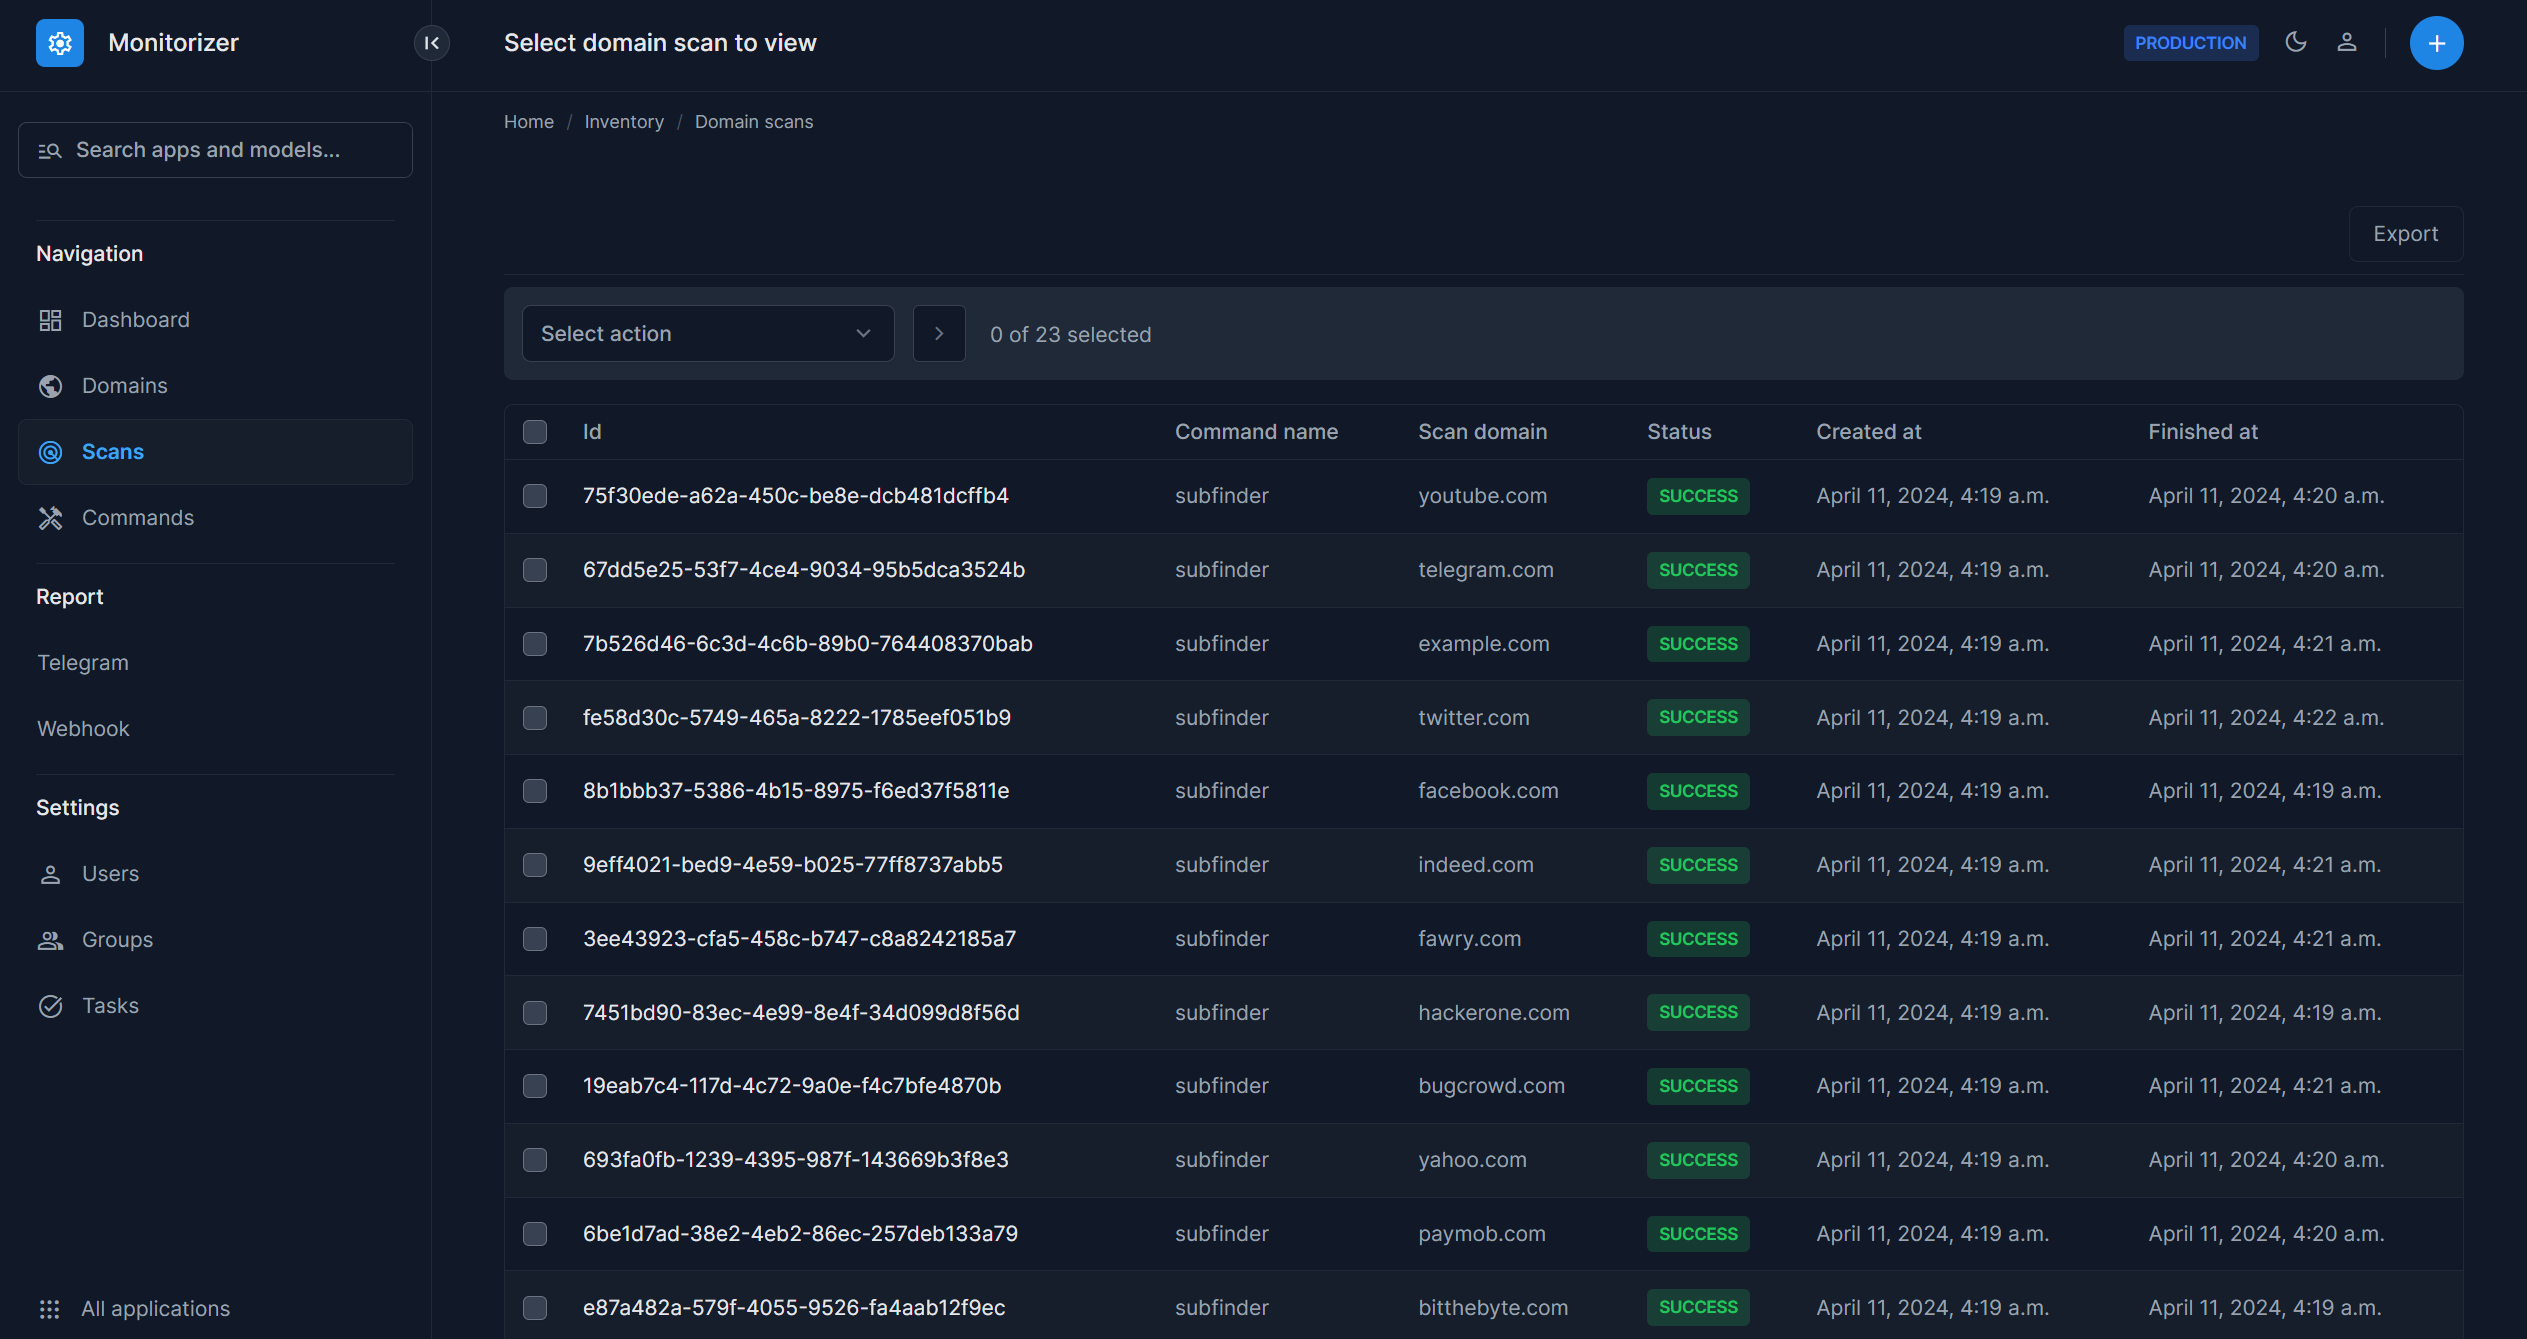
Monitoring framework to detect and report newly found subdomains on a specific target using various scanning tools
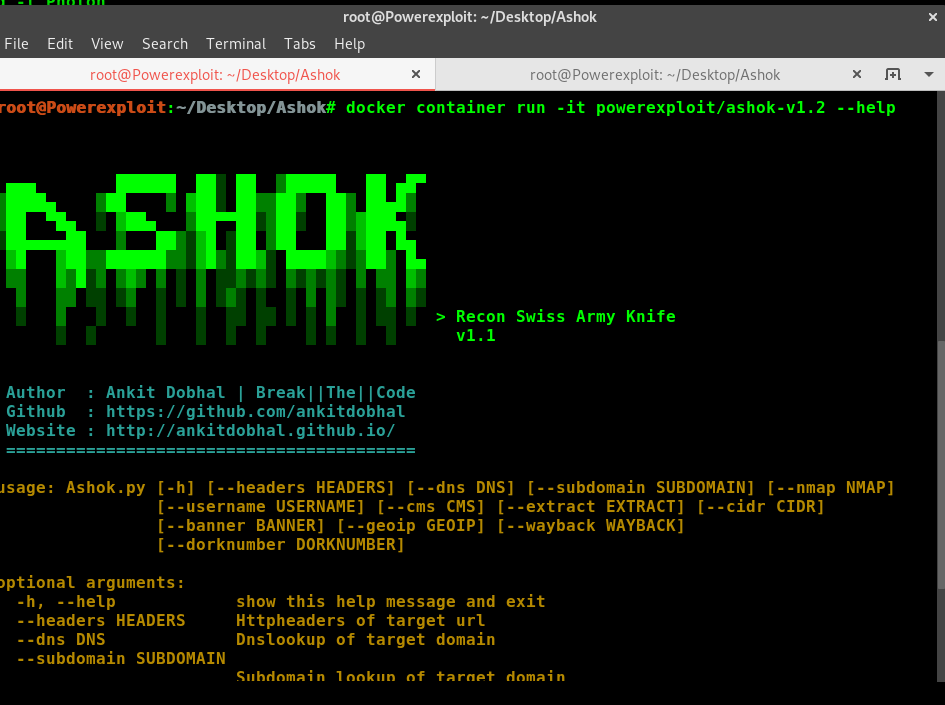 powerexploit/ashok
Ashok is a OSINT Recon Tool , a.k.a 😍 Swiss Army knife .
 abaykan/getsubdomain
Get subdomain list and check whether they are active or not by each response code. Using API by c99.nl
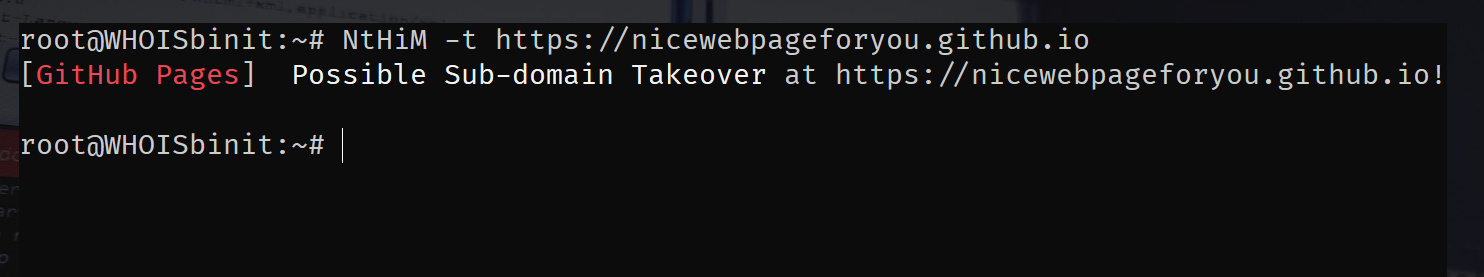 thebinitghimire/nthim
Now, the Host is Mine! - Super Fast Sub-domain Takeover Detection!