
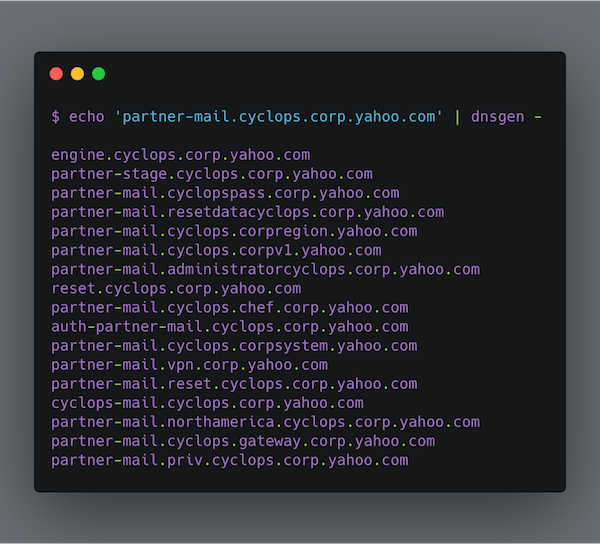
dnsgen
 alephnullsk/dnsgen
Generates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…
dns-analysisdns-fuzzingdns-subdomain-enumeration+5
1.1k
alephnullsk/dnsgenGenerates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…
 netspi/ateam
Python reconnaissance tool for discovering Azure services and attributing tenant ownership via DNS validation, multi-service probing, and response…
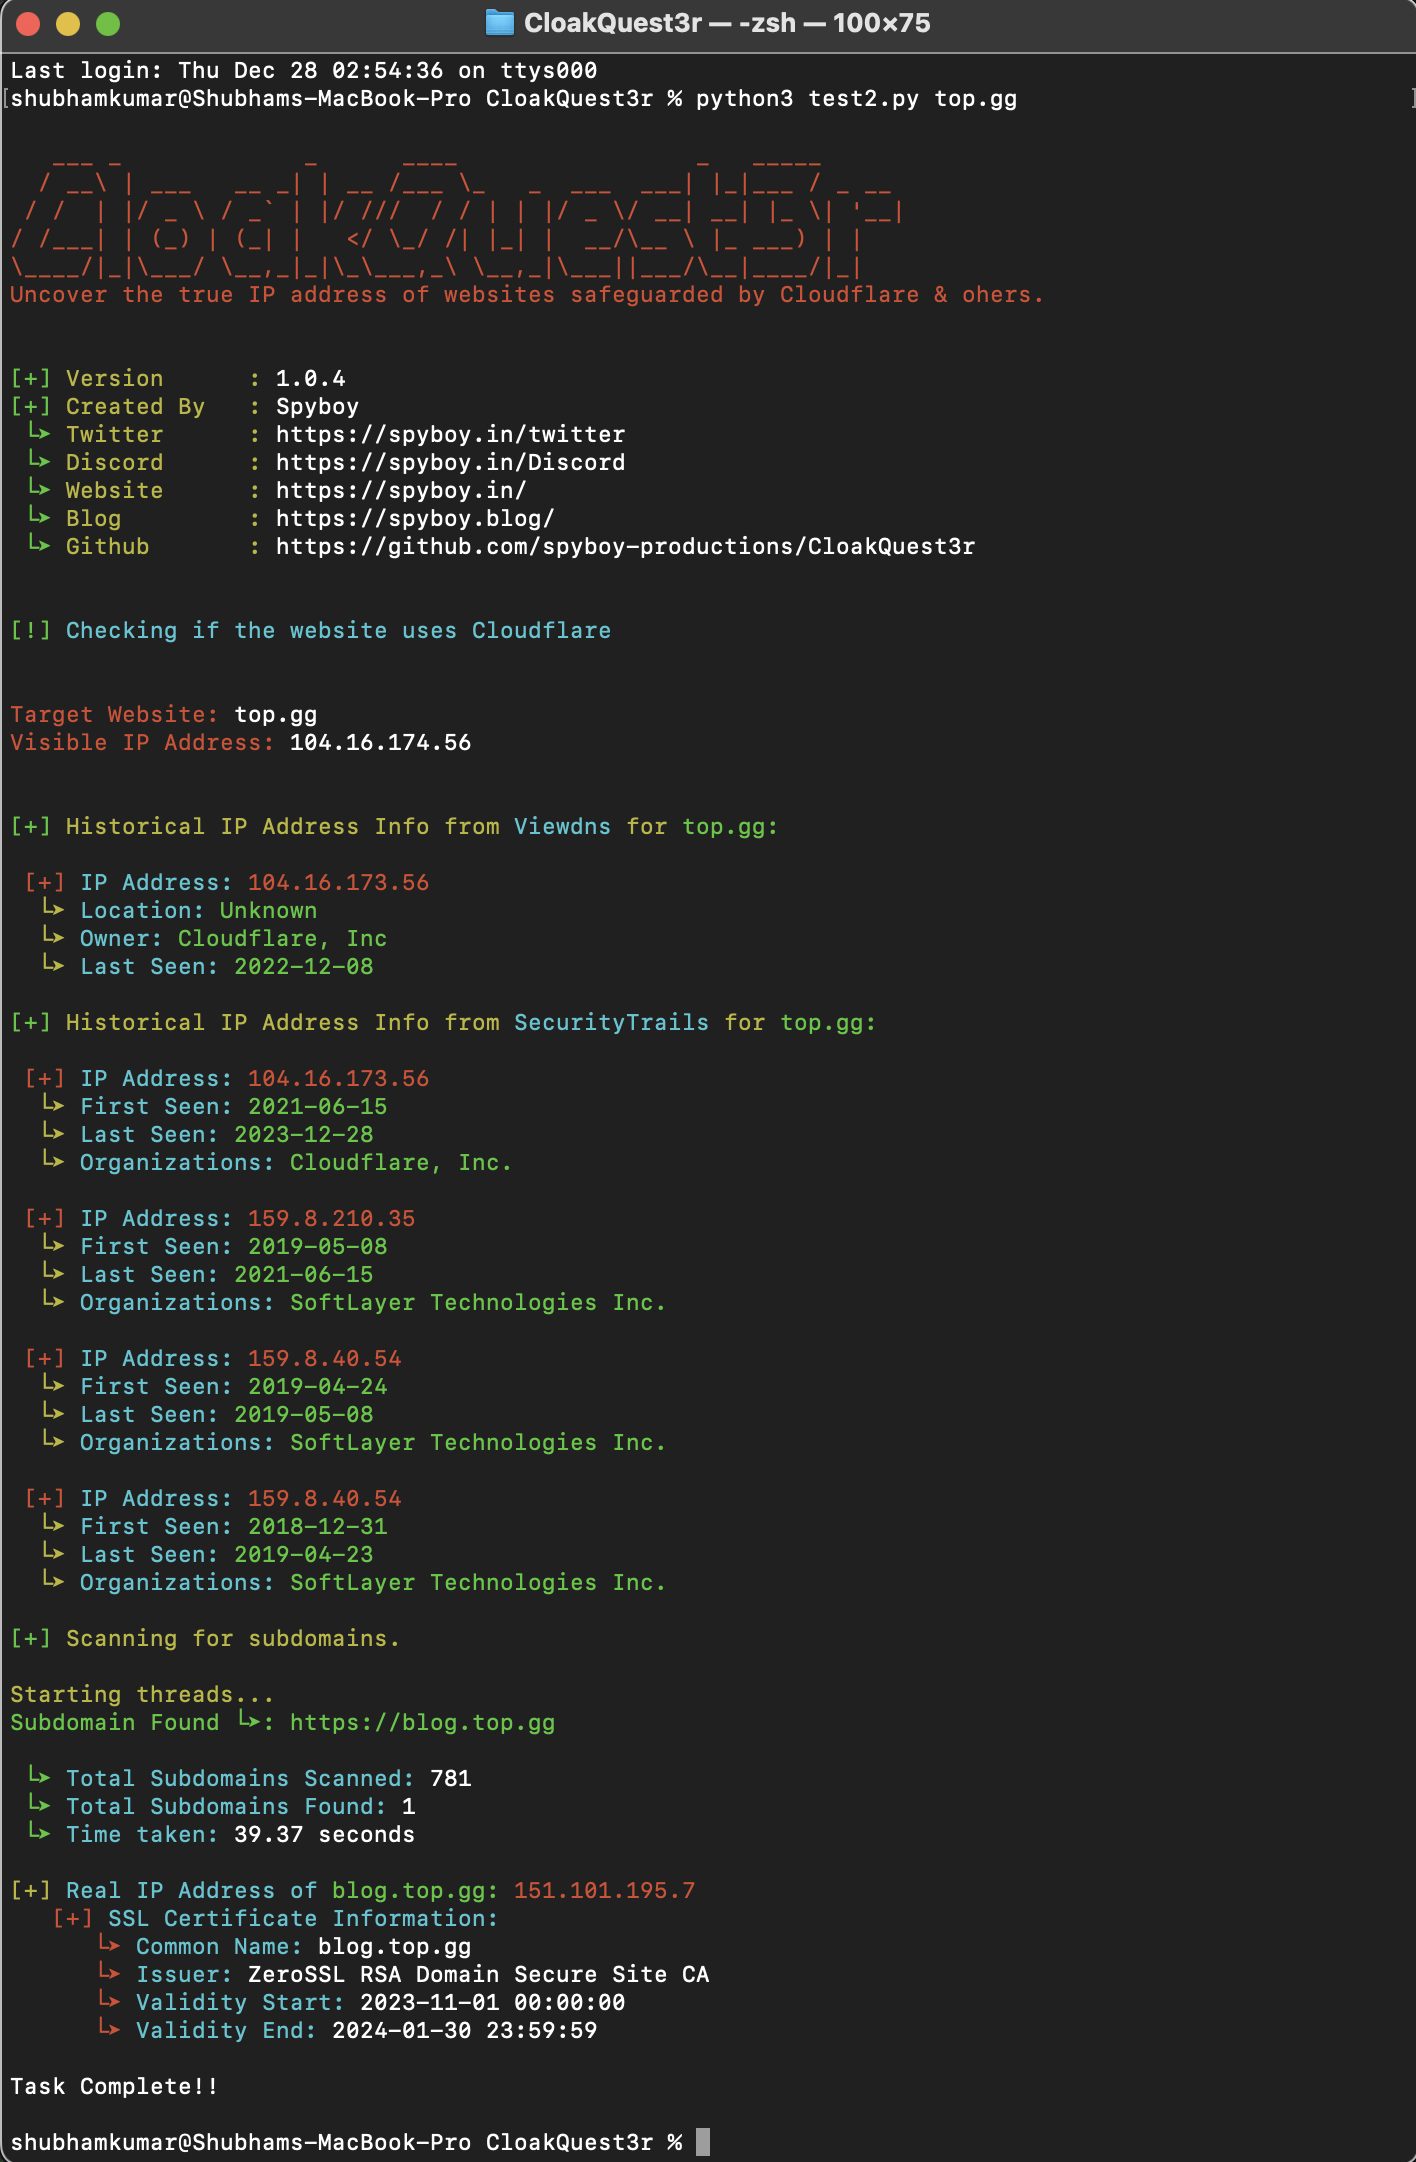 spyboy-productions/cloakquest3r
Open-source security research tool for identifying origin IP exposure of websites protected by Cloudflare and similar reverse proxy services.
 chrismaddalena/odin
Automated network asset, email, and social media profile discovery and cataloguing.
 nahamsec/hostilesubbruteforcer
Subdomain brute-forcing tool that enumerates existing subdomains and detects misconfigured cloud-hosted subdomains vulnerable to takeover across AWS,…
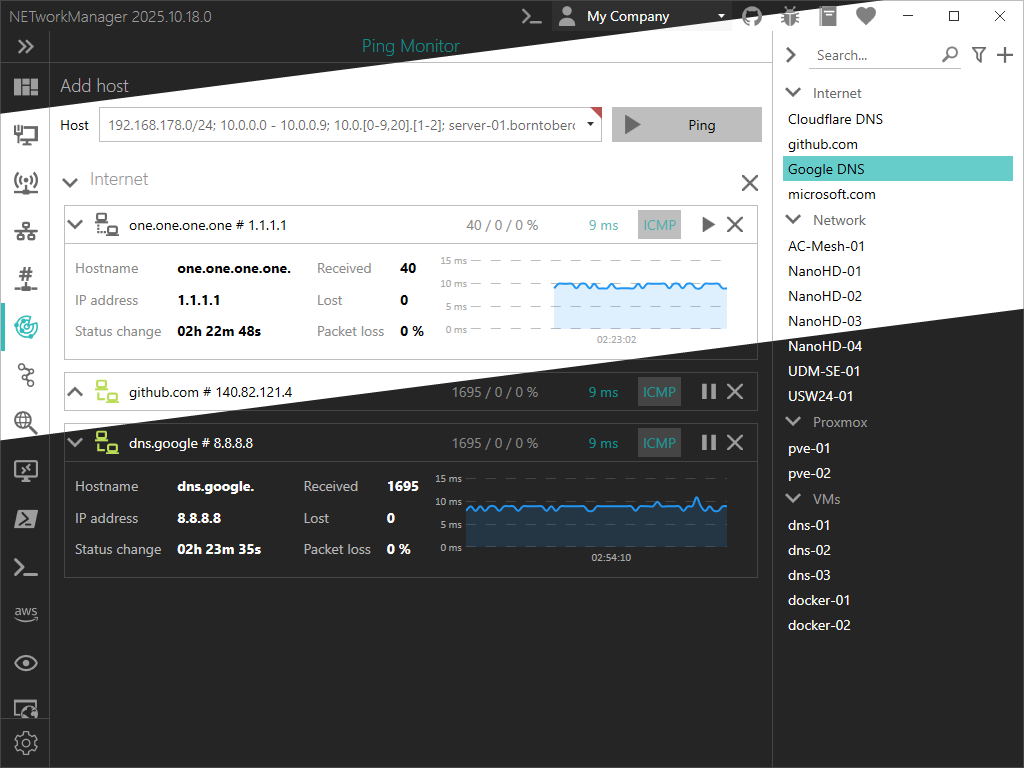 borntoberoot/networkmanager
A powerful open-source tool for managing networks and troubleshooting network problems!
 smiegles/mass3
Multi-threaded DNS-based enumeration tool for discovering AWS S3 buckets using pre-compiled wordlists and custom DNS resolvers, with optional Docker…
 rotemreiss/robusto
Robust Subdomain Takeover Tool
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 anshumanbh/tko-subs
A tool that can help detect and takeover subdomains with dead DNS records
 pwnesia/dnstake
Fast DNS takeover scanner that checks for missing hosted zones by querying nameservers and fingerprinting providers to identify vulnerable subdomains.
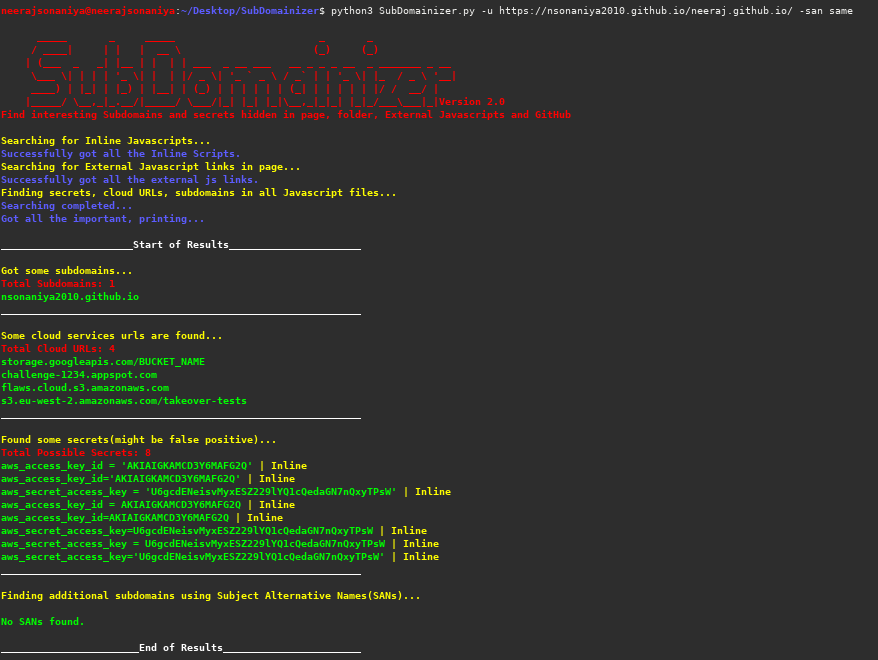 nsonaniya2010/subdomainizer
A tool to find subdomains and interesting things hidden inside, external Javascript files of page, folder, and Github.
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 yuyudhn/azsubenum
DNS-based subdomain enumeration tool for Azure services, probing App Services, Storage Accounts, Databases, Key Vaults, and CDN endpoints via…
 g0ldencybersec/easyeasm
Zero-dollar attack surface management tool
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…