
pentx-vapt-skill
 yashas-13/pentx-vapt-skill
Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
exploitationinformation-gatheringpenetration-testing+6
2
yashas-13/pentx-vapt-skillOpen-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 k8gege/ladon
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32…
 sec-dan/cve-2025-53770-scanner
A Python-based reconnaissance scanner for safely identifying potential exposure to SharePoint vulnerability CVE-2025-53770.
 wddadk/offensive-osint-tools
Curated list of OSINT tools for offensive security, covering email harvesting, subdomain enumeration, threat intelligence, and social engineering for…
 franccesco/getaltname
Extract subdomains from SSL certificates in HTTPS sites.
 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…
 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。
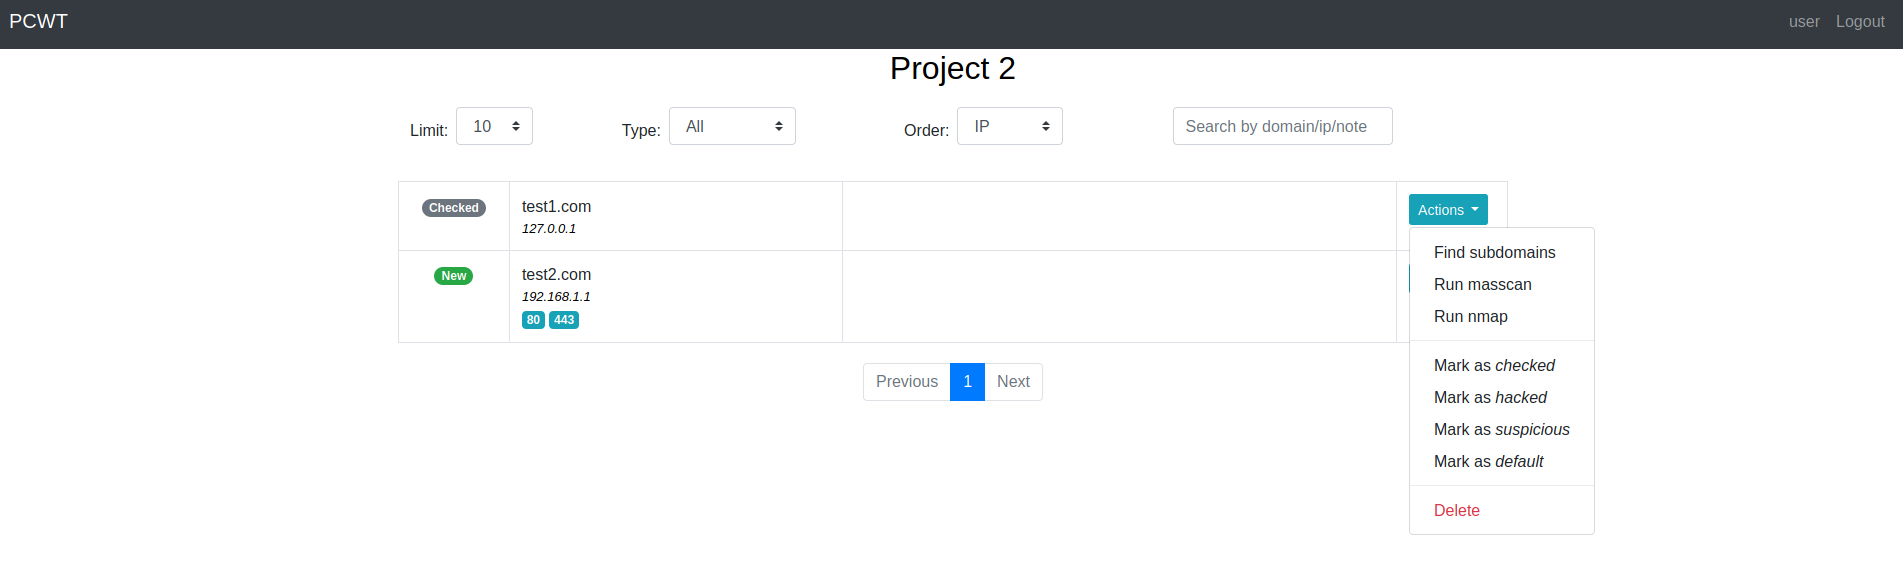 ascr0b/pcwt
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
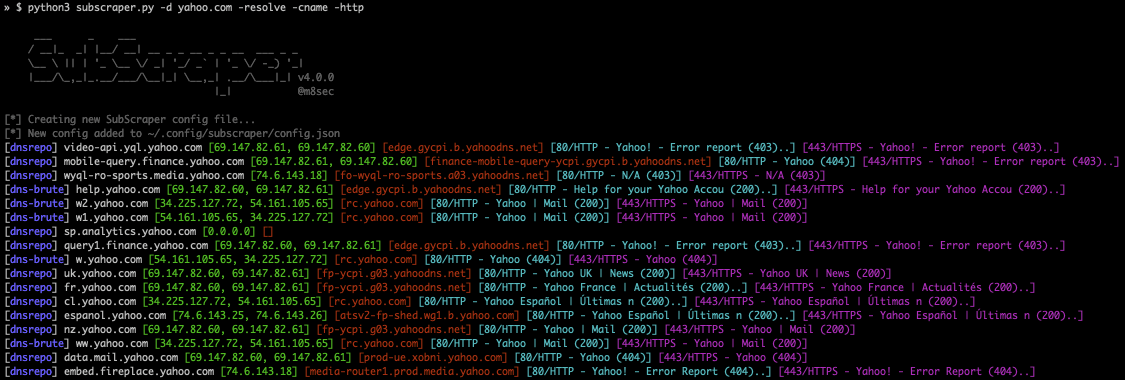 m8sec/subscraper
Subdomain and target enumeration tool built for offensive security testing
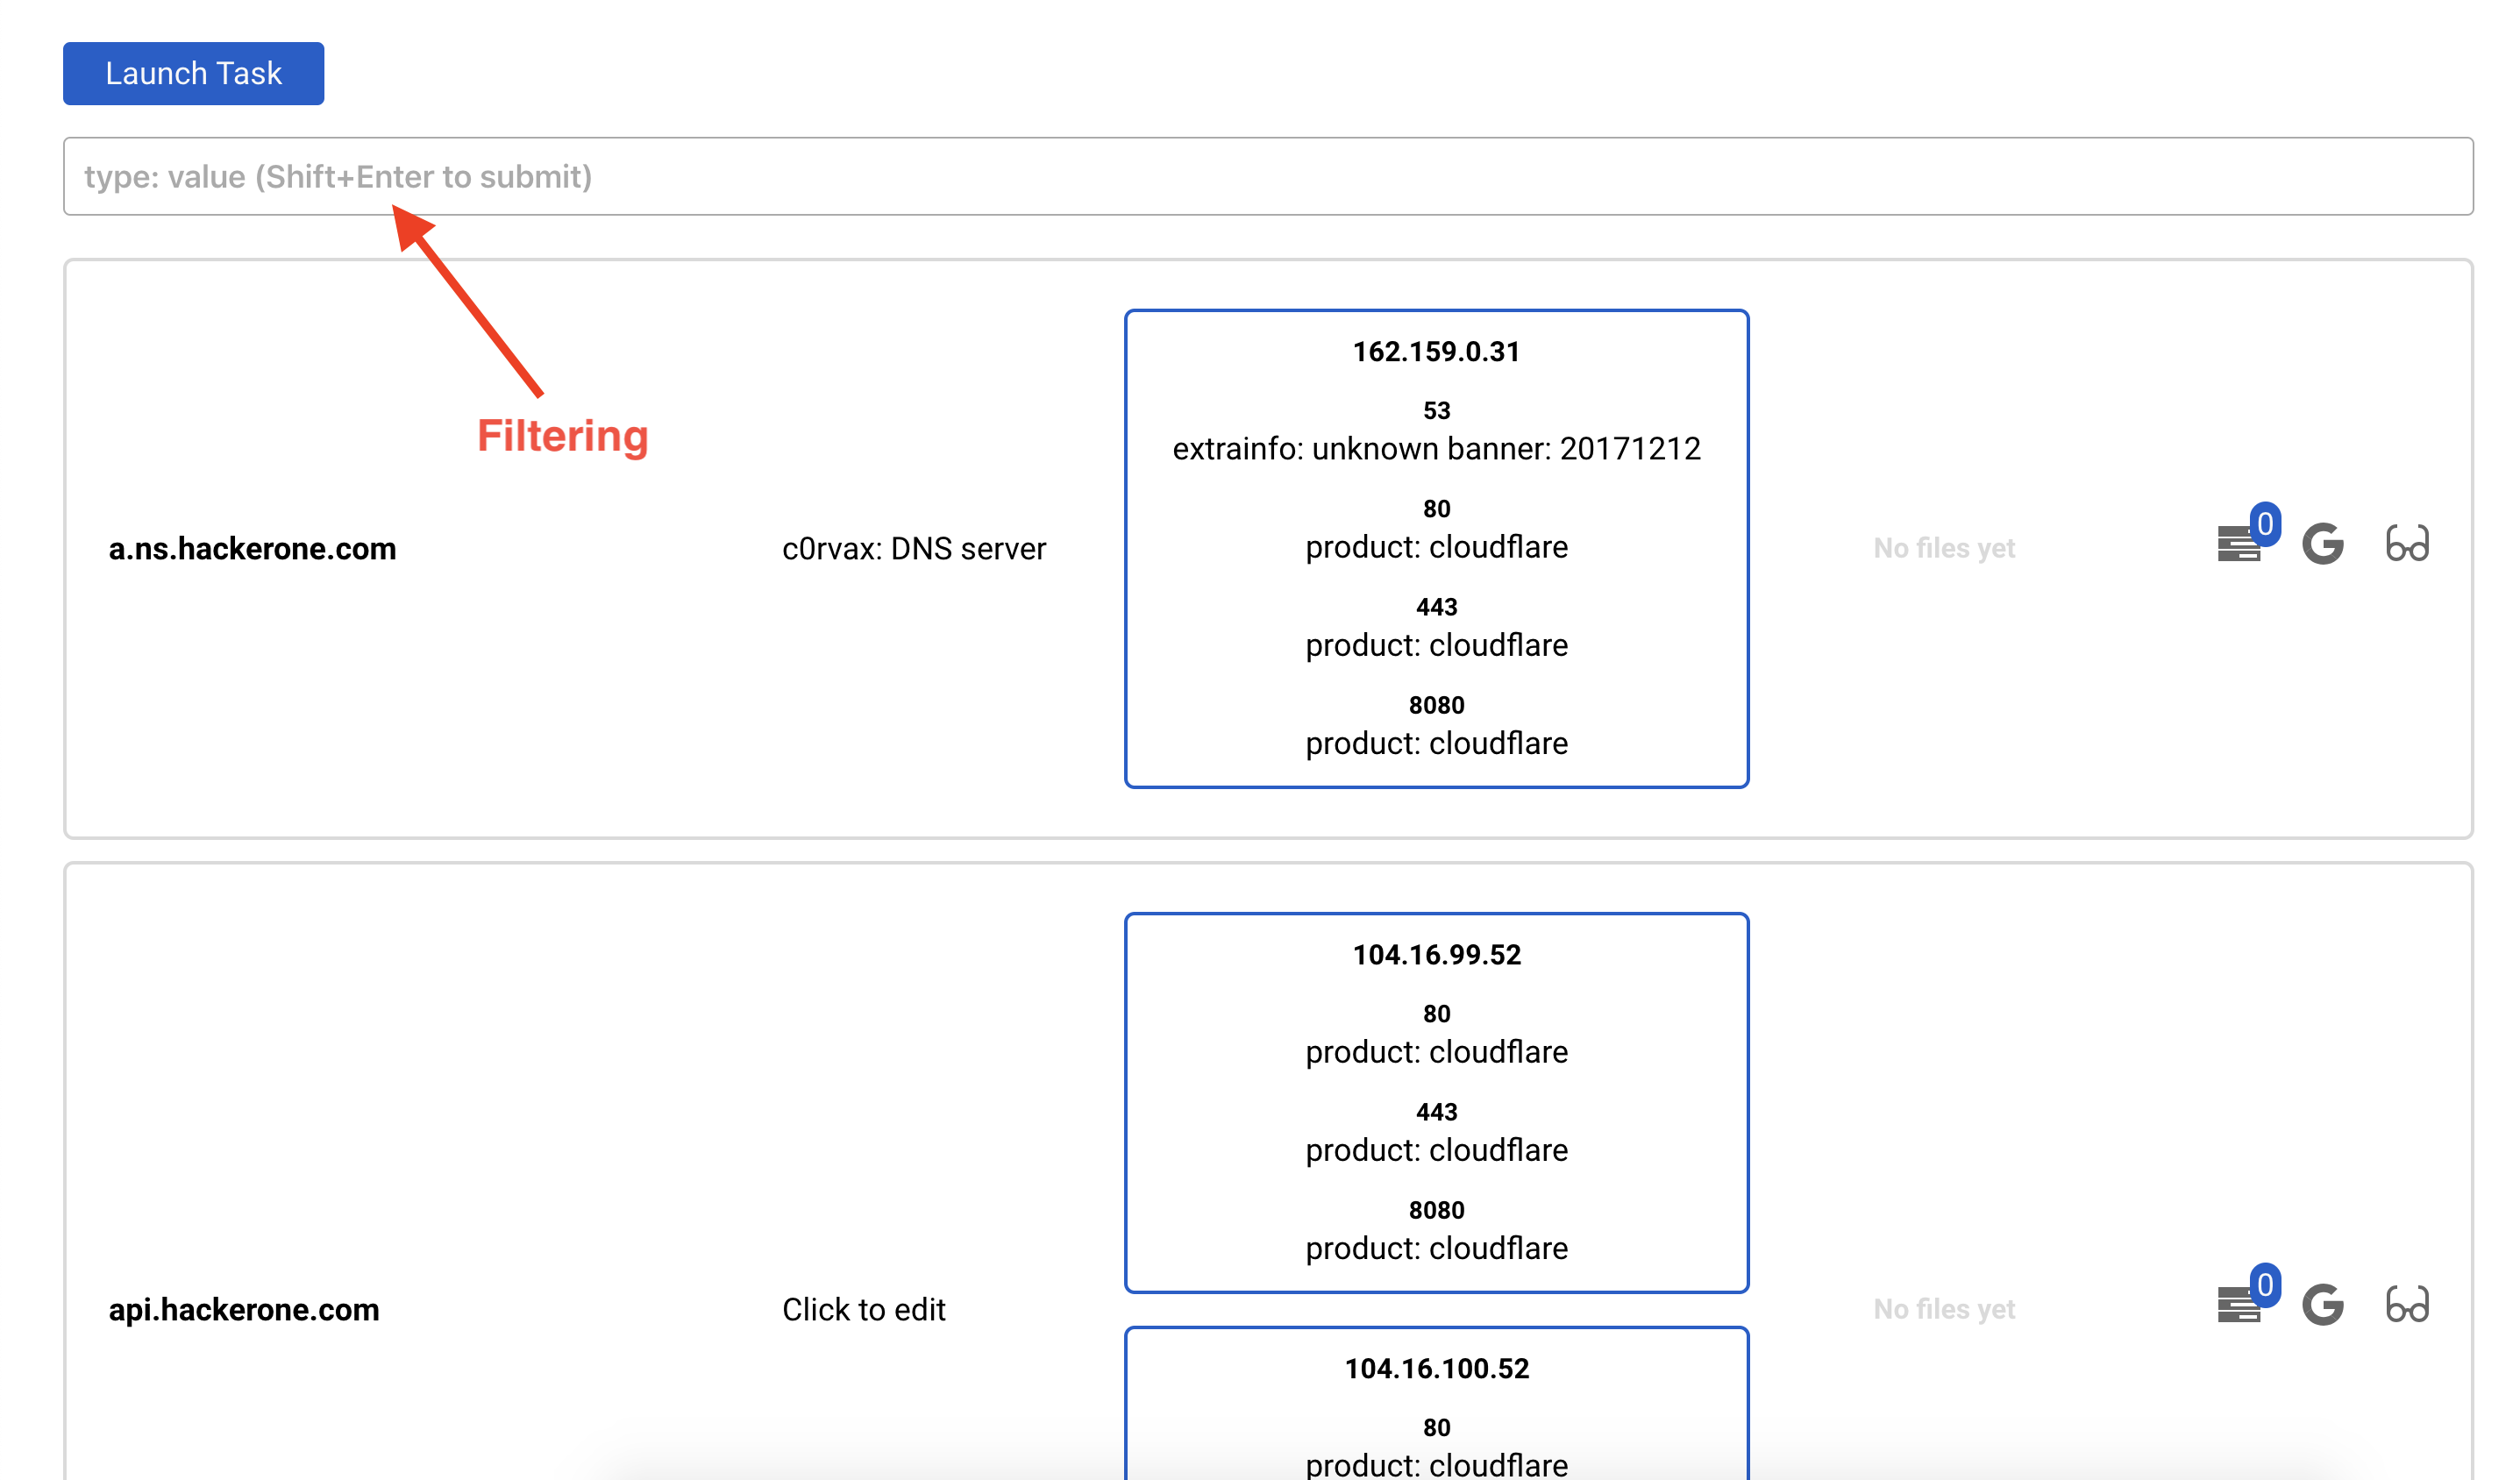 c0rv4x/project-black
Pentest/BugBounty progress control with scanning modules
 j3ers3/searpy
🥀 Search Engine Tookit,URL采集、Favicon哈希值查找真实IP、子域名查找
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…