

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.9k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
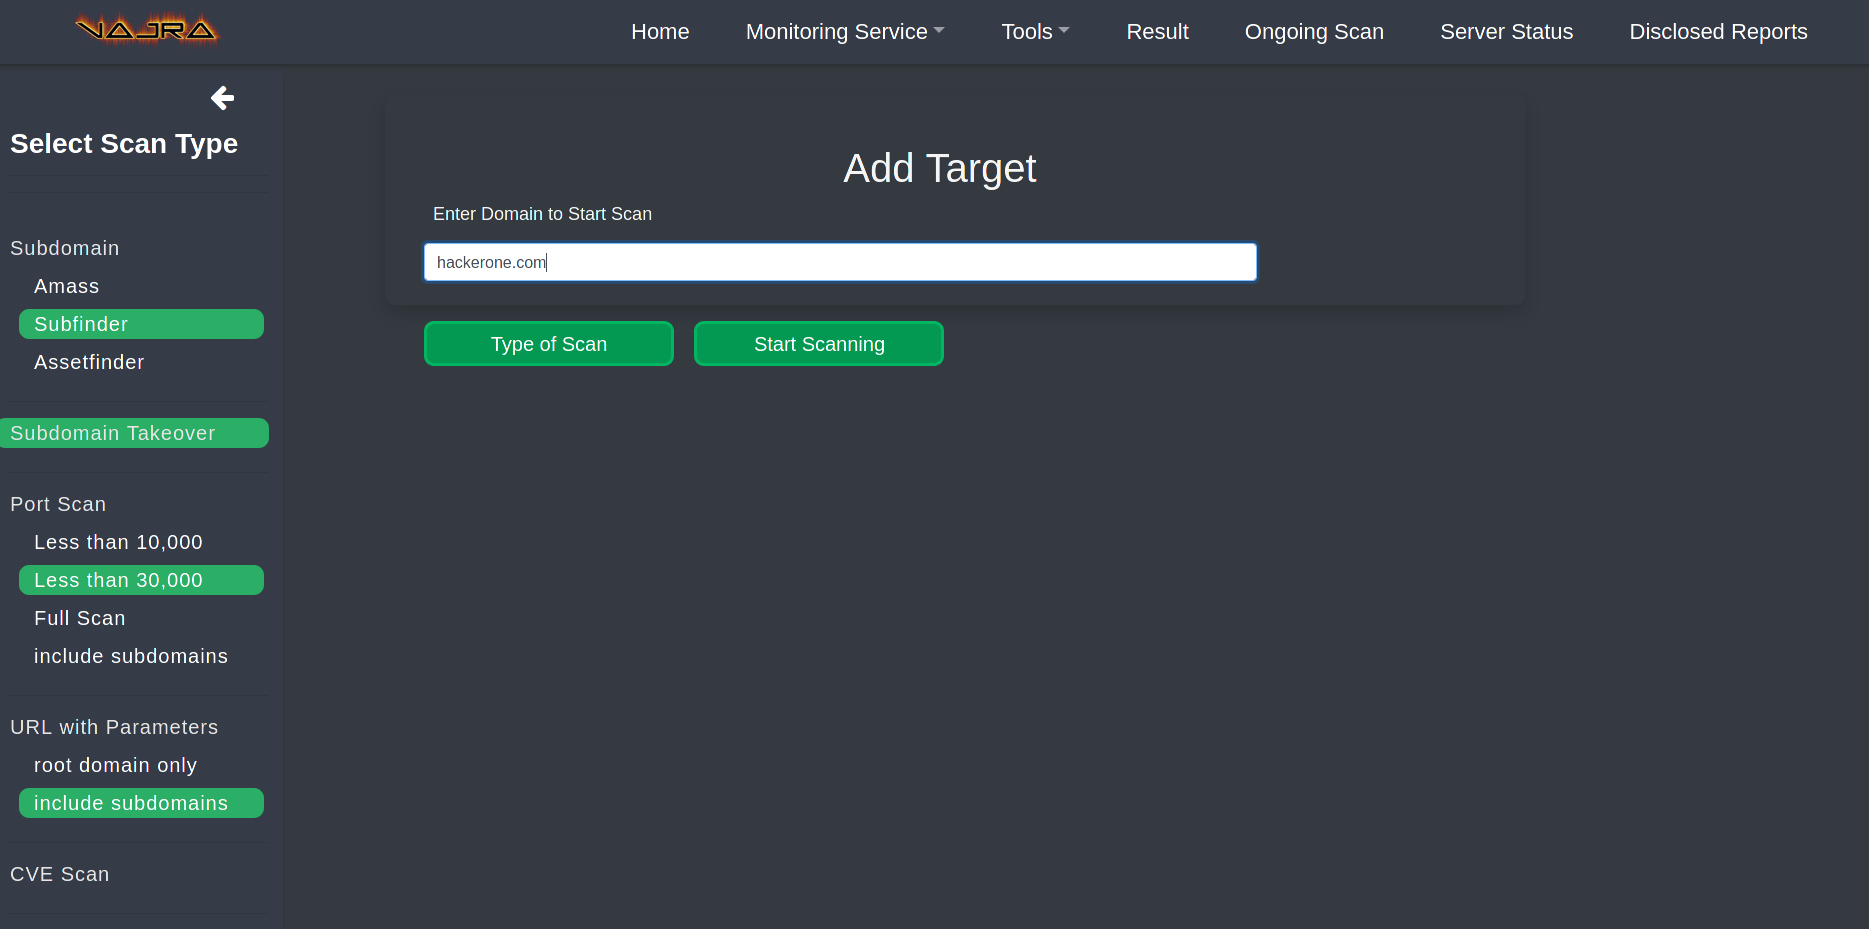 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 cappricio-securities/ghostrecon
gh0str3con is a All in one cloud based web Recon tool.
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
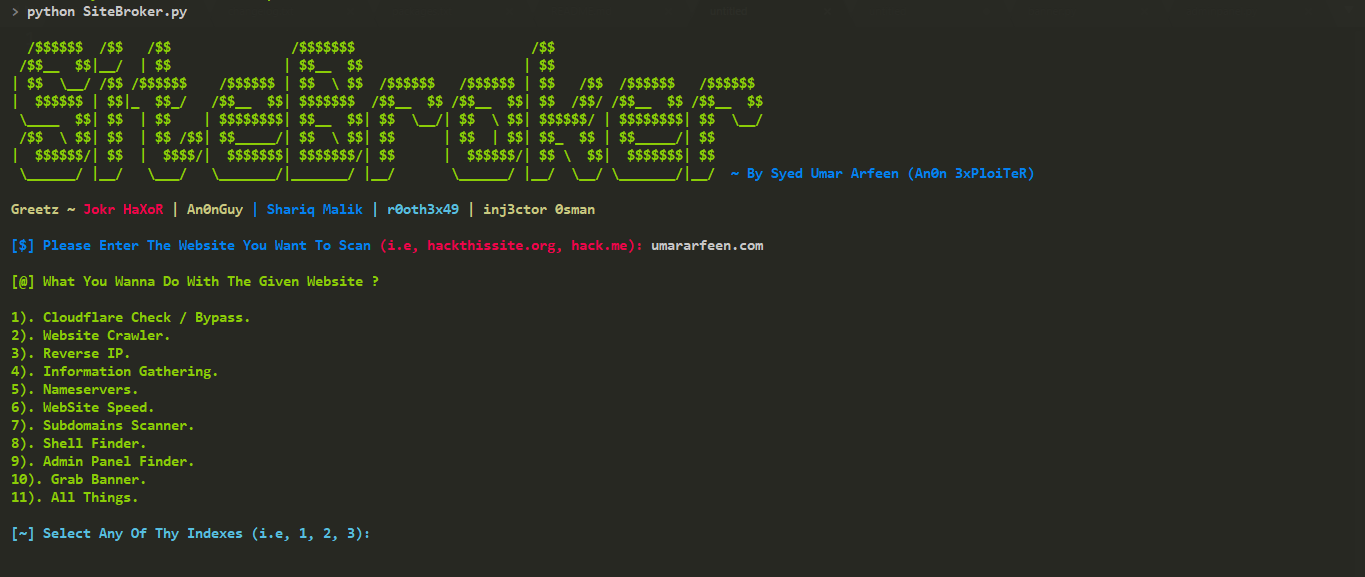 anon-exploiter/sitebroker
A cross-platform python based utility for information gathering and penetration testing automation!
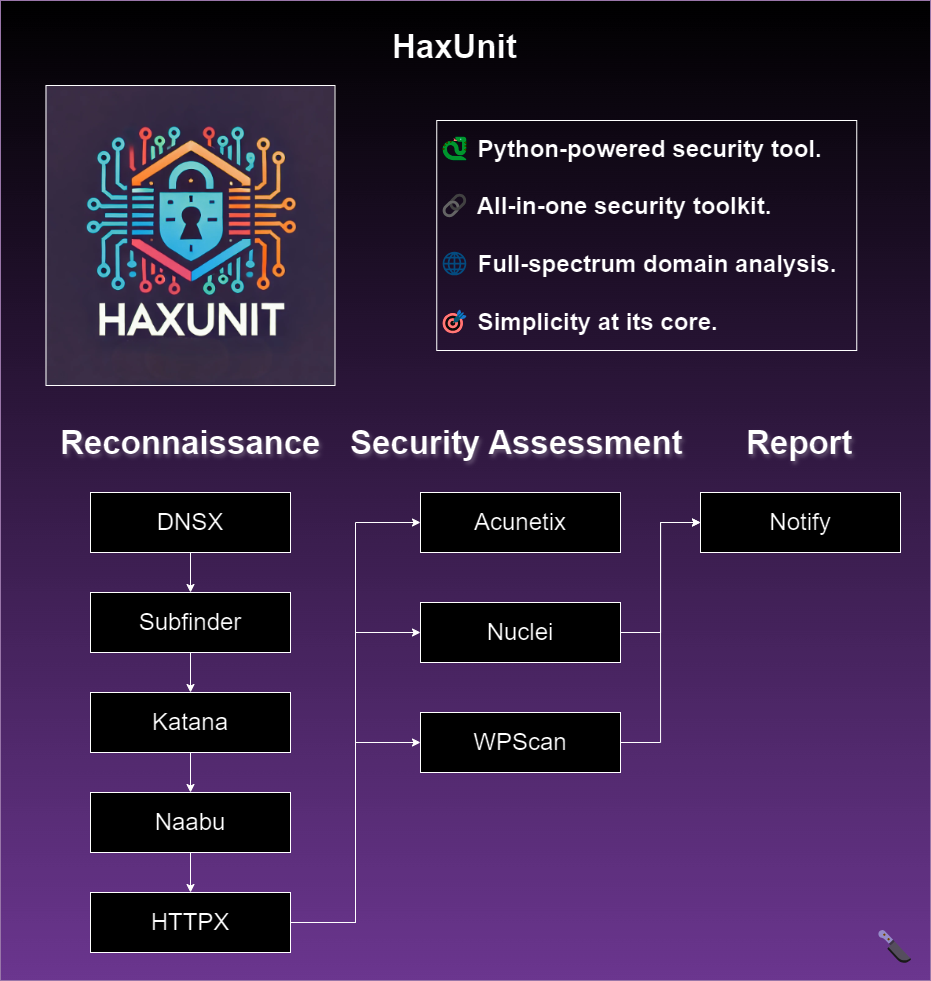 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
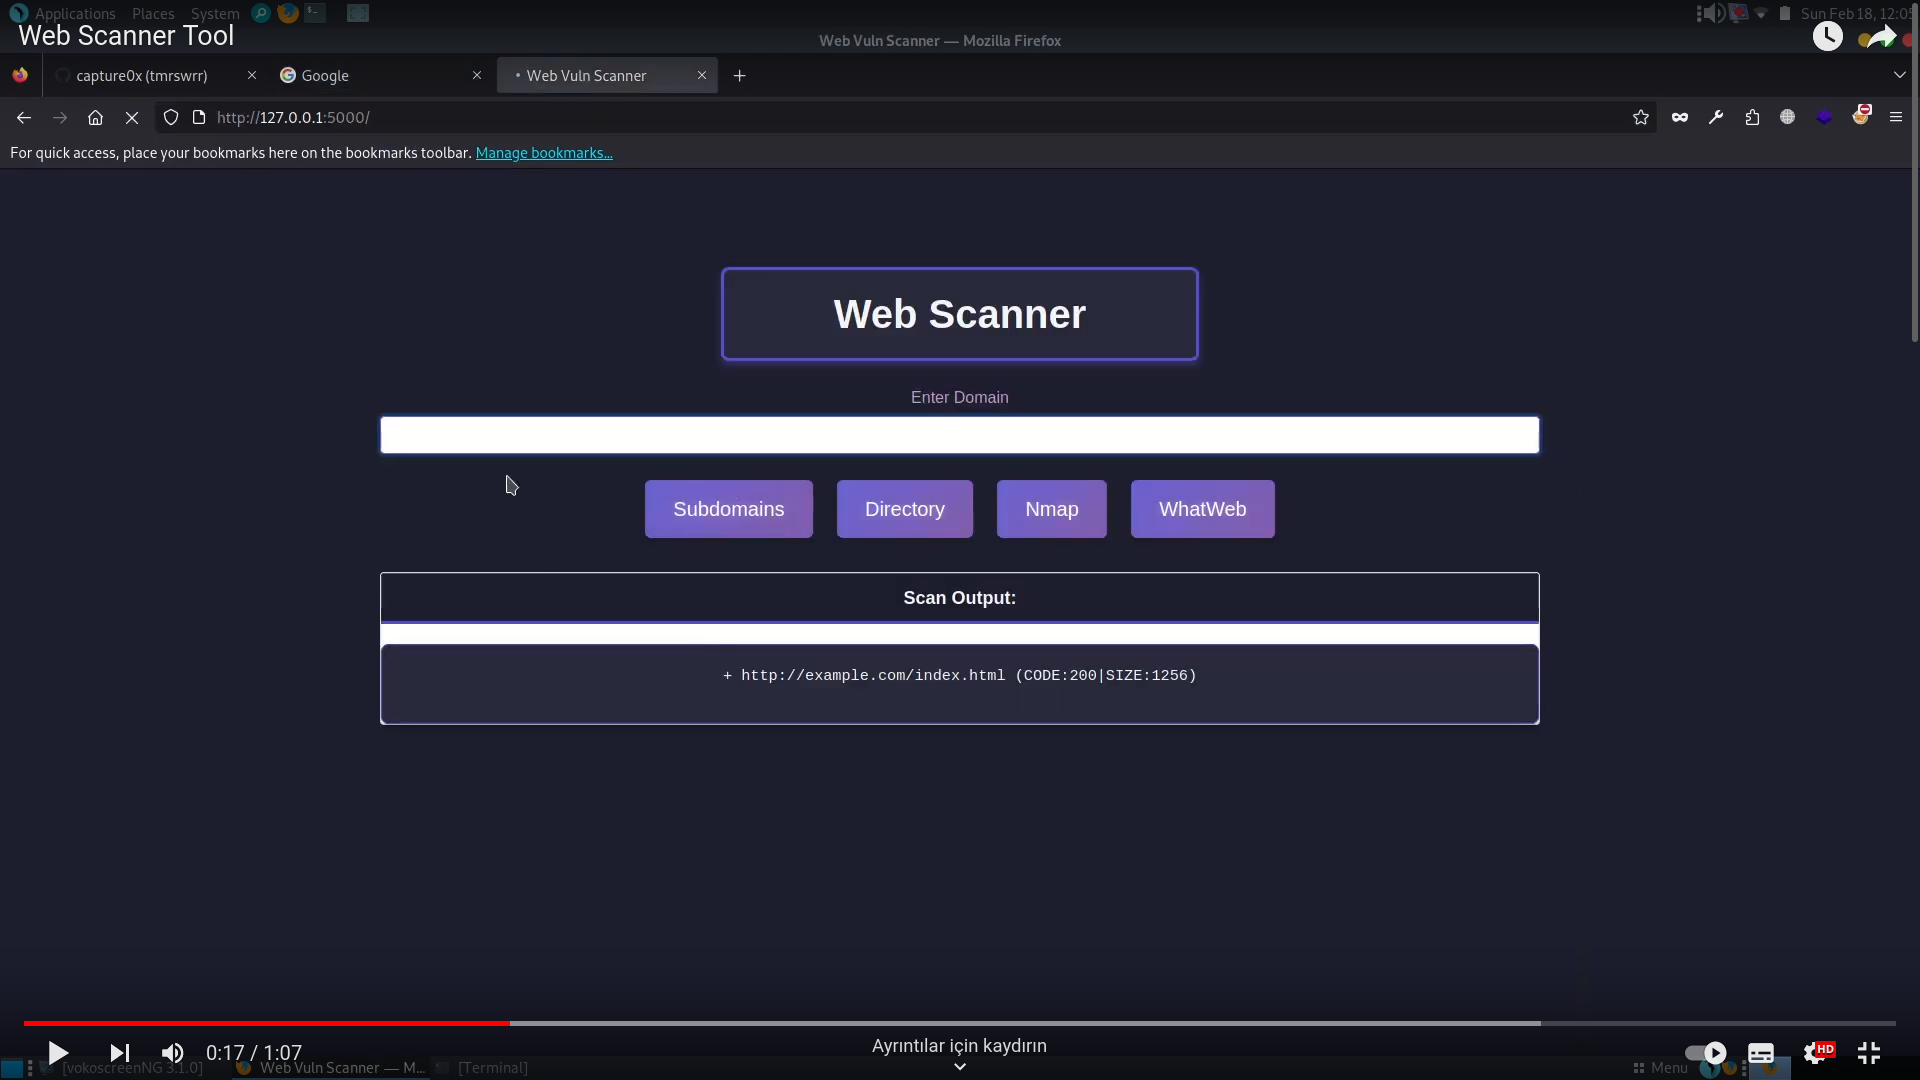 capture0x/web-scanner
Python-based web domain scanner integrating Sublist3r, Dirble, Nmap, and WhatWeb for subdomain discovery, directory enumeration, network scanning,…
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
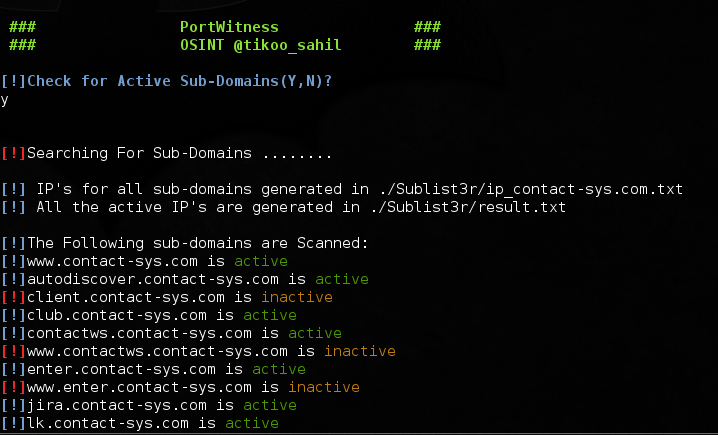 viperbluff/portwitness
Tool for checking Whether a domain or its multiple sub-domains are up and running.
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities
 jevalenciap/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
 xcapri/subdosec
Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
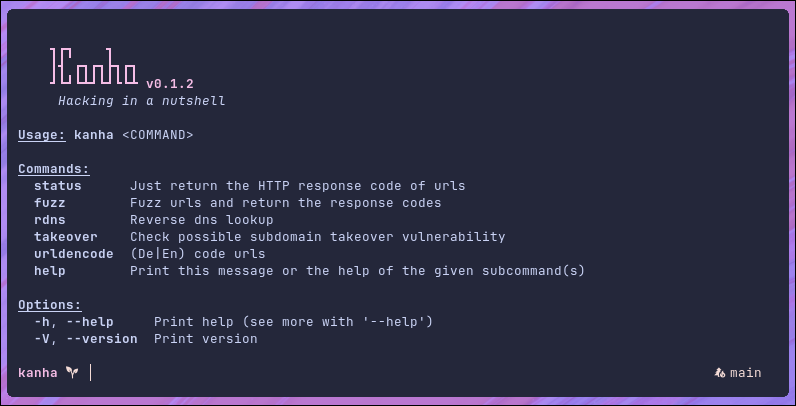 pwnwriter/kanha
🦚 A web-app pentesting suite written in rust .