

JShunter
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
api-securitydynamic-code-analysispenetration-testing+6
543
cc1a2b/jshunterjshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 praetorian-inc/gokart
A static analysis tool for securing Go code
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 samsung/utopia
UT based automated fuzz driver generation
 whitesquirrell/c0devari4nt
A variant analysis and visualisation tool that scans codebases for similar vulnerabilities
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
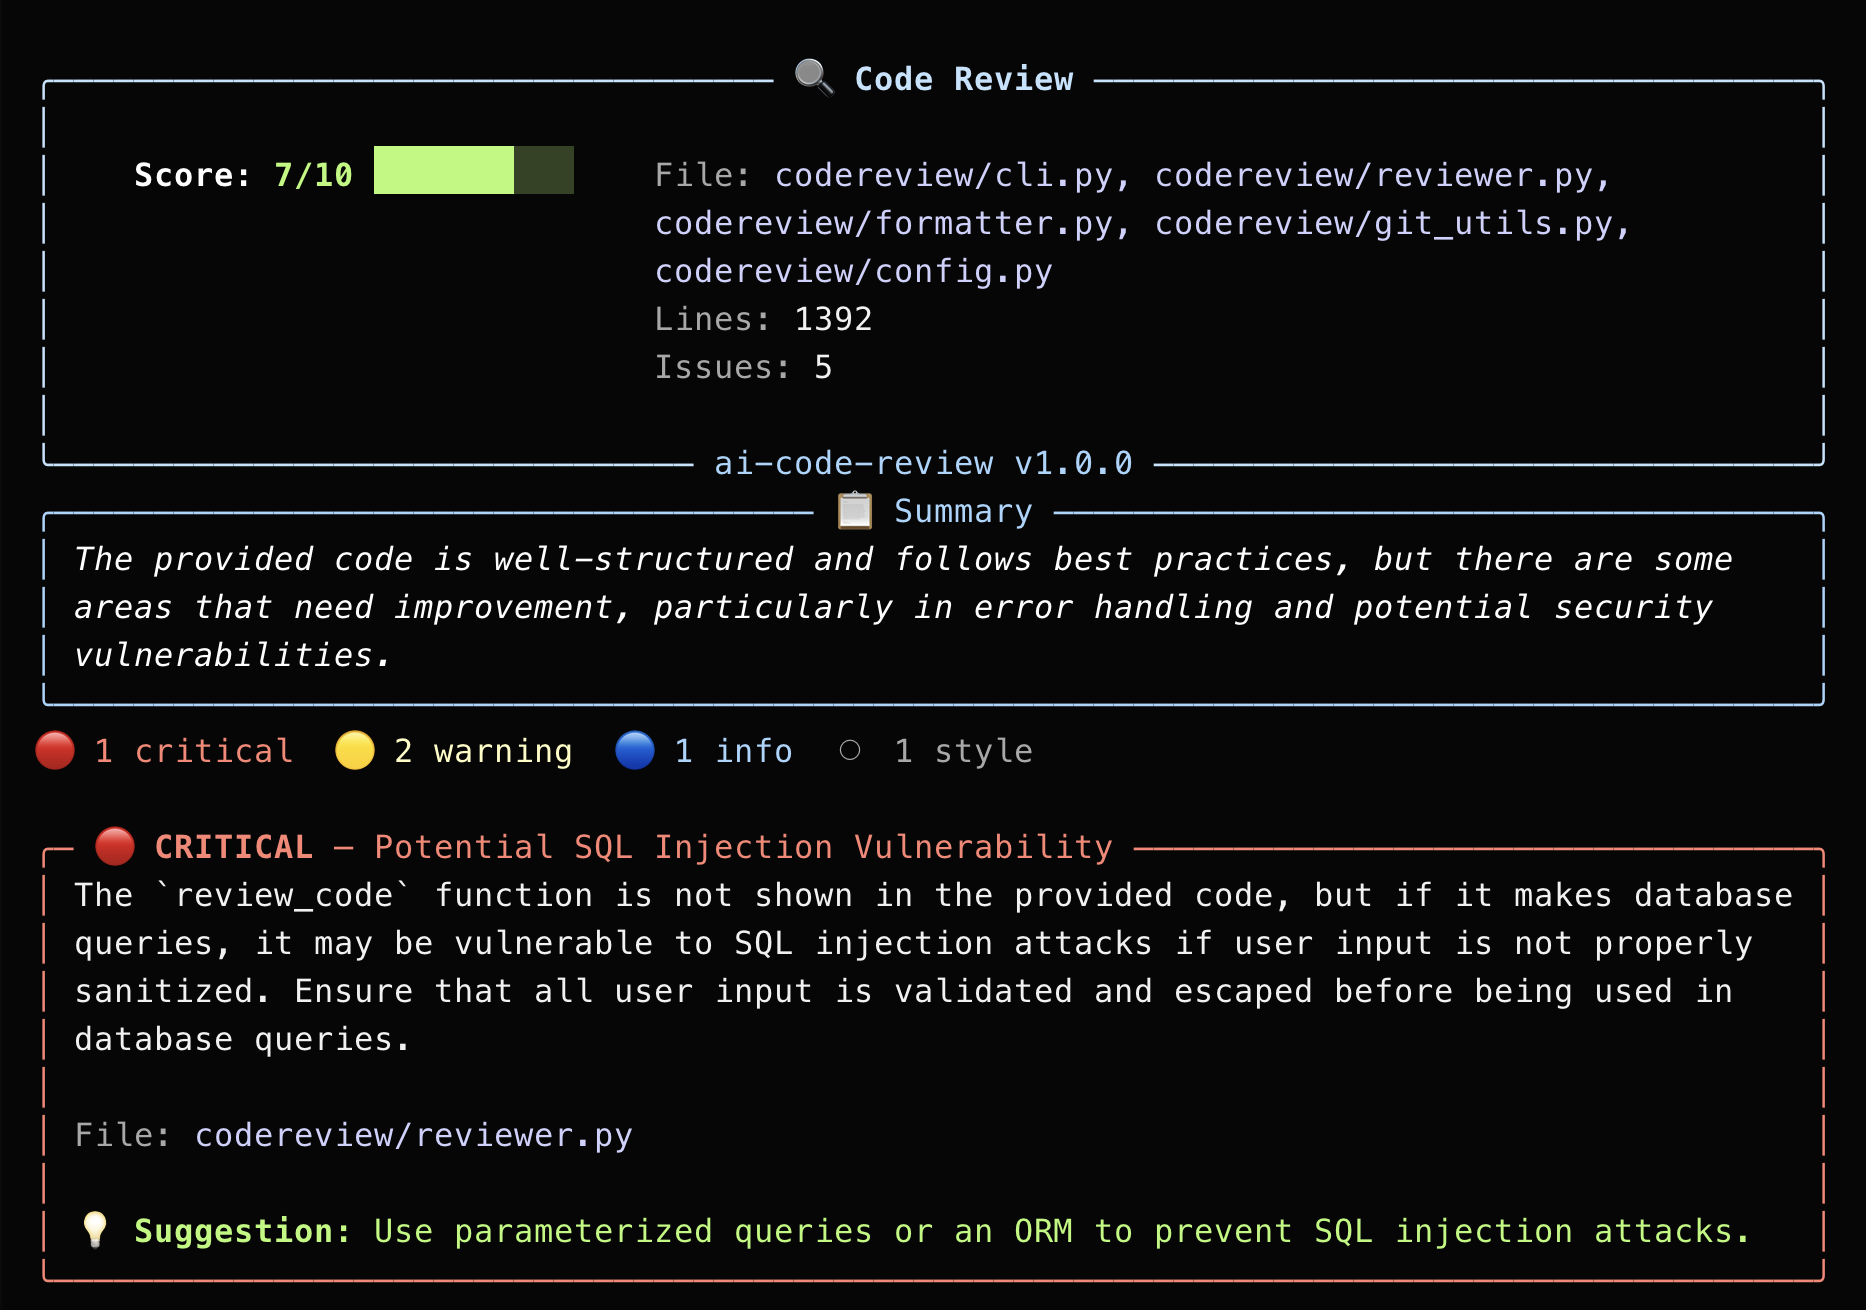 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
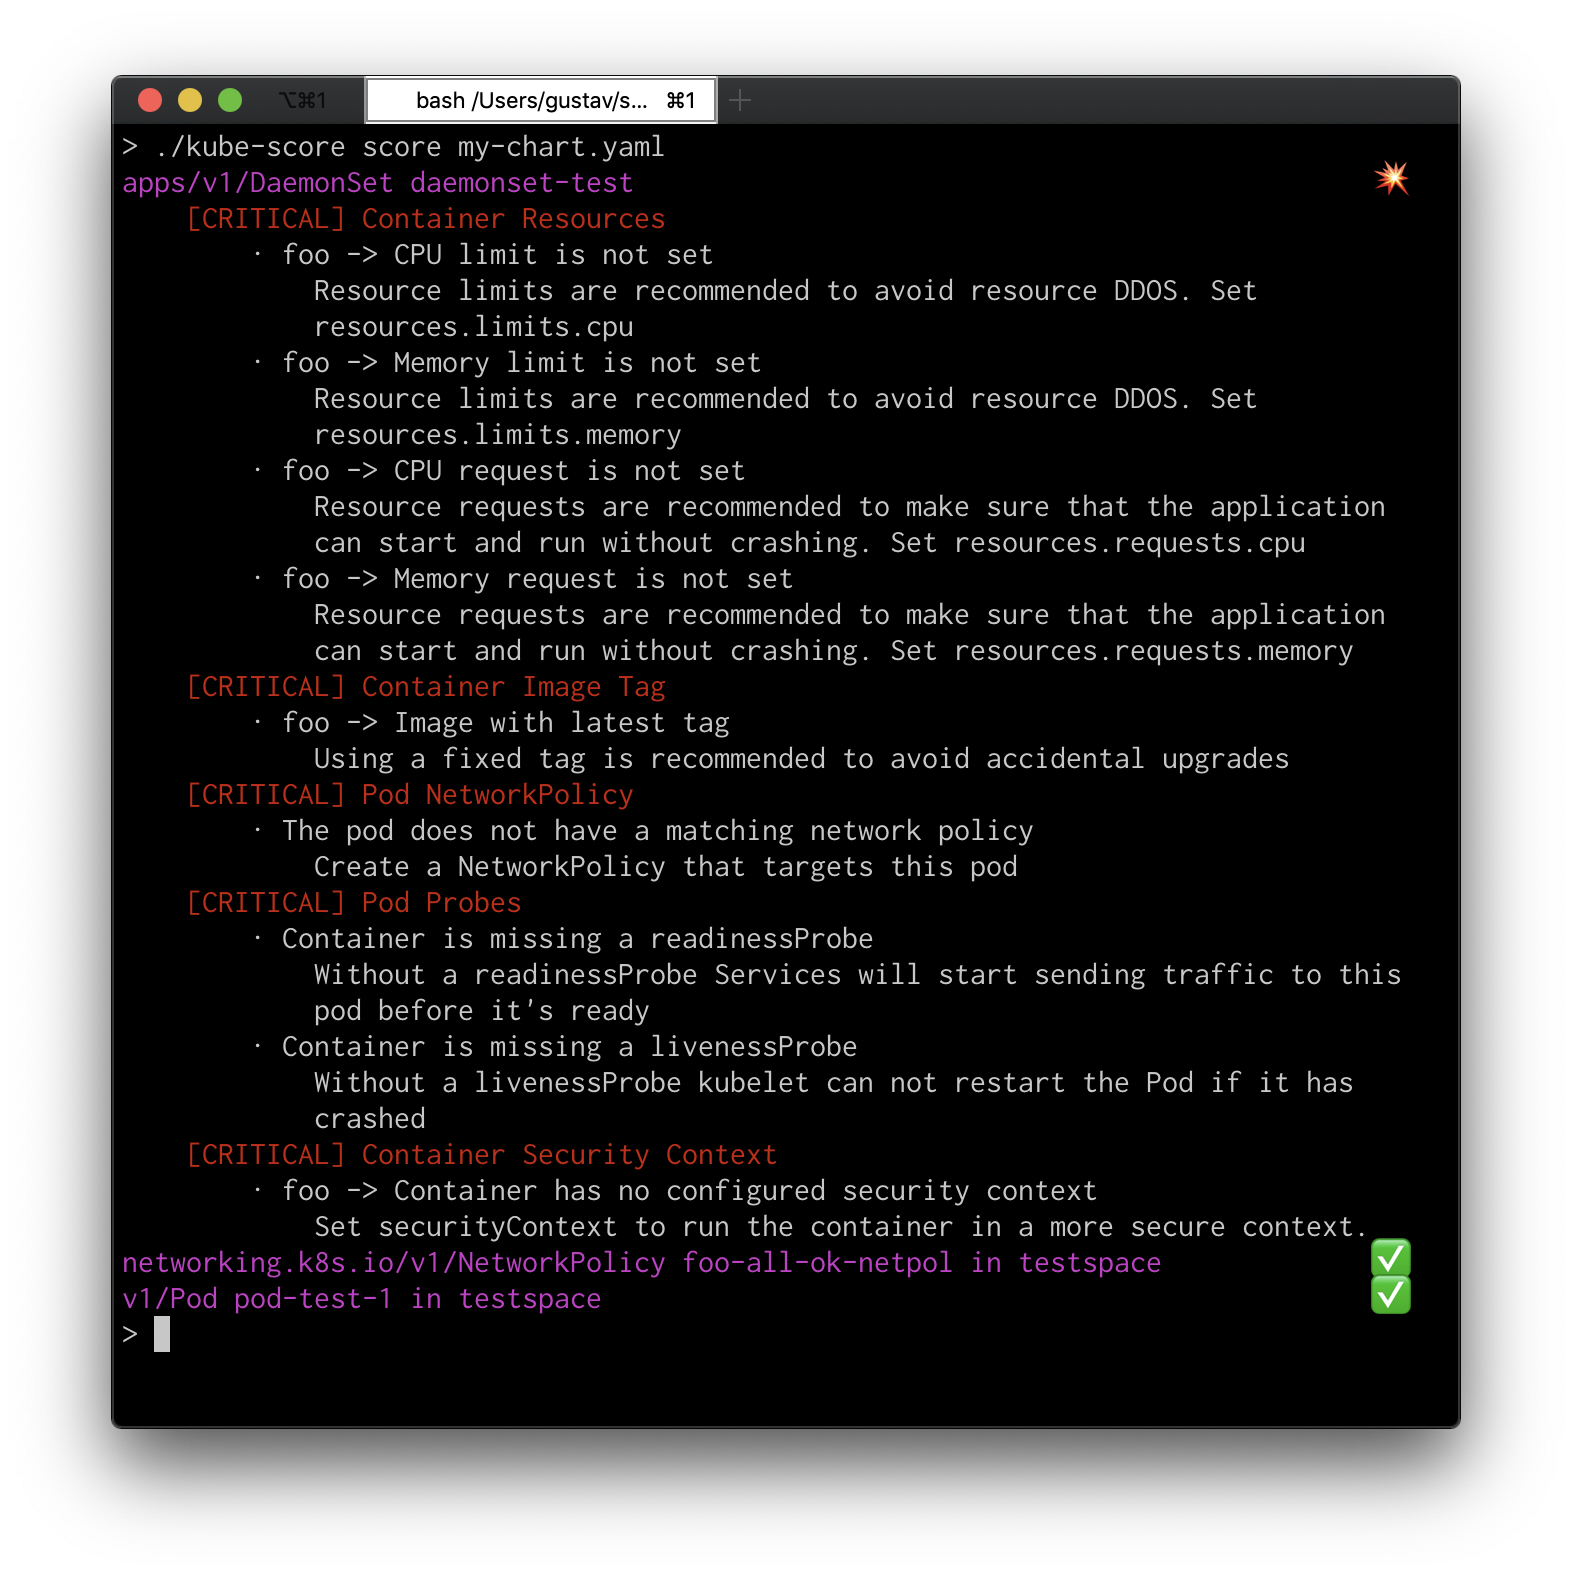 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
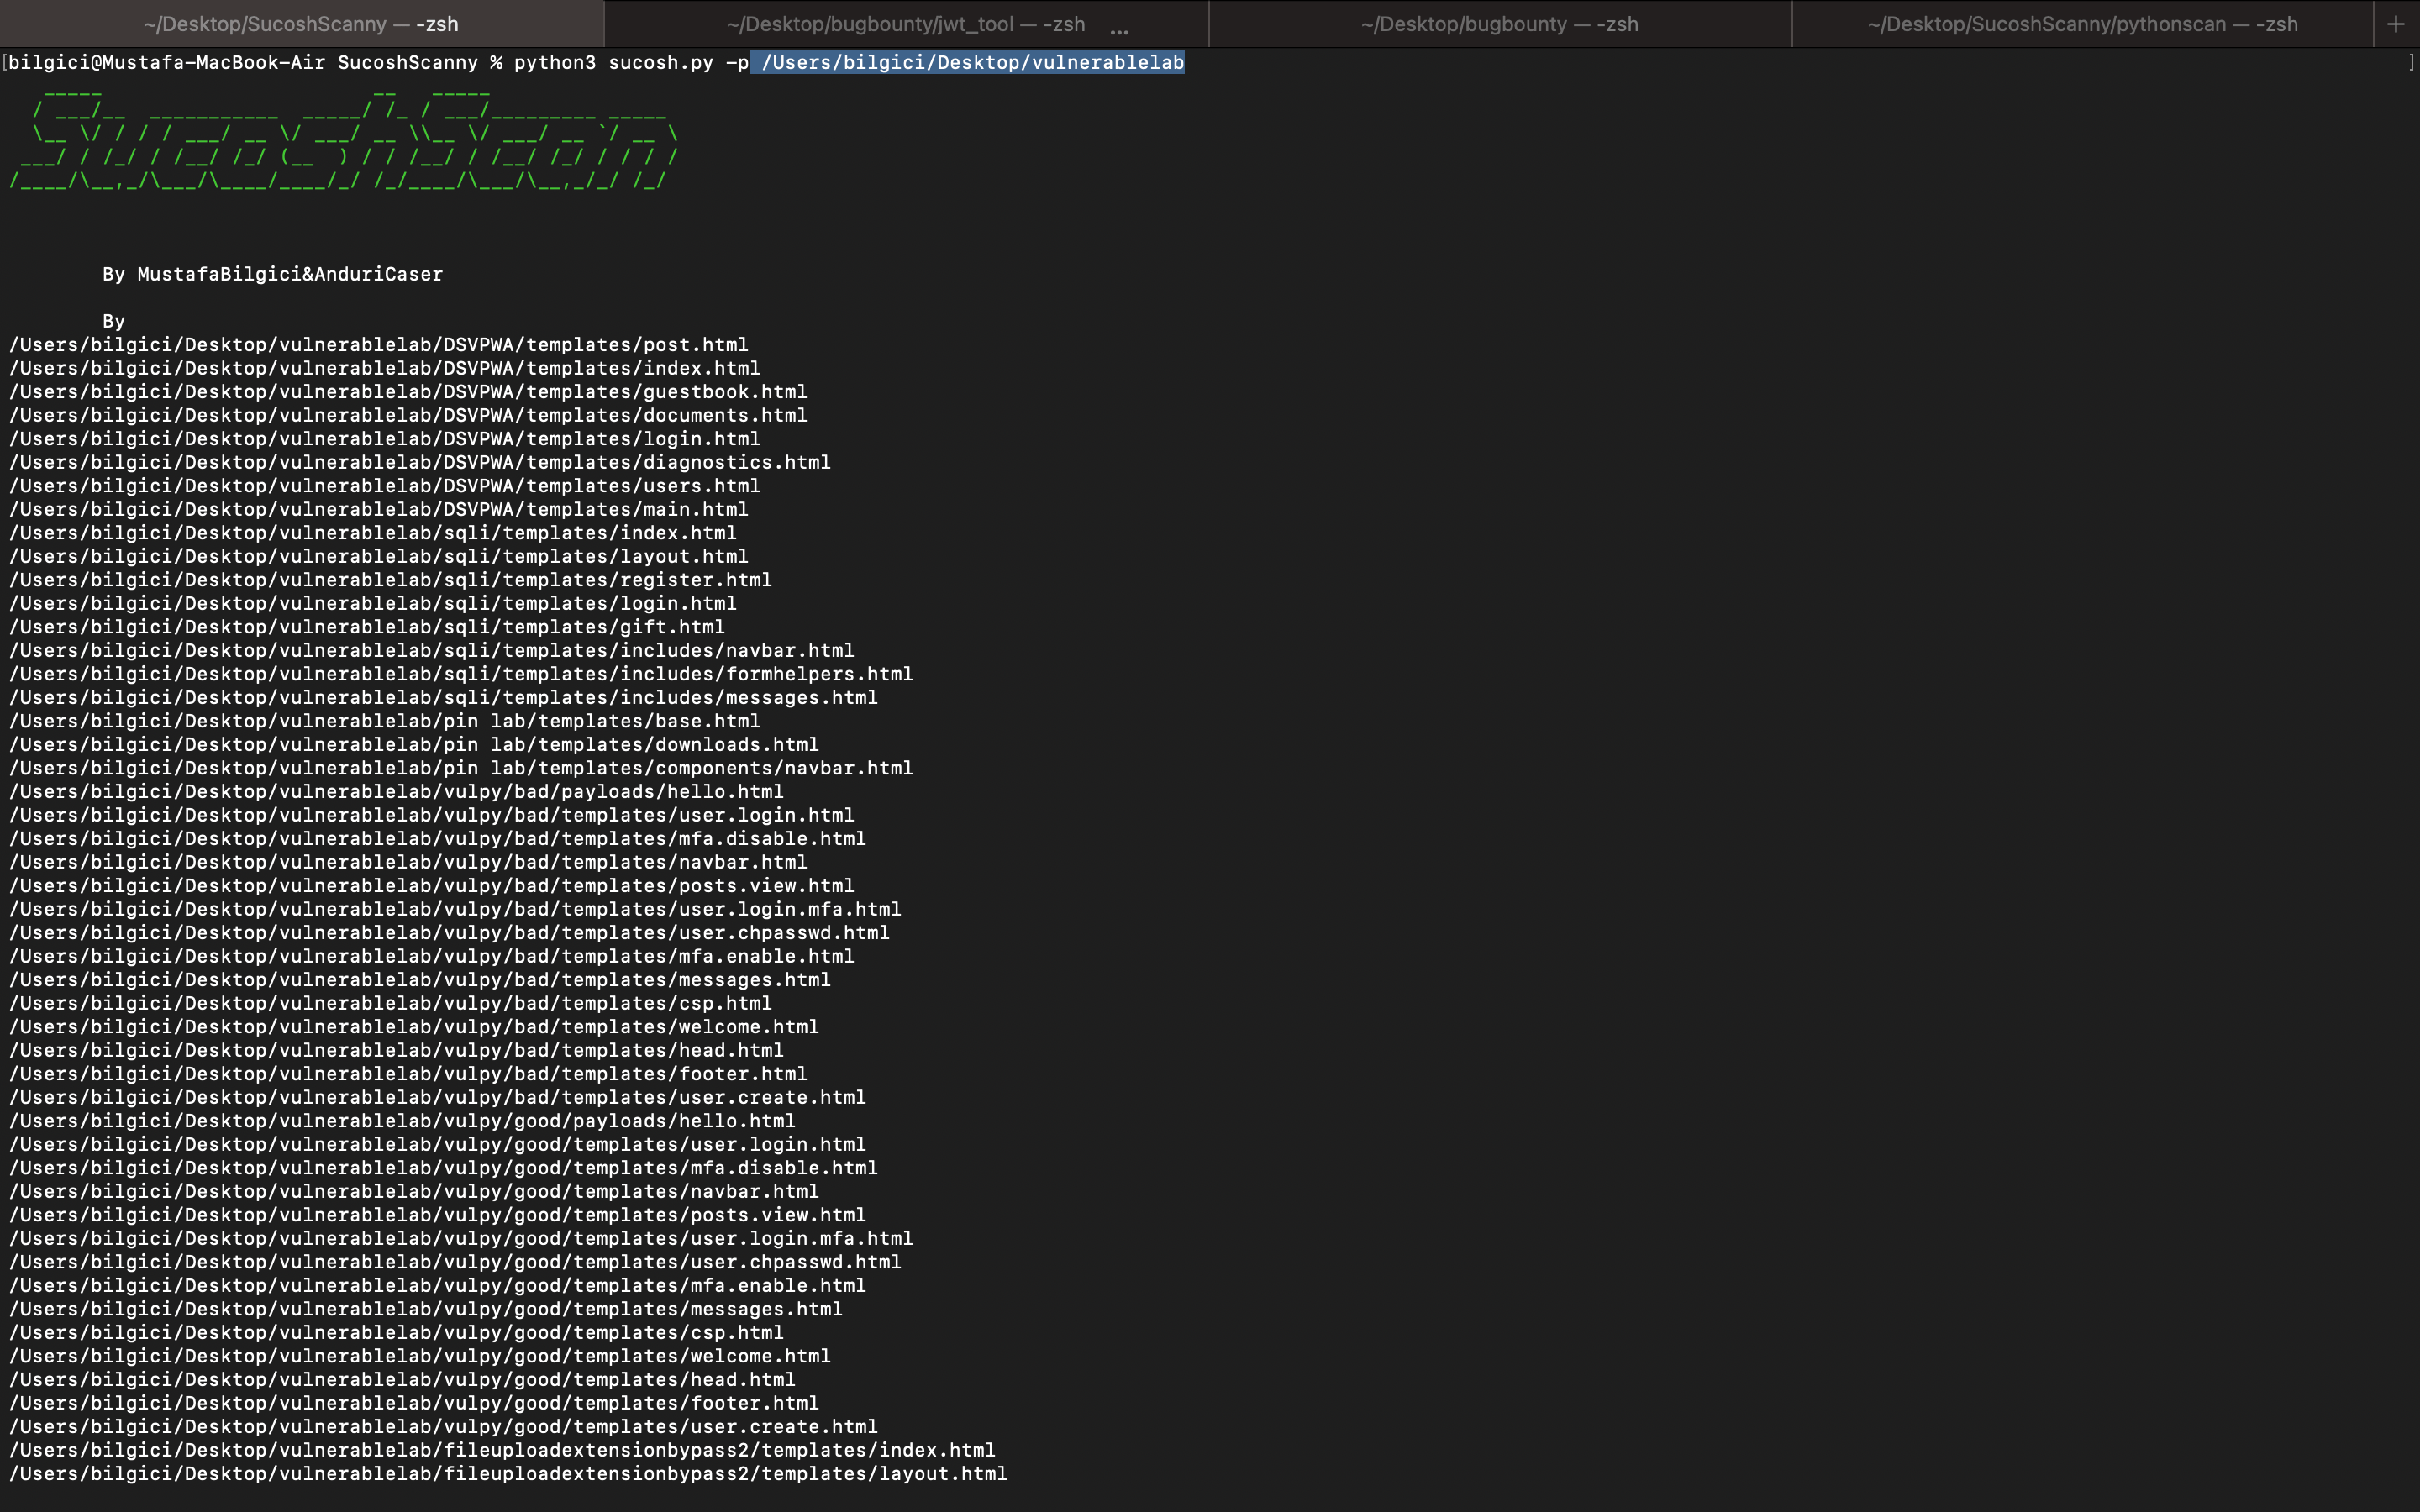 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…