

jackhammer
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
code-analysisconfiguration-auditingdevsecops+9
739
olacabs/jackhammerJackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 nccgroup/cq
Fast code security scanner designed for manual security code review by experts. Outputs line-referenced findings to text files for easy filtering and…
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
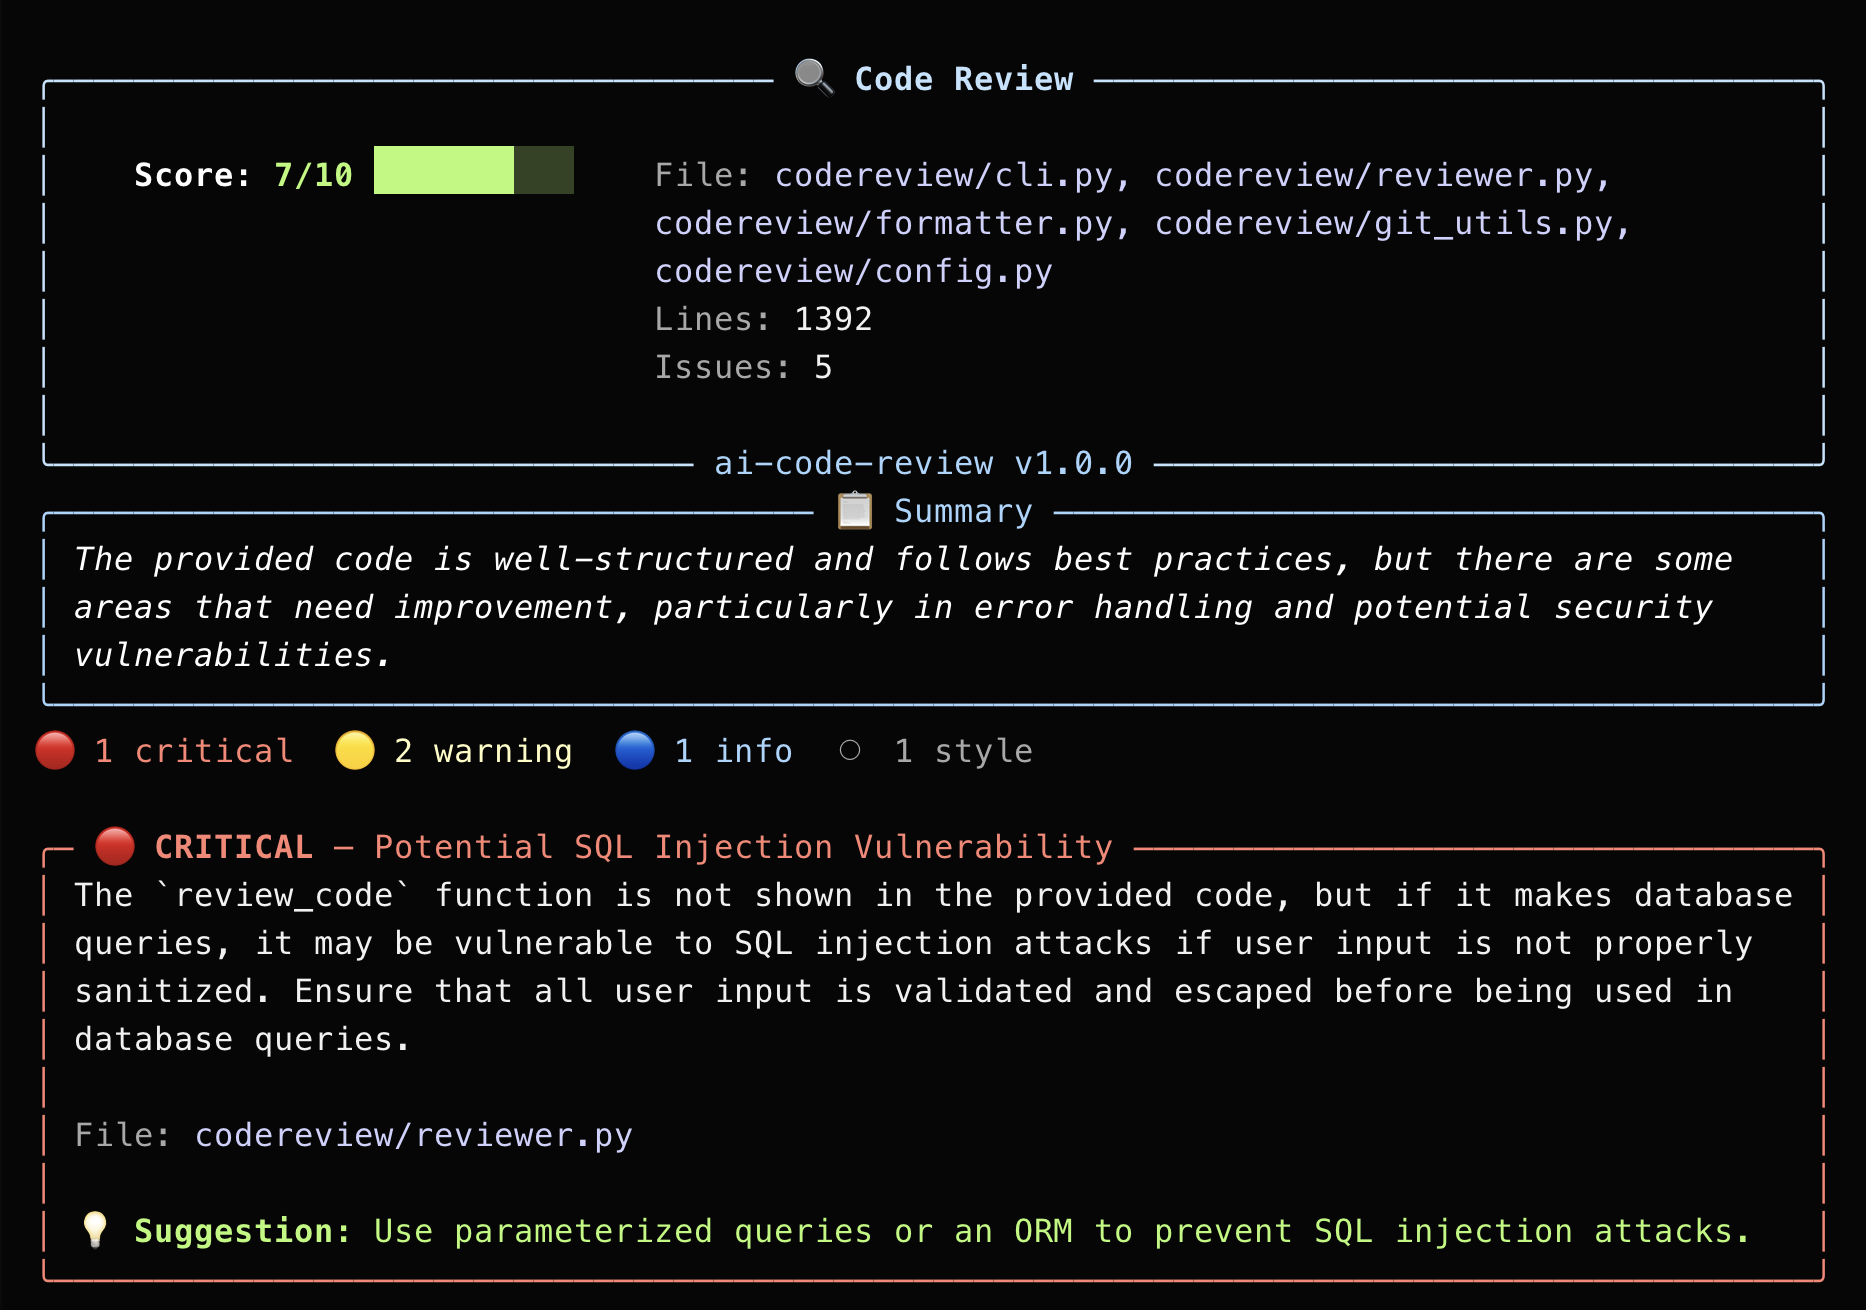 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
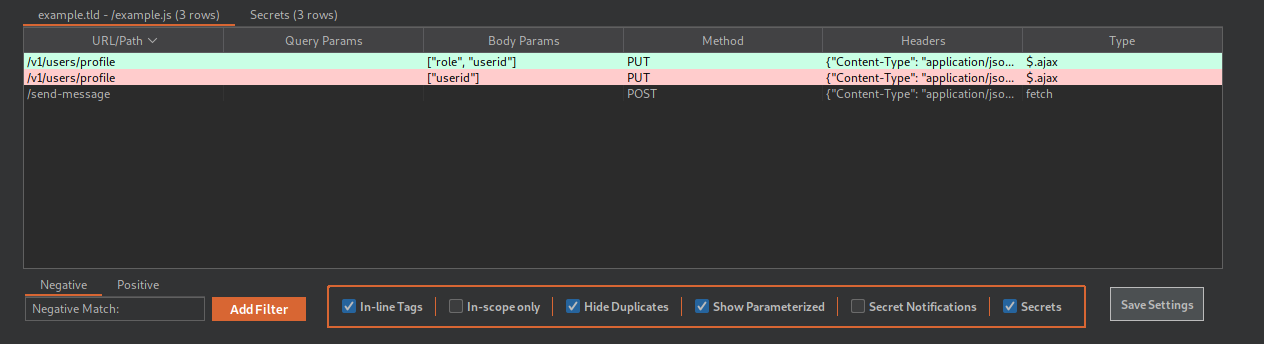 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 samsung/utopia
UT based automated fuzz driver generation
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 advanced-threat-research/creosote
Creosote is our solution to searching for the tarfile vulnerability described by CVE-2007-4559.