
call_map
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
code-analysisreverse-engineeringstatic-code-analysis+1
29
nccgroup/call_mapCurrent development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 whitesquirrell/c0devari4nt
A variant analysis and visualisation tool that scans codebases for similar vulnerabilities
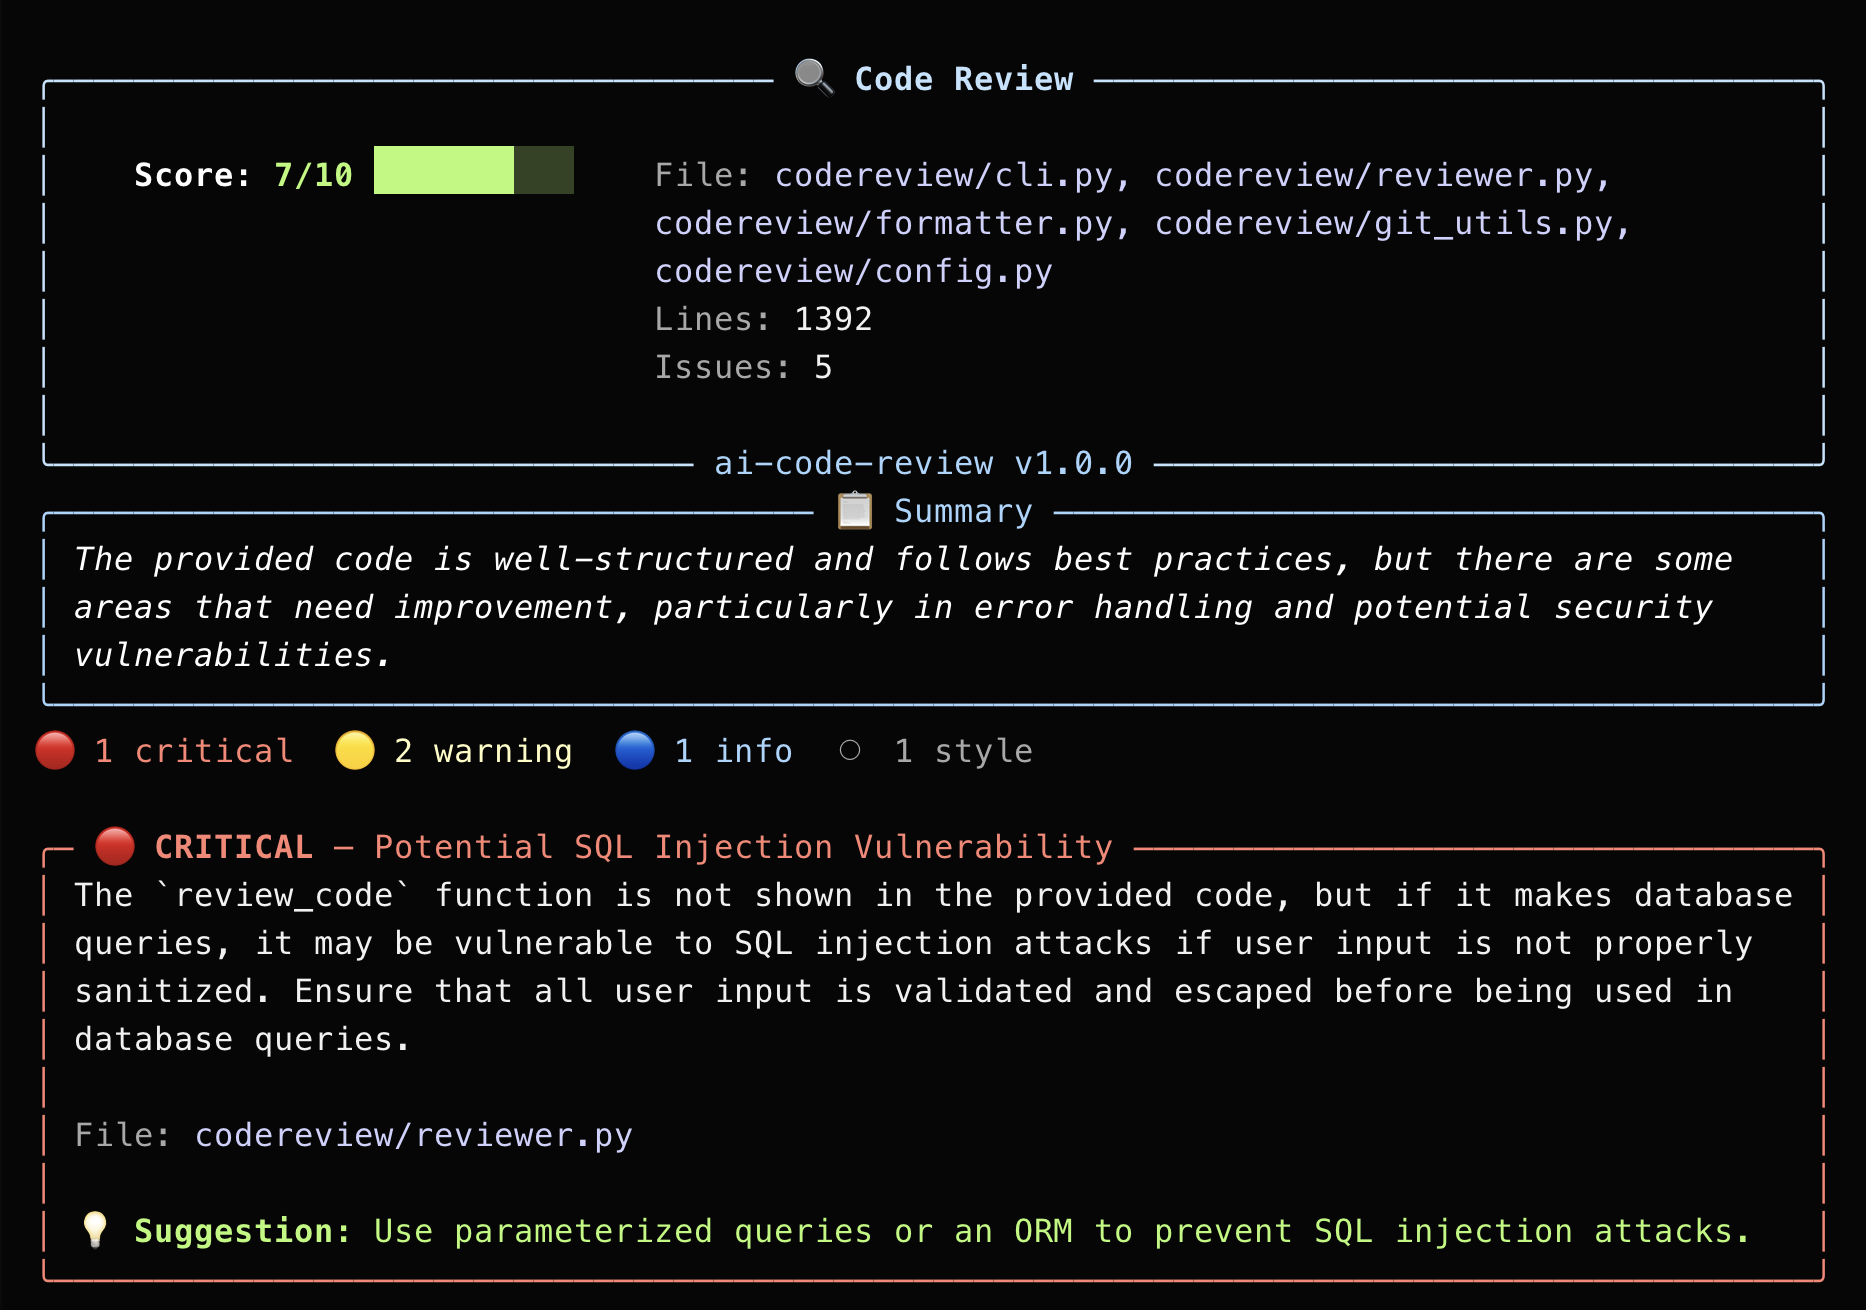 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
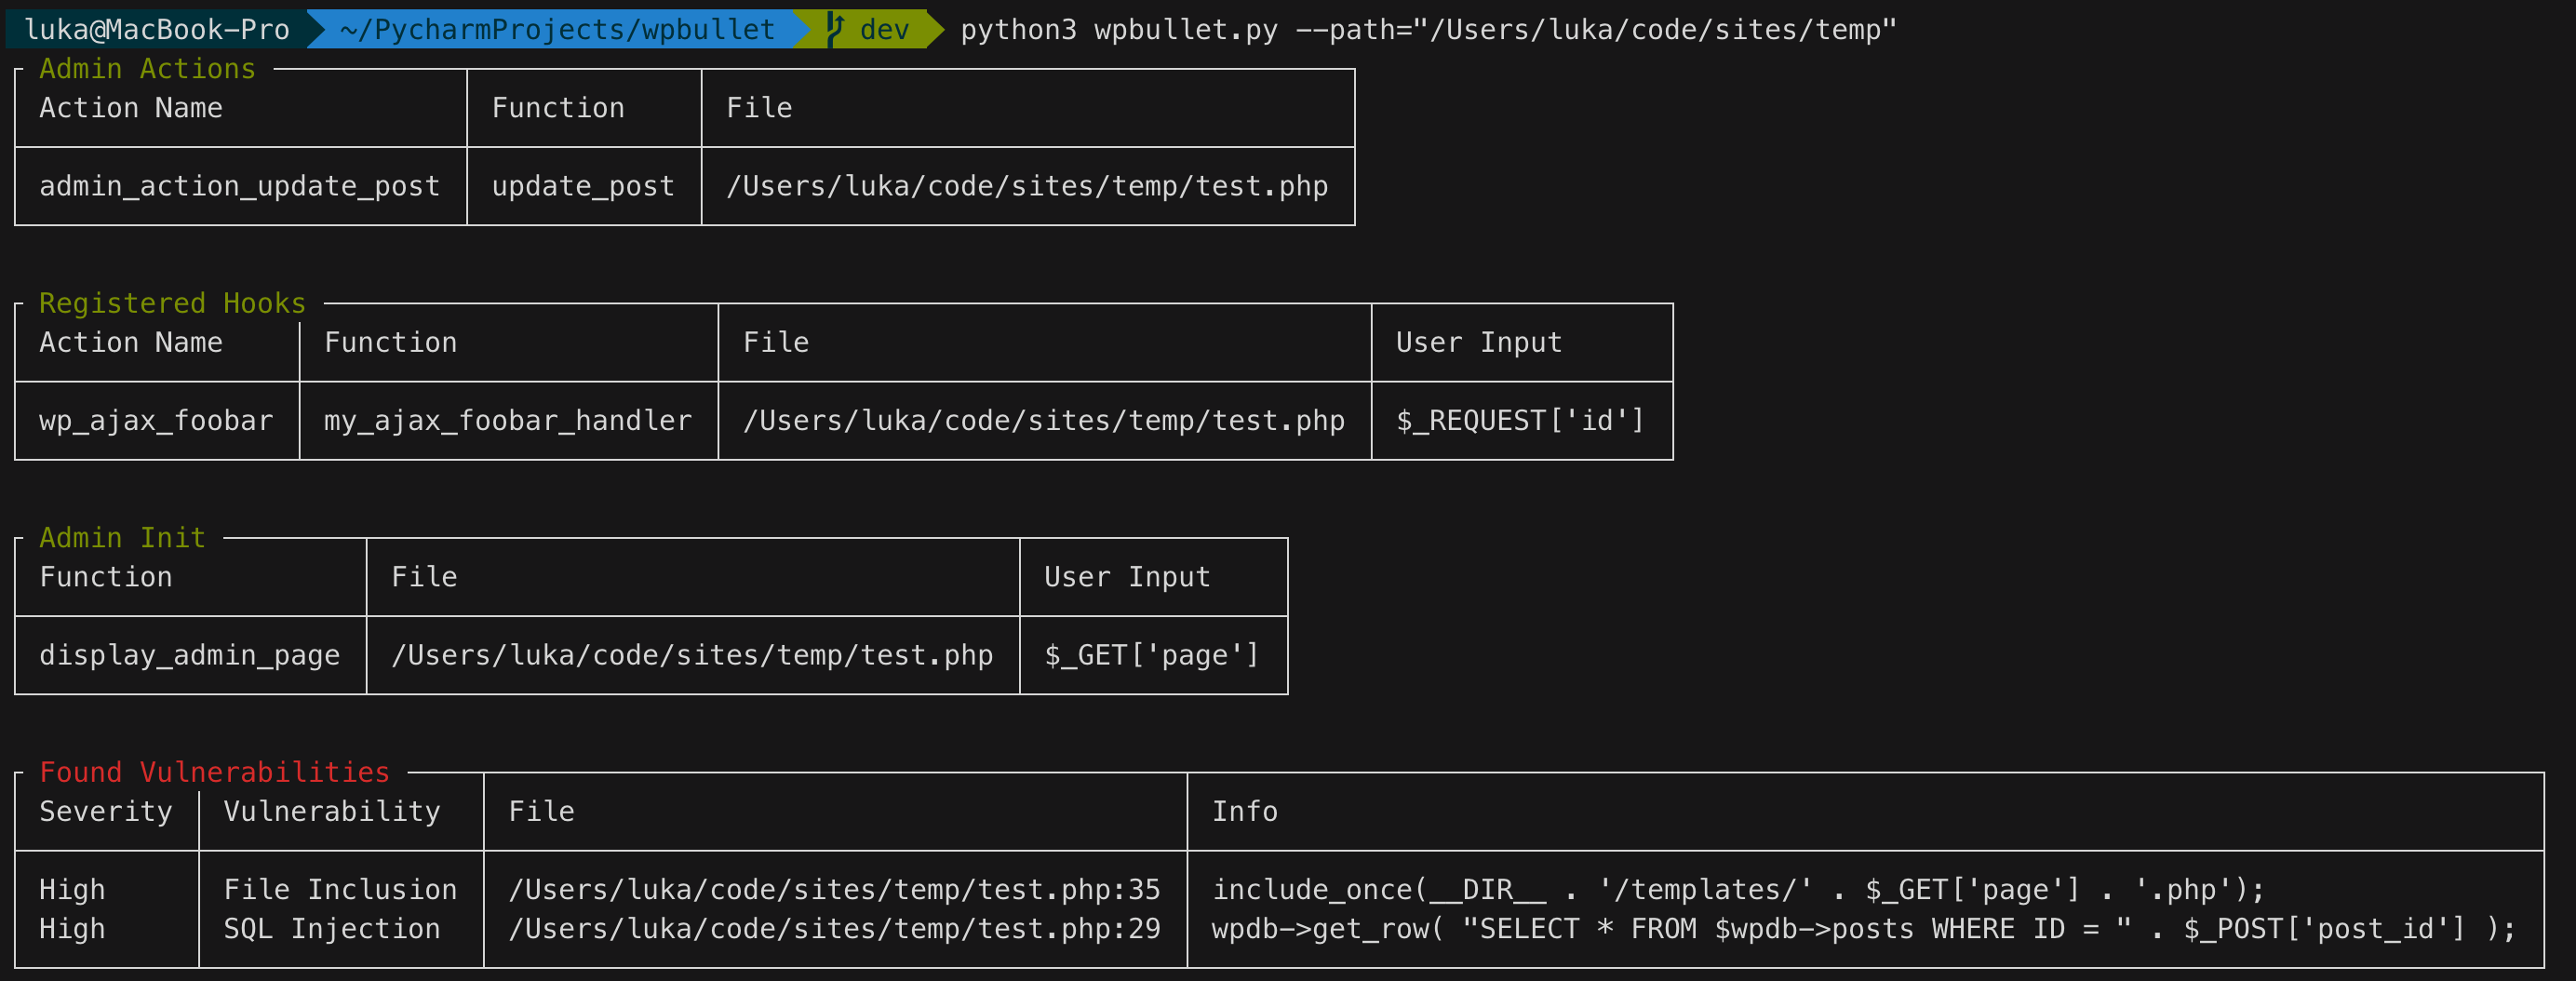 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…