
ghostrace
 vusec/ghostrace
Proof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.
binary-exploitationexploitationpapers-research+2
74
vusec/ghostraceProof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
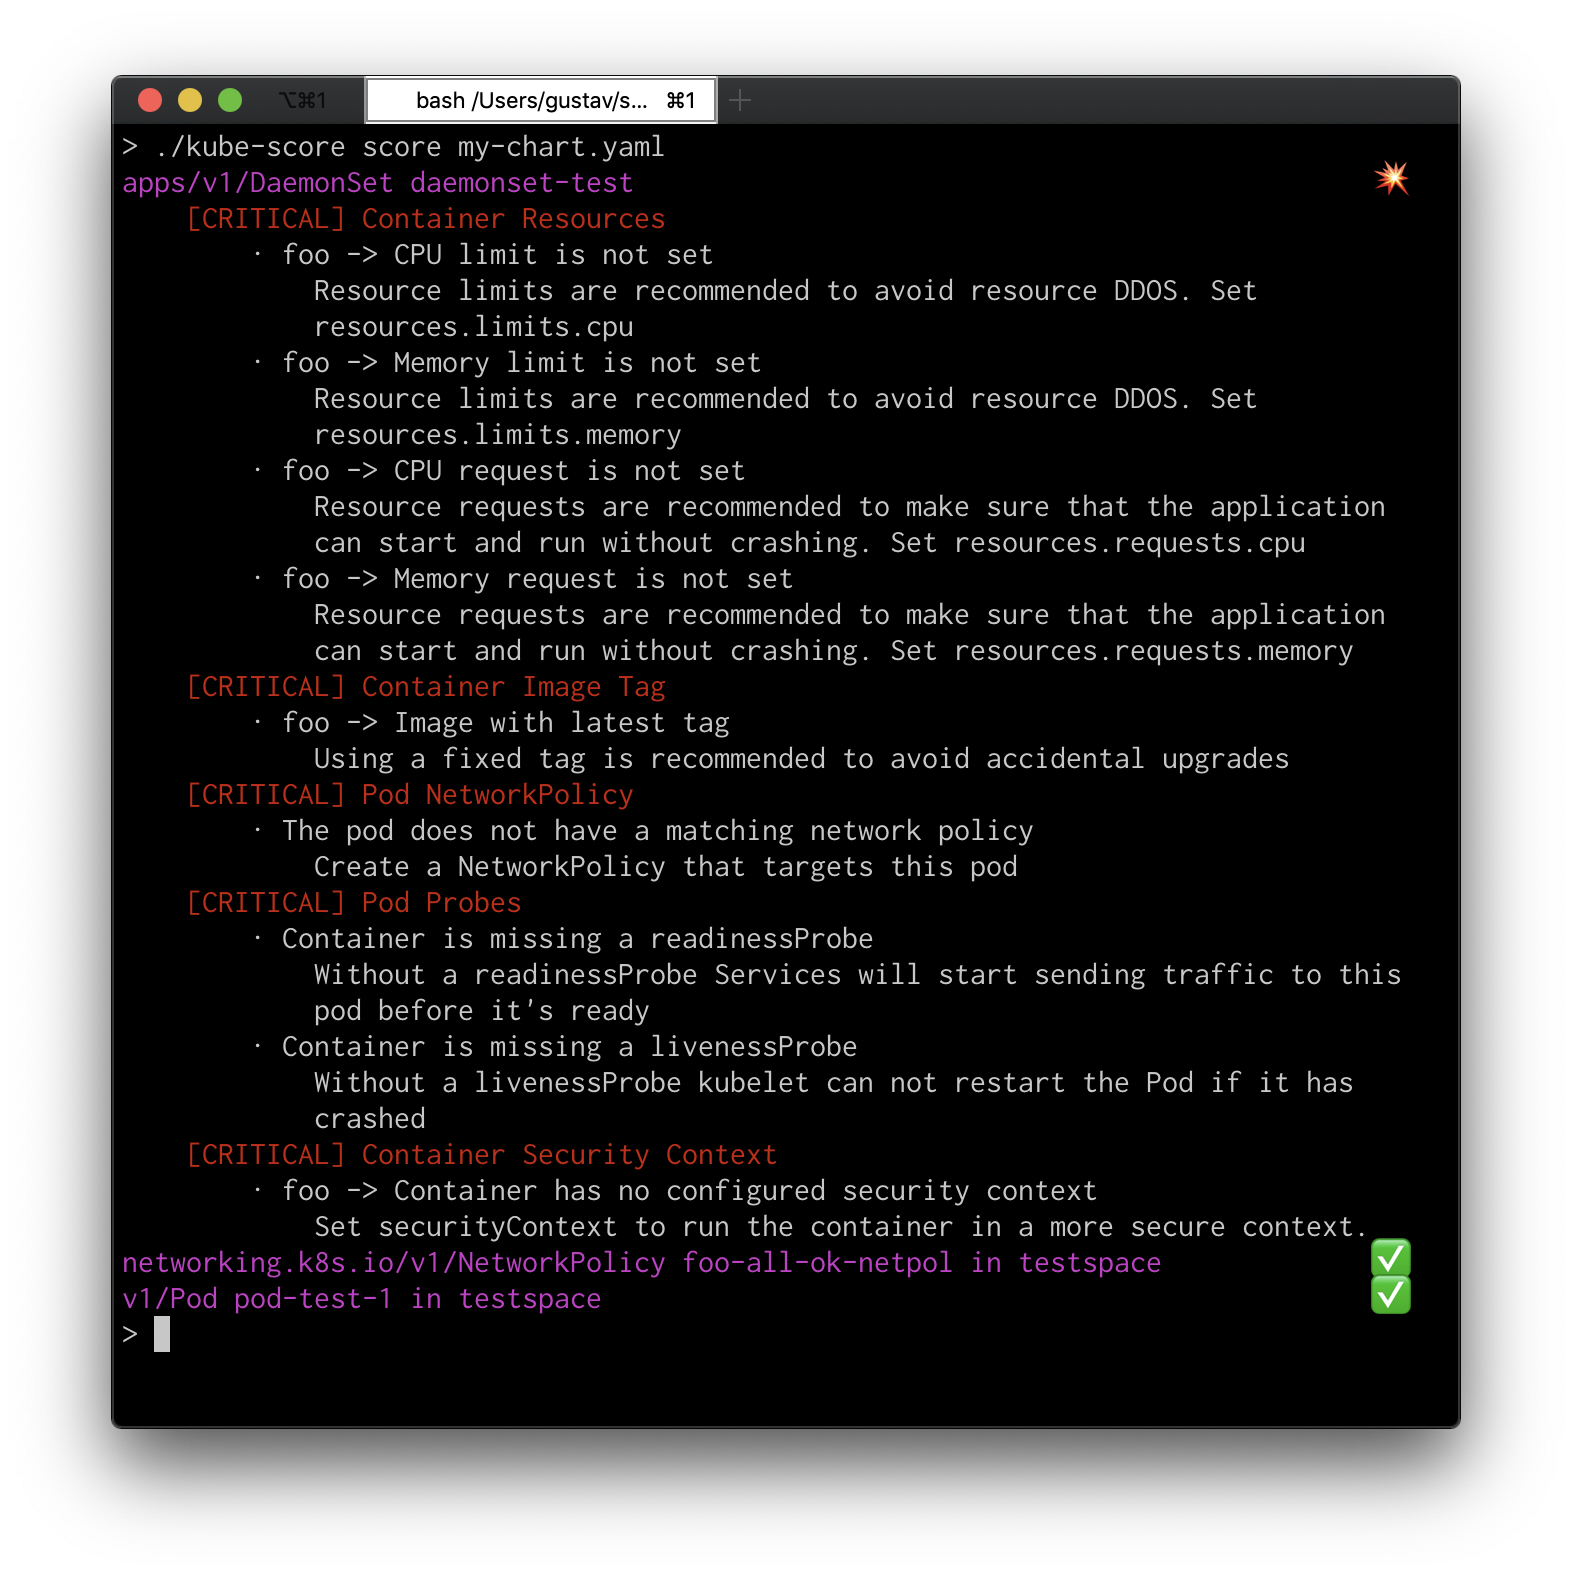 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
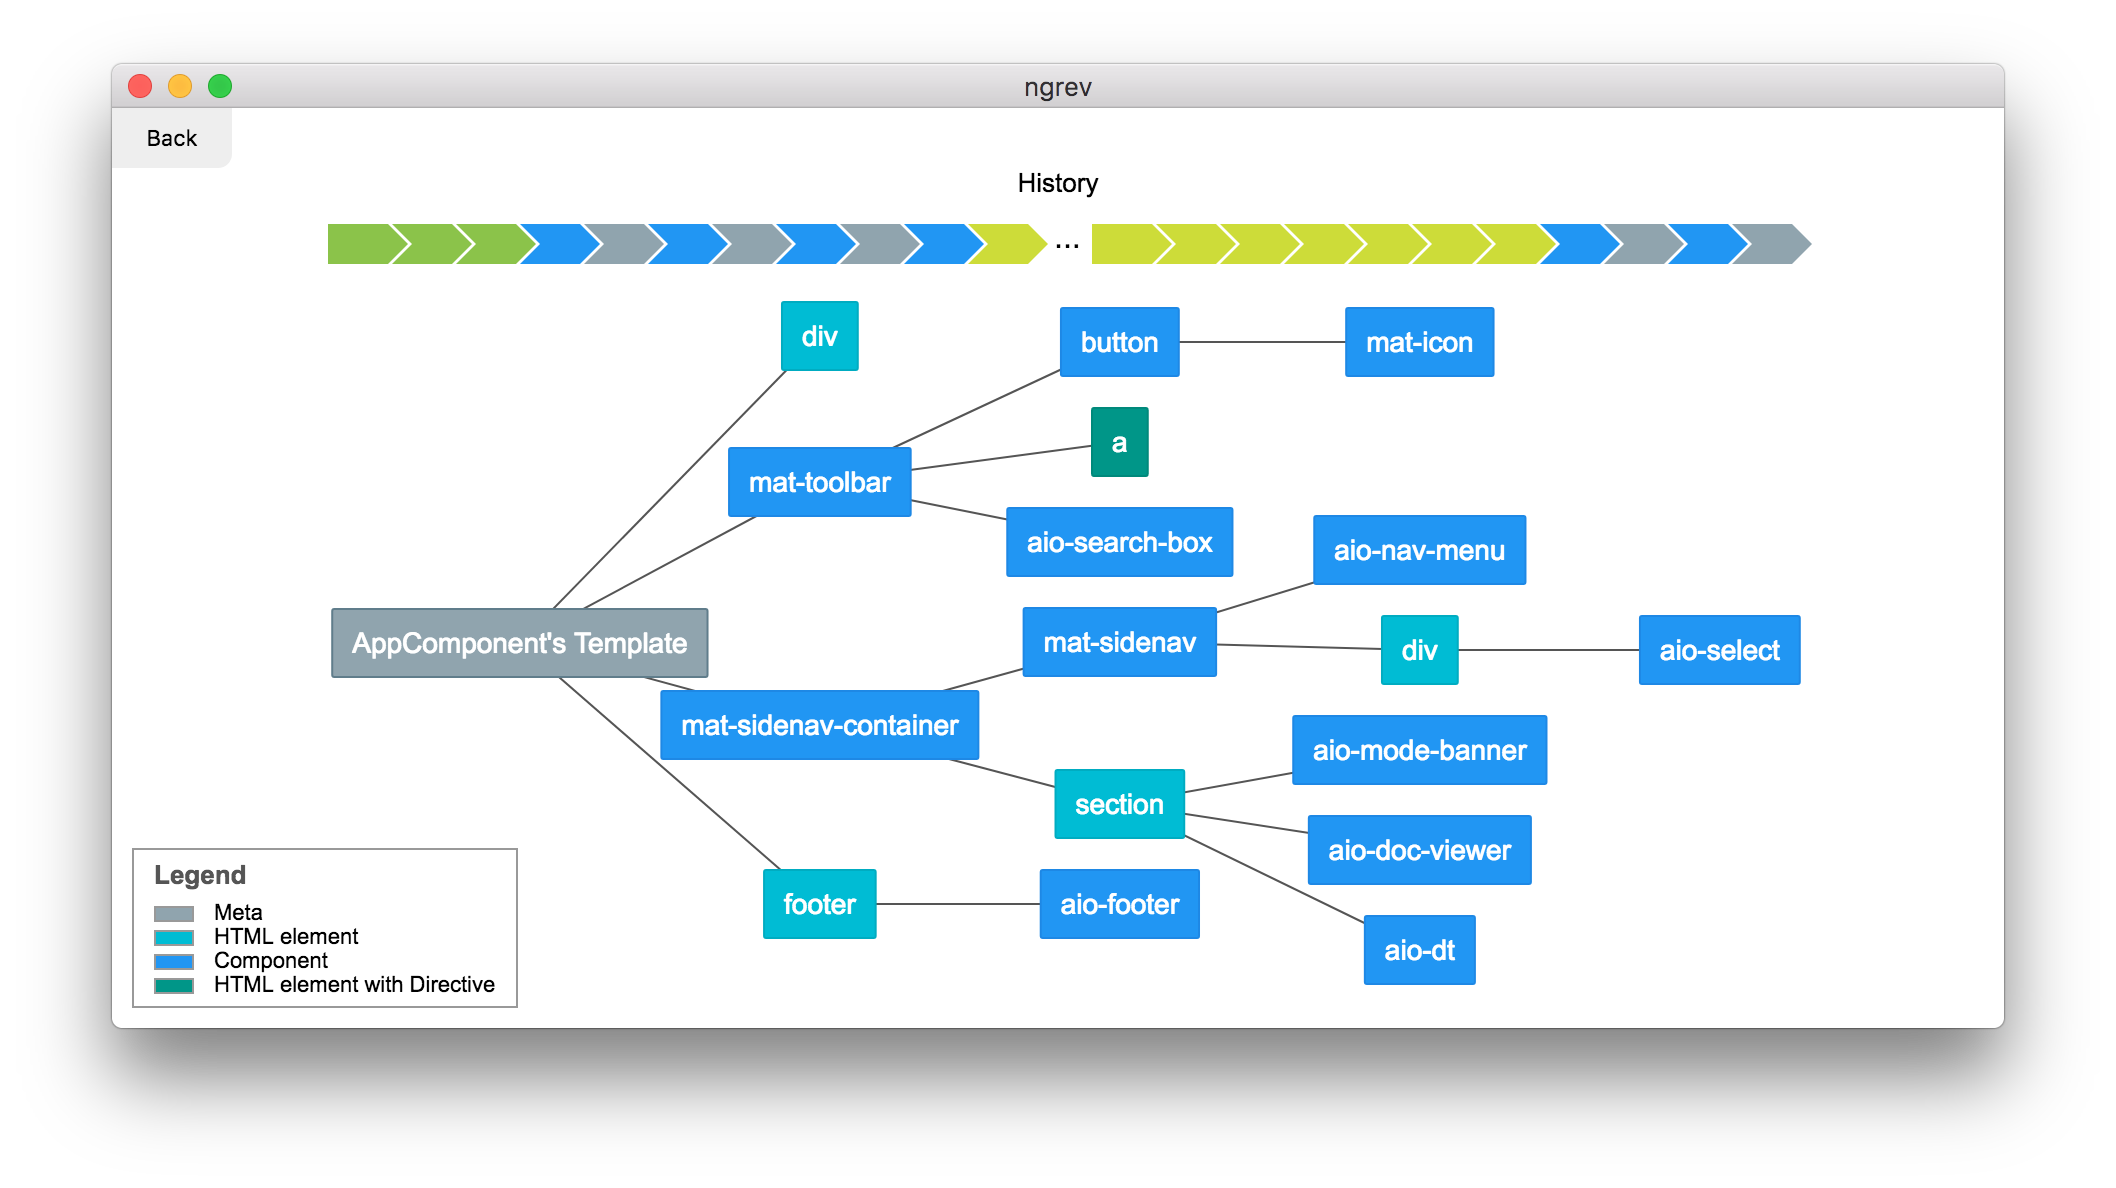 mgechev/ngrev
Tool for reverse engineering of Angular applications
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
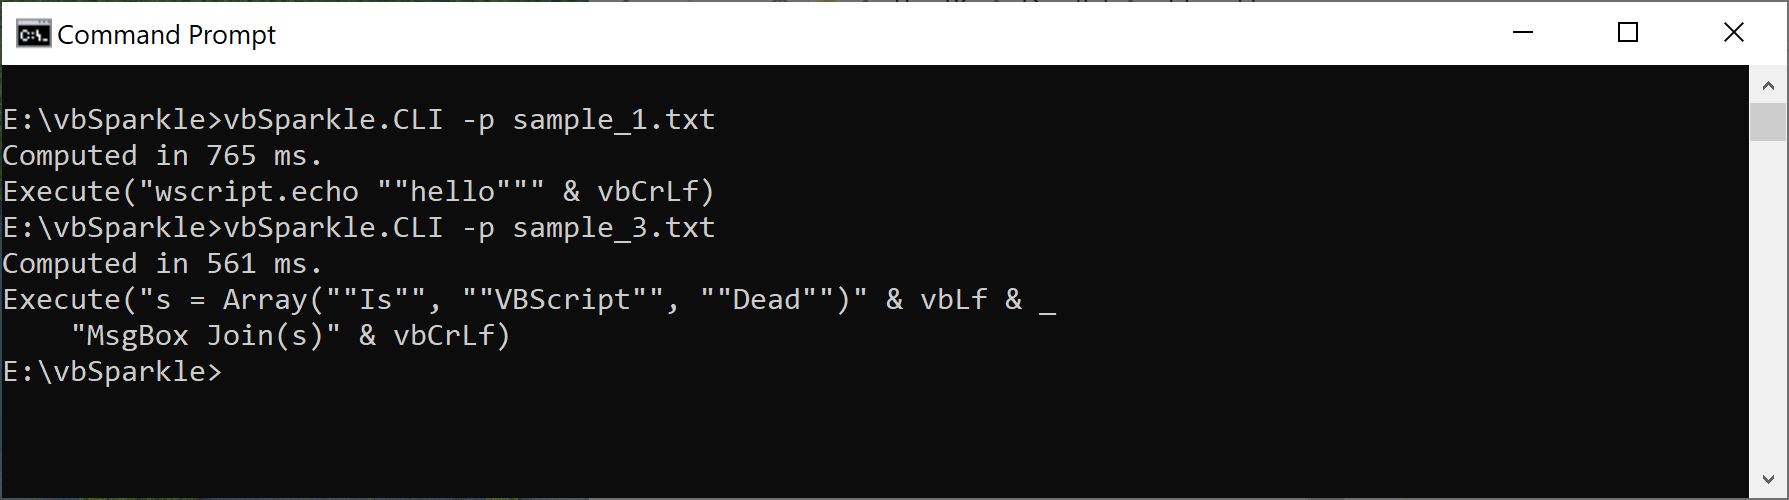 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
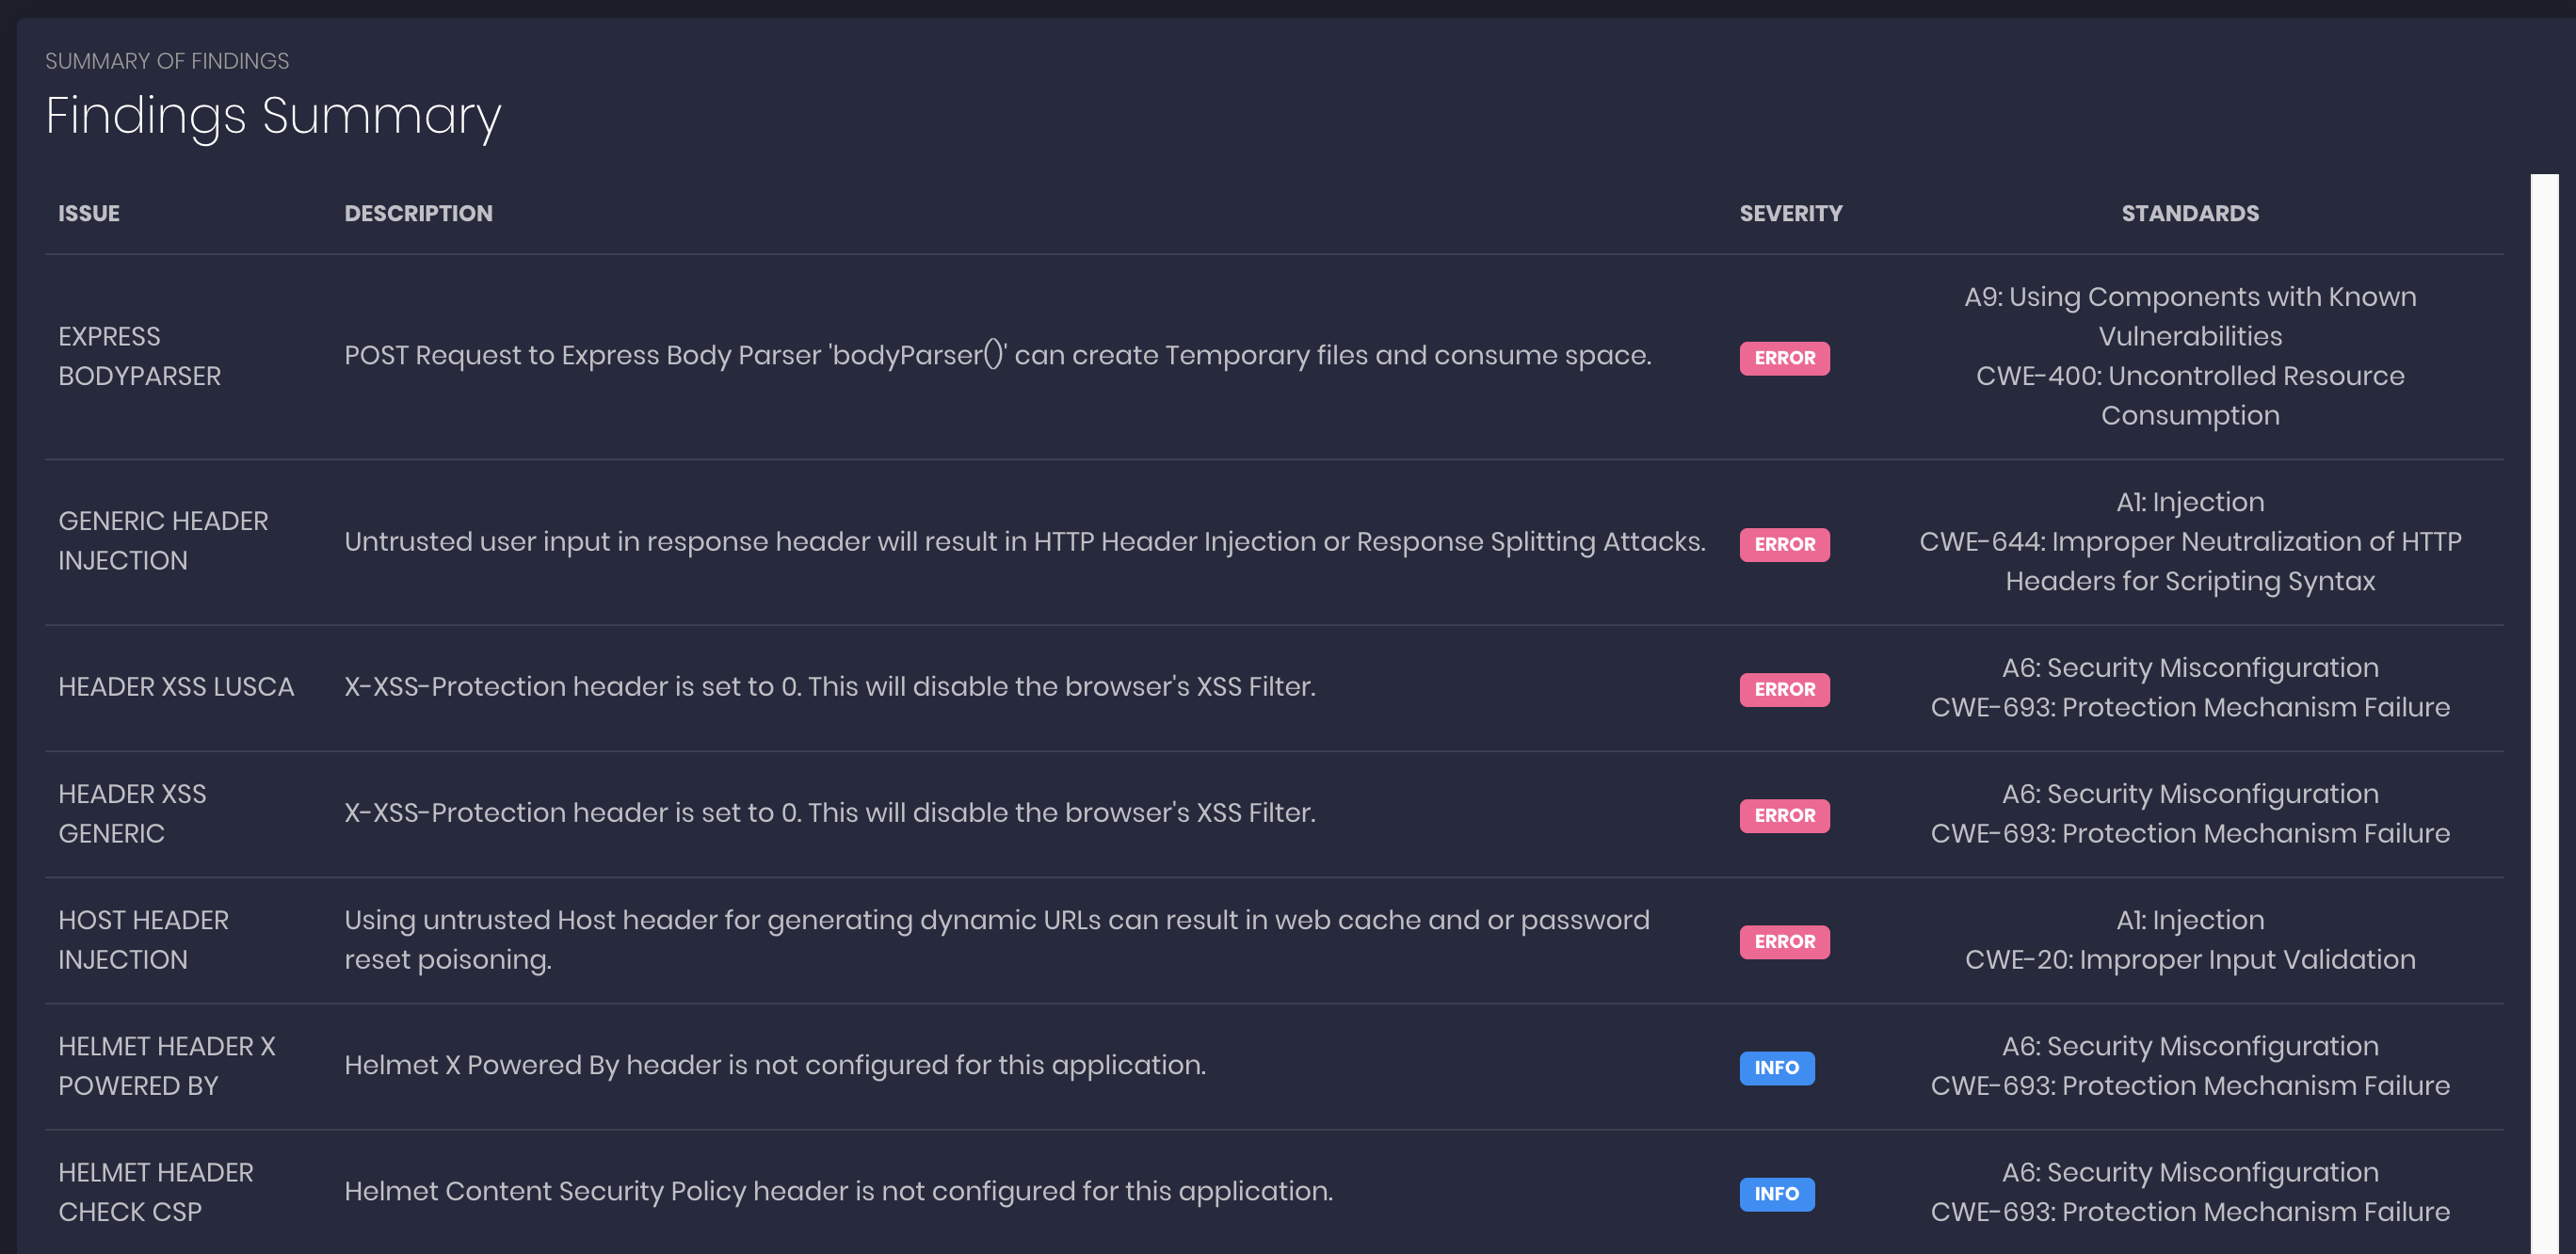 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.