

slowql
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
code-analysisconfiguration-auditingdatabase-security+6
220
slowql/slowqlNext-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 advanced-threat-research/creosote
Creosote is our solution to searching for the tarfile vulnerability described by CVE-2007-4559.

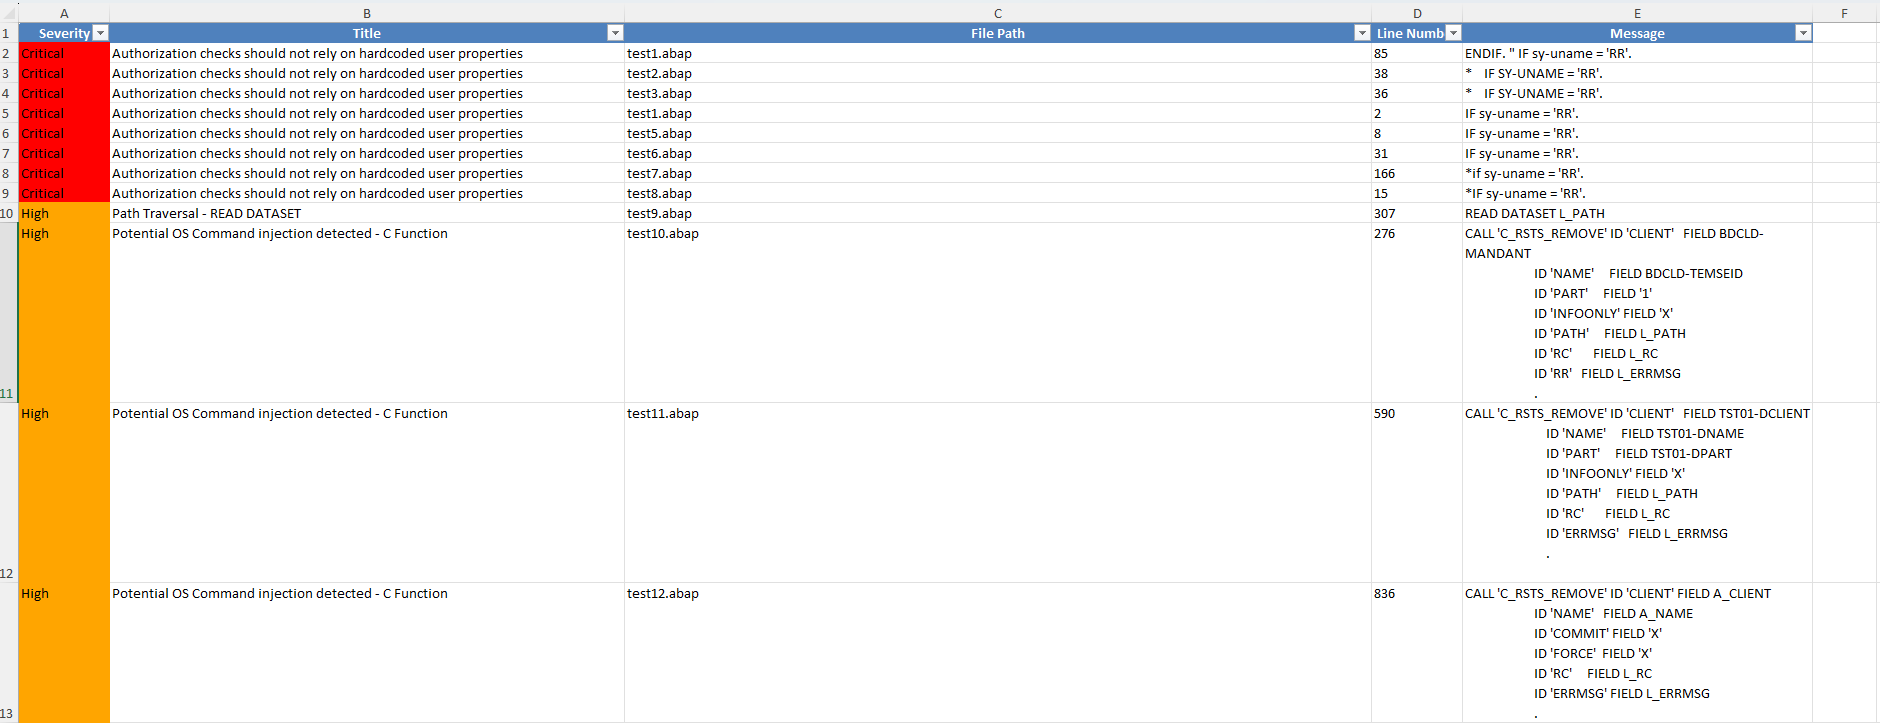
 nccgroup/cq
Fast code security scanner designed for manual security code review by experts. Outputs line-referenced findings to text files for easy filtering and…
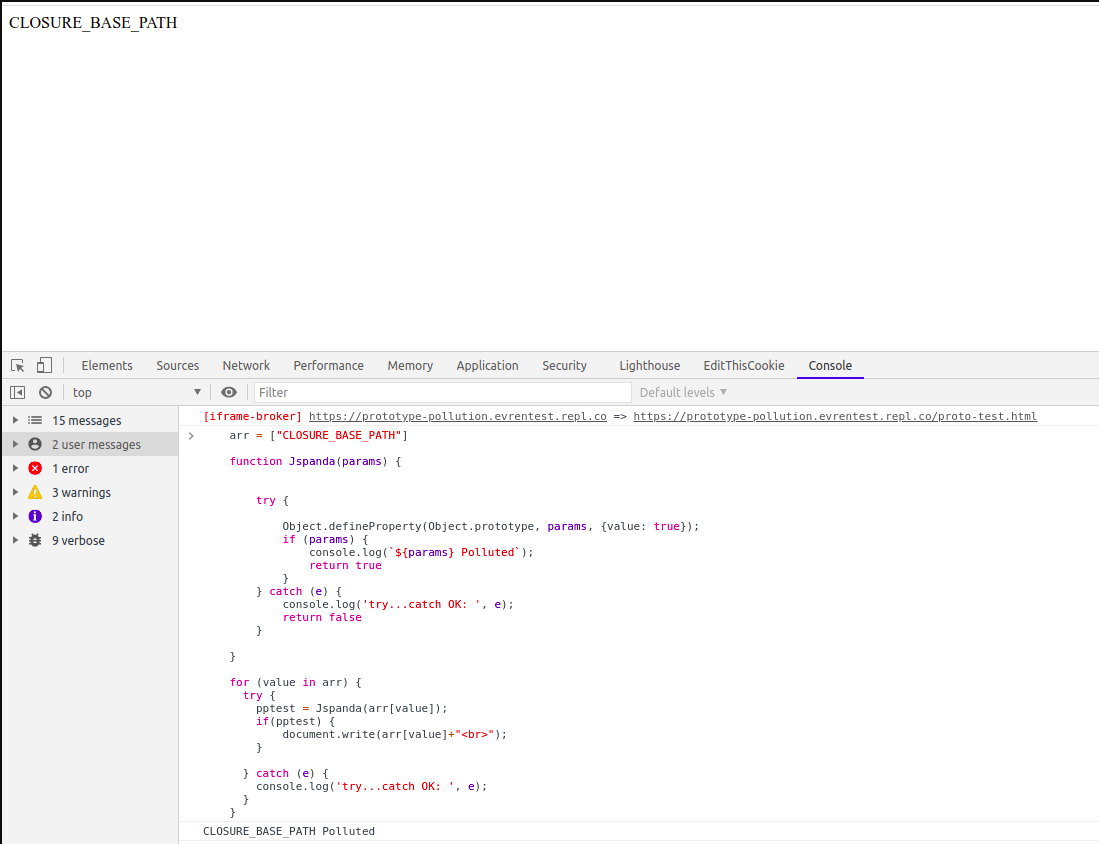 redsection/jspanda
client-side prototype pullution vulnerability scanner

 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
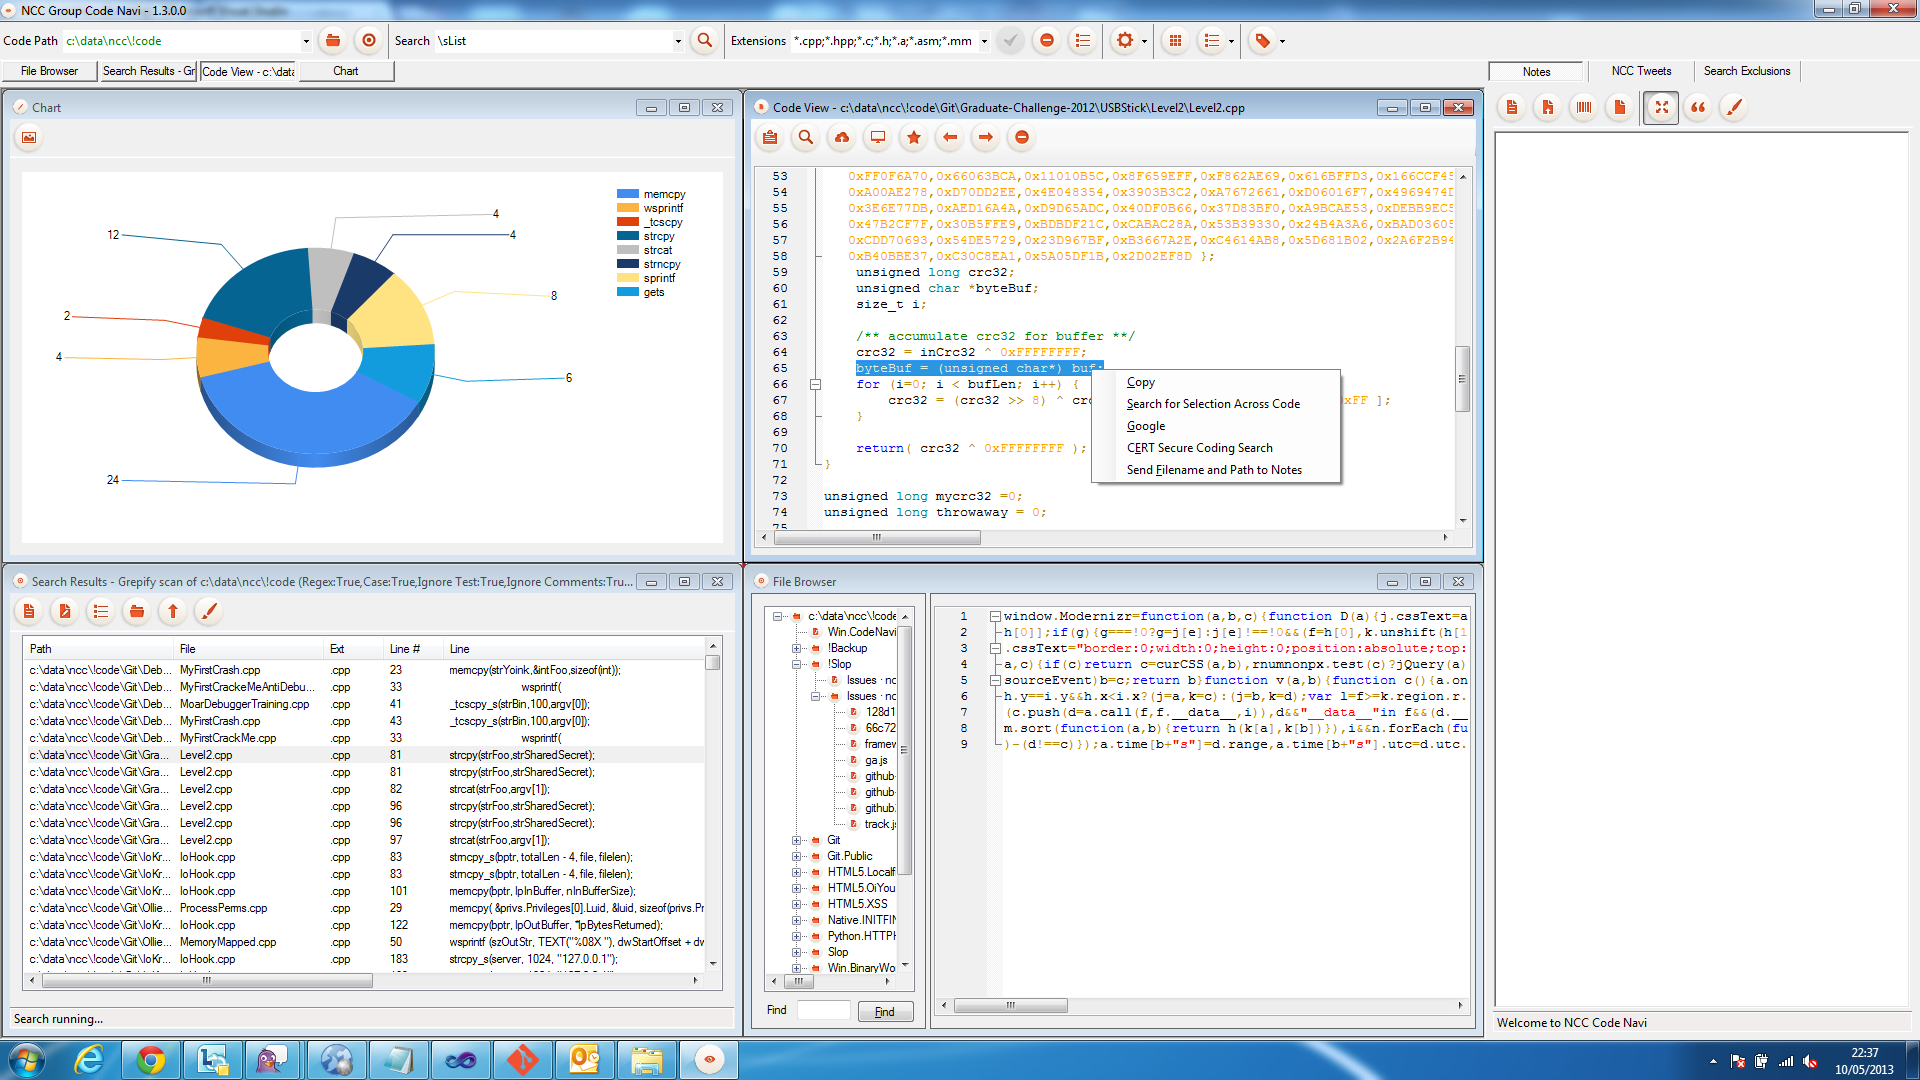 nccgroup/ncccodenavi
NCC Code Navigator
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
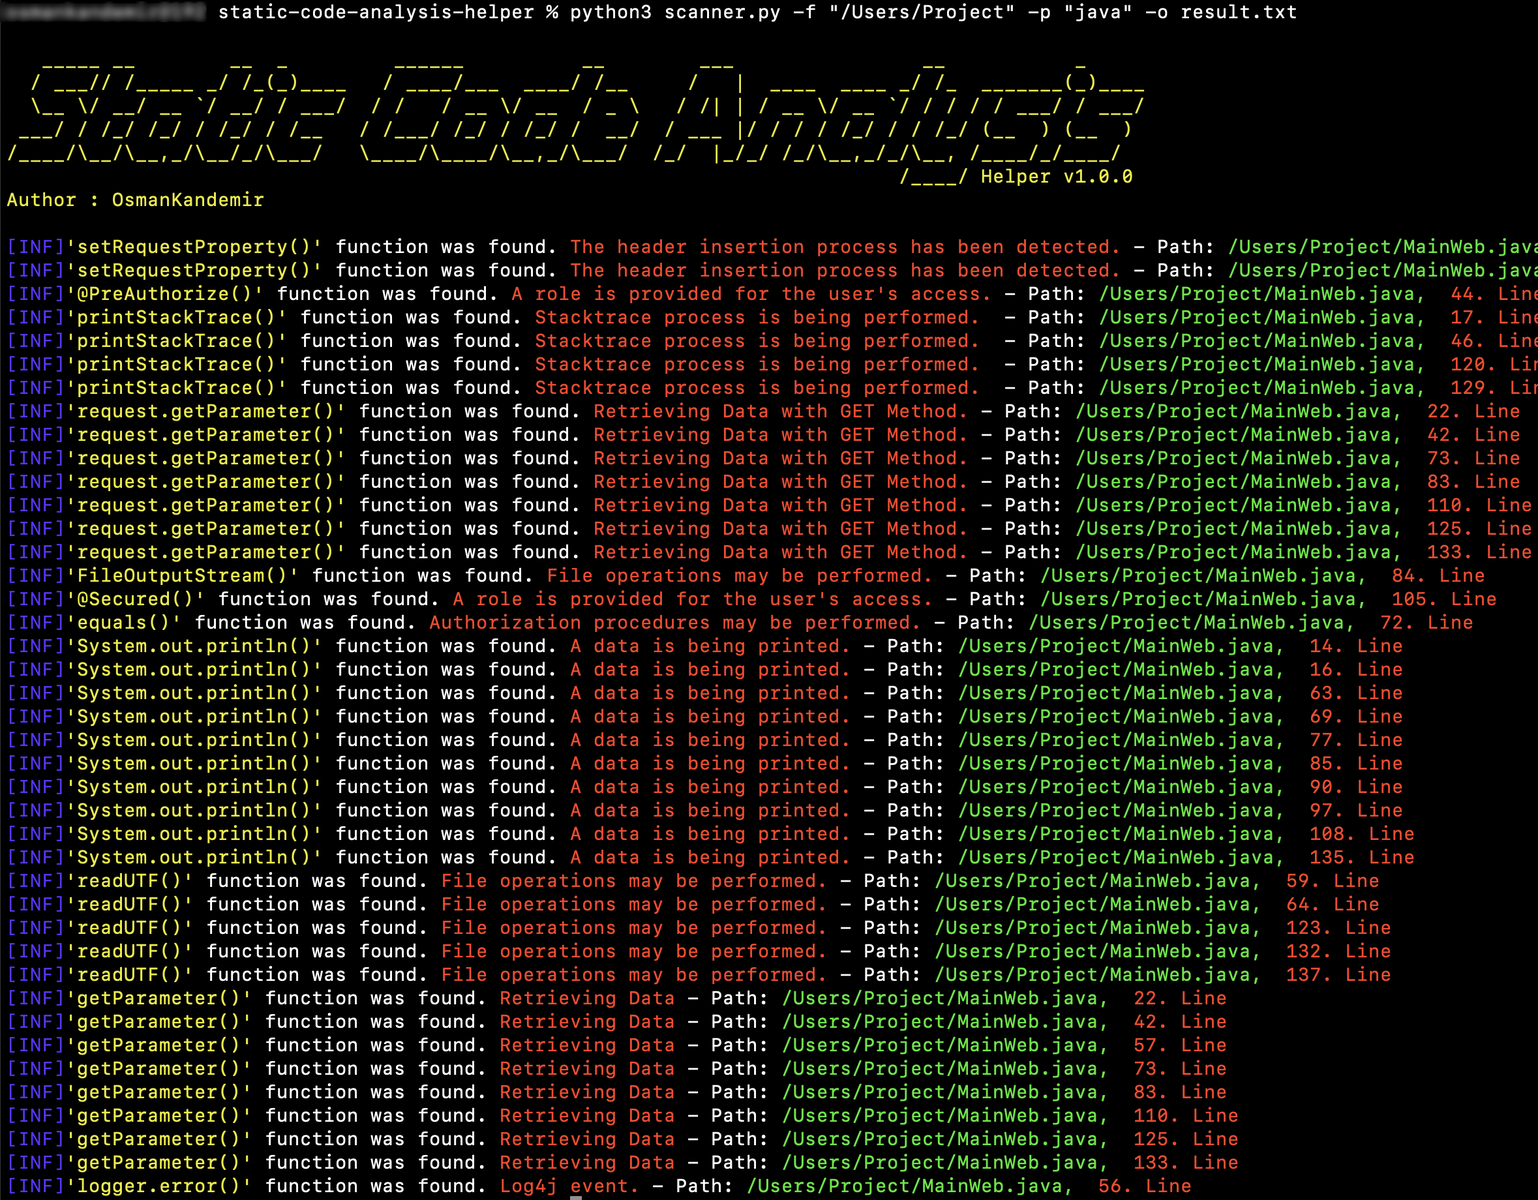 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…