
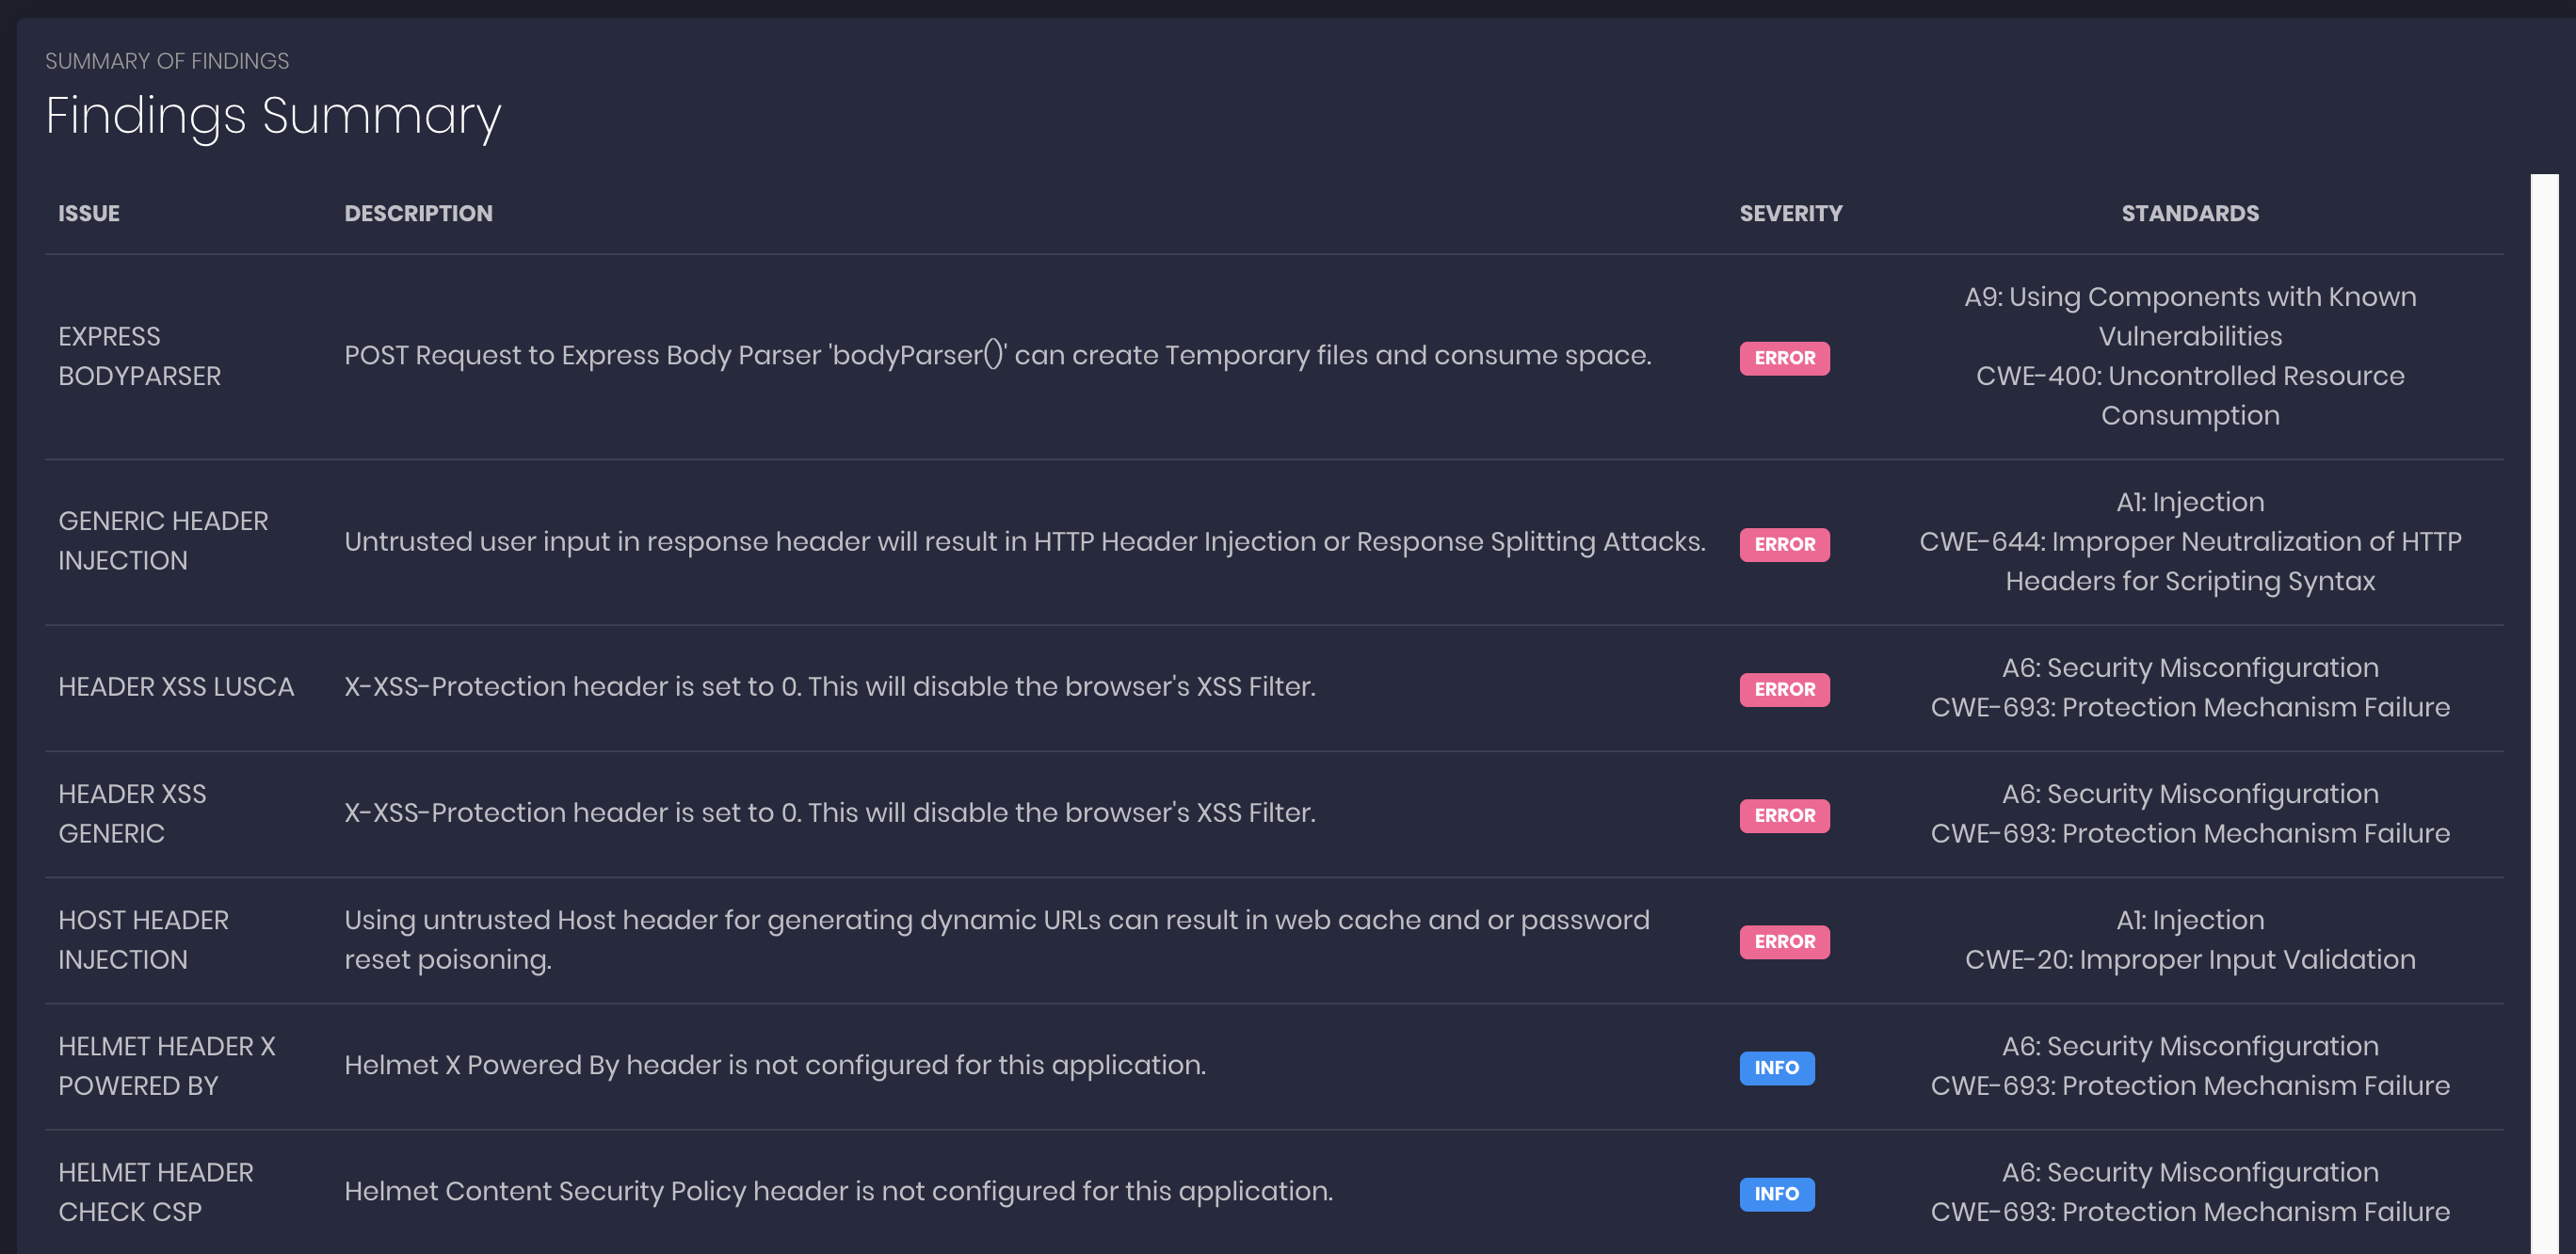
nodejsscan
 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
code-analysisdevsecopsstatic-analysis+3
ajinabraham/nodejsscannodejsscan is a static security code scanner for Node.js applications.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
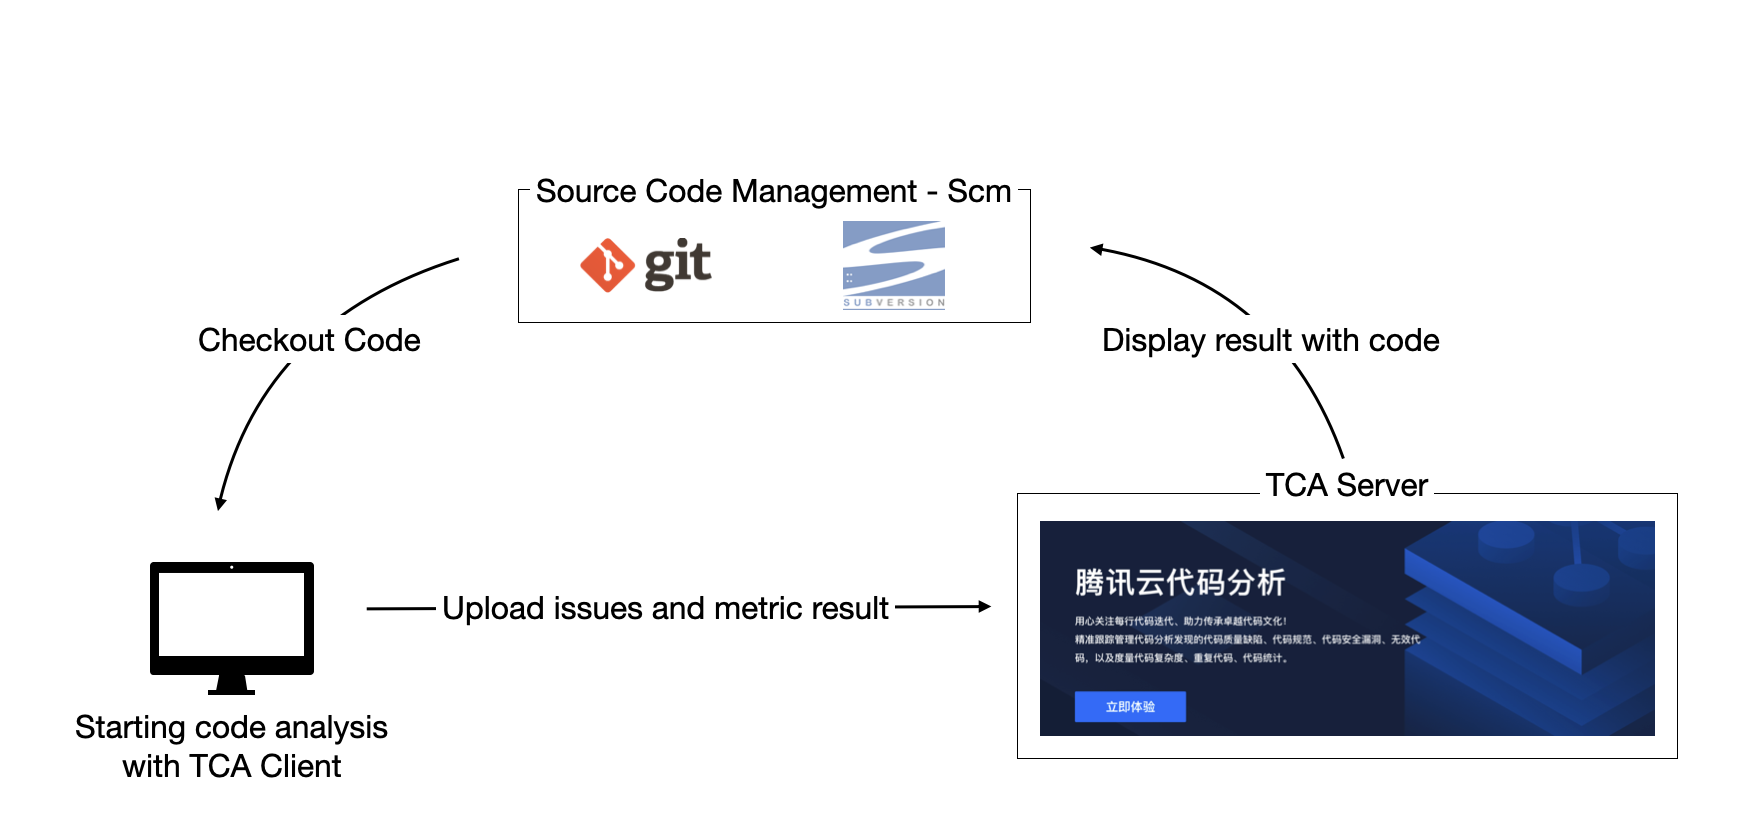 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
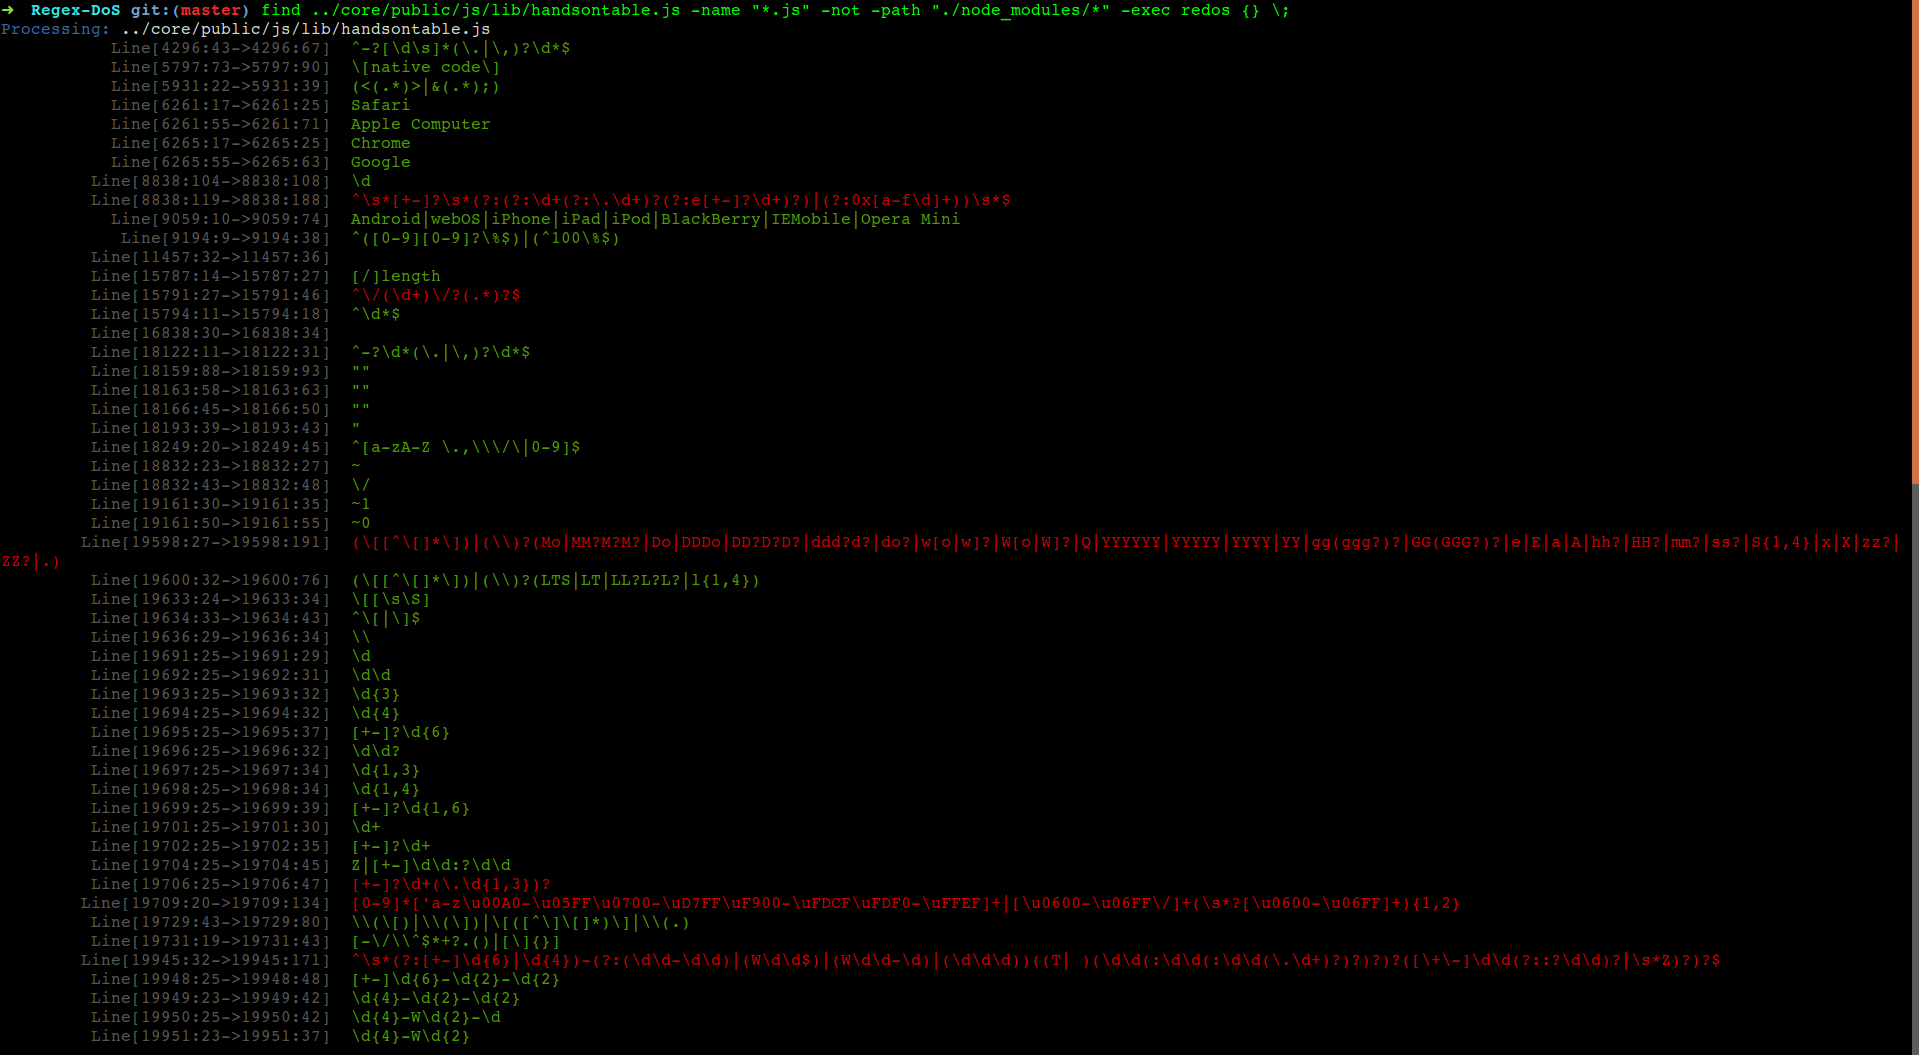 jagracey/regex-dos
👮 👊 RegEx Denial of Service (ReDos) Scanner

 gitlab-org/security-products/sast-rules
Curated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…
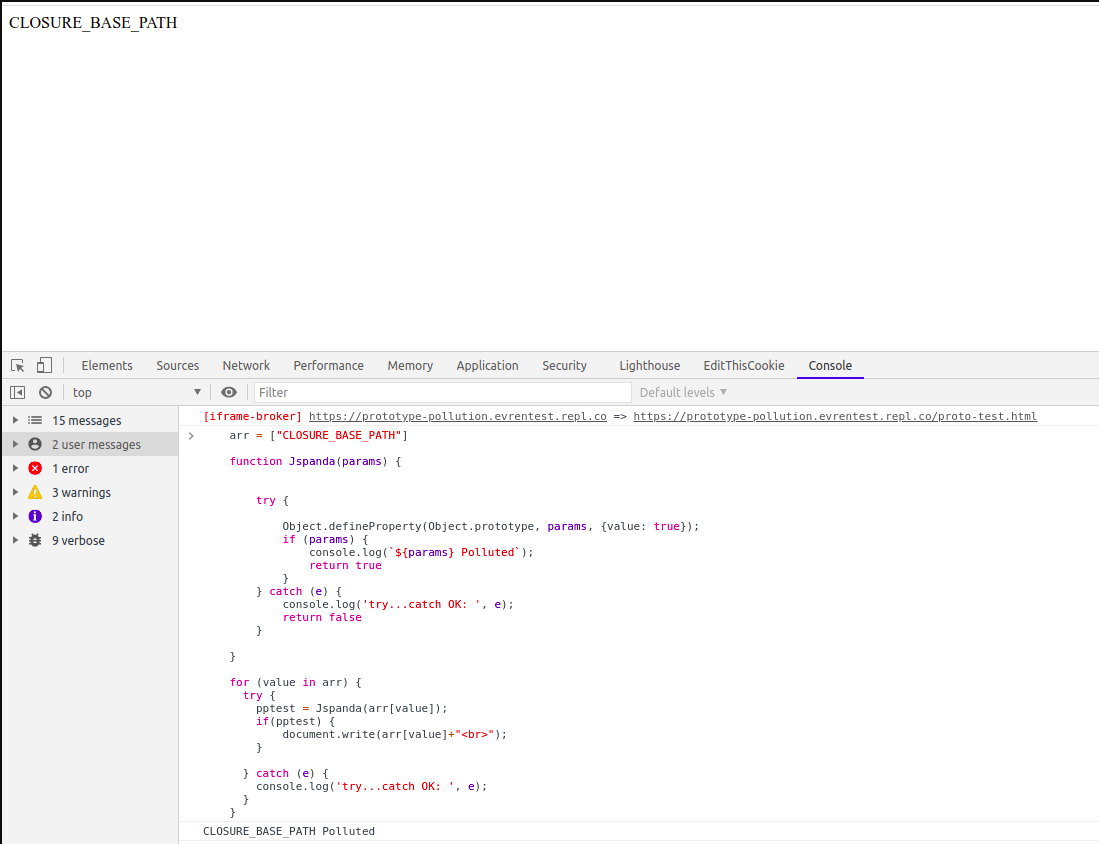 redsection/jspanda
client-side prototype pullution vulnerability scanner
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
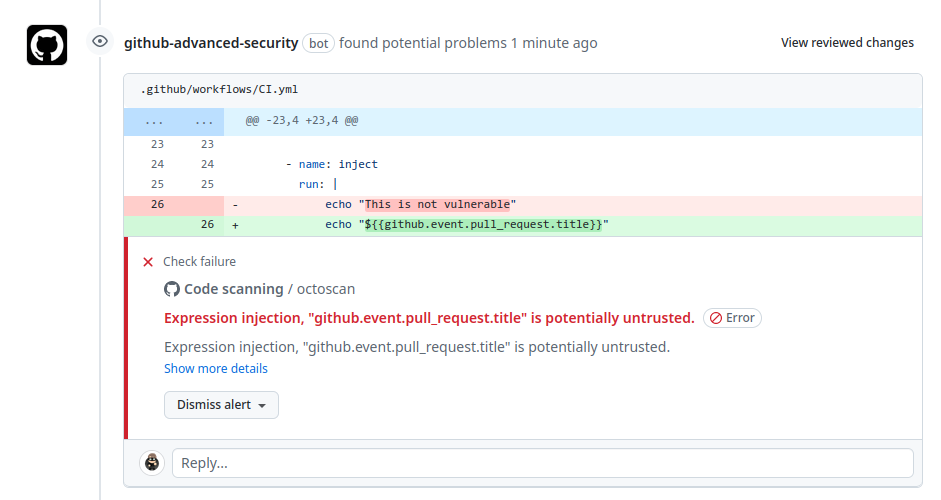 synacktiv/action-octoscan
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.
 nccgroup/matt.net
Matt.Net is a simple GUI wrapper around Microsoft's CAT.NET Code Auditing Tool