

sonarqube
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
code-analysisdevsecopsstatic-analysis+2
11.1k
sonarsource/sonarqubeCode-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
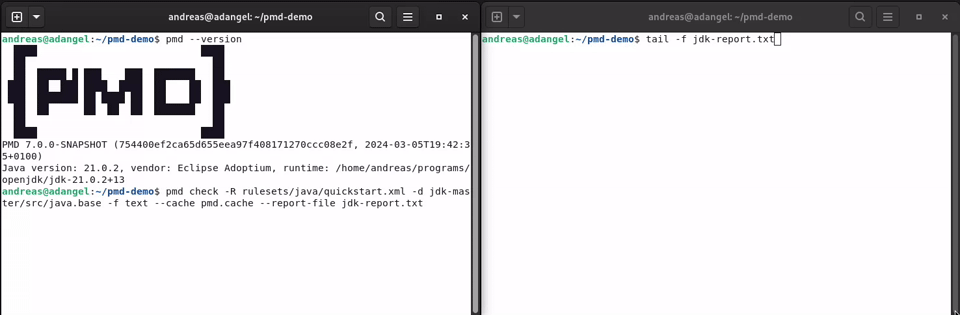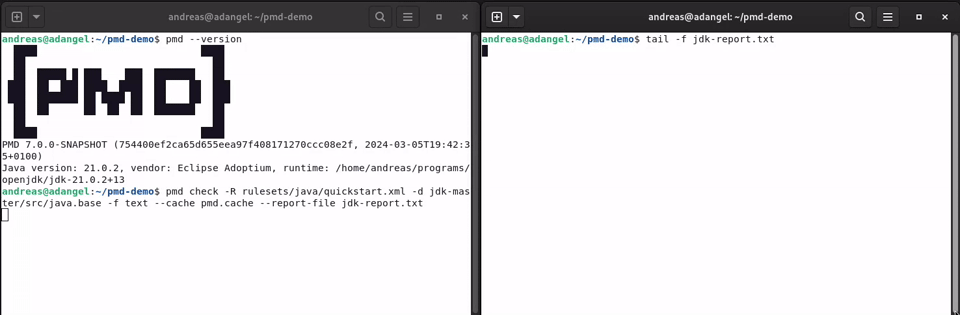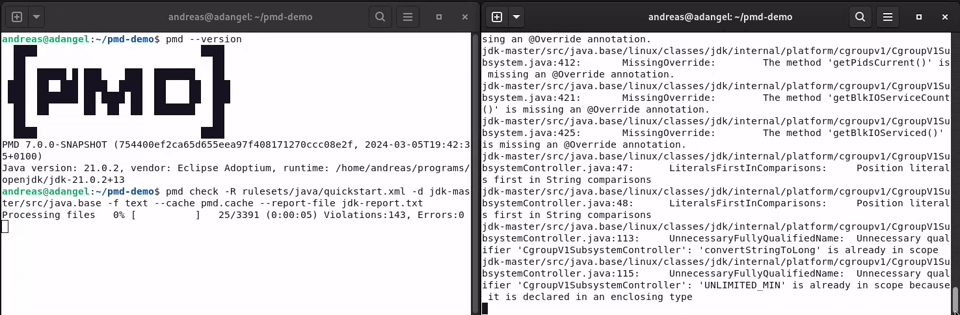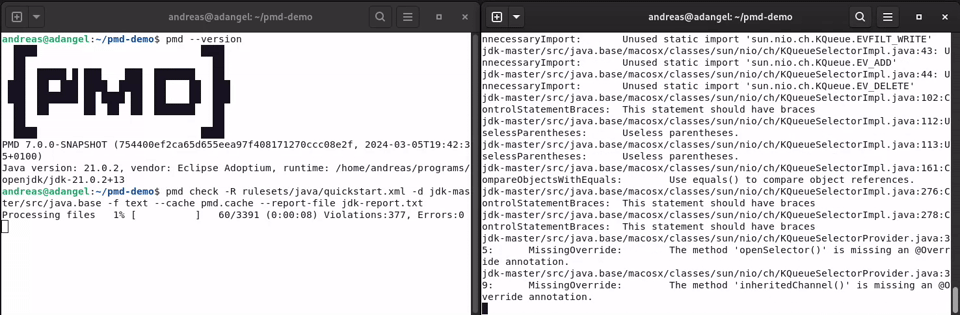 pmd/pmd
An extensible multilanguage static code analyzer.
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 zrax/pycdc
C++ python bytecode disassembler and decompiler
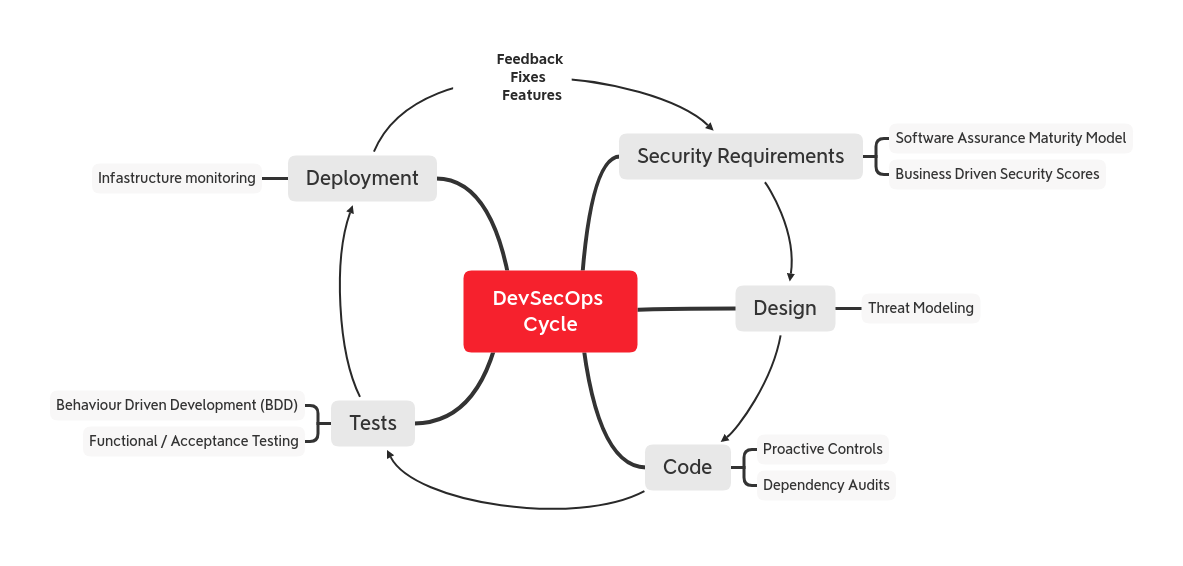 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 kadenzipfel/smart-contract-vulnerabilities
A collection of smart contract vulnerabilities along with prevention methods
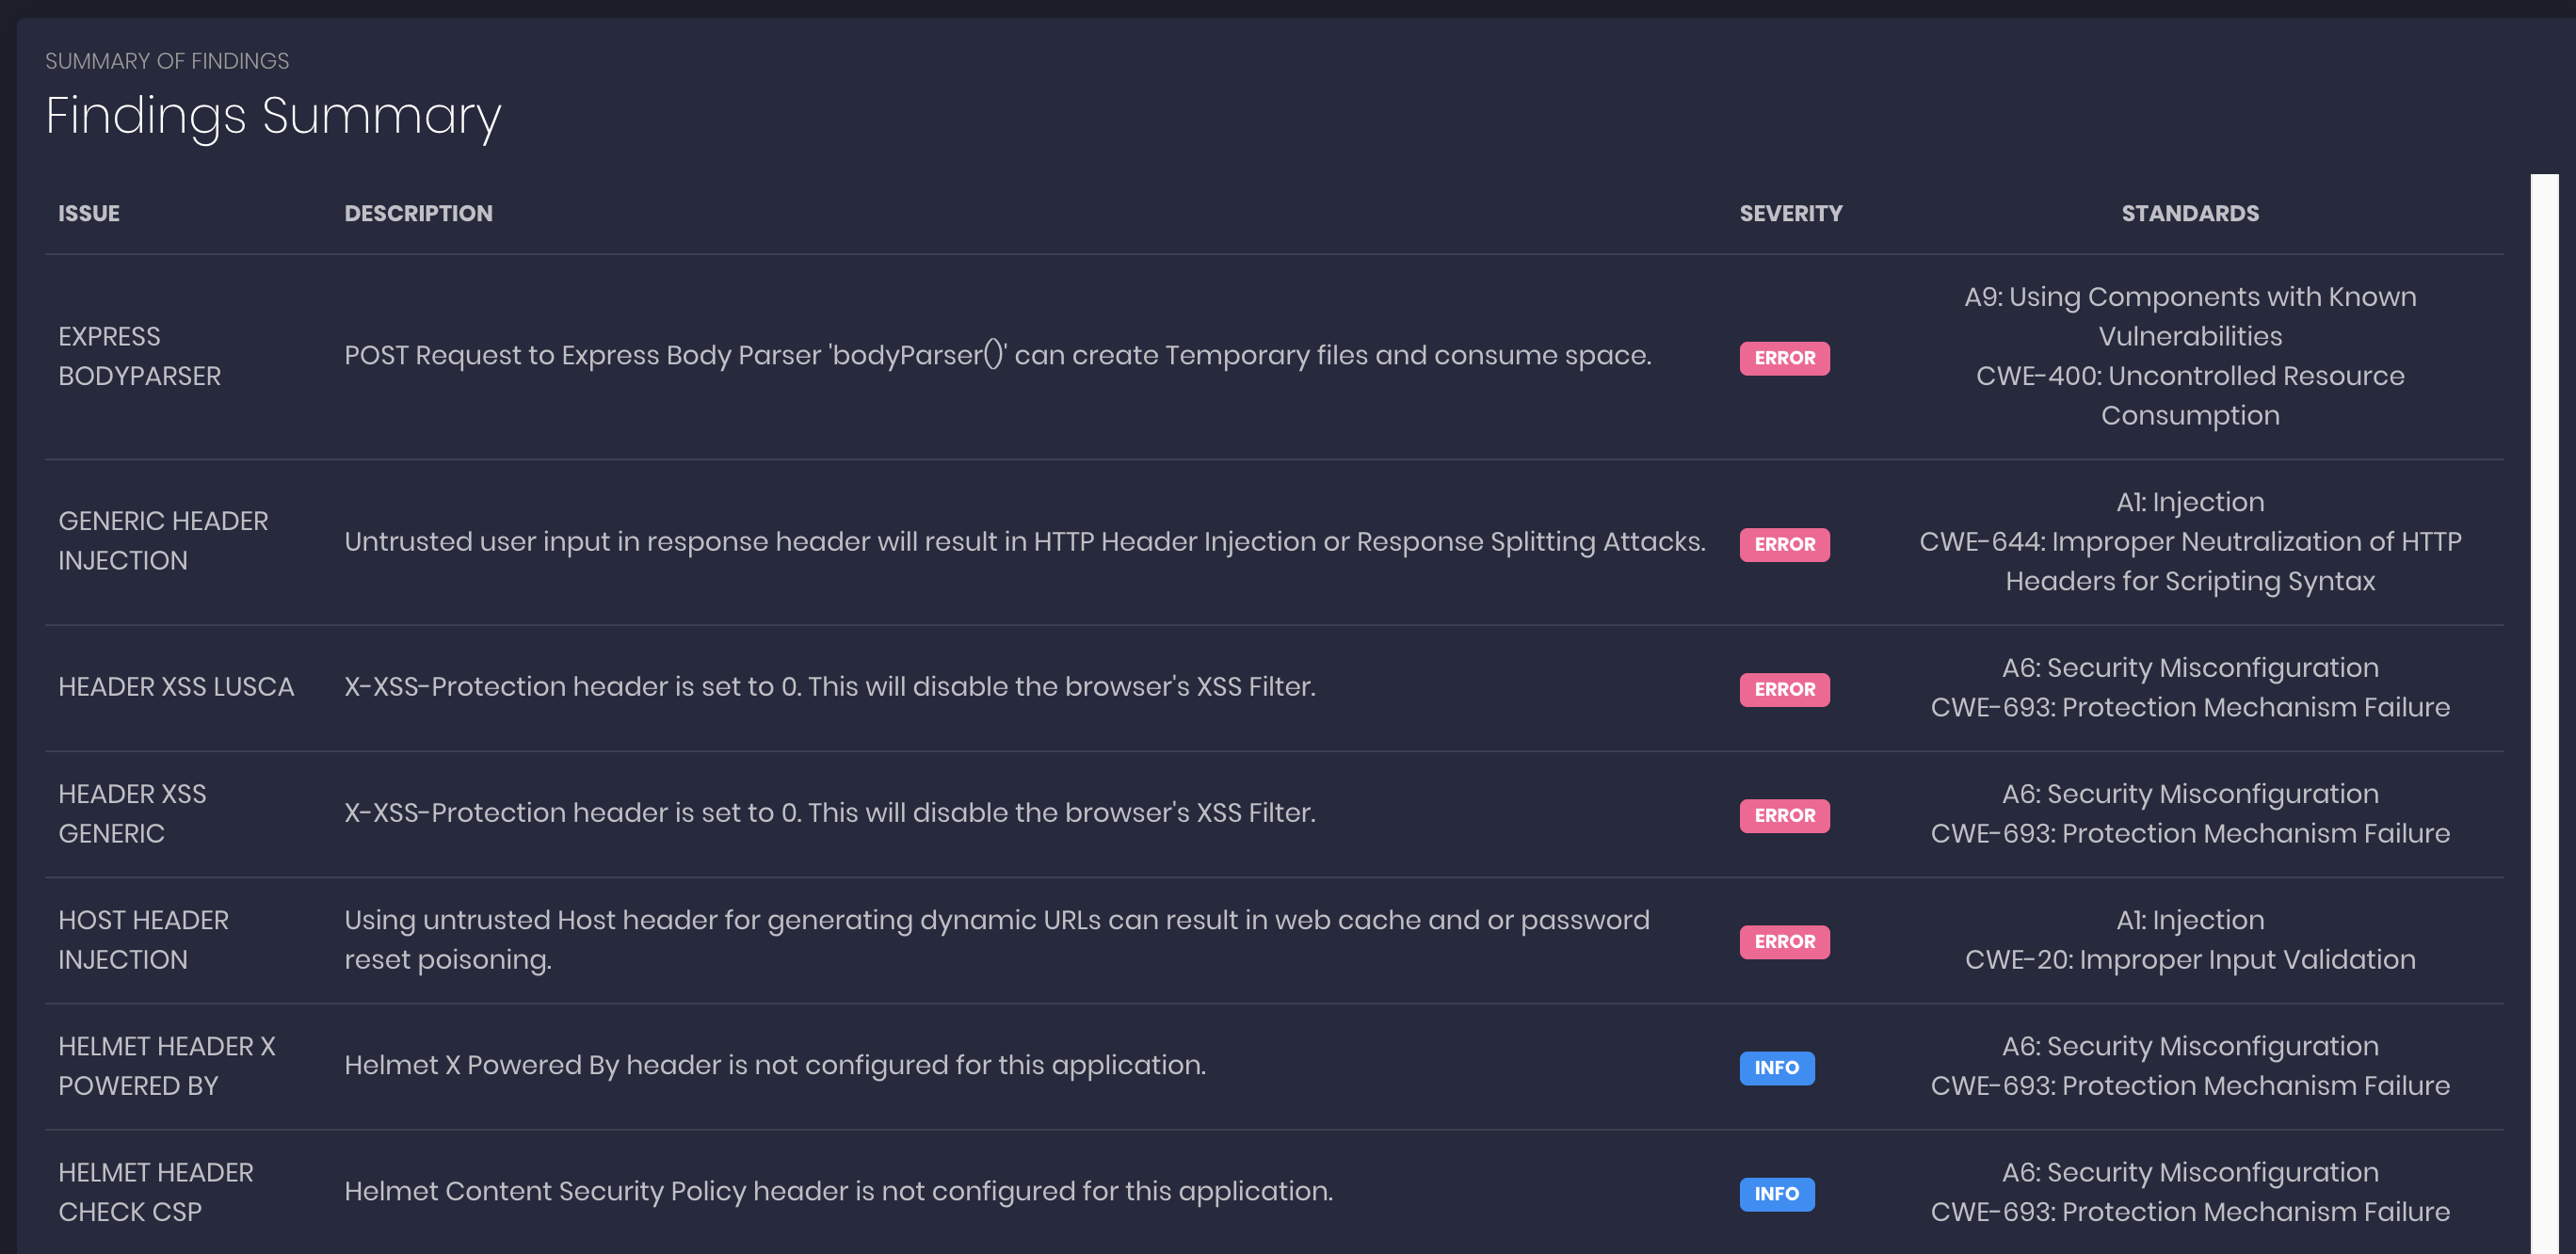 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 wireghoul/graudit
grep rough audit - source code auditing tool
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 0xdea/semgrep-rules
A collection of my Semgrep rules to facilitate vulnerability research.
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…