
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
177 results
SucoshScanny preview

SucoshScanny

GitHubmustafabilgici/sucoshscanny

"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…

code-analysissecret-detectionstatic-code-analysis+3
39
2 years ago
Vigil preview

Vigil

GitHubvigiloss/vigil

AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
ai-securitycode-analysisexploitation+9
311 day ago
static-code-analysis-helper preview

static-code-analysis-helper

GitHubosmankandemir/static-code-analysis-helper

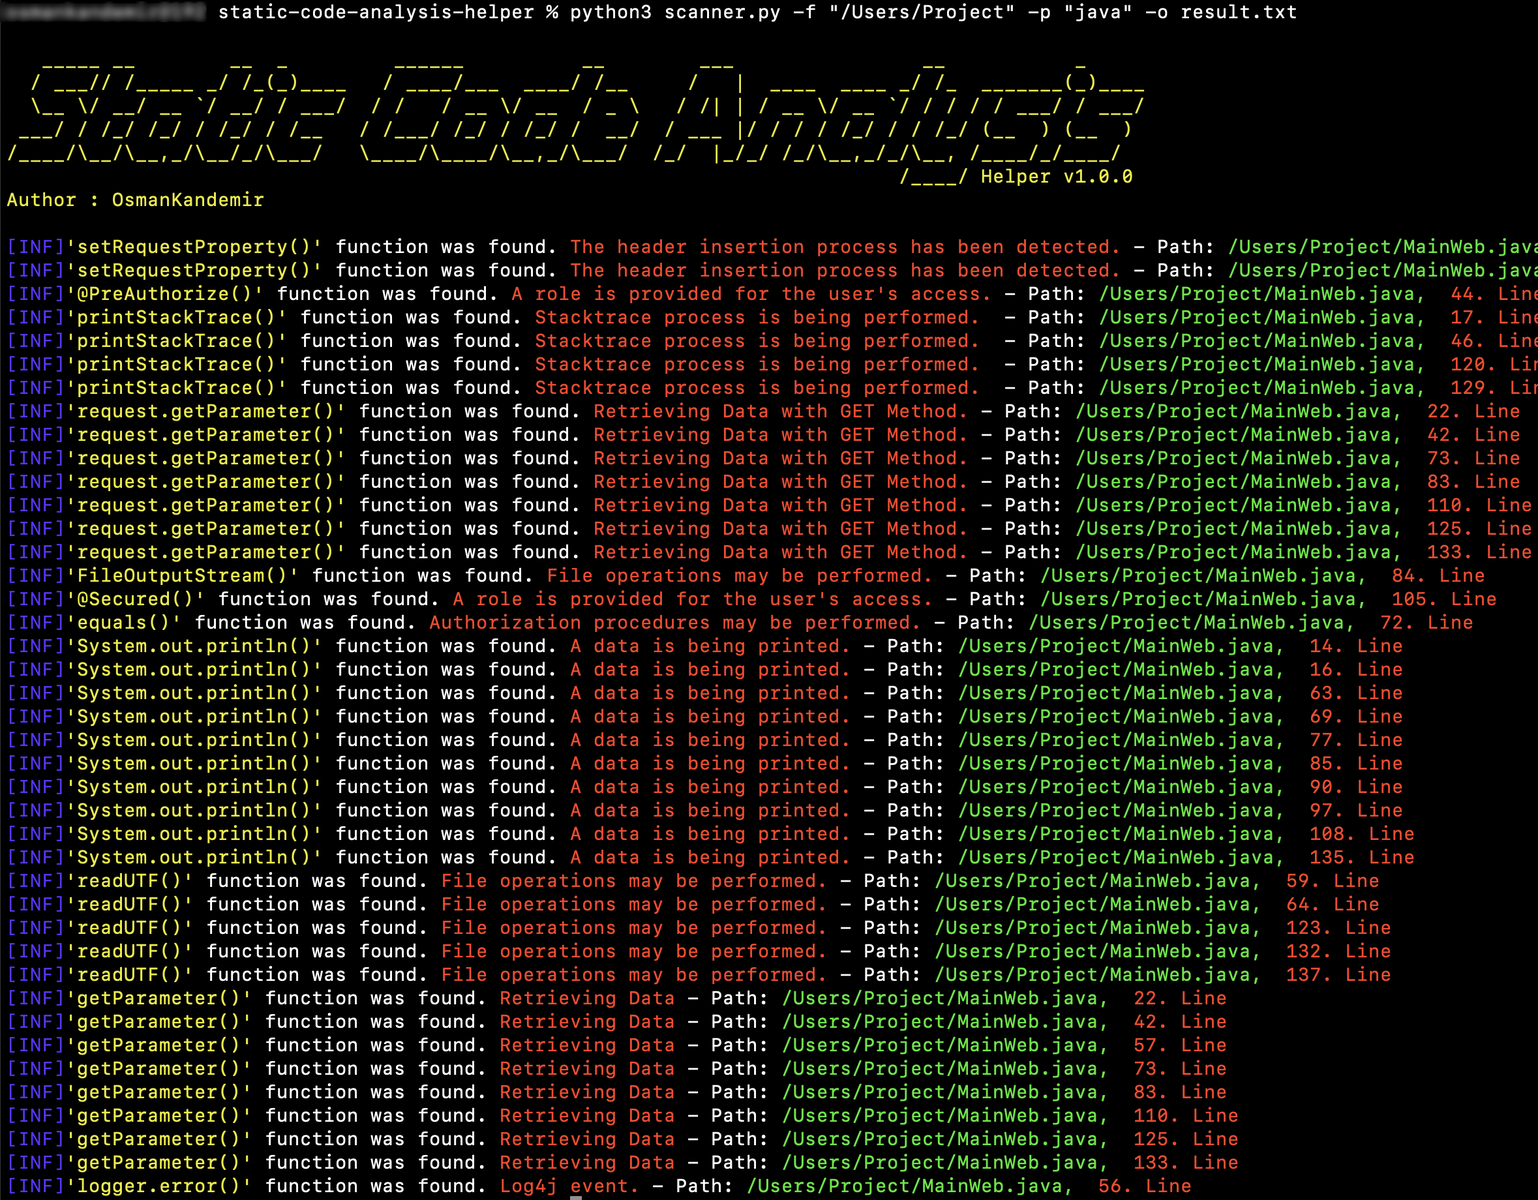
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
code-analysisstatic-code-analysisvulnerability-analysis+1
328 months ago
Weggli_rules_SSTIC2023 preview

Weggli_rules_SSTIC2023

GitHubsynacktiv/weggli_rules_sstic2023

Curated weggli queries for static analysis of C/C++ code to identify dangerous functions, stack issues, and malloc overflow vulnerabilities.
code-analysiscurated-resourcesstatic-code-analysis+1
323 years ago
airflowscan preview

airflowscan

GitHubnightwatchcybersecurity/airflowscan

Checklist and tools for increasing security of Apache Airflow

cloud-securityconfiguration-auditingdevsecops+2
325 years ago
cryptoptic preview

cryptoptic

GitHubnationwide-group-oss/cryptoptic

CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…

code-analysisconfiguration-auditingcryptography+6
191 month ago
appledb_rs preview

appledb_rs

GitHubsynacktiv/appledb_rs

Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
curated-resourcesinformation-gatheringios-security+3
271 year ago
contrast preview

contrast

GitHubcontrastsecurity/contrast

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…

cloud-infrastructure-securitycloud-securitycode-analysis+6
204 years ago
VulnFanatic-NG preview

VulnFanatic-NG

GitHubmartyx00/vulnfanatic-ng

BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.

ai-assisted-reversingbinary-analysiscode-analysis+9
144 months ago
CanoP preview

CanoP

GitHubopenbreach/canop

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
ai-securitycode-analysisdefensive-tools+7
74 days ago
CVE-2024-57521-RuoYi-SQLi preview

CVE-2024-57521-RuoYi-SQLi

GitHubxs2024770/cve-2024-57521-ruoyi-sqli

Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
educationexploitationpapers-research+4
1 month ago
o1js-scan preview

o1js-scan

GitHubauditinfra-io/o1js-scan

Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
code-analysiscryptographydefensive-tools+5
321 days ago
nullorigin preview

nullorigin

GitHubrakib-nyc/nullorigin

Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
adversarial-attackai-securityeducation+4
52 months ago
advisory preview

advisory

GitHubcarlosalbertotuma/advisory

Public security advisories and PoCs for vulnerabilities discovered in open-source web software, with root-cause analysis, CVE references,…

code-analysiscurated-resourceseducation+7
21 month ago
gitgalaxy preview

gitgalaxy

GitLabsquid-protocol1/gitgalaxy

AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…

code-analysisdevsecopsmalware-analysis+3
1 month ago
Deserializer preview

Deserializer

GitHubjoshuaprovoste/deserializer

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

ai-securitycode-analysisexploitation+6
21 day ago
sast preview

sast

GitHubvulnz/sast

Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…

cloud-securitycode-analysisdefensive-tools+9
26 days ago
TriSuElla-AIDLCA-Framework preview

TriSuElla-AIDLCA-Framework

GitHubowasp/trisuella-aidlca-framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

ai-securitycloud-securitycode-analysis+7
31 month ago
Previous1…345…10Next