

advisory
 carlosalbertotuma/advisory
Public security advisories and PoCs for vulnerabilities discovered in open-source web software, with root-cause analysis, CVE references,…
code-analysiscurated-resourceseducation+7
2
carlosalbertotuma/advisoryPublic security advisories and PoCs for vulnerabilities discovered in open-source web software, with root-cause analysis, CVE references,…
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…

 daveyd347/self-hosted-ctf-platform
Self-hosted CTF: original web challenges + scoreboard, deployed with Docker Compose via GitLab CI and a GitOps agent. Flags derived from one CI…
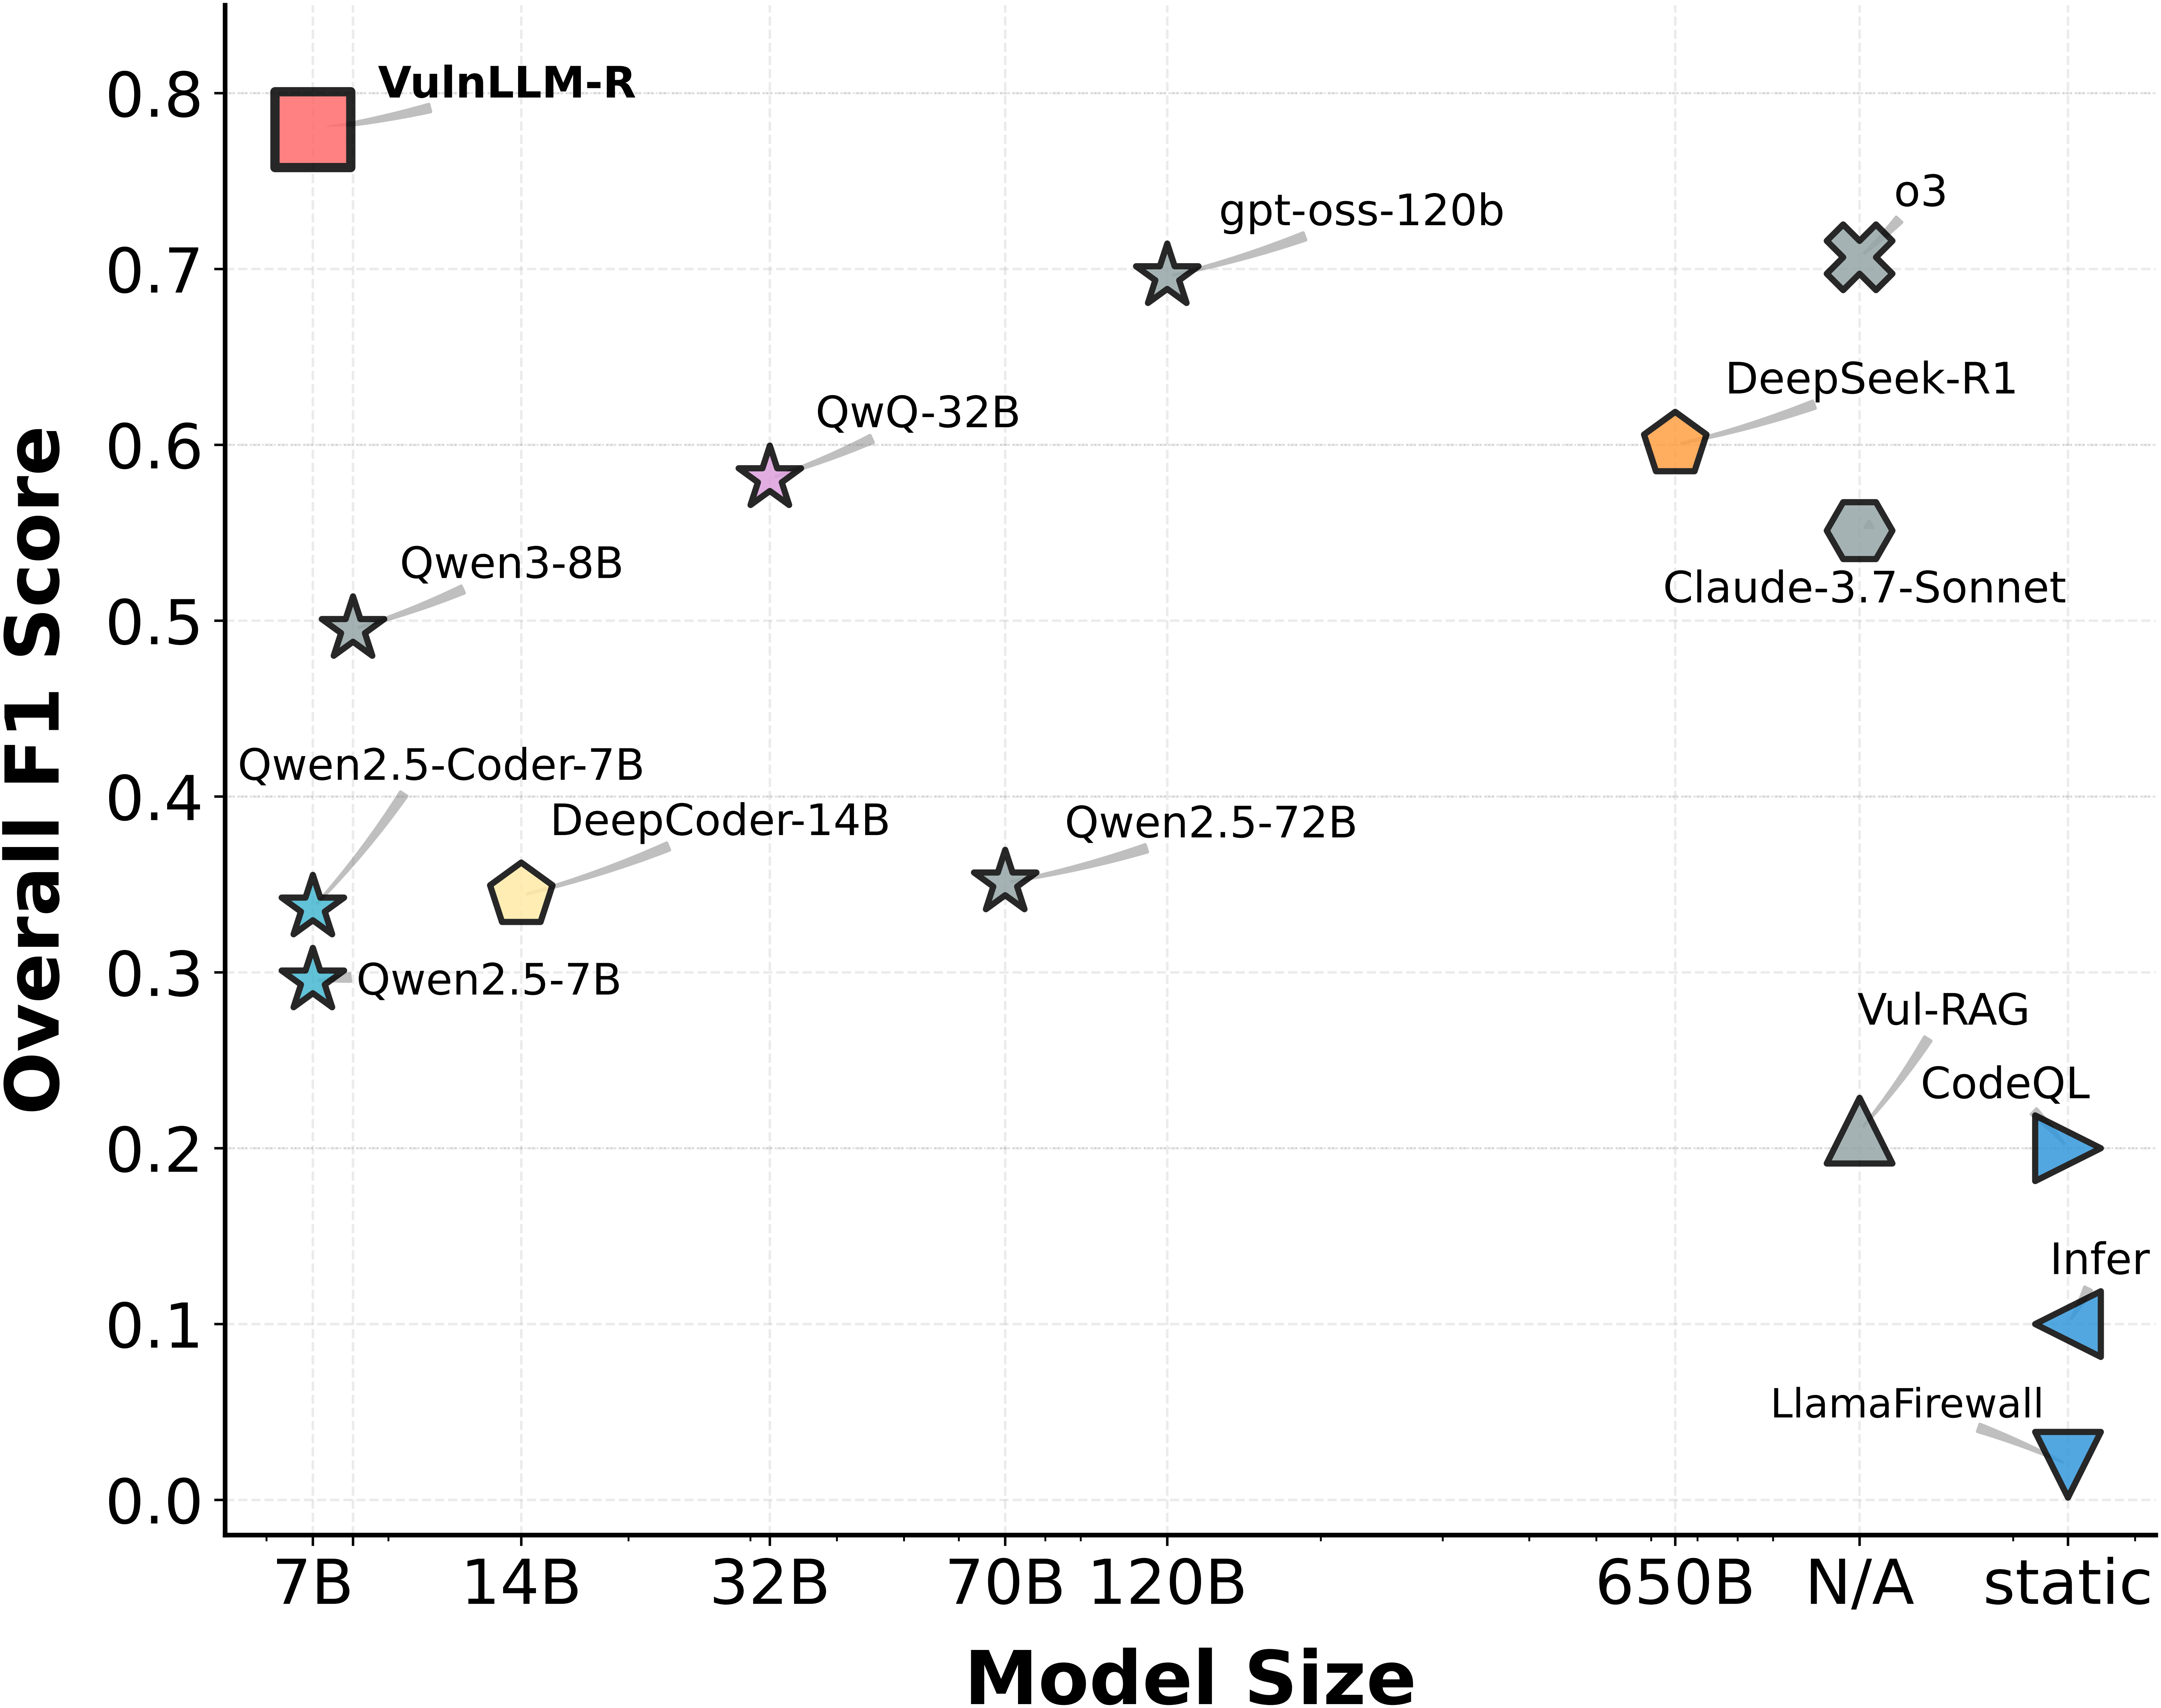 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…

 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 skyscanner/lambdaguard
AWS Serverless Security
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.