seclab-taskflow-agent

MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…

MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…

a static analysis tool for finding vulnerabilities in C/C++ source code

Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…

MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.

RIPS - A static source code analyser for vulnerabilities in PHP scripts

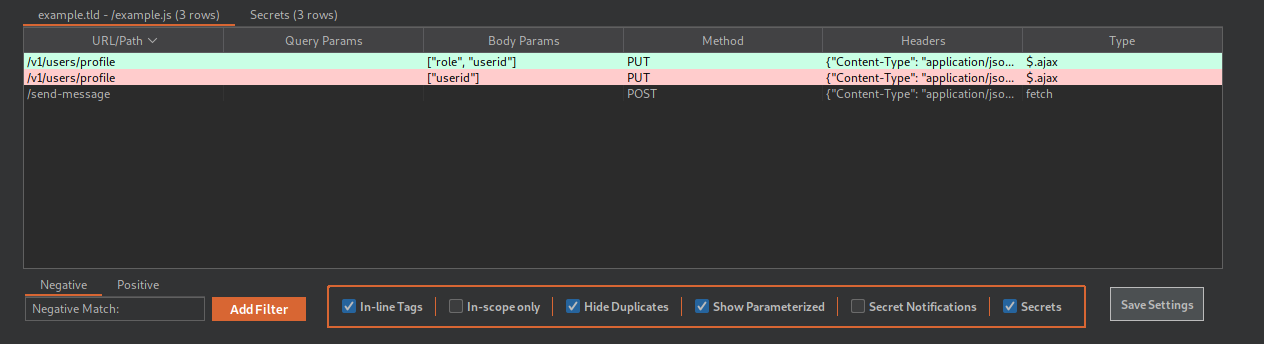
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice

RAM efficient terminal agent harness for coding, cybersecurity, and automation.

Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment

Creosote is our solution to searching for the tarfile vulnerability described by CVE-2007-4559.

A variant analysis and visualisation tool that scans codebases for similar vulnerabilities

Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…


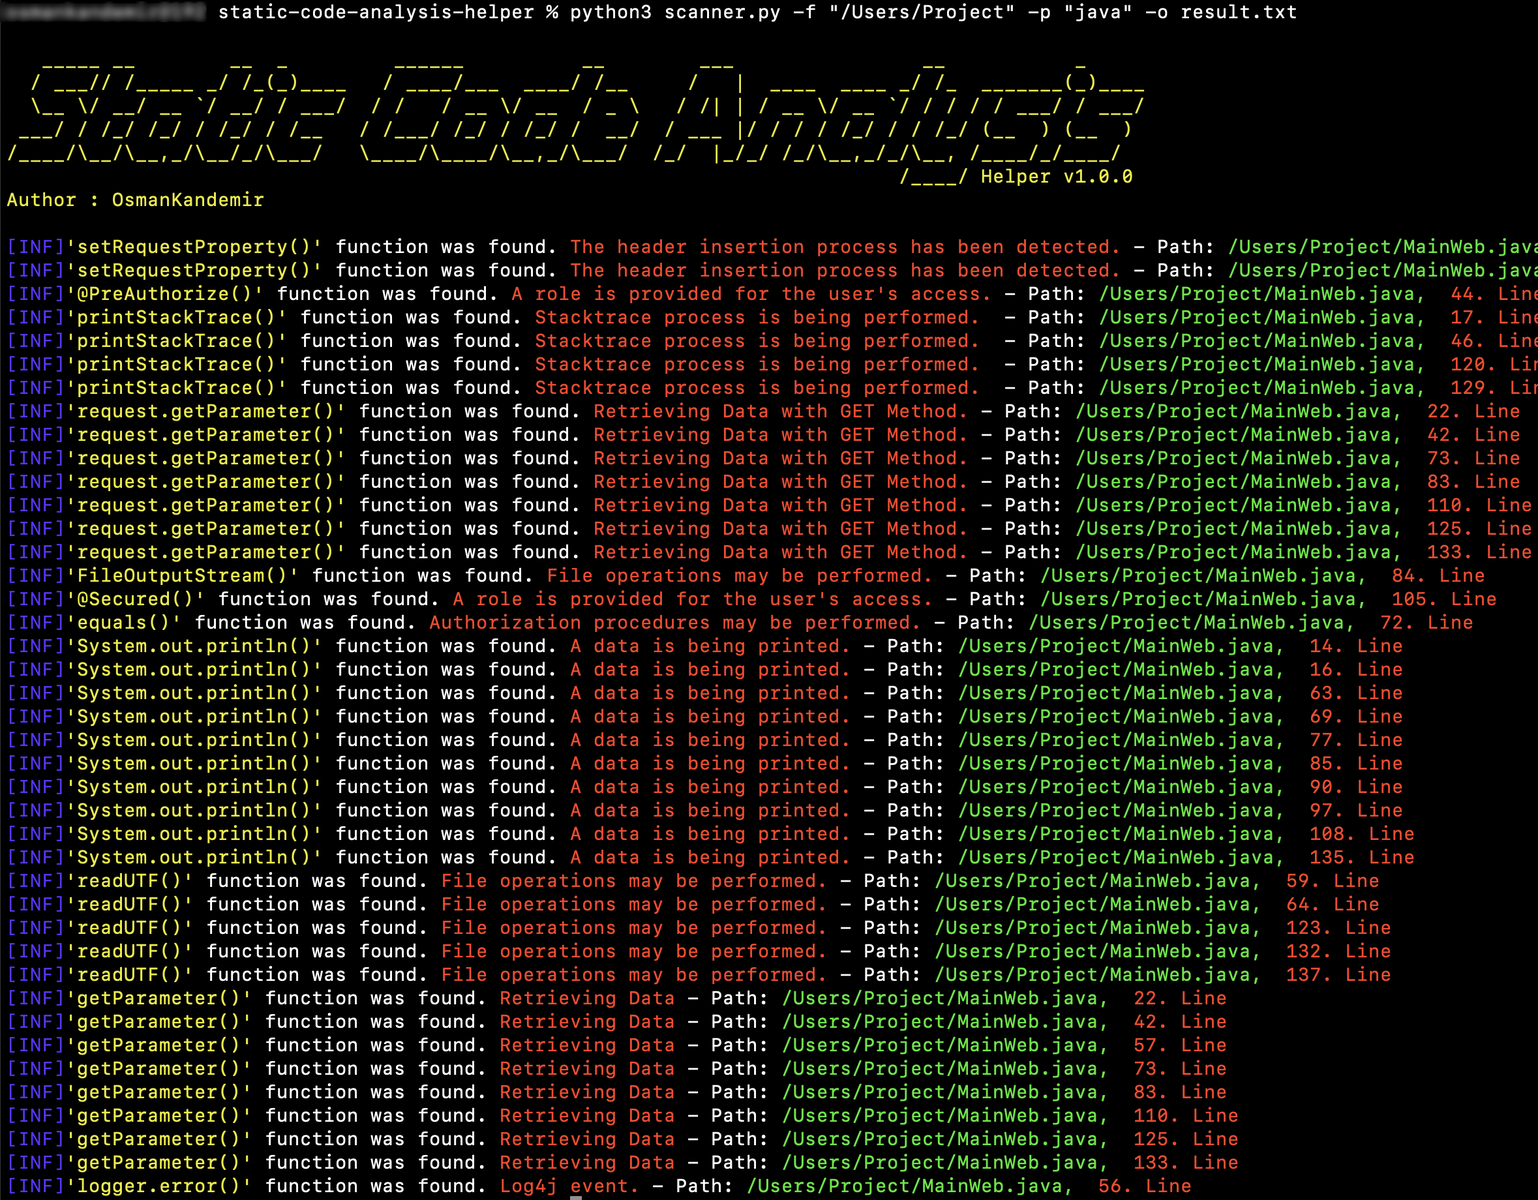
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…

Checklist and tools for increasing security of Apache Airflow

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…

BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.

Create useful, lightweight static analyses using open source tools + a tiny bit of your code