
ghostrace
 vusec/ghostrace
Proof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.
binary-exploitationexploitationpapers-research+2
74
vusec/ghostraceProof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.
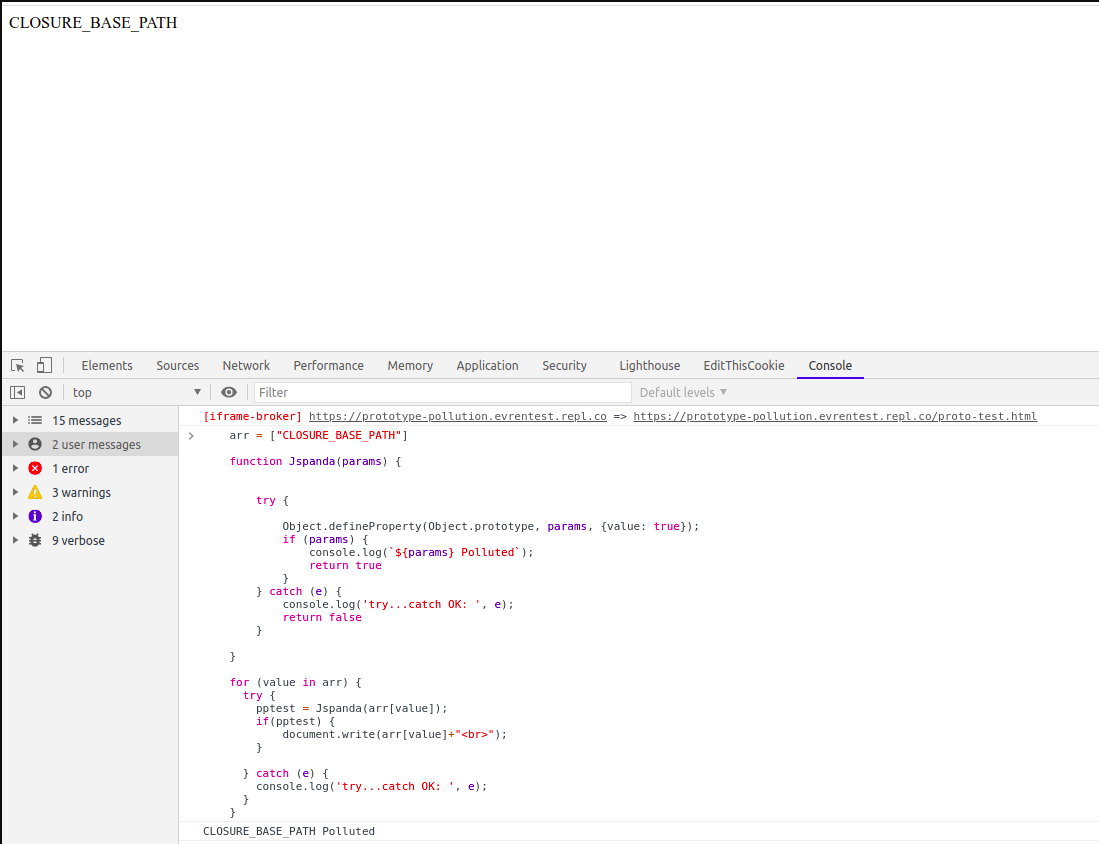 redsection/jspanda
client-side prototype pullution vulnerability scanner
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 atlassian/git-secrets-scan
Scans Git repositories for hardcoded secrets, keys, and passwords using Gitleaks, integrating security into Bitbucket Pipelines with Code Insights…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
