

ApplicationInspector
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
code-analysisdevsecopsstatic-analysis+3
4.4k
microsoft/applicationinspectorA source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
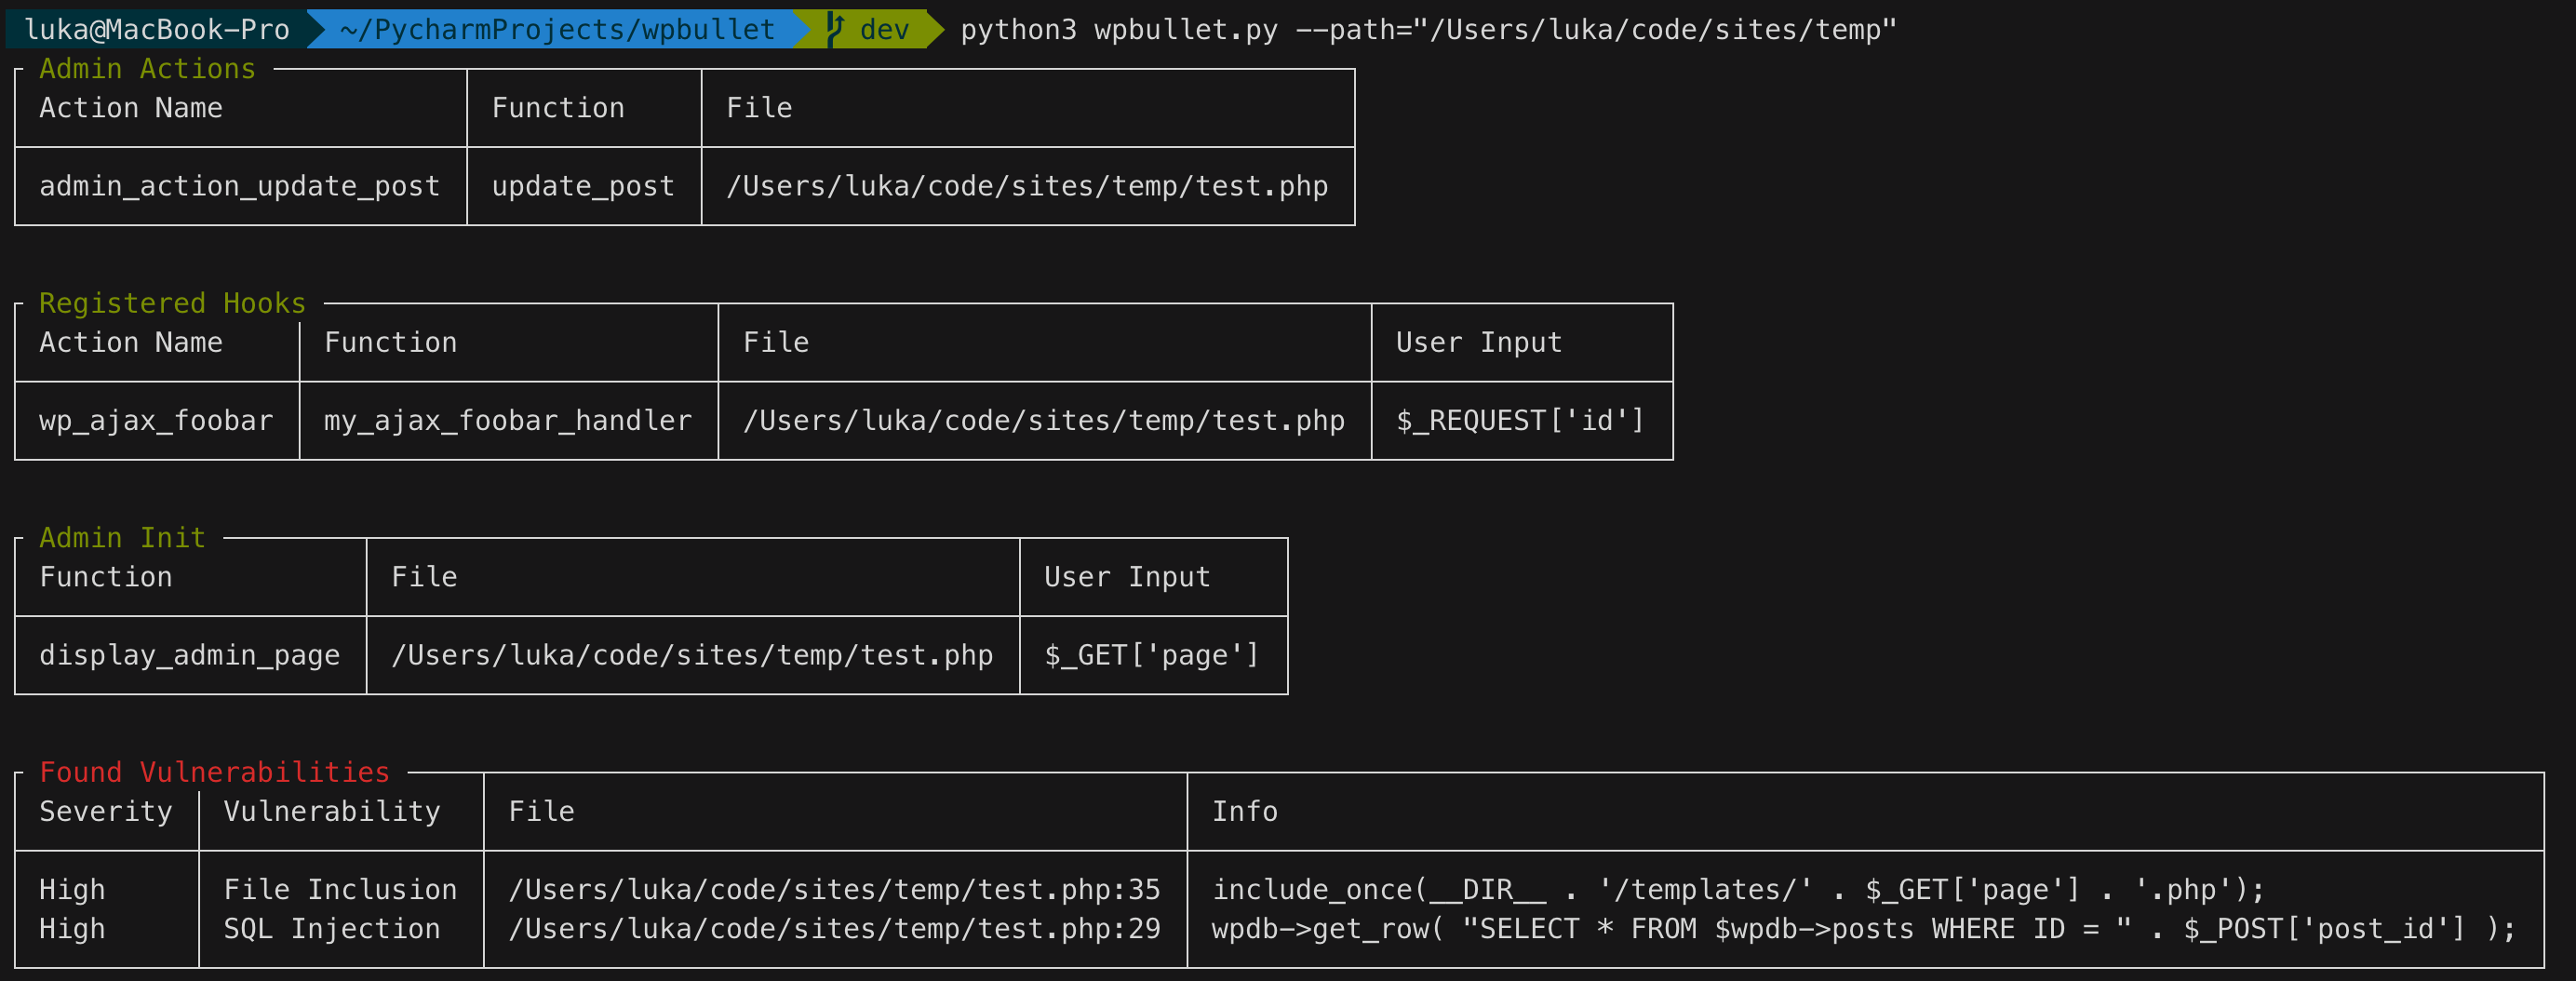 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
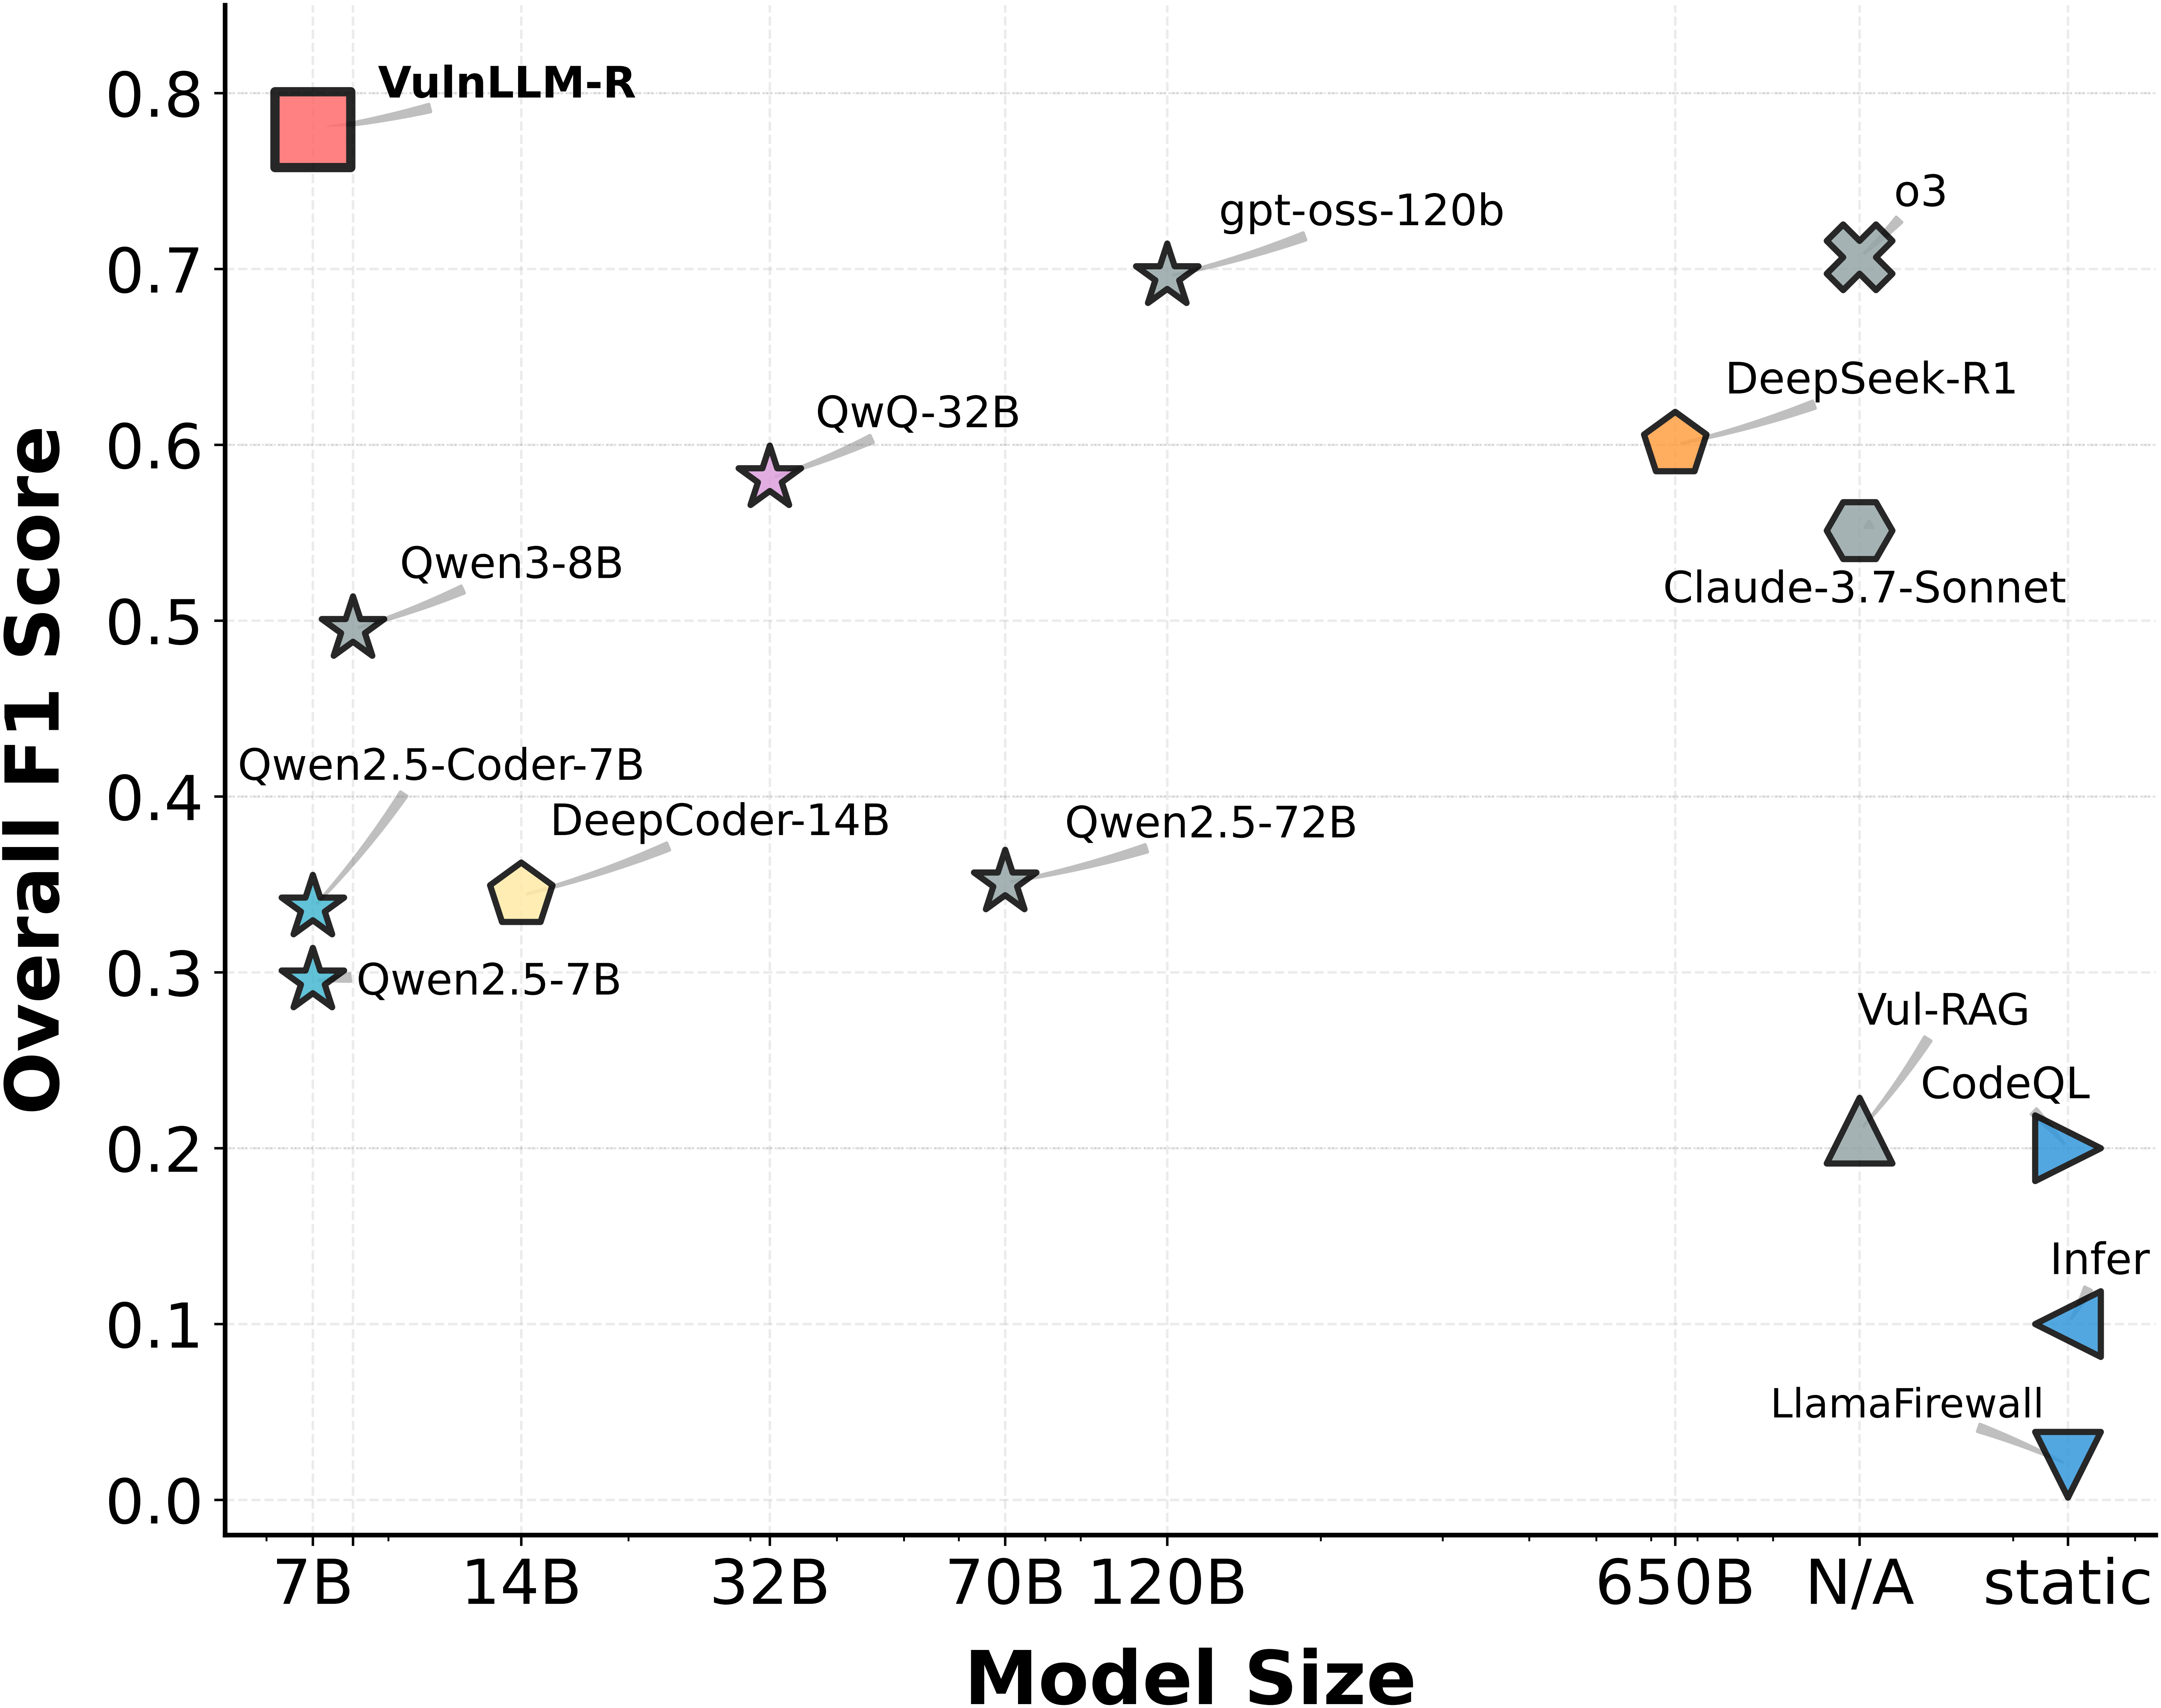 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
 robocoder/rips-scanner
RIPS - A static source code analyser for vulnerabilities in PHP scripts
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
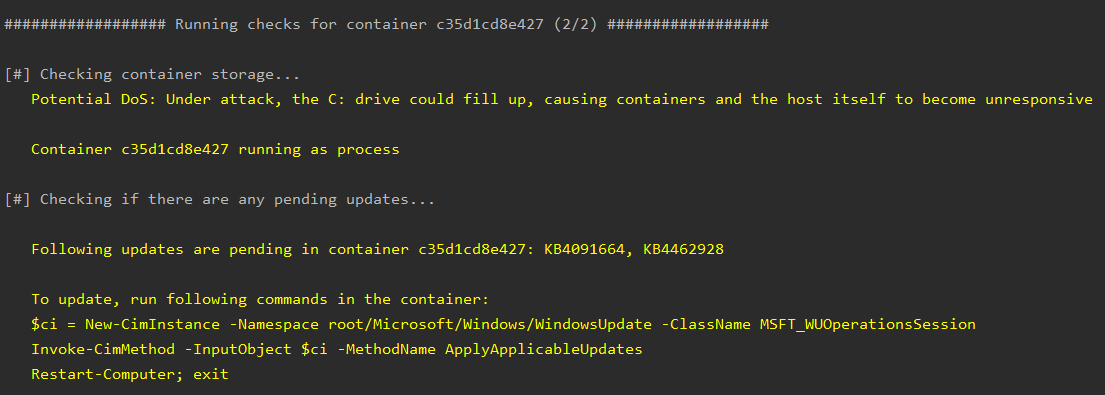 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…