kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…

Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…

Security risk analysis for Kubernetes resources

AWS Serverless Security

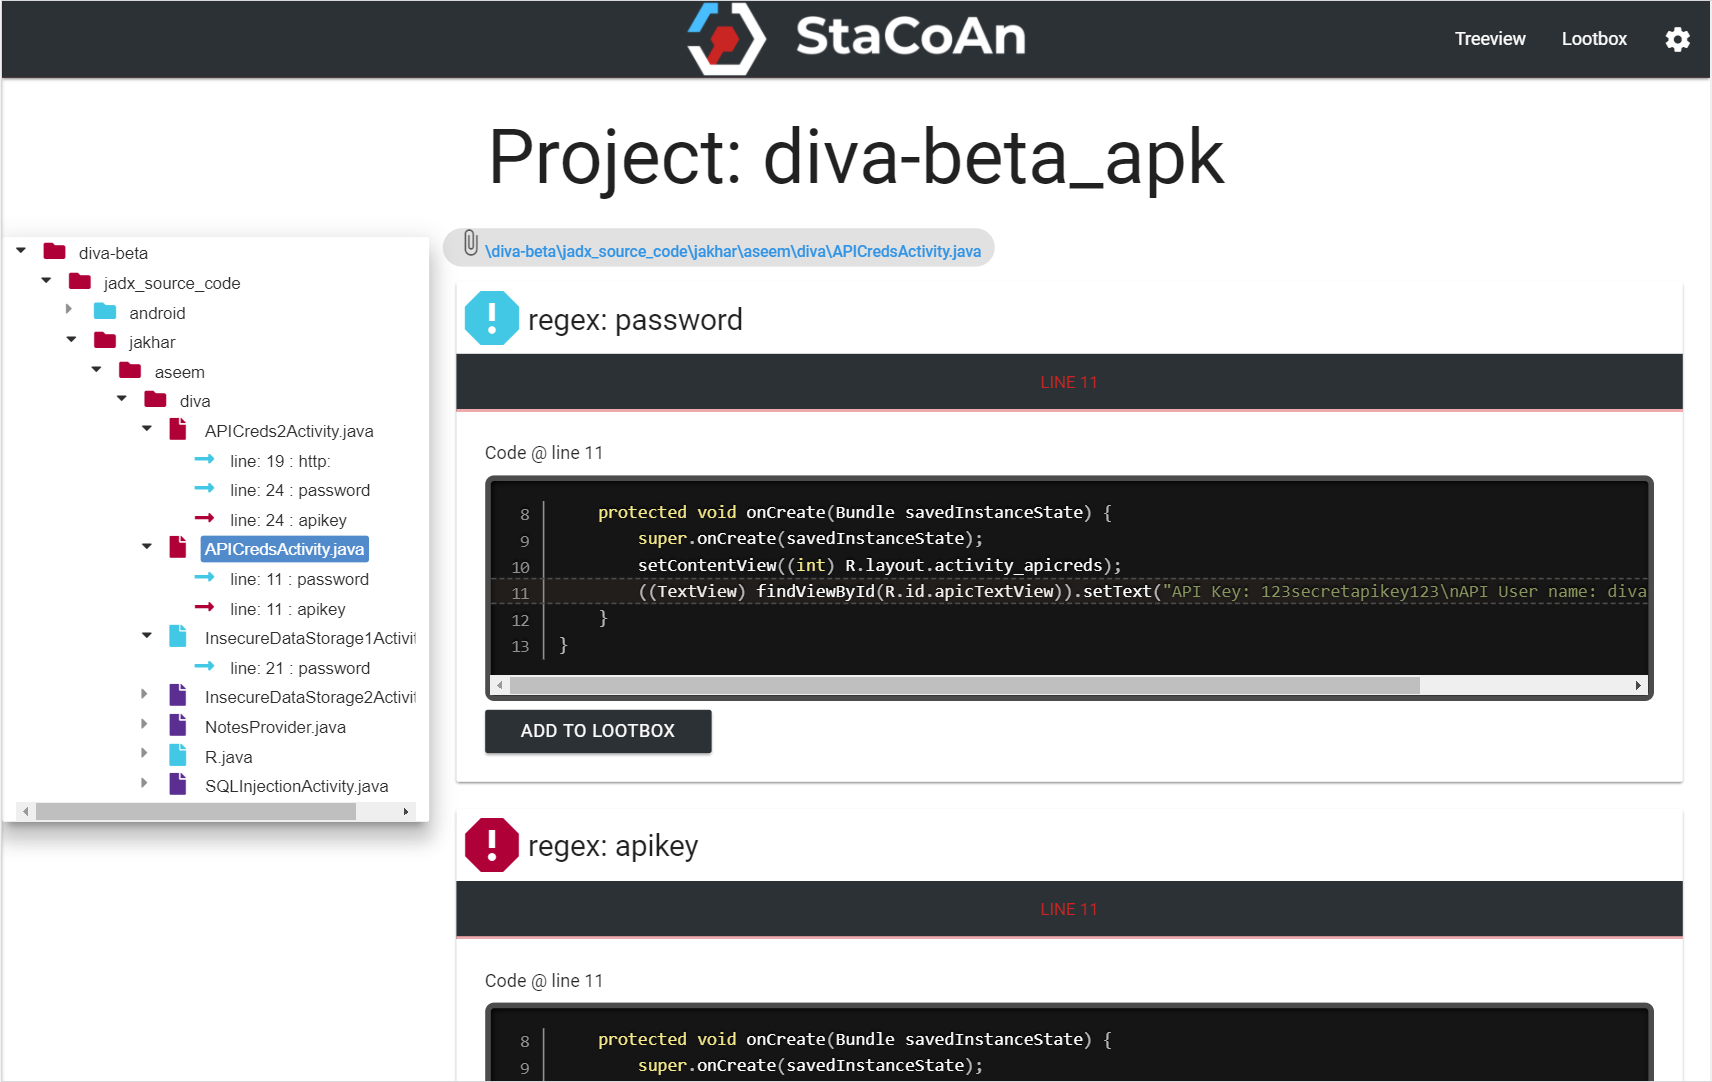
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.

Static code analysis plugin for Android project. (Checkstyle, PMD)

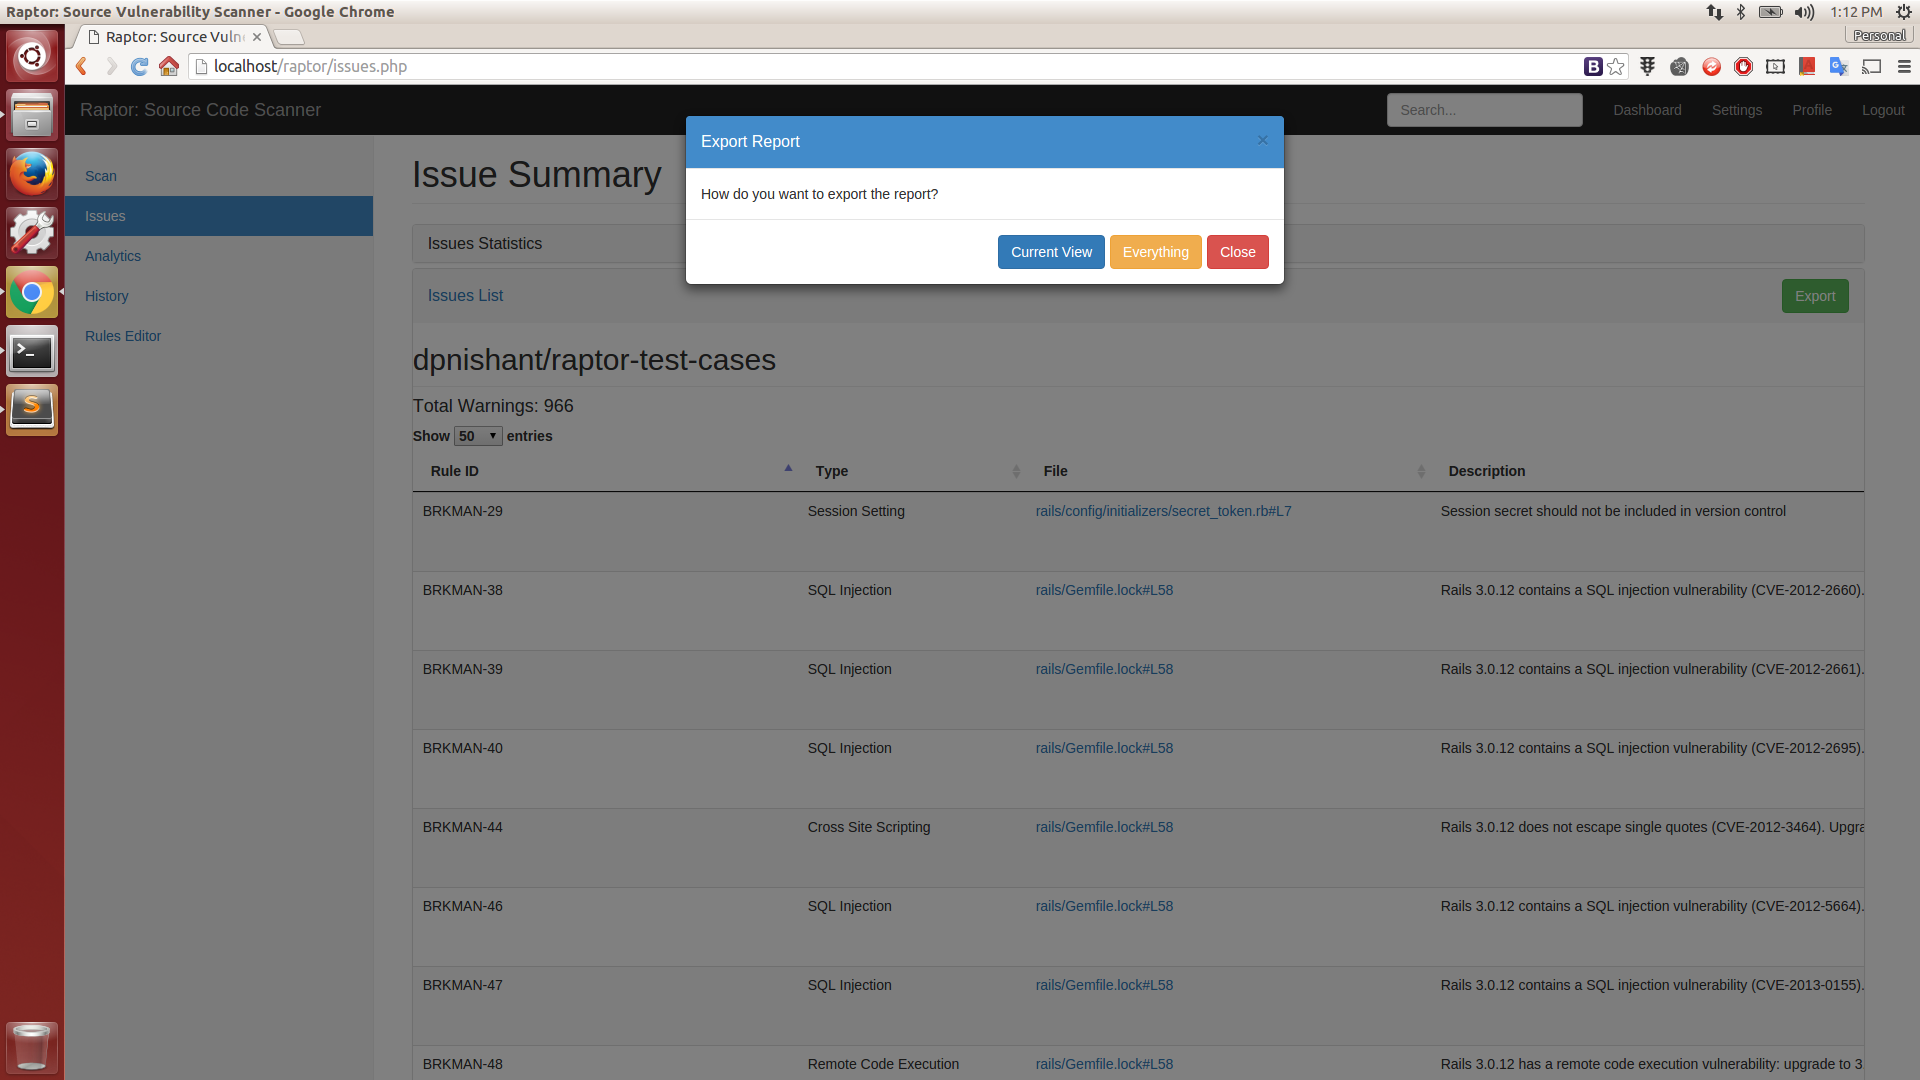
Web-based Source Code Vulnerability Scanner

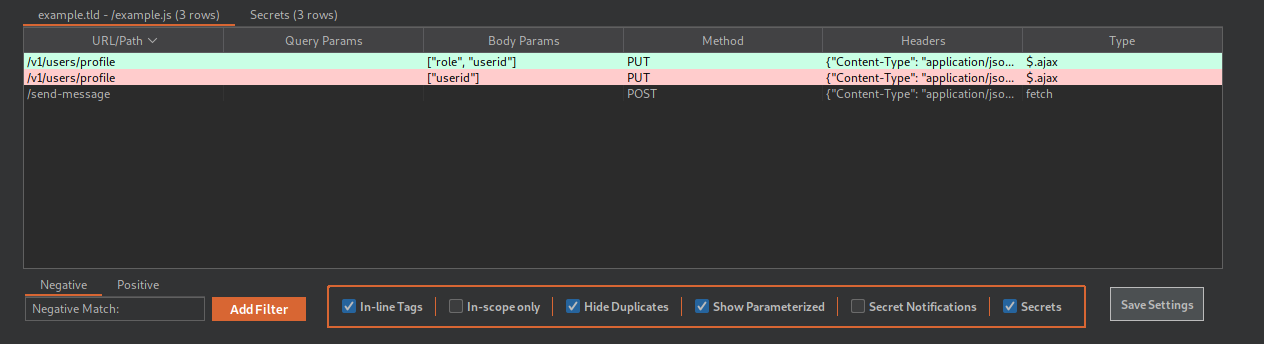
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice

GitHub Action for Offensive360 SAST: scan a repository and upload SARIF results to GitHub code scanning. Free for eligible open-source projects.

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

Proof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.

Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…

client-side prototype pullution vulnerability scanner