

raptor
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+7
gadievron/raptorAutonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 0xdea/semgrep-rules
A collection of my Semgrep rules to facilitate vulnerability research.
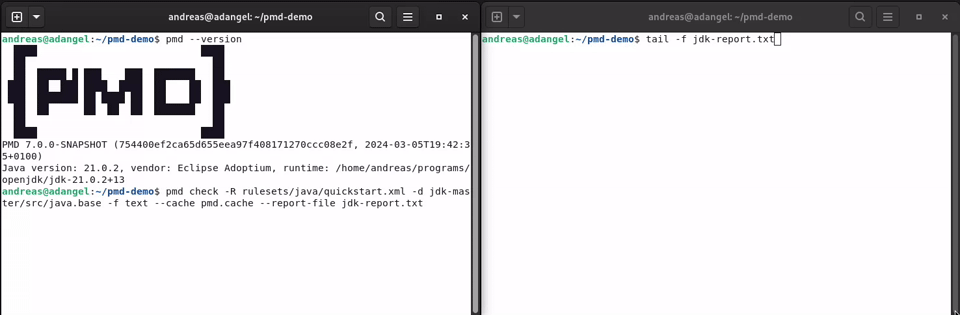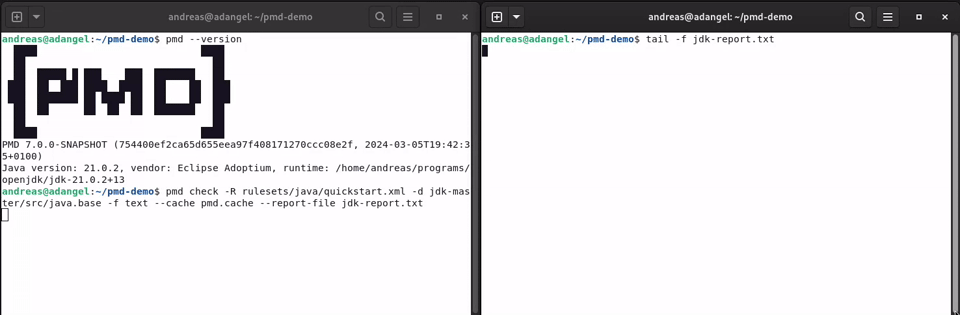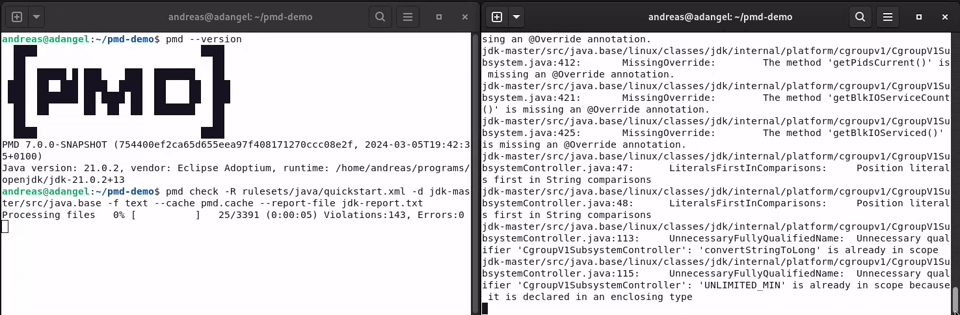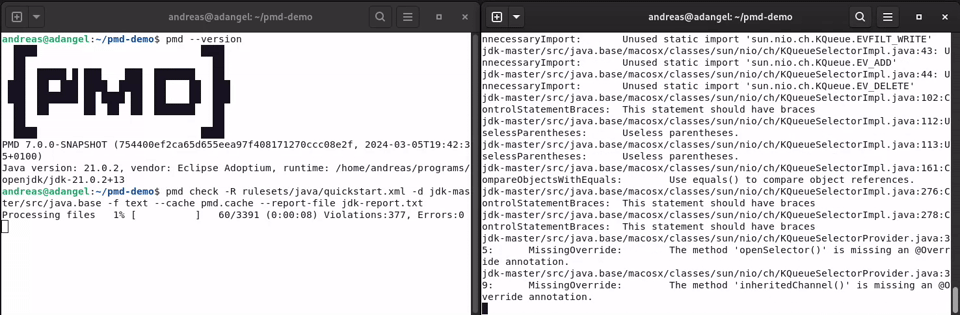 pmd/pmd
An extensible multilanguage static code analyzer.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 gitlab-org/security-products/sast-rules
Curated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…

 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…