kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…

PHP Static Analysis Tool - discover bugs in your code without running it!

CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security

Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.

A static analyzer for Java, C, C++, and Objective-C

Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

Bandit is a tool designed to find common security issues in Python code.

Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…

Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity

jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…

Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…

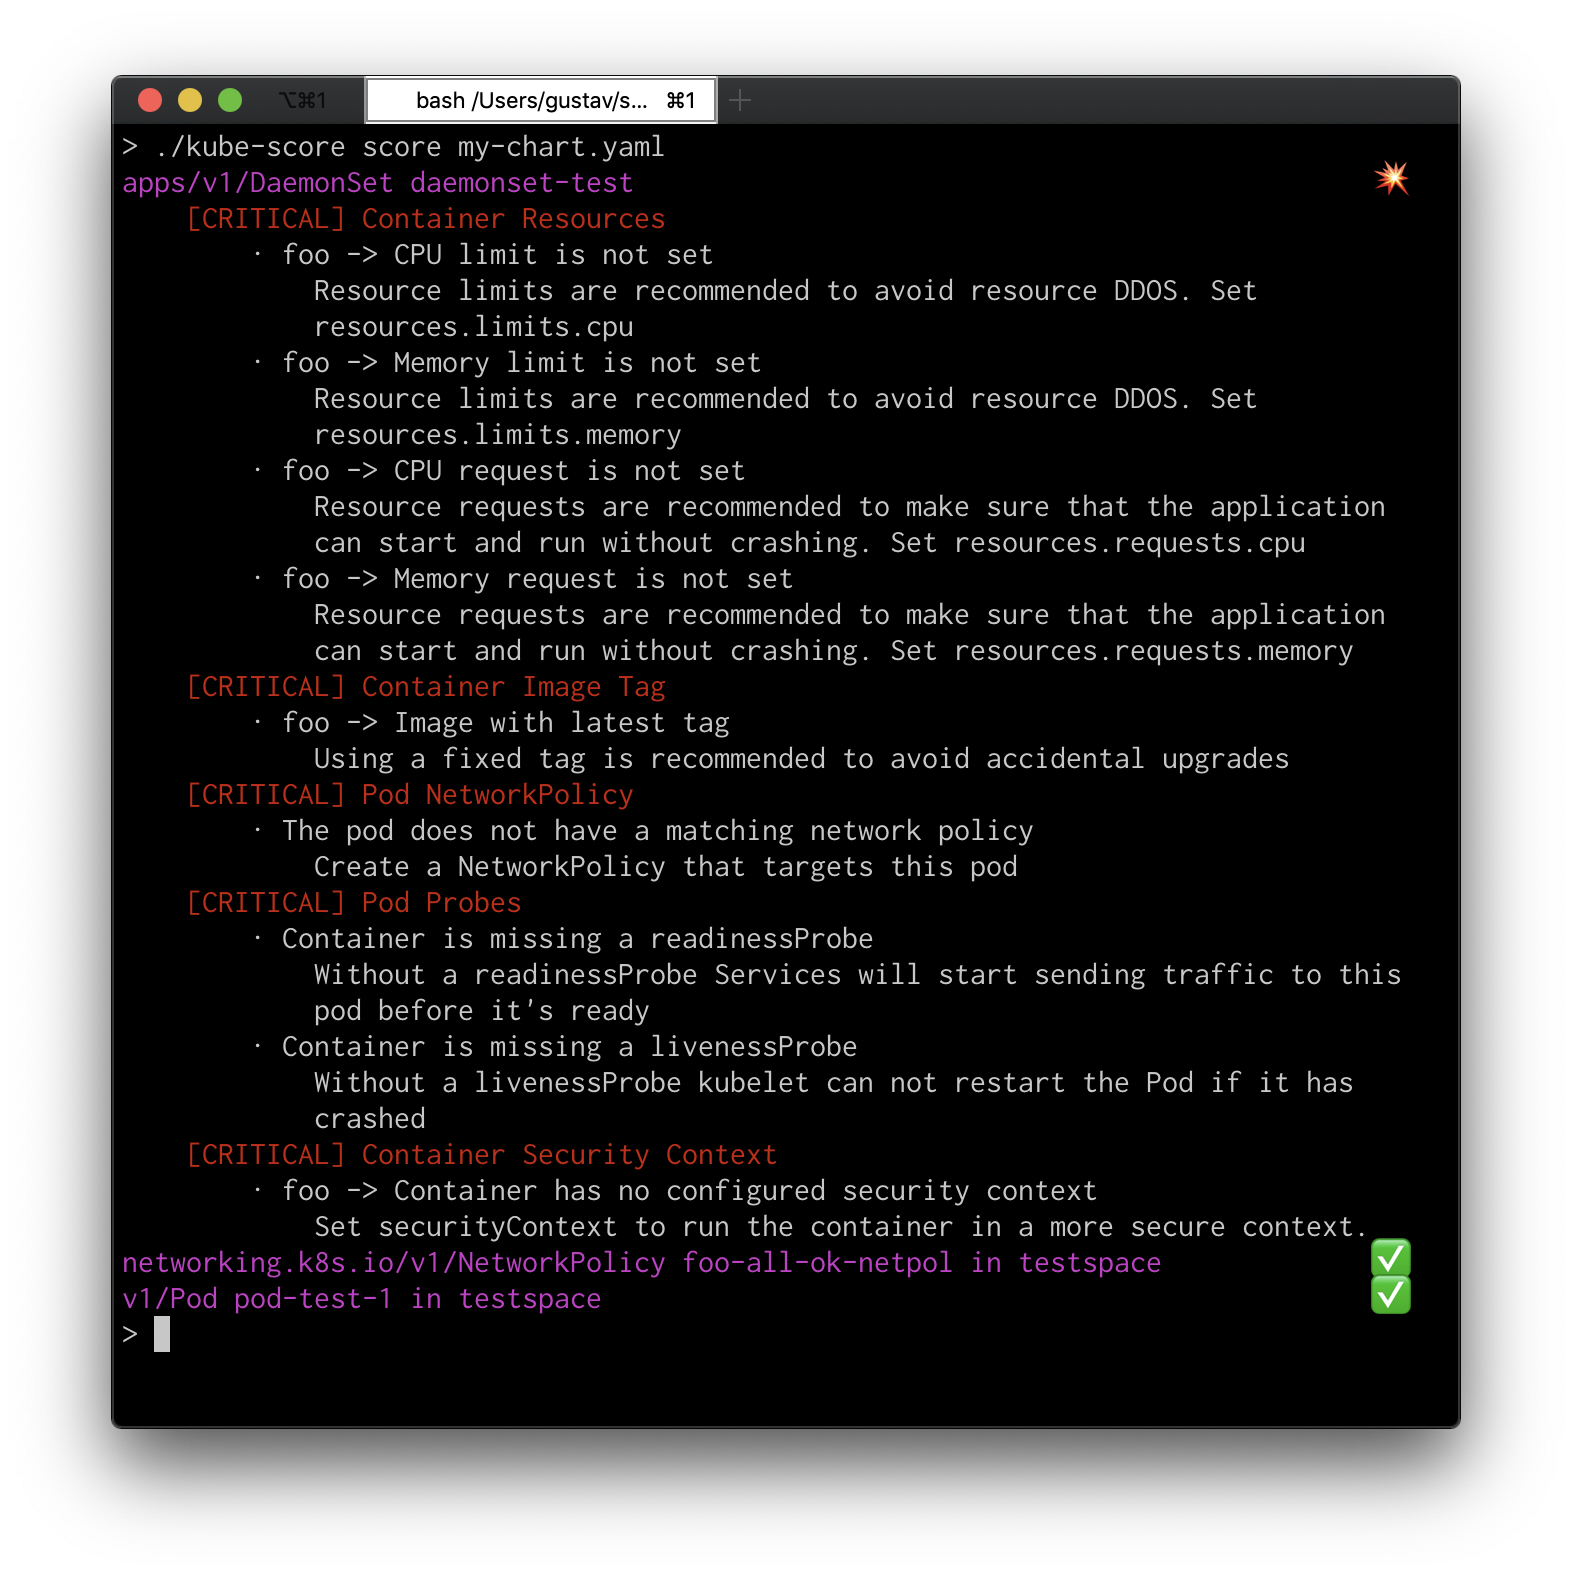
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…

a static analysis tool for finding vulnerabilities in C/C++ source code

Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.