

checkov
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
cloud-infrastructure-securitycloud-securitycode-analysis+12
9.0k
bridgecrewio/checkovStatic analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security

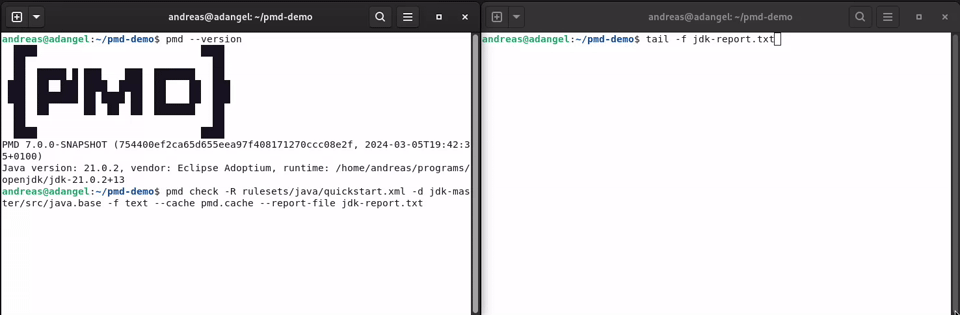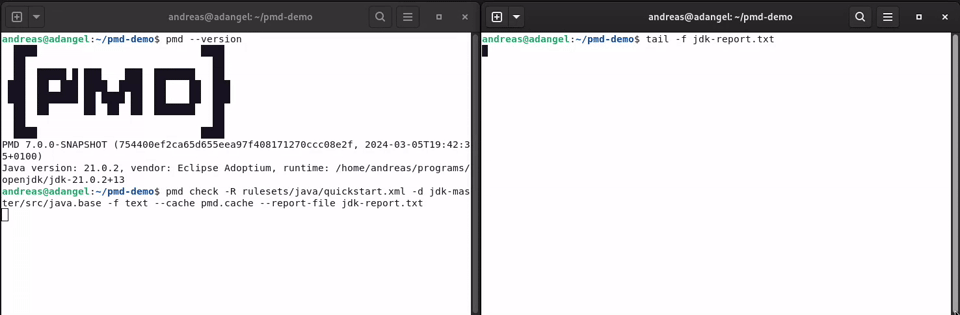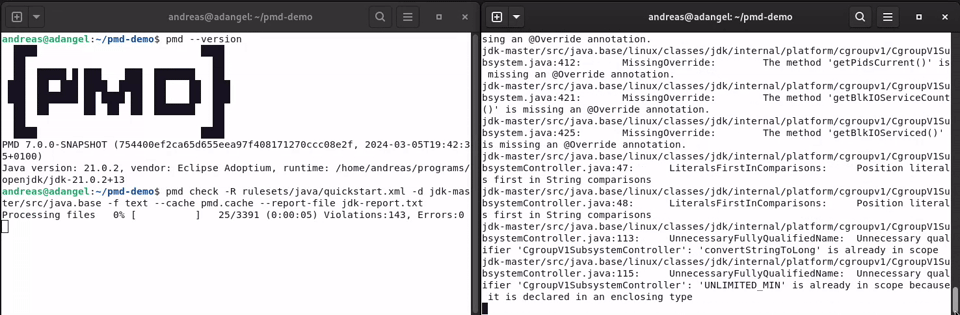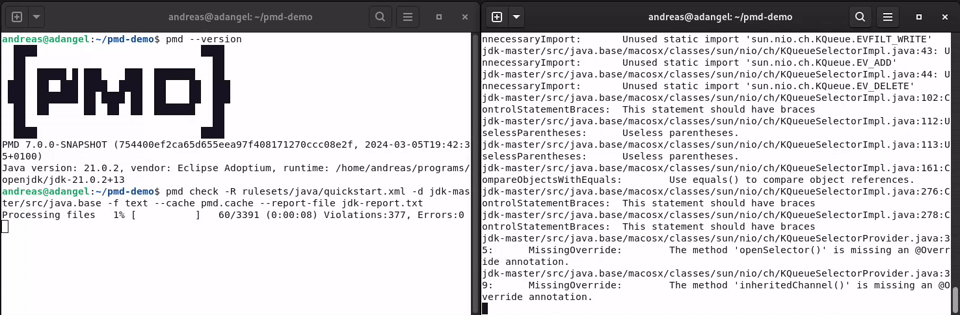 pmd/pmd
An extensible multilanguage static code analyzer.
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
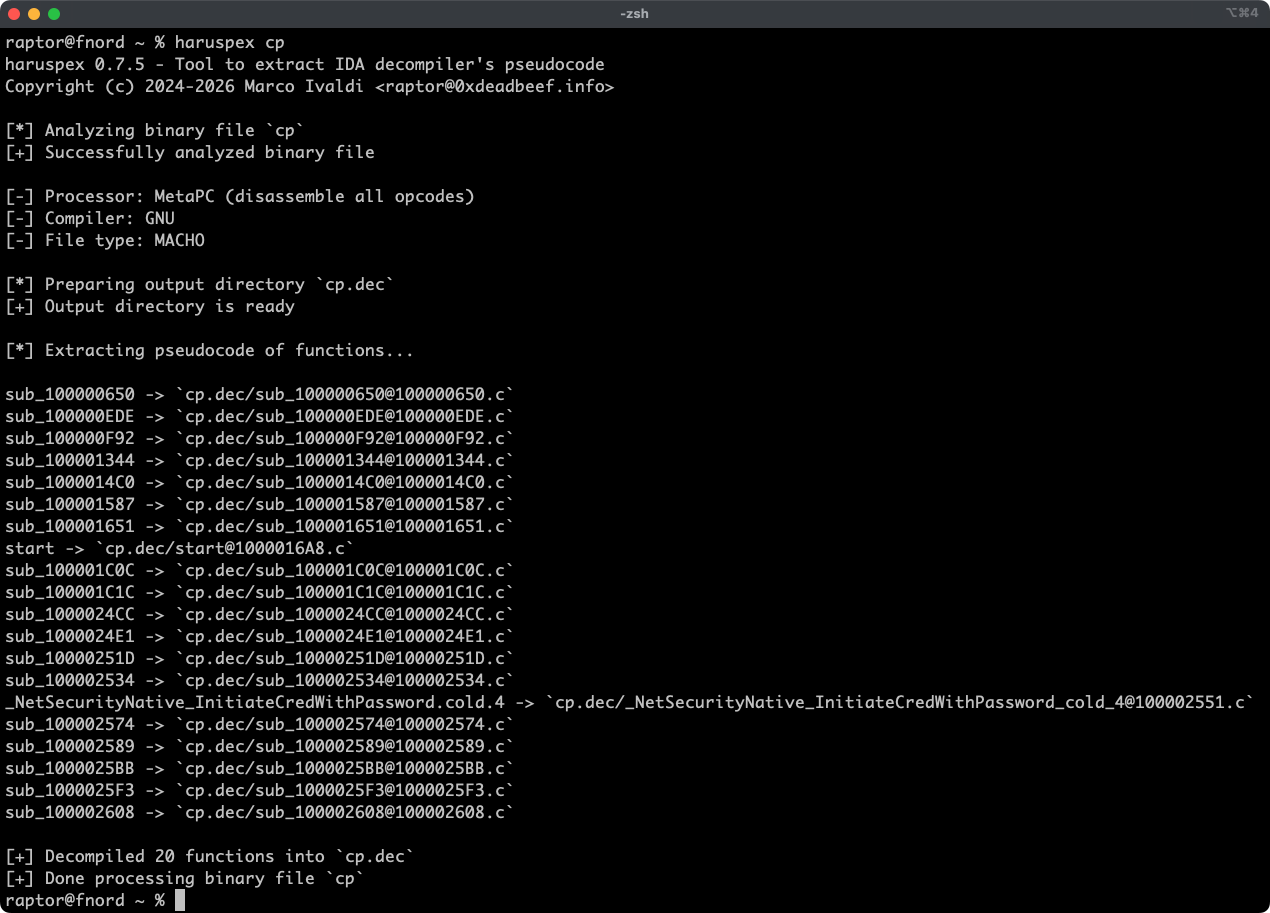 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…