

bearer
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
code-analysisdevsecopsprivacy+3
2.7k3 days ago
bearer/bearerCode security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 filipi86/drogonsec
High-performance open-source security scanner combining SAST, SCA, Secret Detection, and IaC analysis, built for developers and CI/CD pipelines,…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation

 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST: scan a repository and upload SARIF results to GitHub code scanning. Free for eligible open-source projects.
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
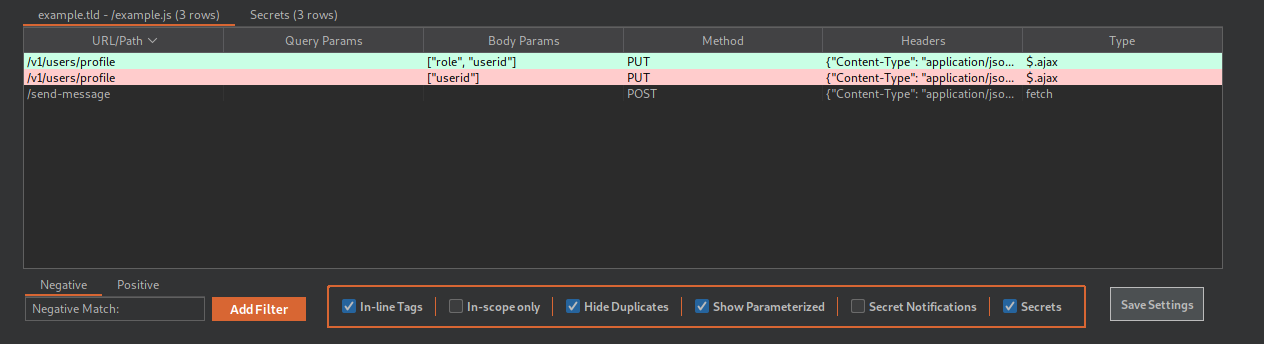 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
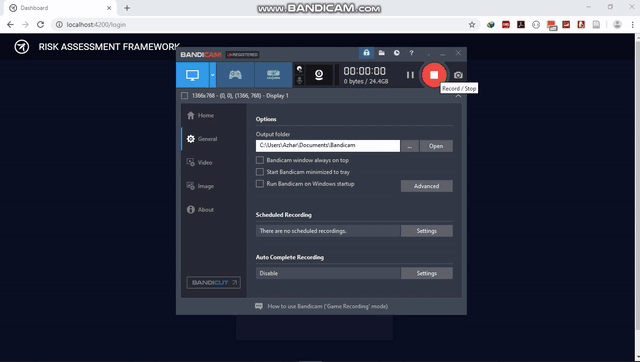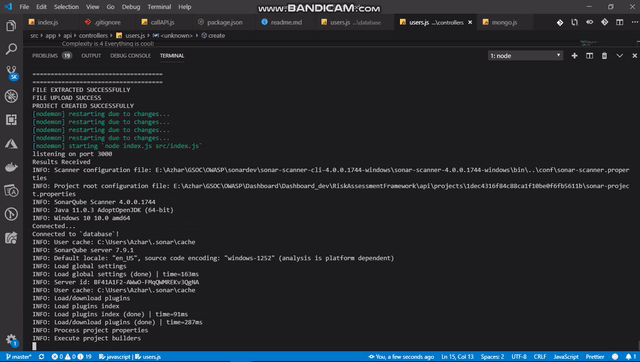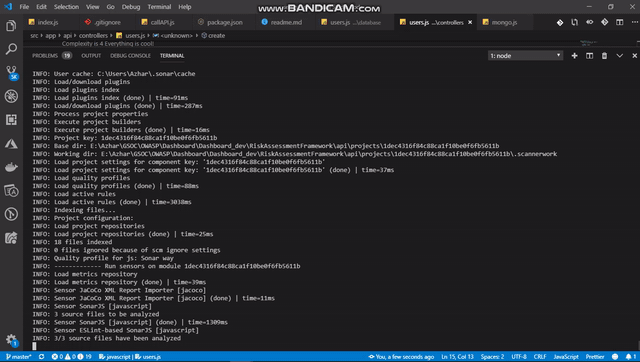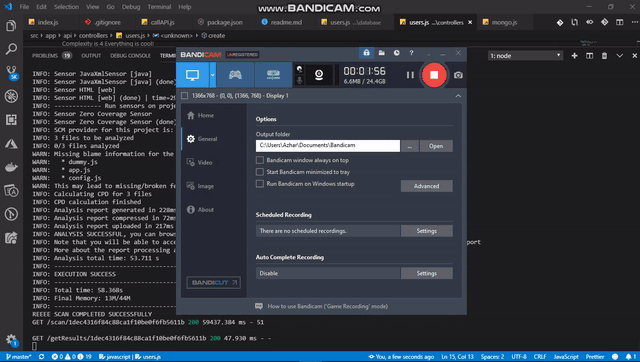 owasp/riskassessmentframework
The Secure Coding Framework