
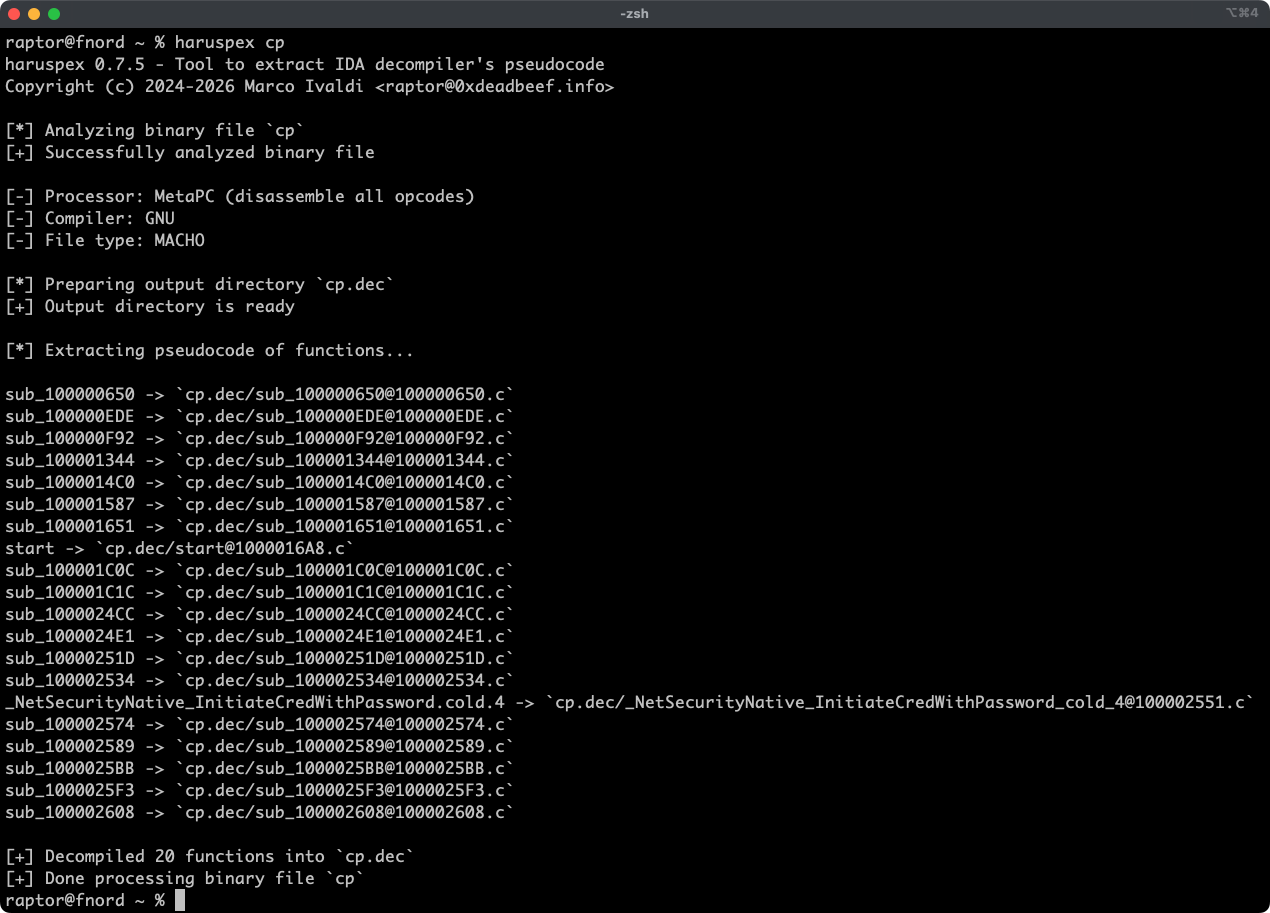
haruspex
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
binary-analysisreverse-engineeringstatic-code-analysis+1
1355 days ago
0xdea/haruspexVulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 sassoftware/shiro
CVE-2026-49268 — Analysis and Remediation of an LDAP Injection Authentication Bypass Vulnerability
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
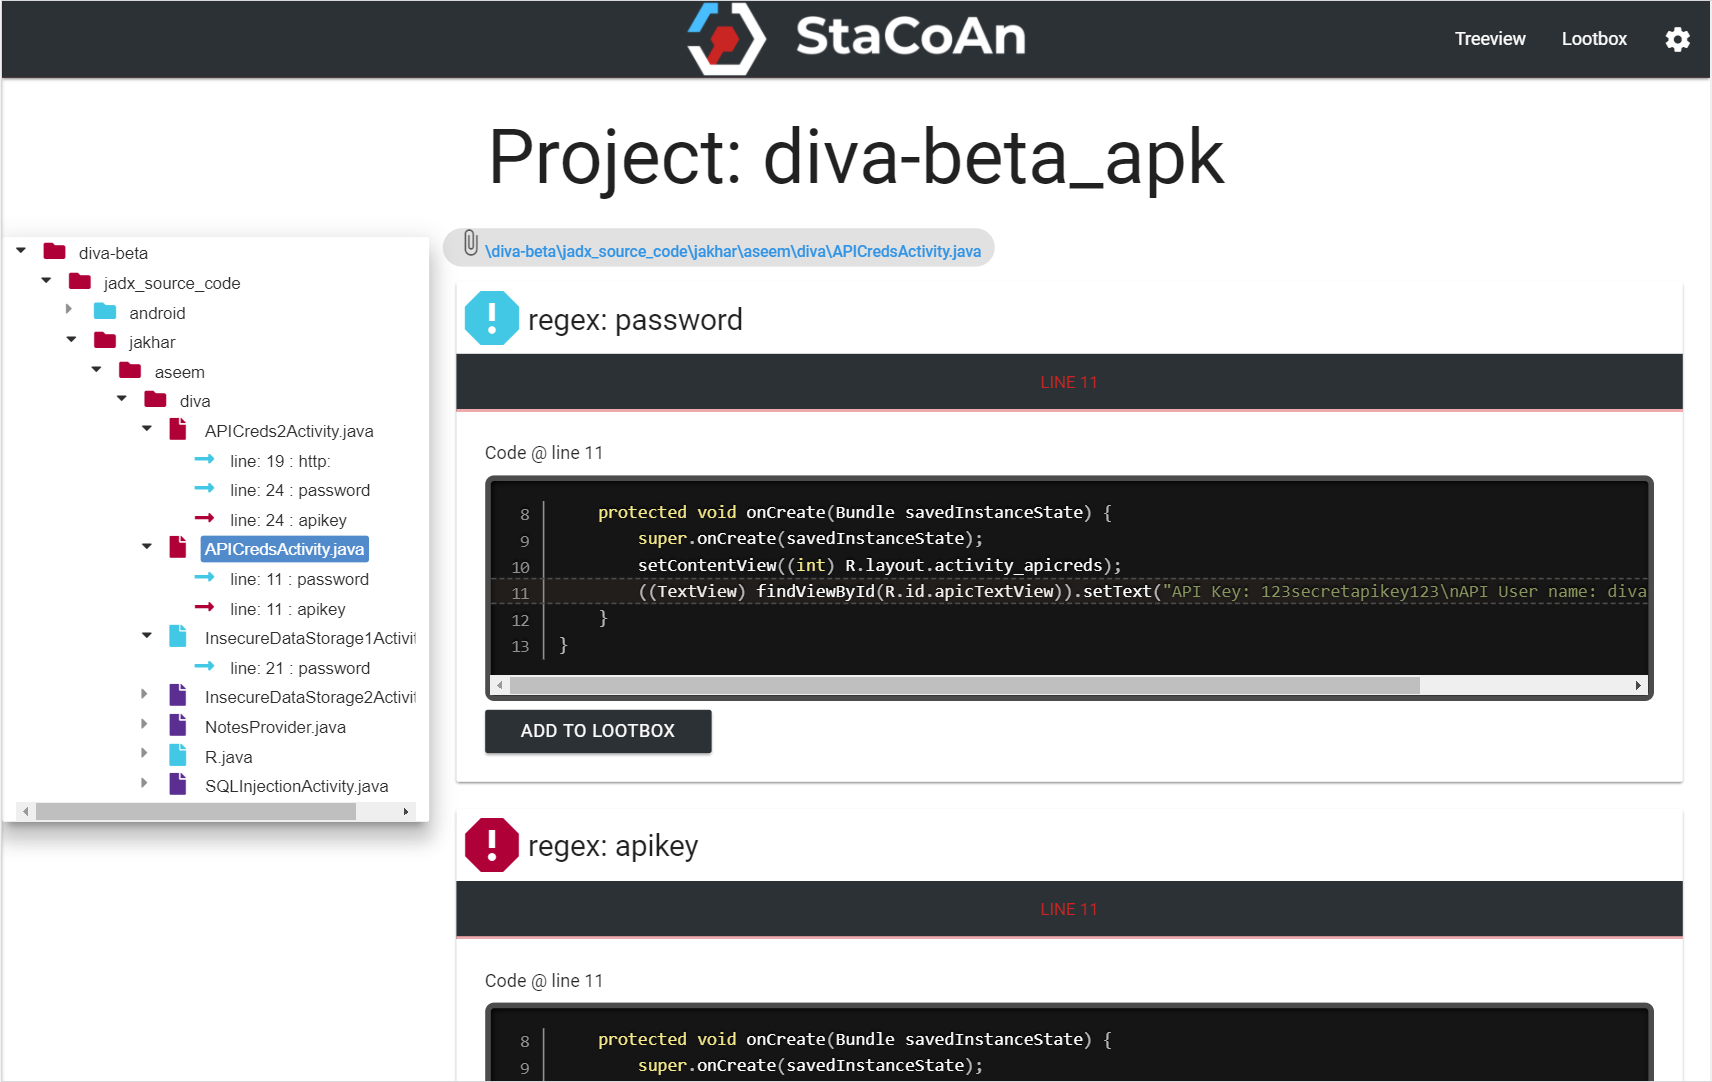 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
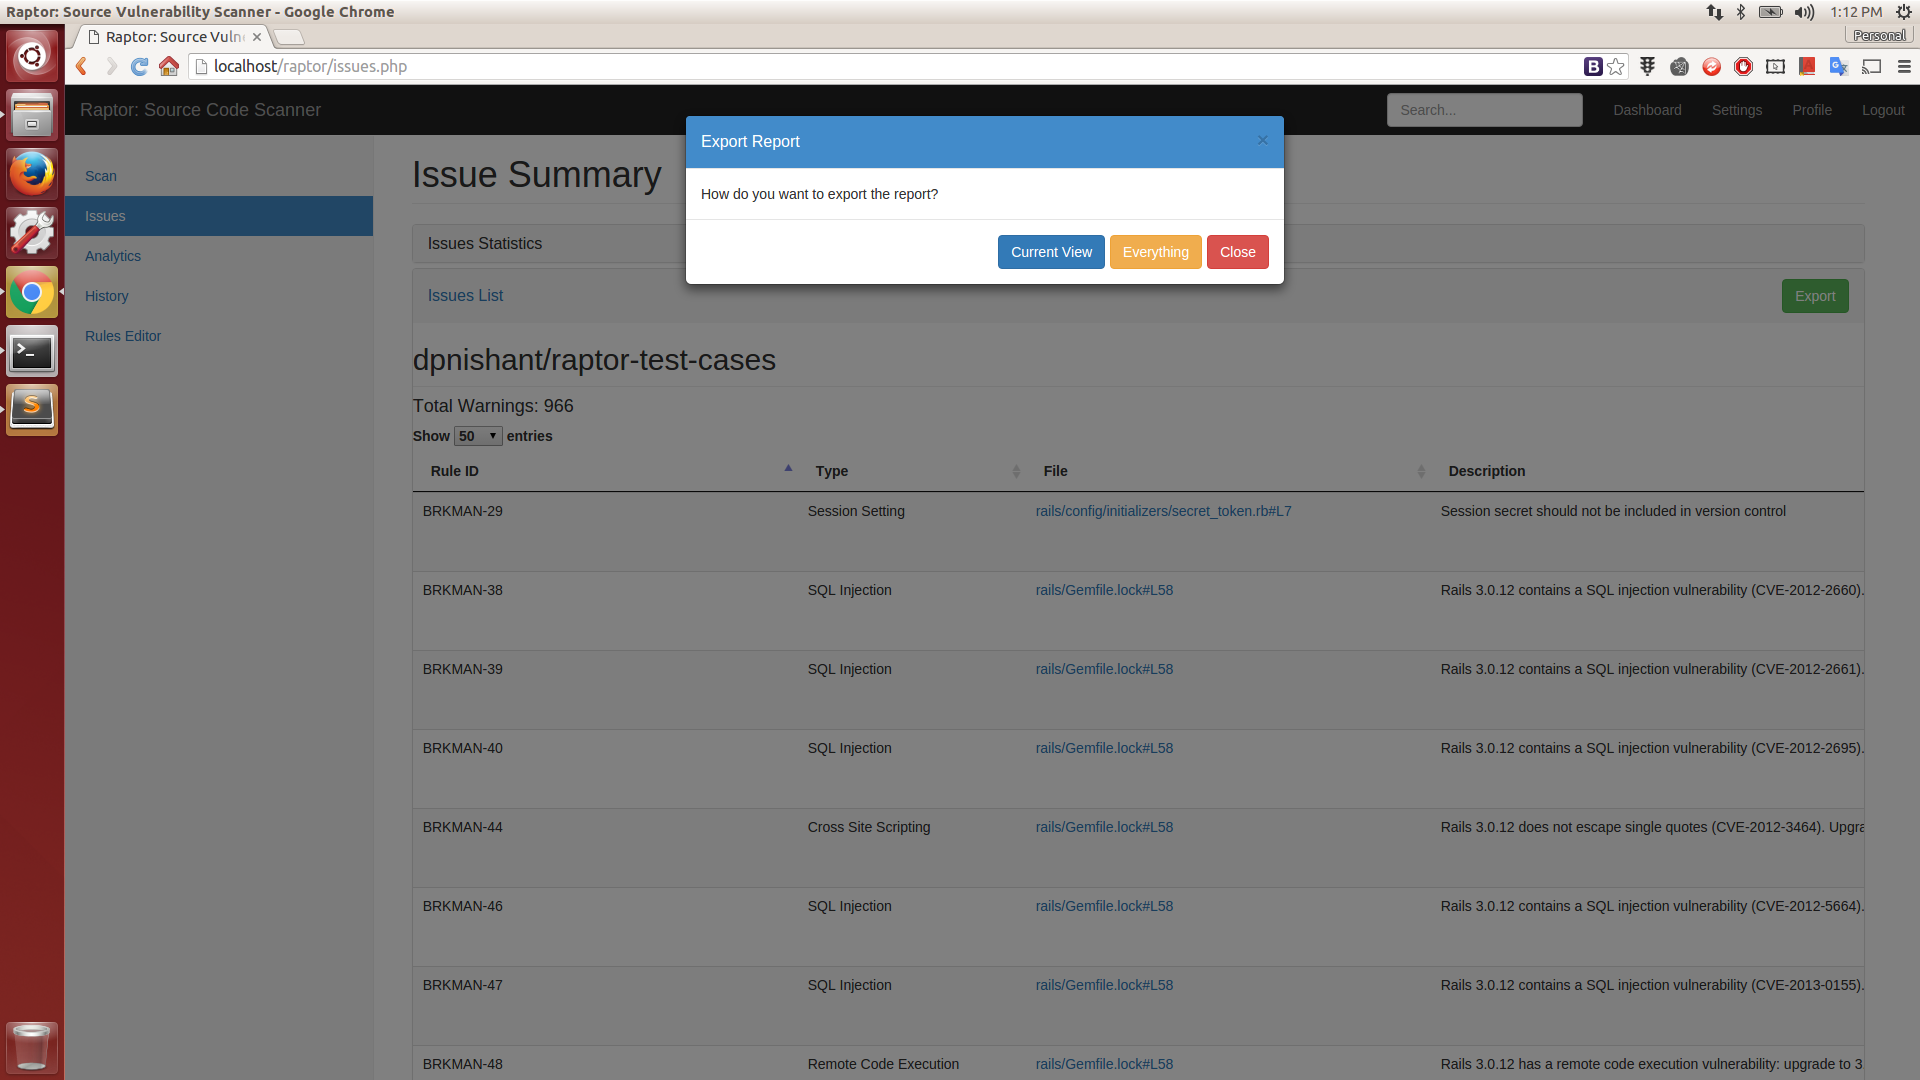 dpnishant/raptor
Web-based Source Code Vulnerability Scanner
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)