kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

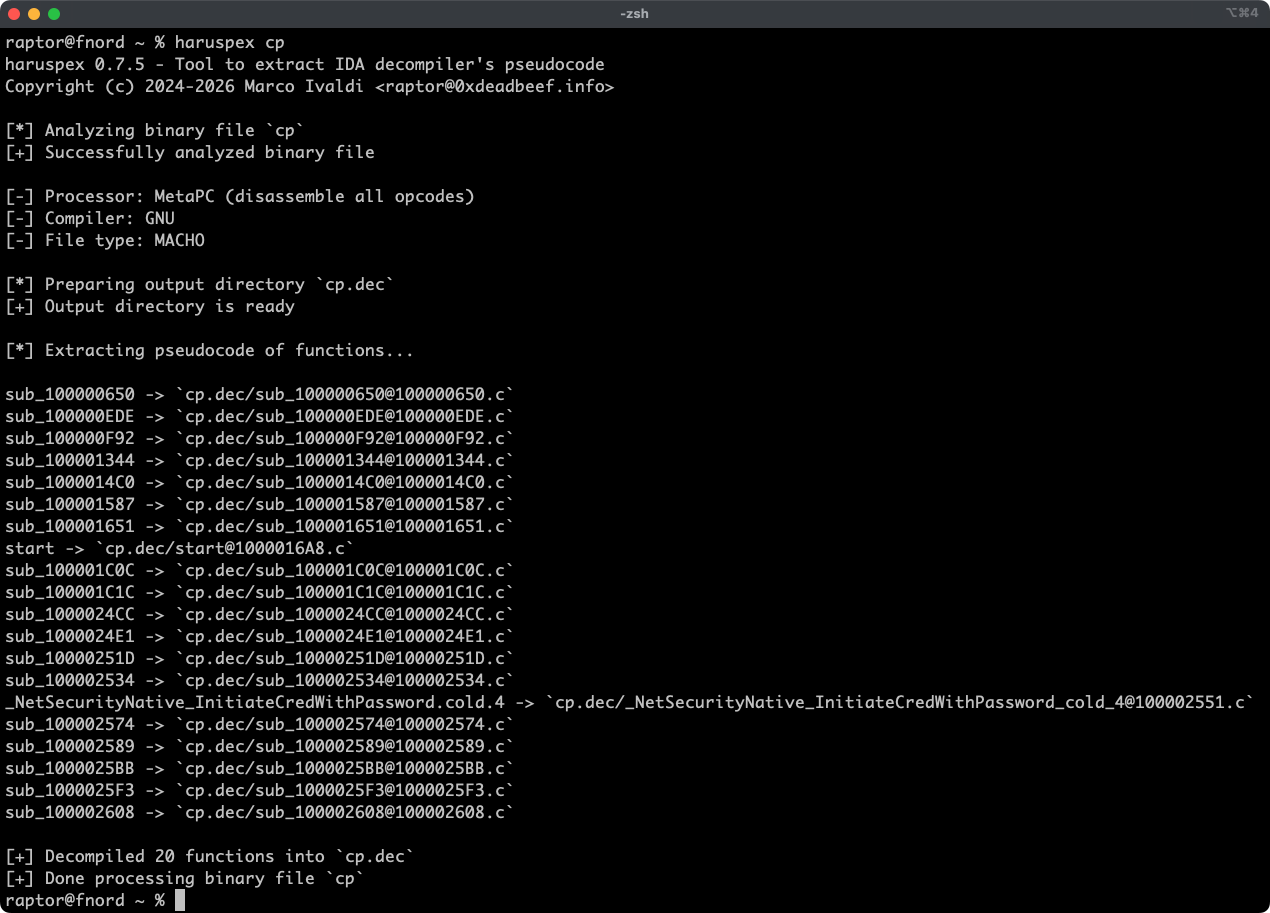
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…

An extensible multilanguage static code analyzer.

Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…

OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…

Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…

Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…

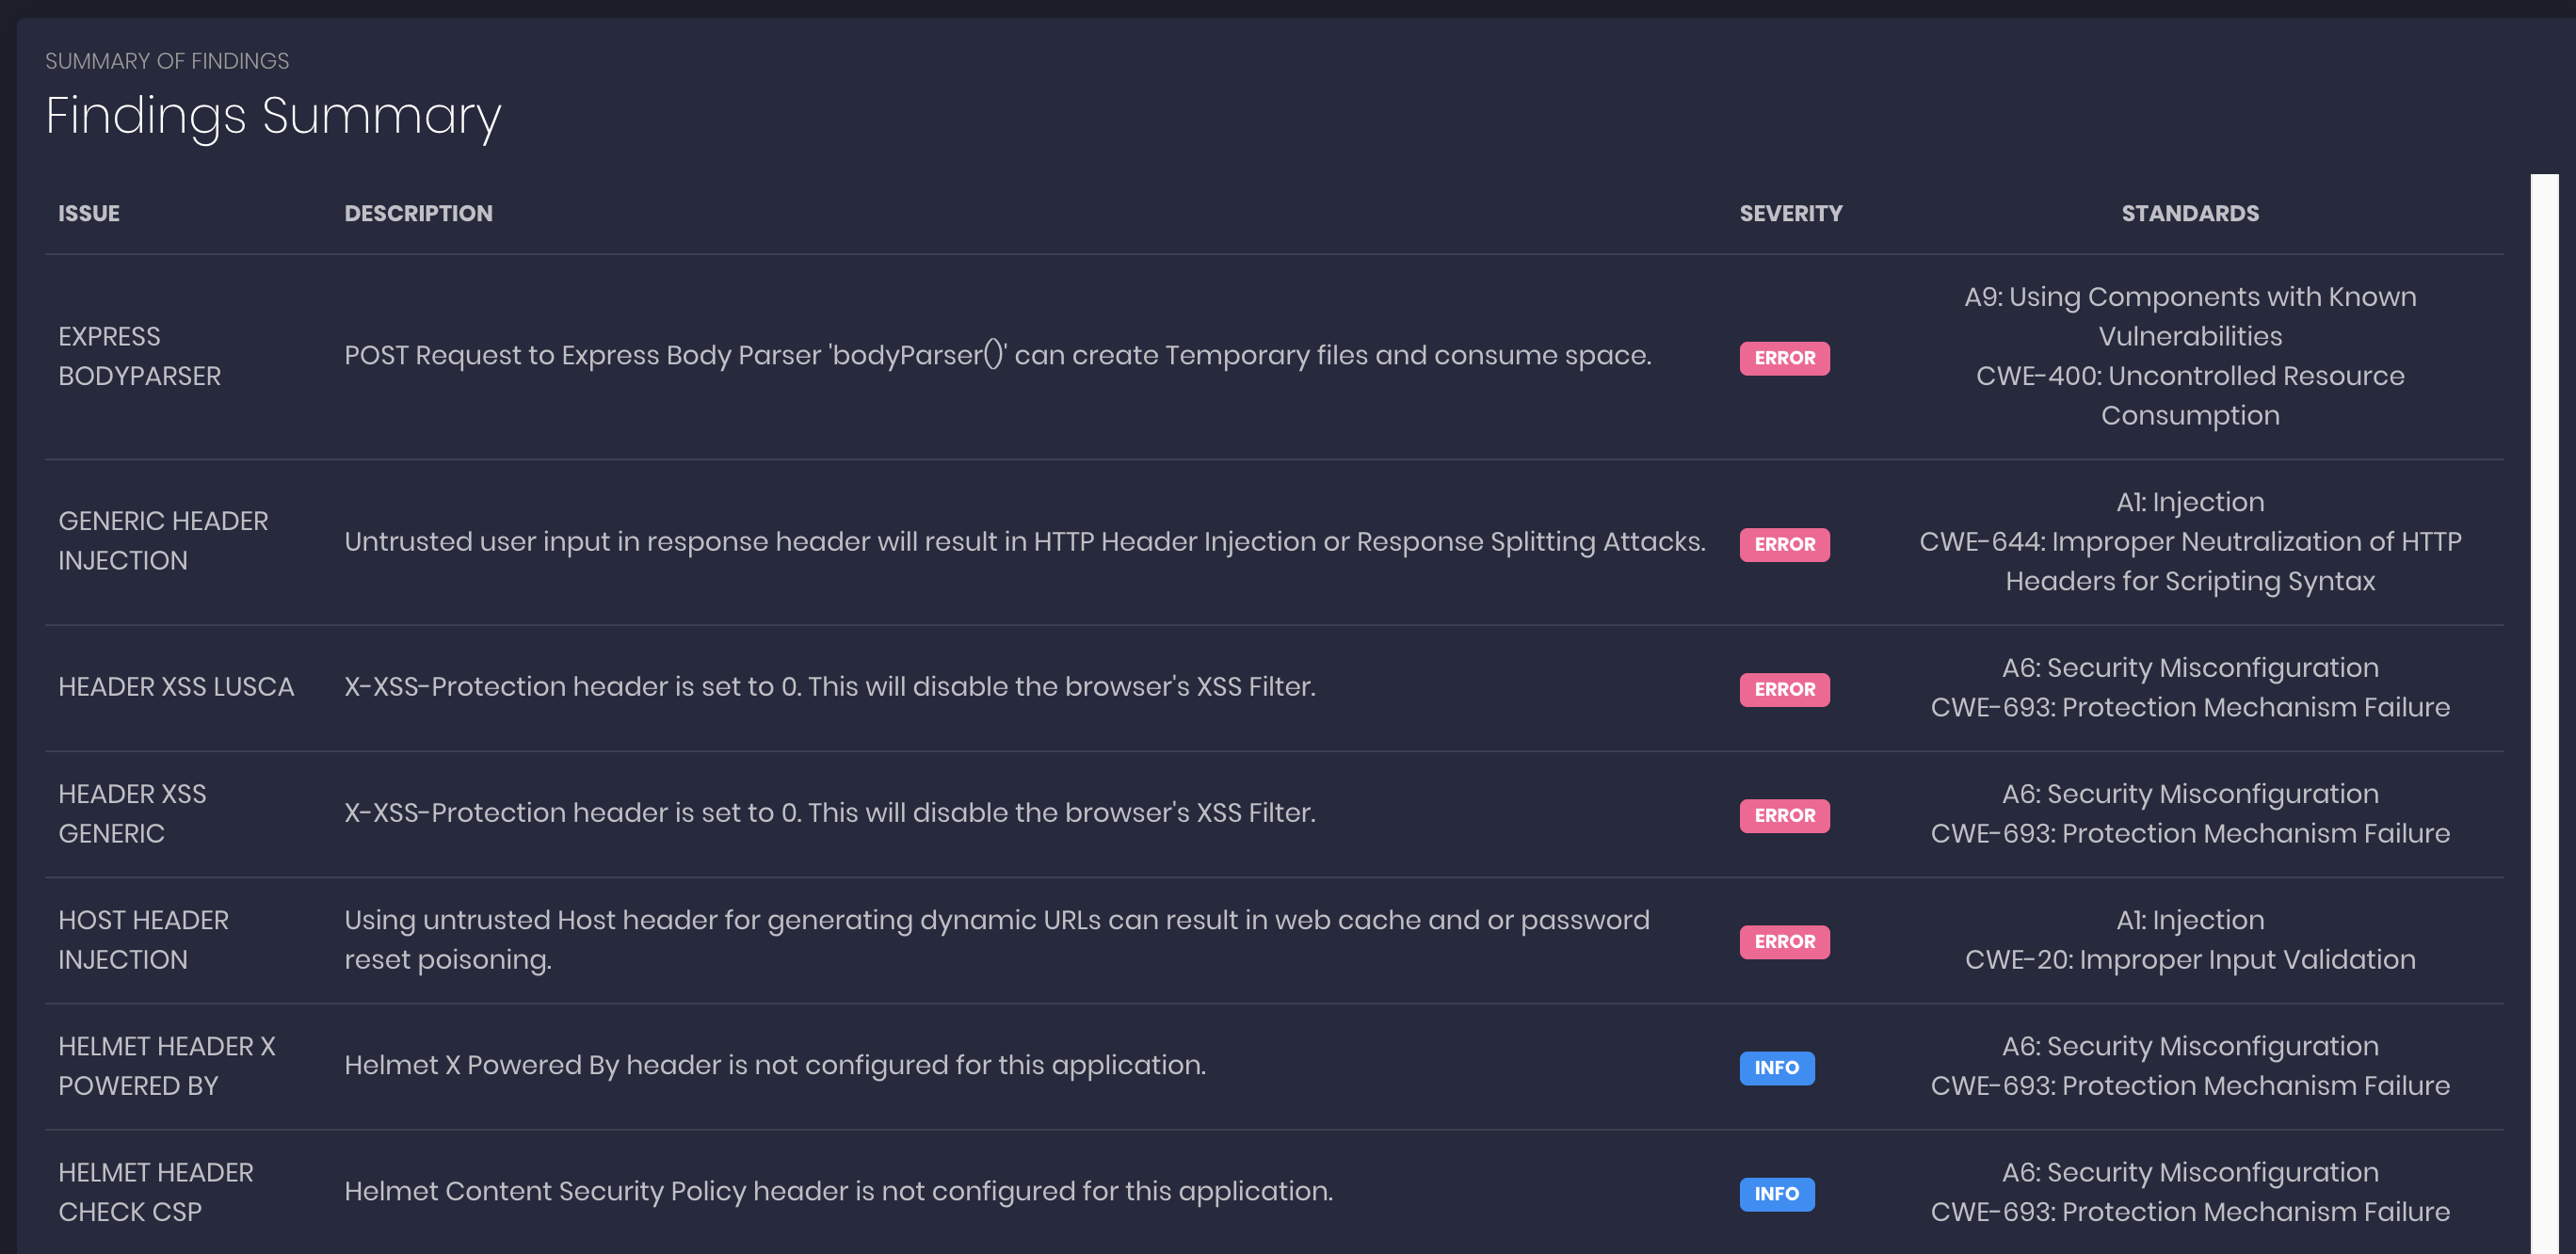
nodejsscan is a static security code scanner for Node.js applications.

Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…

AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

A static analyzer for Java, C, C++, and Objective-C

Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…

Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits

Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment

A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…

Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…