
phpstan
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
code-analysisstatic-code-analysis
phpstan/phpstanPHP Static Analysis Tool - discover bugs in your code without running it!
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
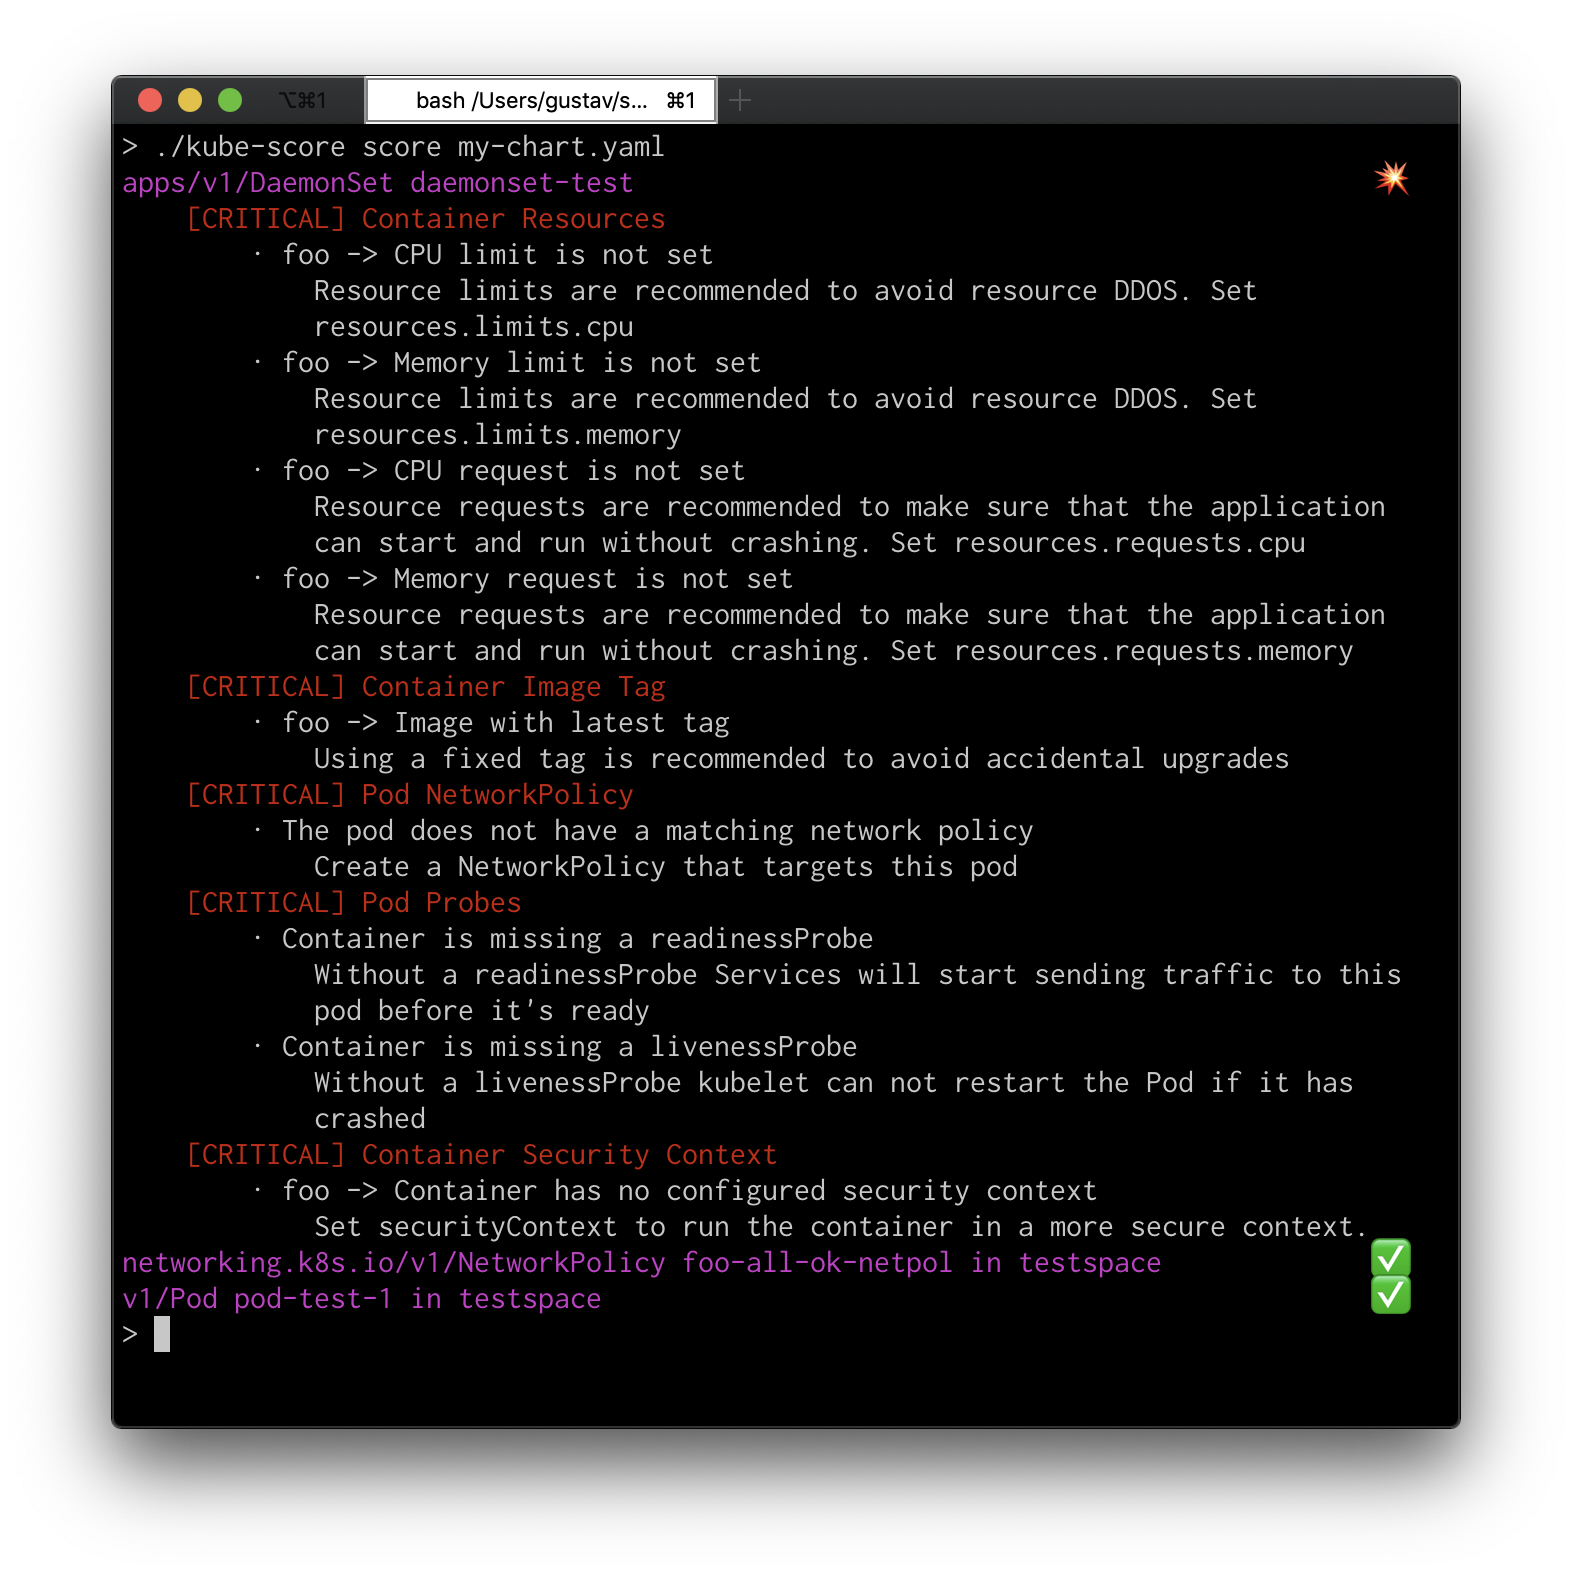 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…