self-hosted-ctf-platform

Self-hosted CTF: original web challenges + scoreboard, deployed with Docker Compose via GitLab CI and a GitOps agent. Flags derived from one CI…

Self-hosted CTF: original web challenges + scoreboard, deployed with Docker Compose via GitLab CI and a GitOps agent. Flags derived from one CI…

Scans WordPress plugins for missing-guard vulnerabilities using ripgrep signatures, Semgrep rules, attack-surface mapping, and an LLM review cascade…

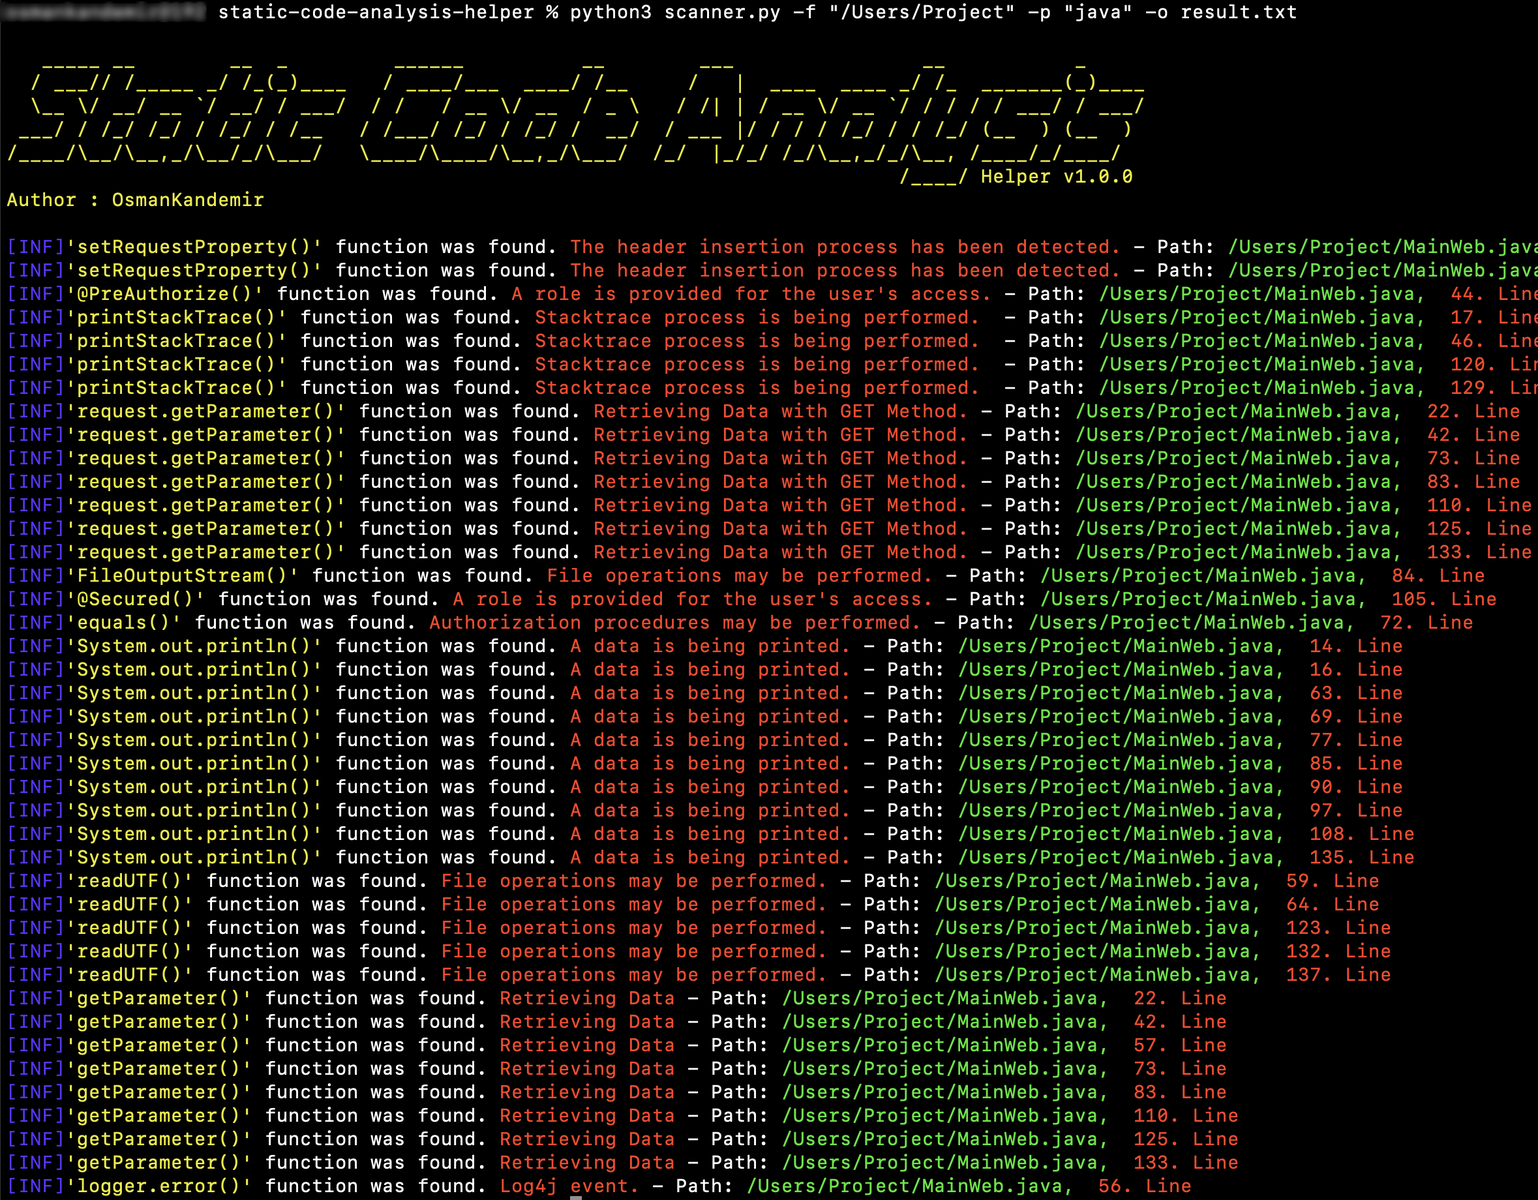
🔎 Static code analysis engine to find security issues in code.

MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…

Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…

RAM efficient terminal agent harness for coding, cybersecurity, and automation.

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…

Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.

AI-powered bug bounty hunting toolkit that works with or without subscription.

A security scanner for your LLM agentic workflows

Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…

Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…

Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment