Agentic-Bug-Hunter
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
ai-securityapi-security-testingcloud-security+8
4.8k
awarexone/agentic-bug-hunterAI-powered bug bounty hunting toolkit that works with or without subscription.
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
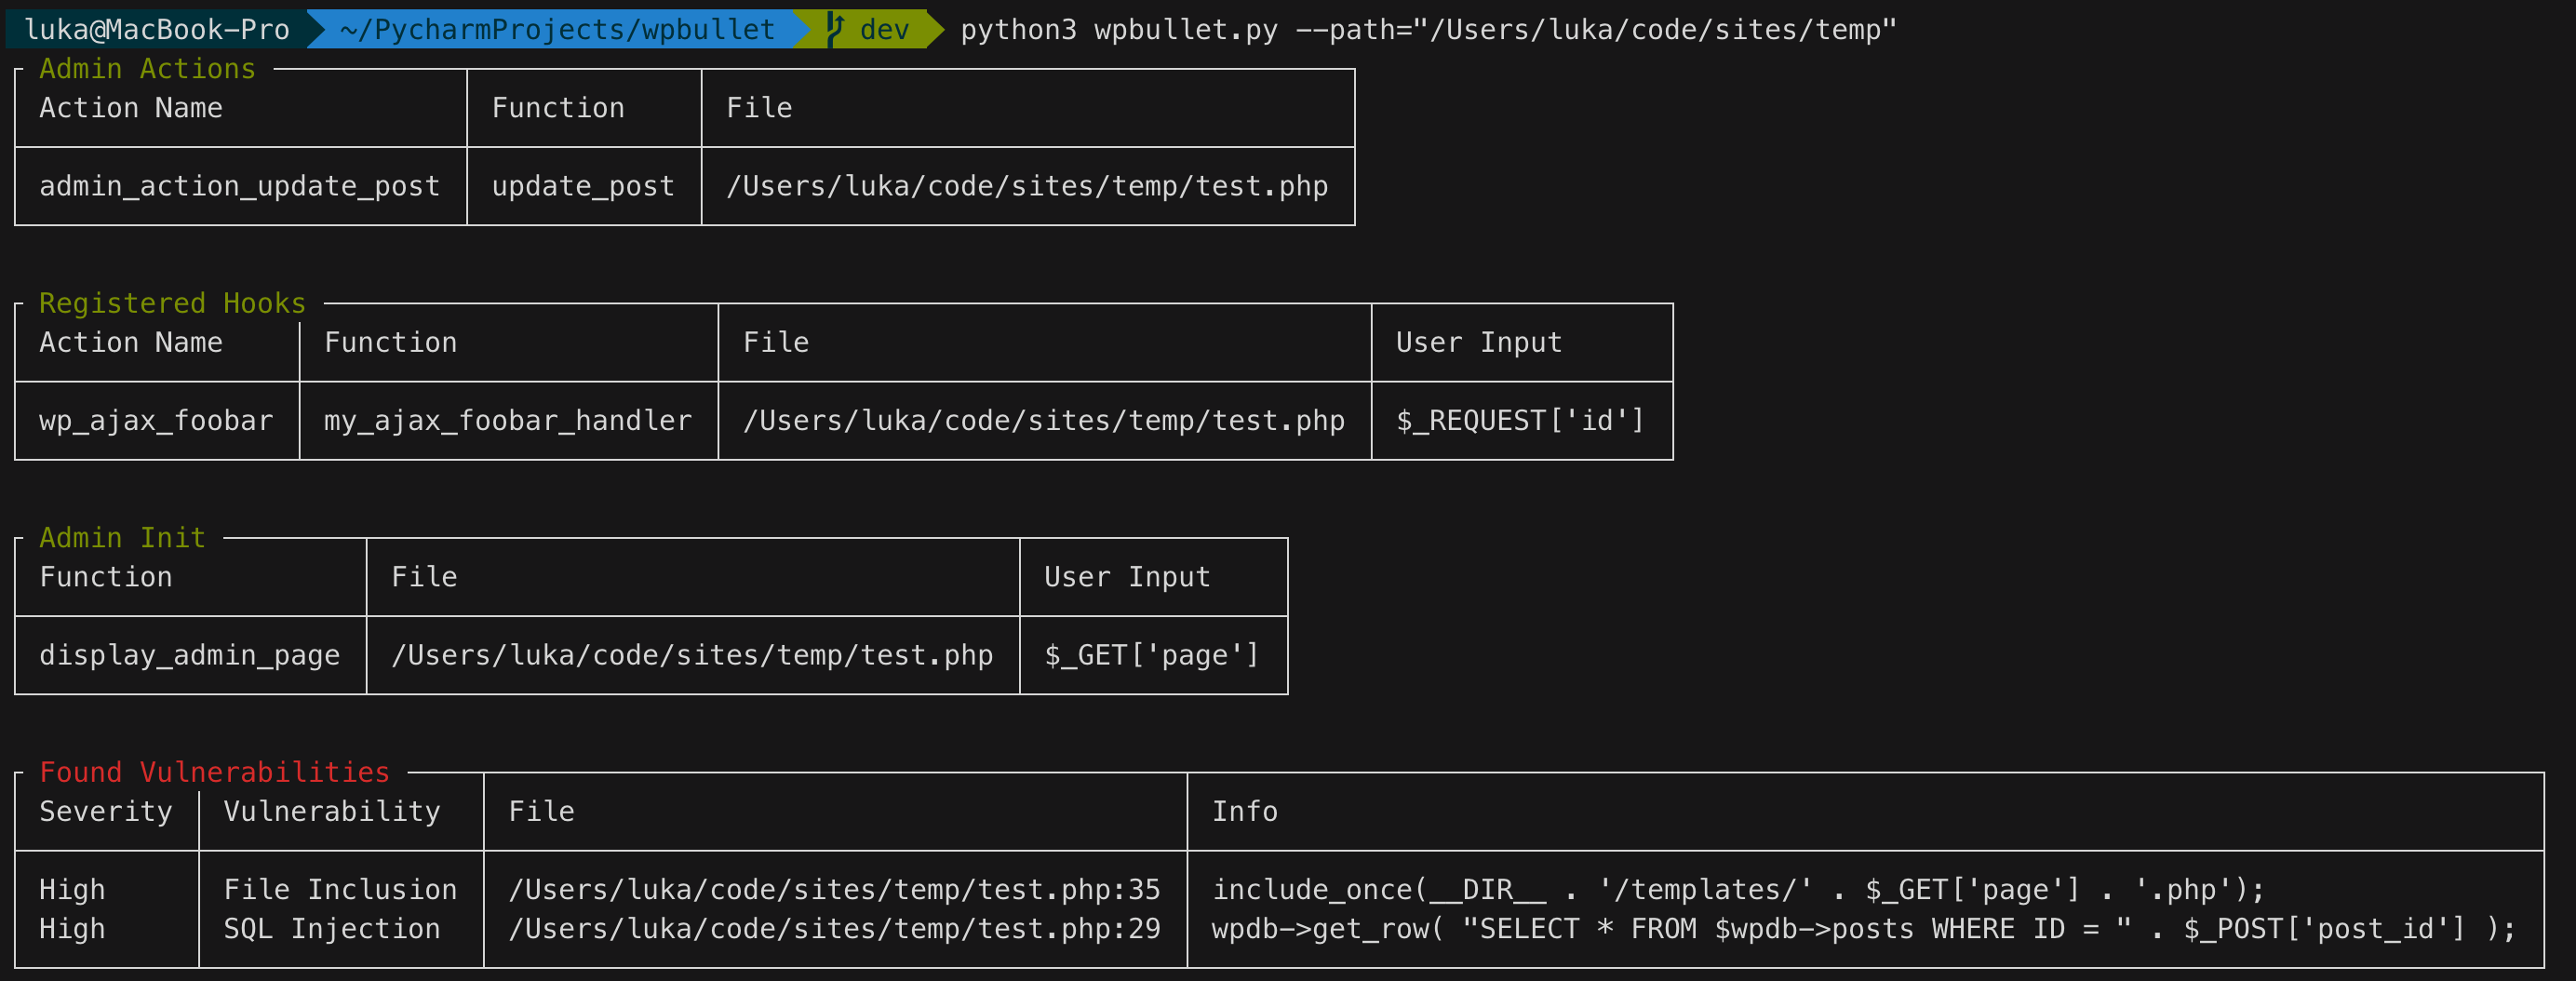 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
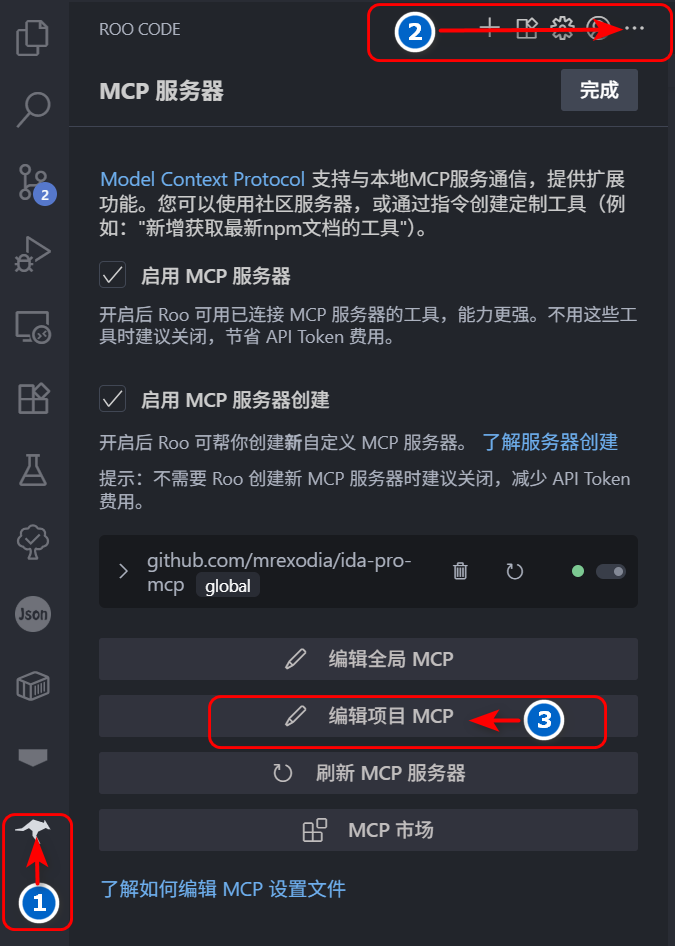 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 nccgroup/secretscrub
Processes SARIF output from static analysis tools to detect and redact hard-coded secrets in source code, creating a clean copy without the original…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 owasp/riskassessmentframework
The Secure Coding Framework
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 opsxcq/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution exploit and vulnerable container