
hardcodes
 s0md3v/hardcodes
find hardcoded strings from source code
code-analysisgeneral-purpose-utilitiessecret-detection+1
s0md3v/hardcodesfind hardcoded strings from source code
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
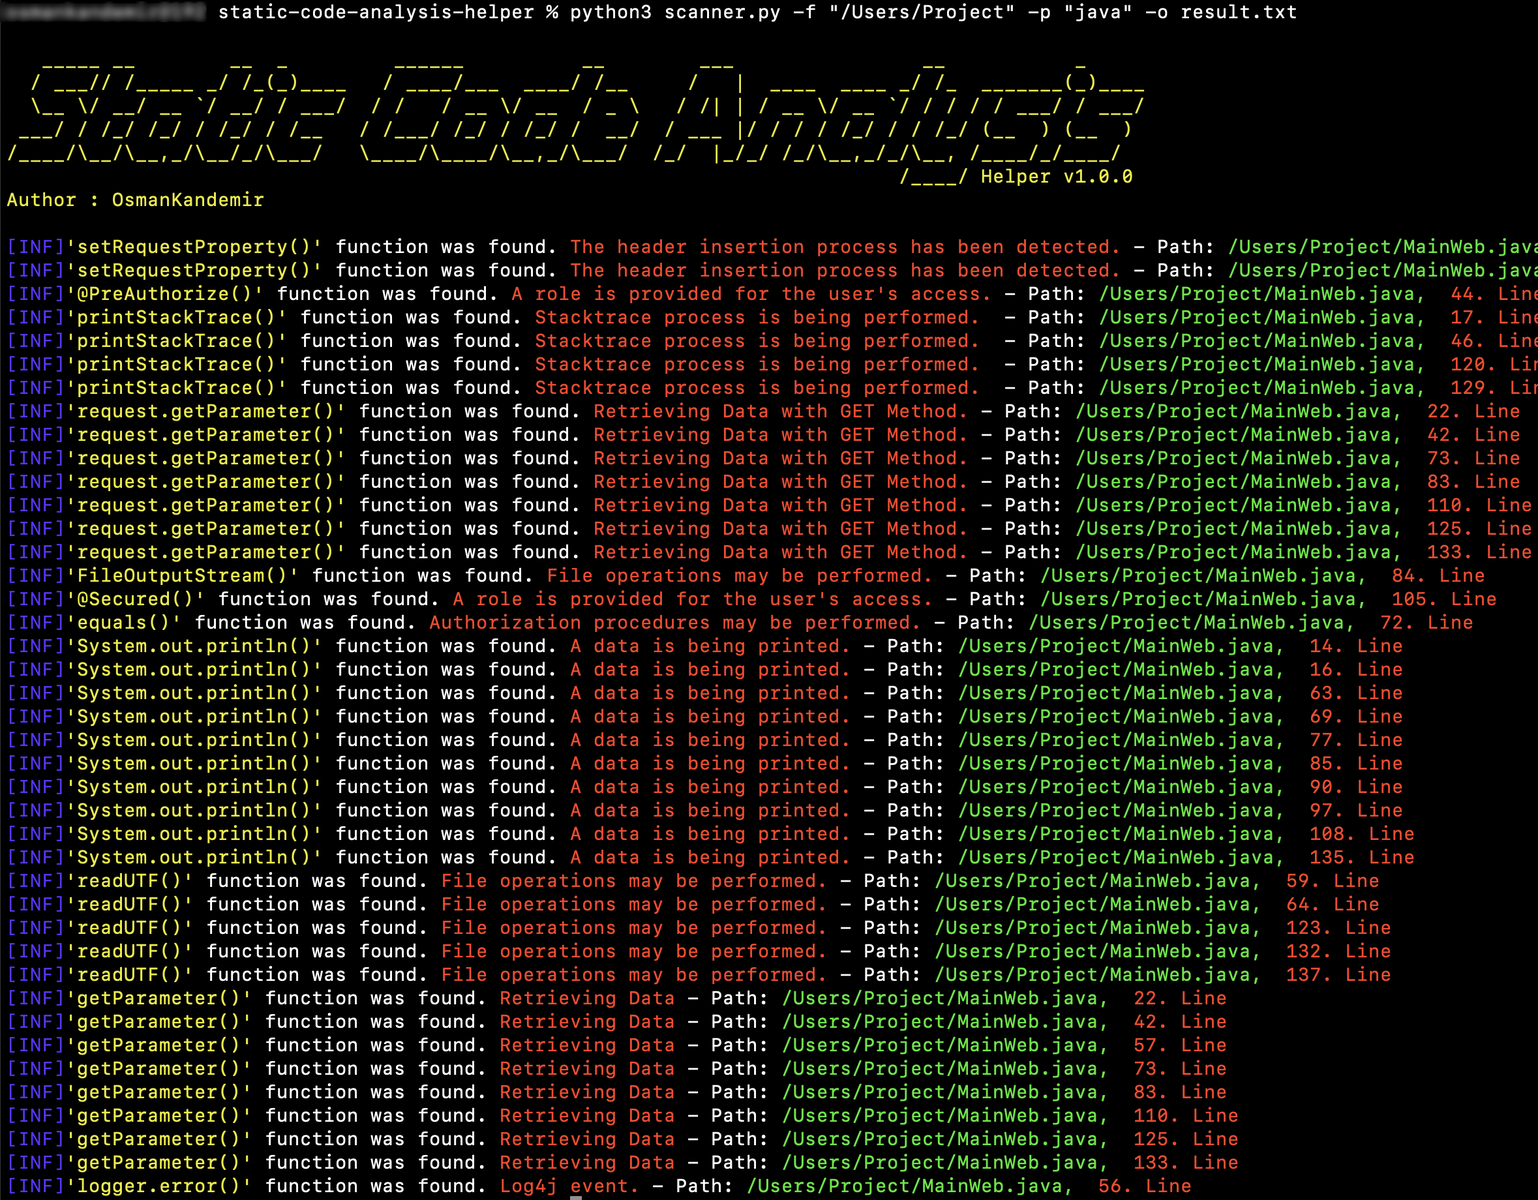 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 whitesquirrell/c0devari4nt
A variant analysis and visualisation tool that scans codebases for similar vulnerabilities
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
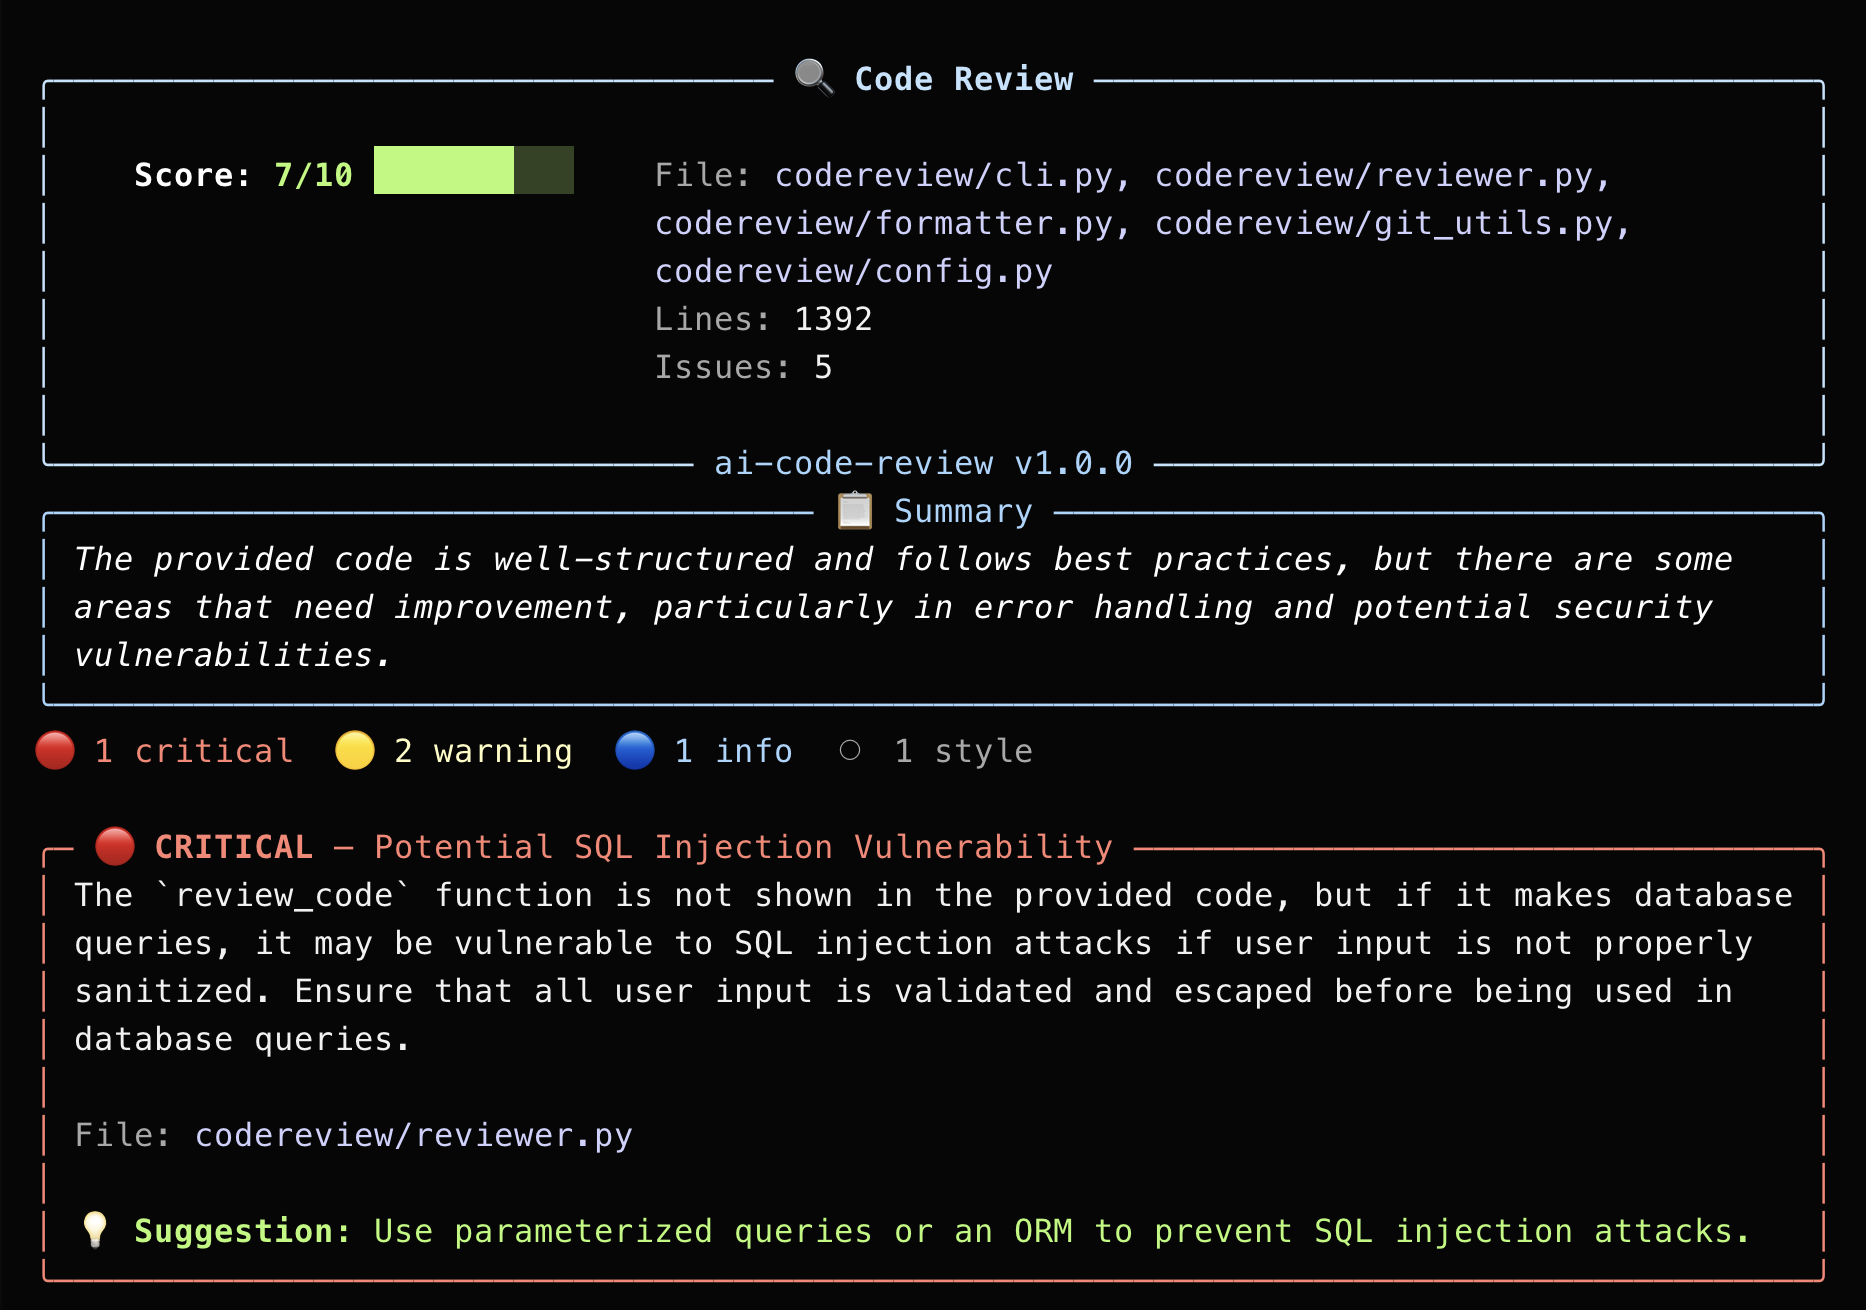 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 shoucheng3/codehaus-plexus__plexus-utils_cve-2022-4244_3-0-23
Java utility library with patched CVE-2022-4244 vulnerability, providing common helper classes for I/O, reflection, and CLI argument parsing in…
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
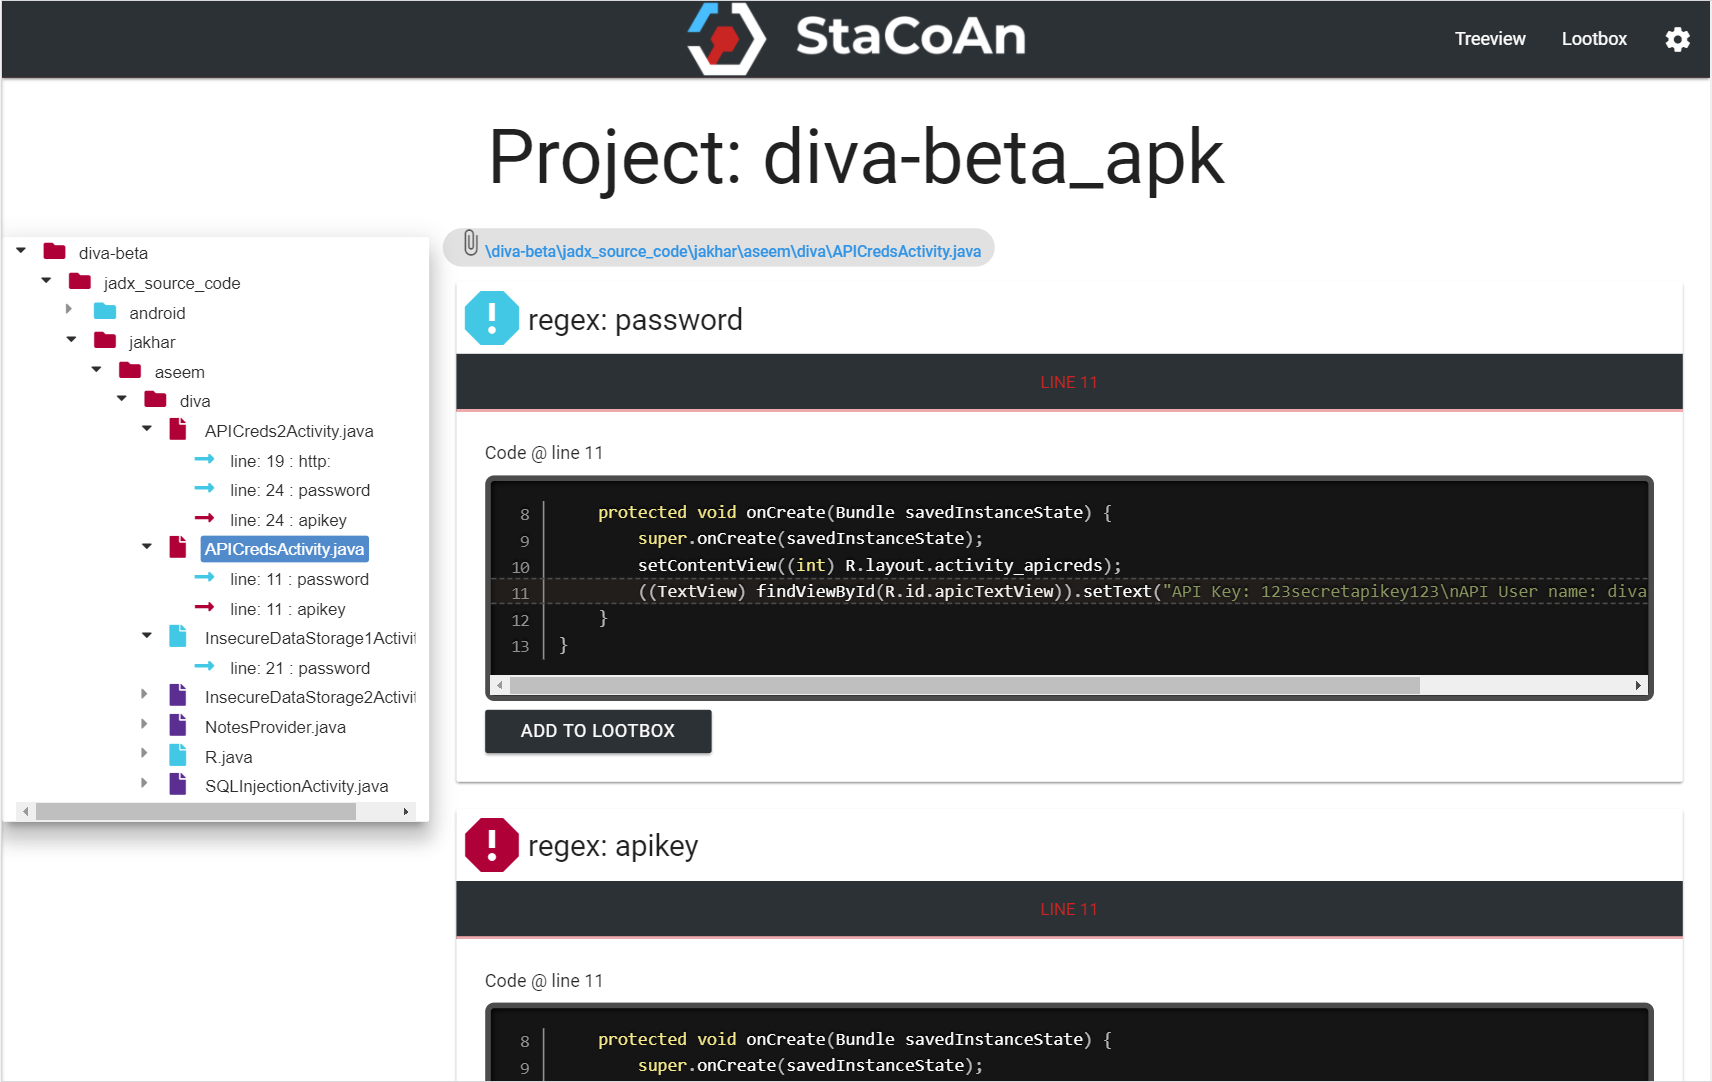 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
 epicosy/obridge
Java source code generator that creates calling classes for Oracle PL/SQL package procedures, supporting various parameter types and automatic type…
