
bandit
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
code-analysisstatic-code-analysisvulnerability-analysis
pycqa/banditBandit is a tool designed to find common security issues in Python code.
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
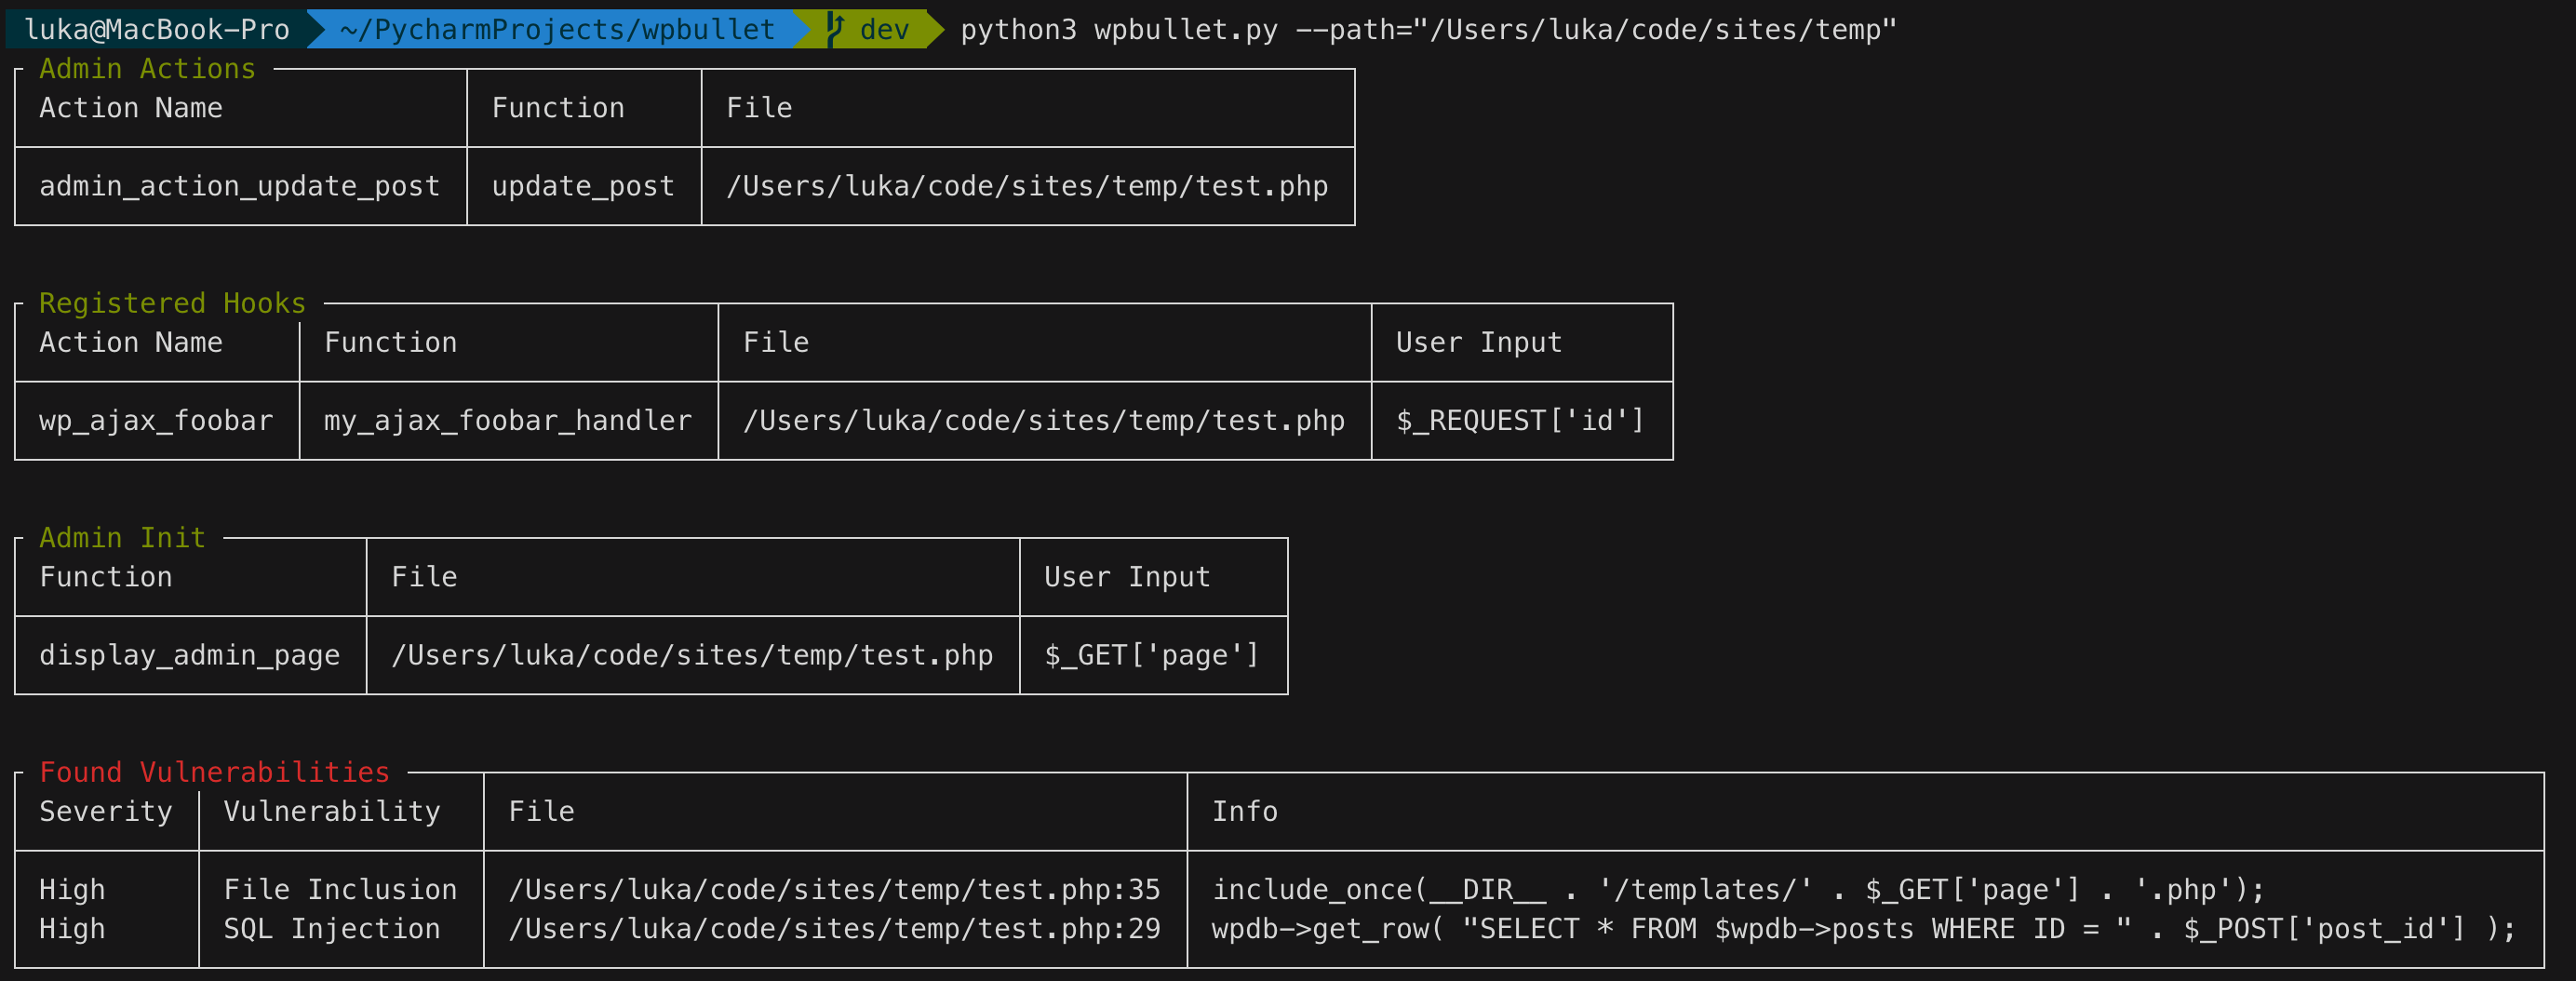 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
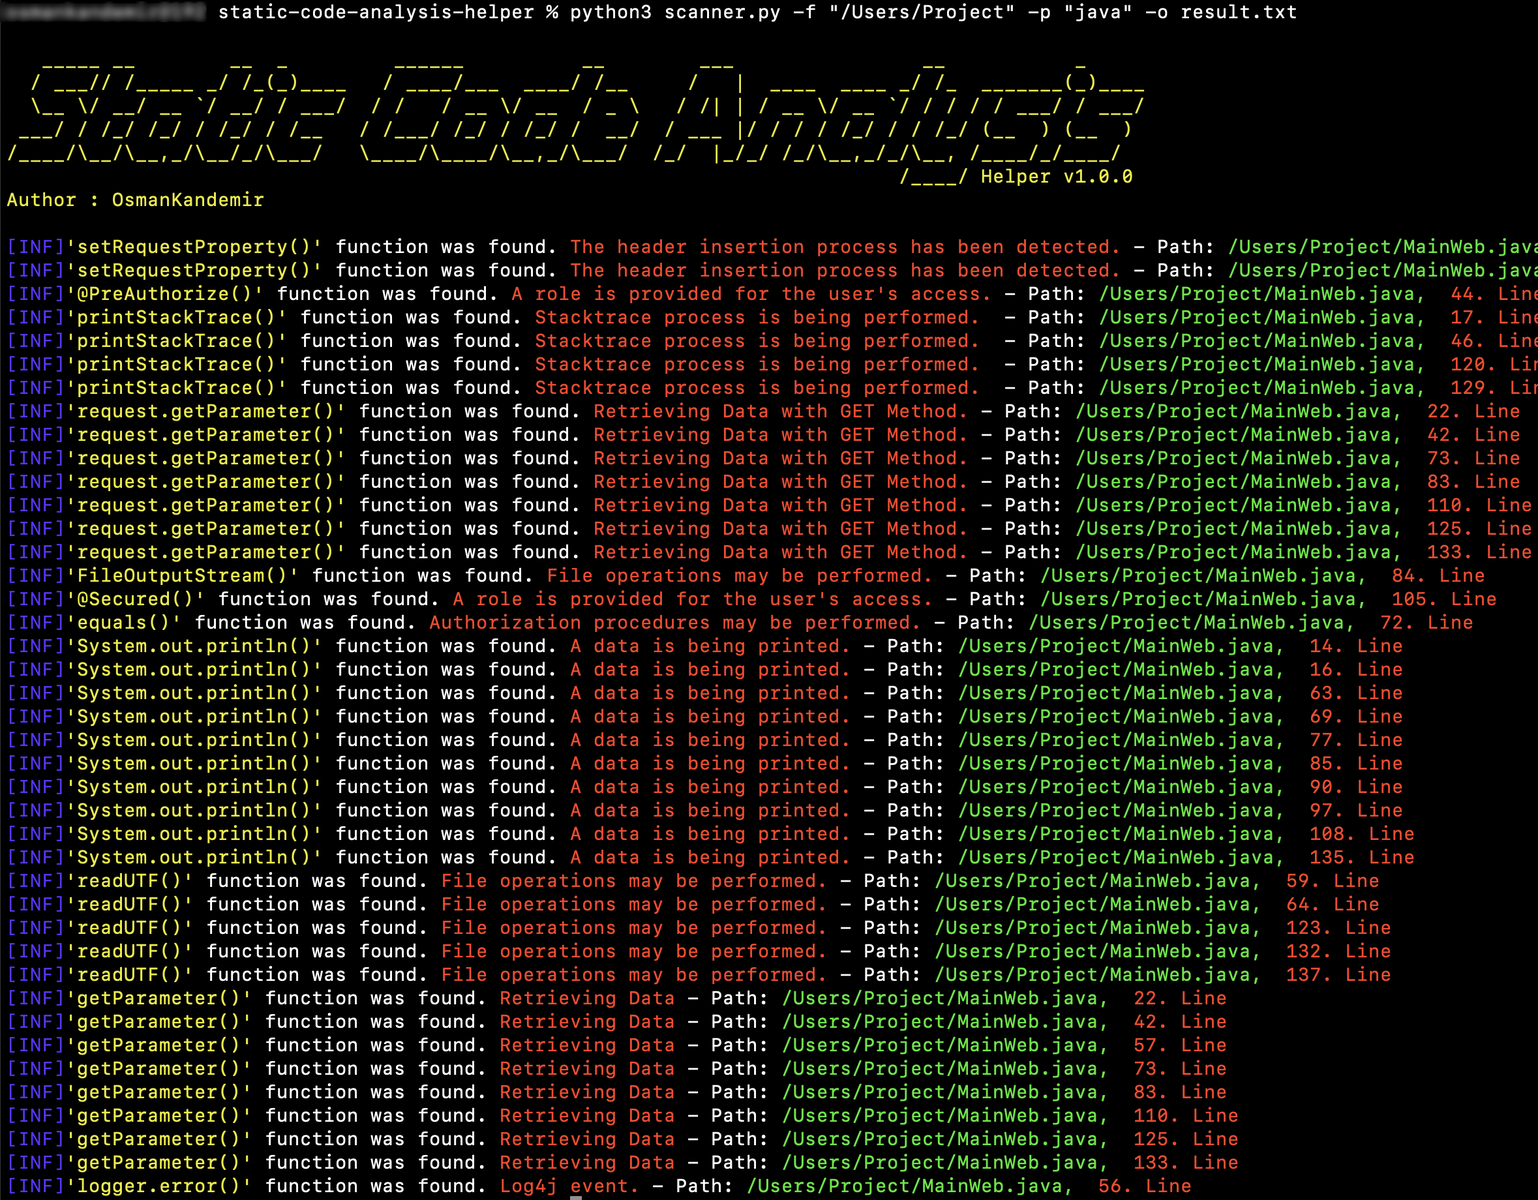 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
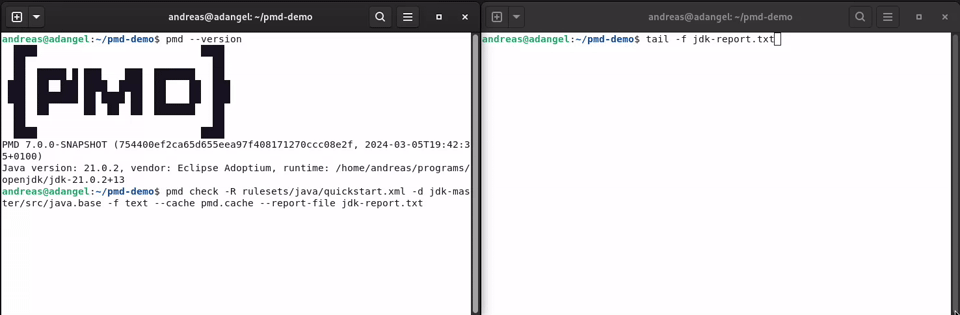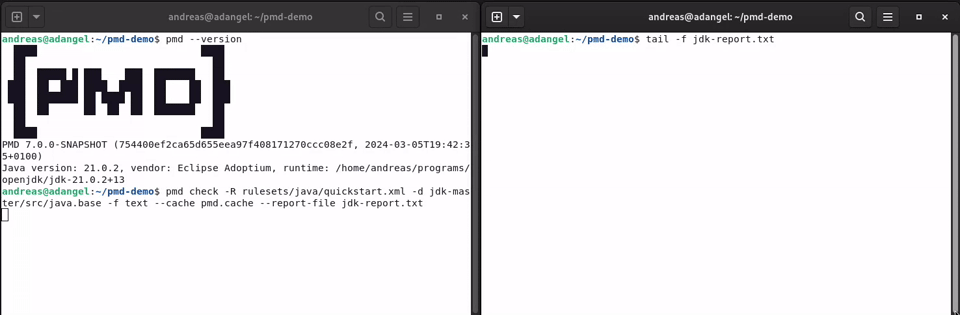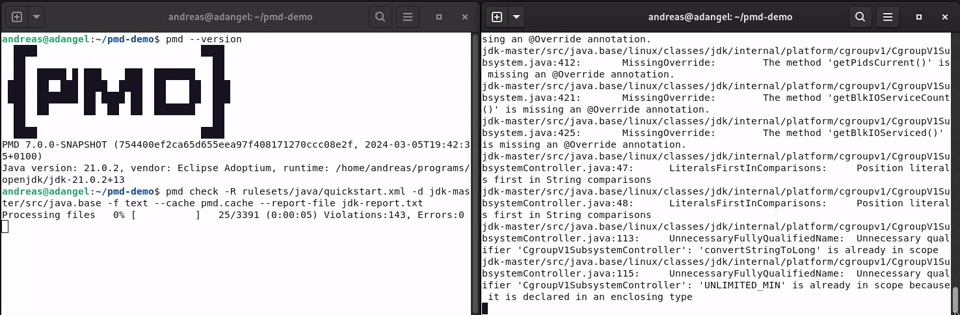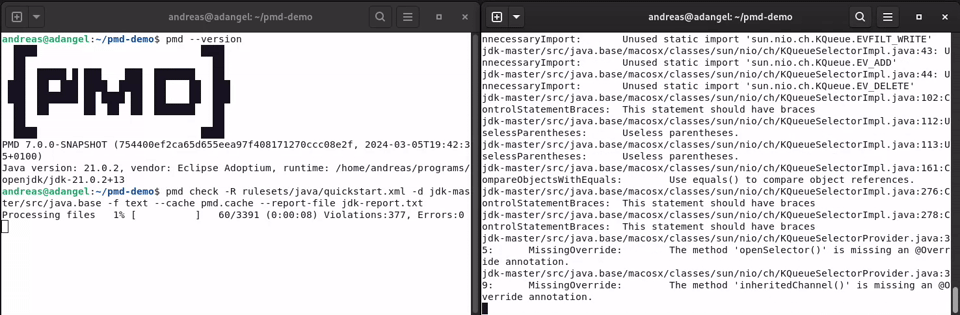 pmd/pmd
An extensible multilanguage static code analyzer.
 whitesquirrell/c0devari4nt
A variant analysis and visualisation tool that scans codebases for similar vulnerabilities
 nccgroup/secretscrub
Processes SARIF output from static analysis tools to detect and redact hard-coded secrets in source code, creating a clean copy without the original…