

bandit
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
code-analysisstatic-code-analysisvulnerability-analysis
pycqa/banditBandit is a tool designed to find common security issues in Python code.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…

 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
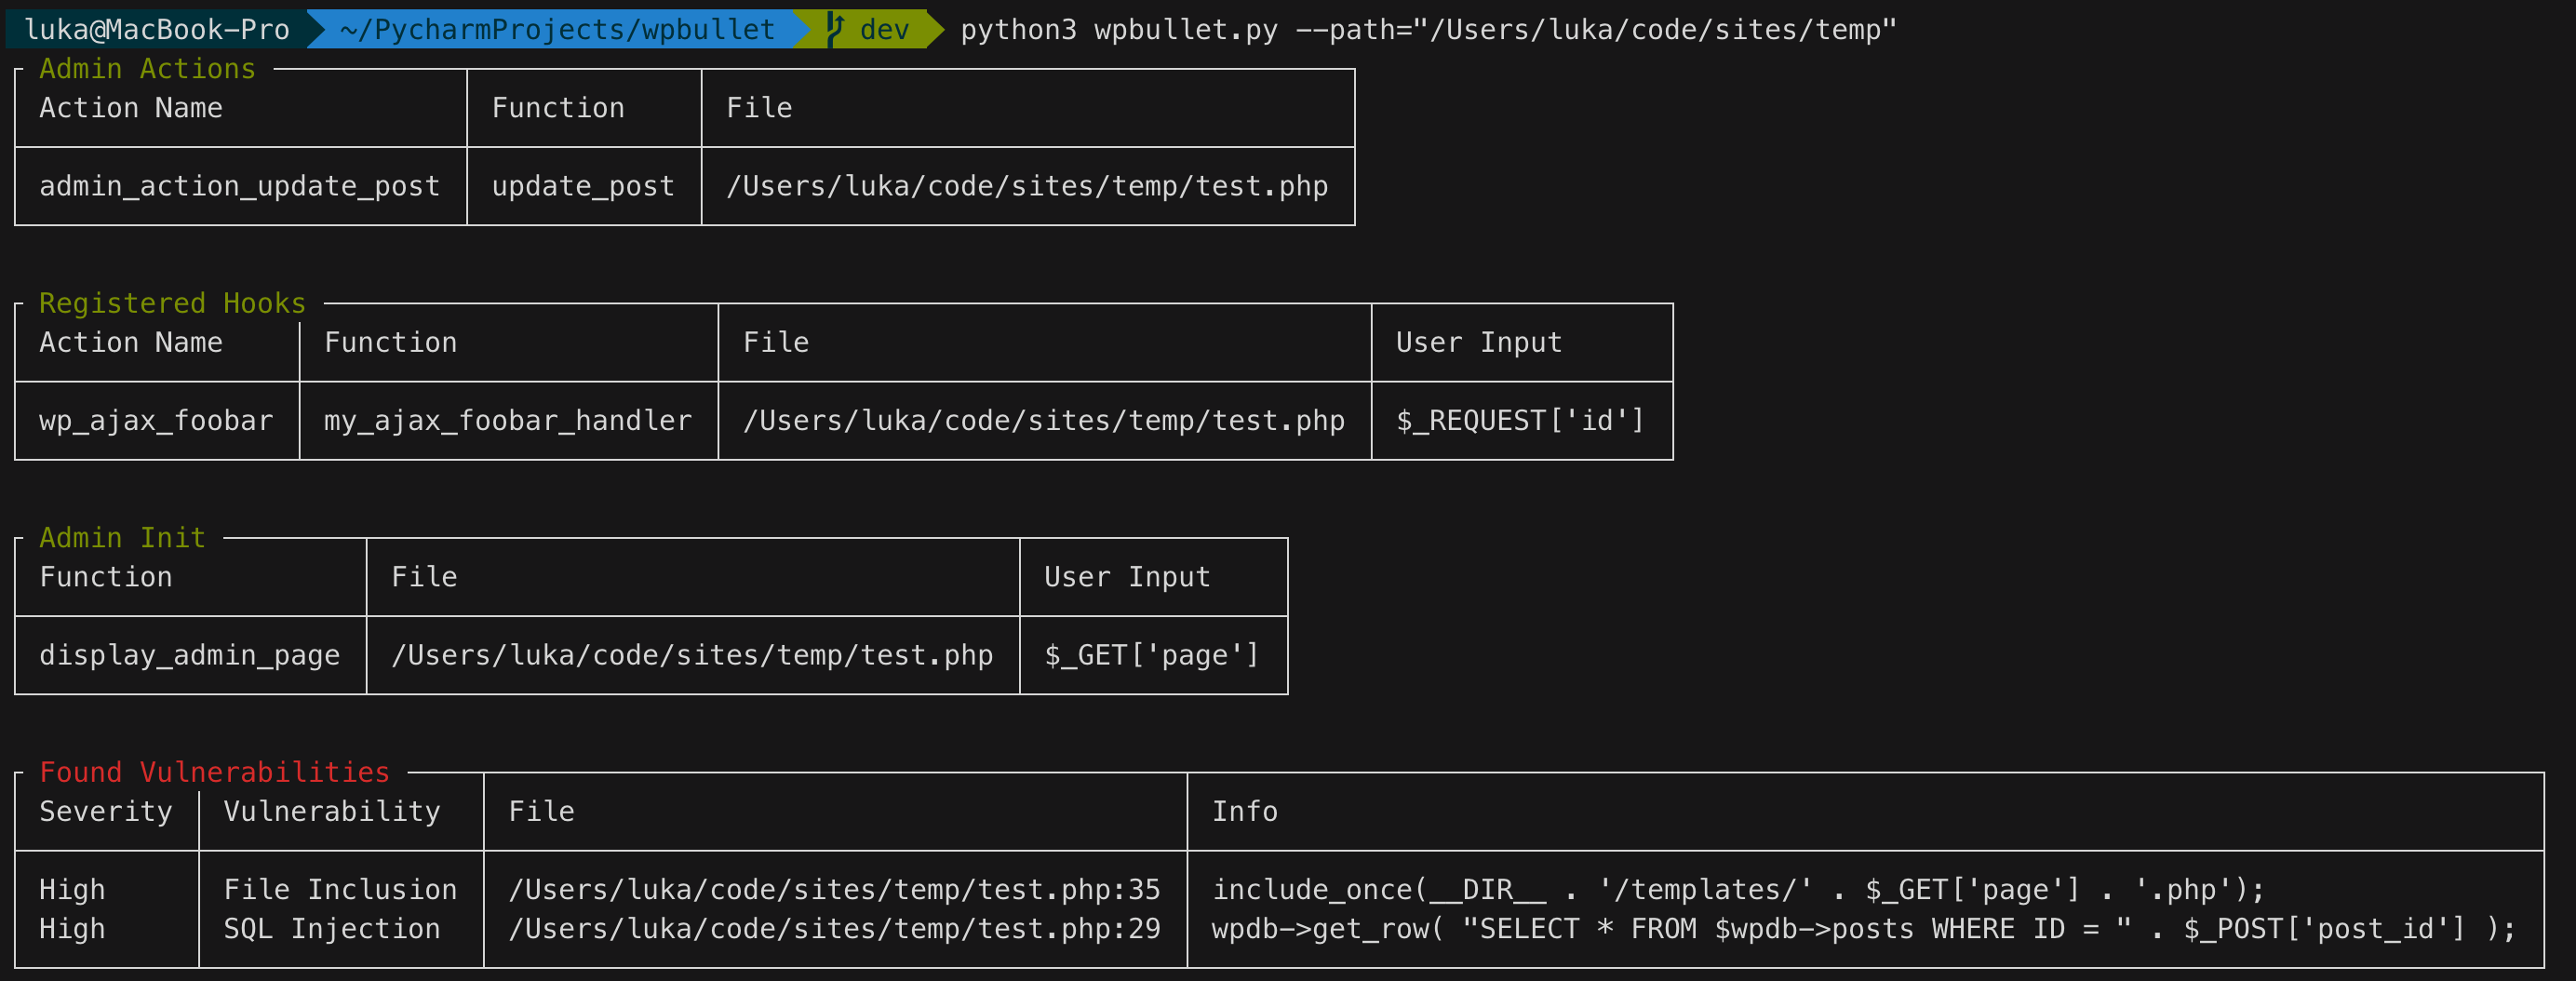 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
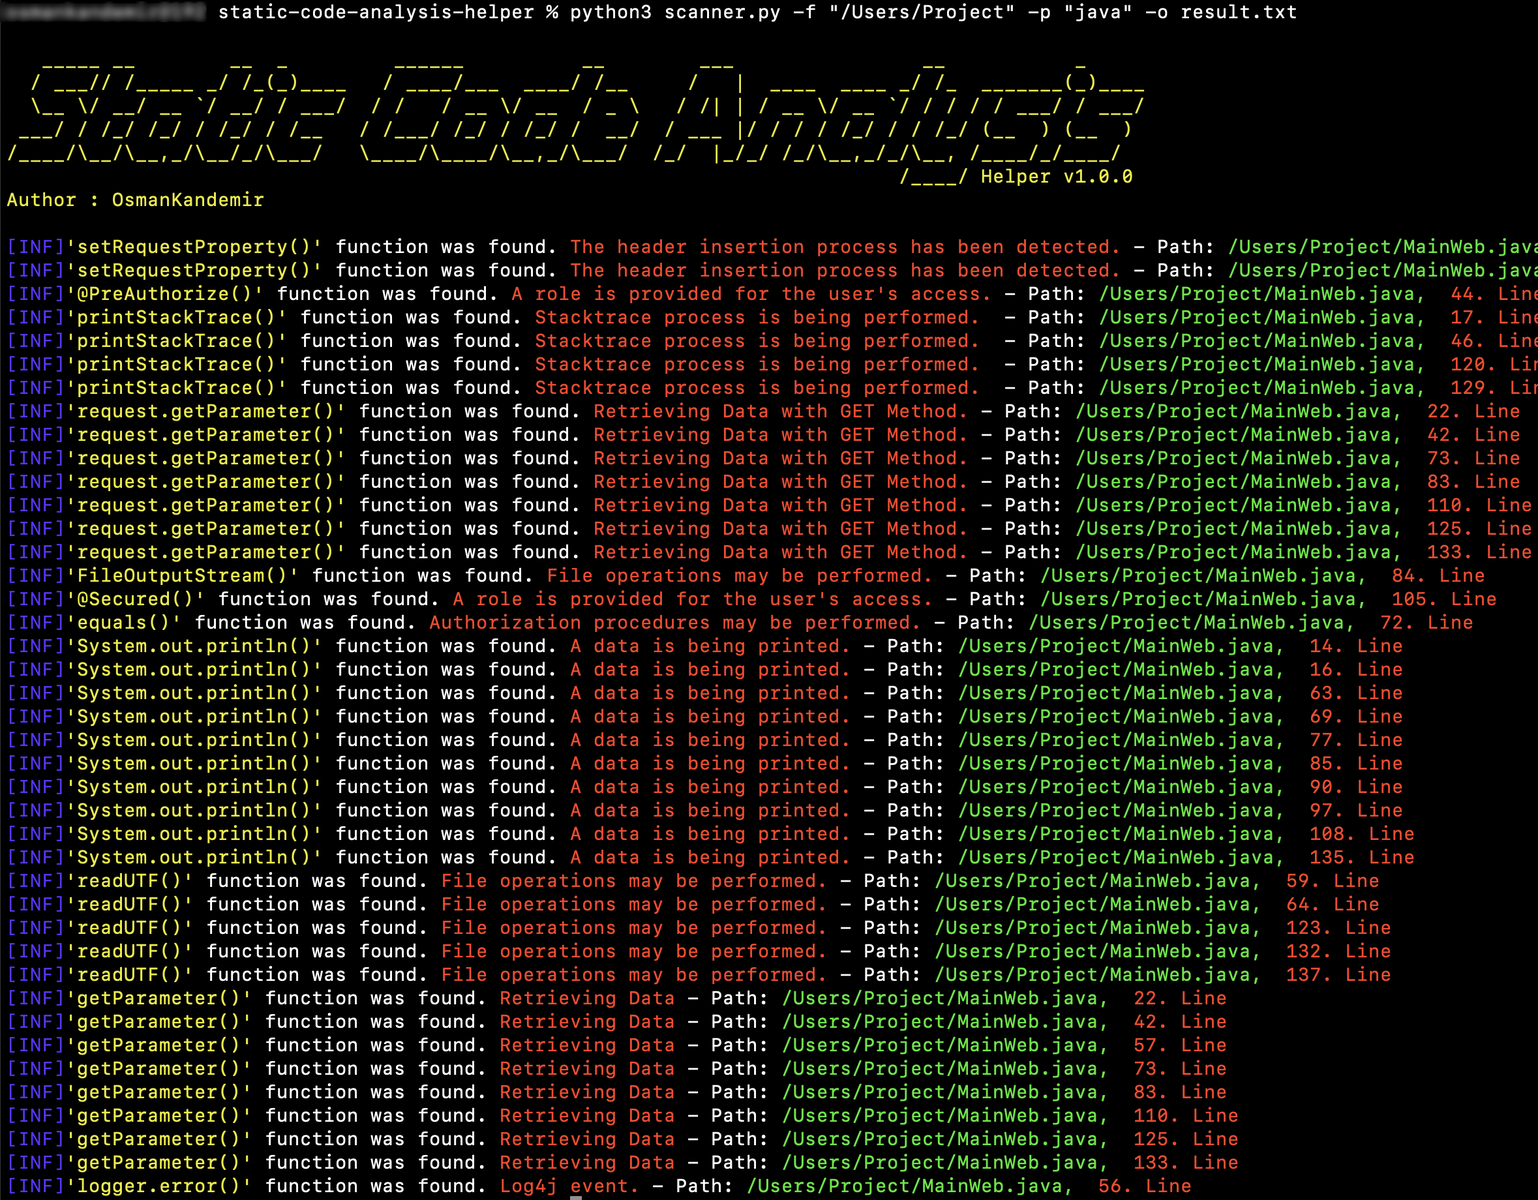 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
 whitesquirrell/c0devari4nt
A variant analysis and visualisation tool that scans codebases for similar vulnerabilities
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 owasp/riskassessmentframework
The Secure Coding Framework
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool