
CVE-2007-4559-lab
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
binary-exploitationcode-analysisctf+6
jithinodattu/cve-2007-4559-labSelf-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 ashishsecdev/mobsf_ai
AI powered security analysis extension for Mobile Security Framework MobSF
 quay/clair
Vulnerability Static Analysis for Containers
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
 mhaggis/package-inferno
A Public Package Scanner for The Community
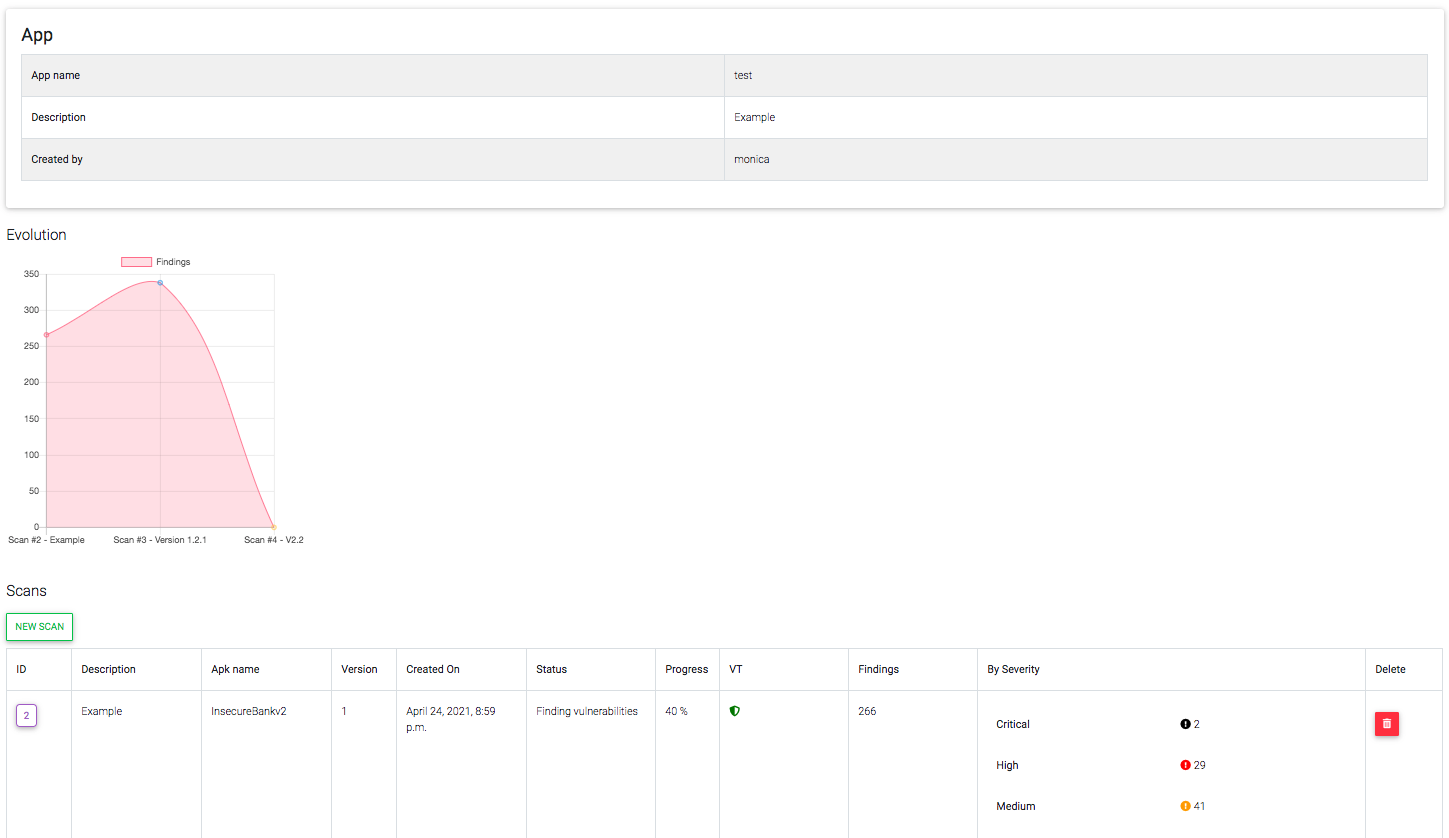 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
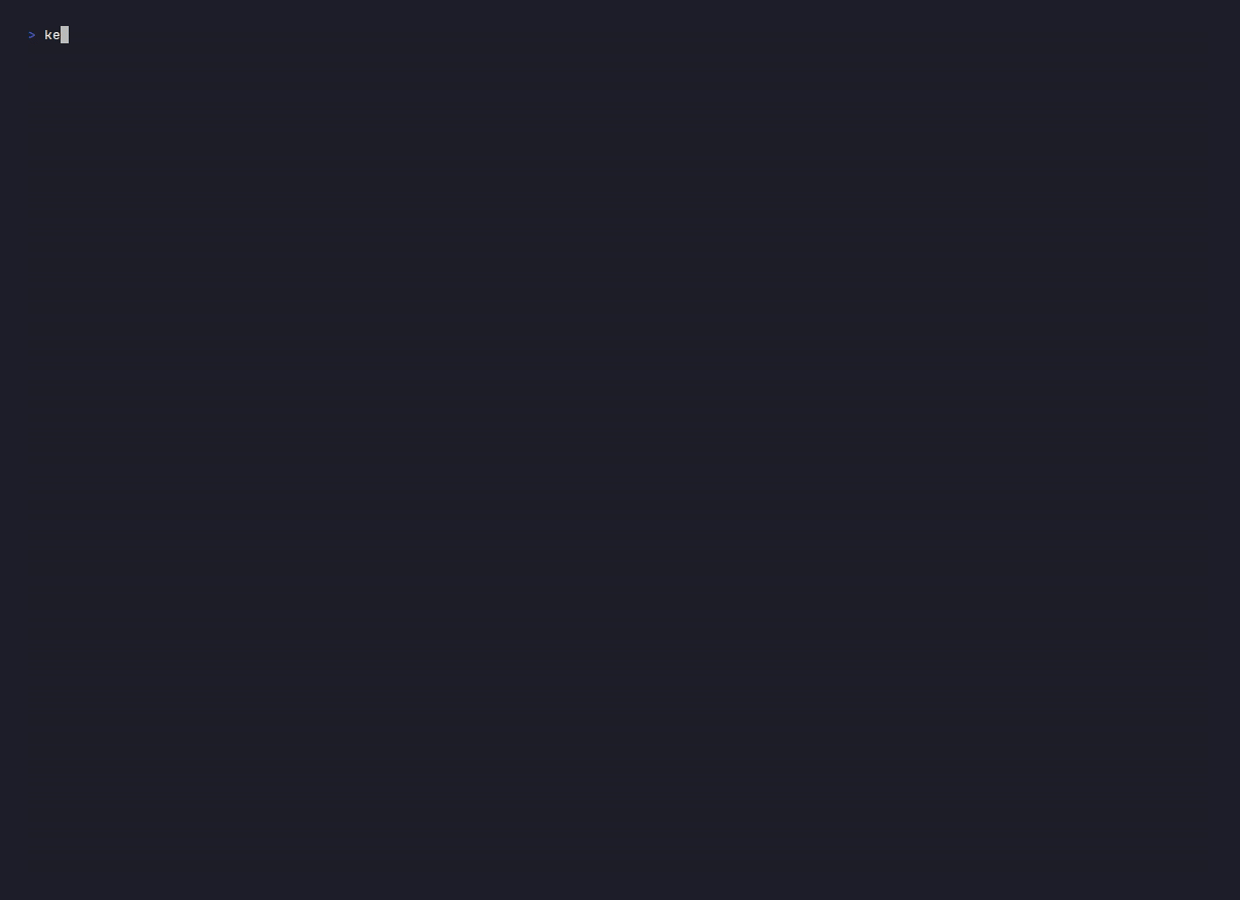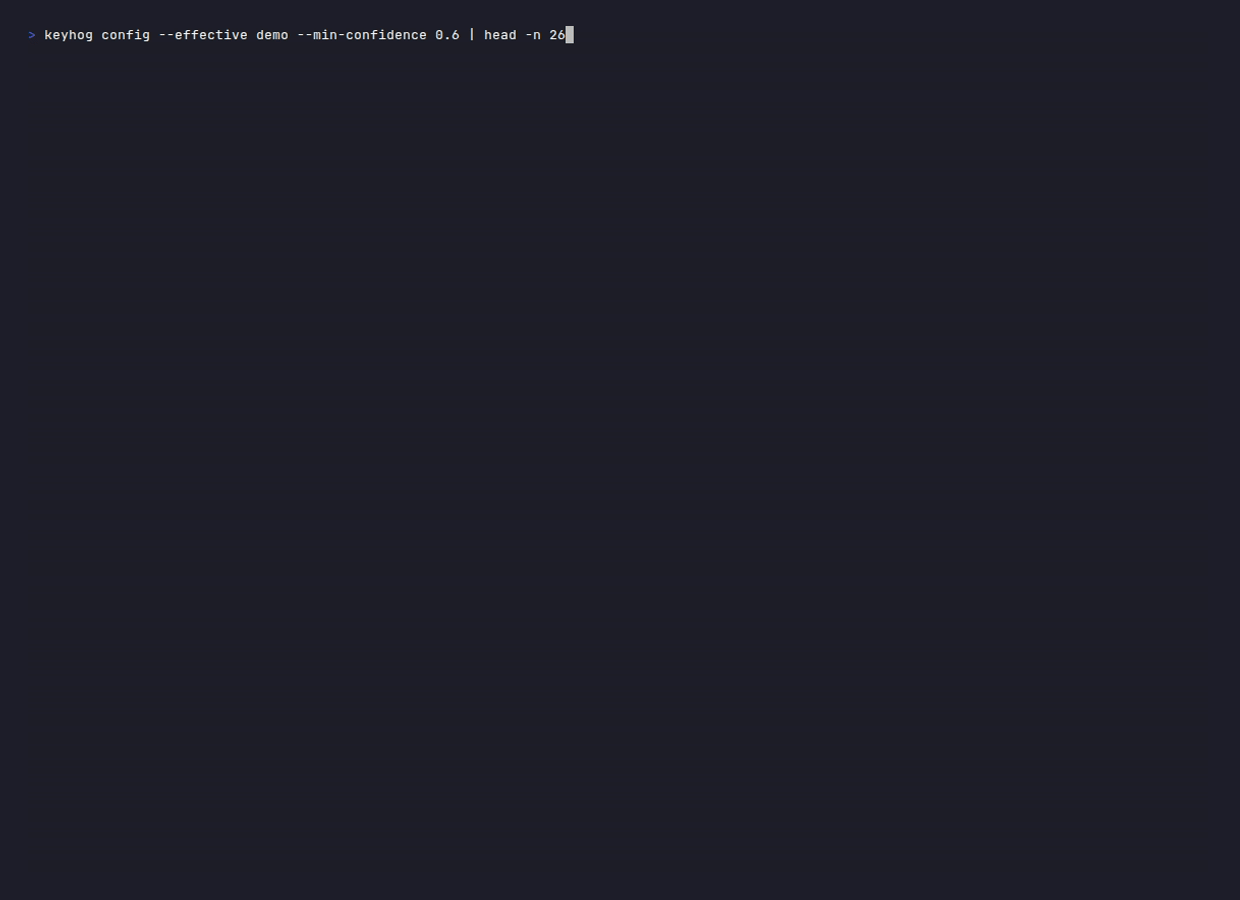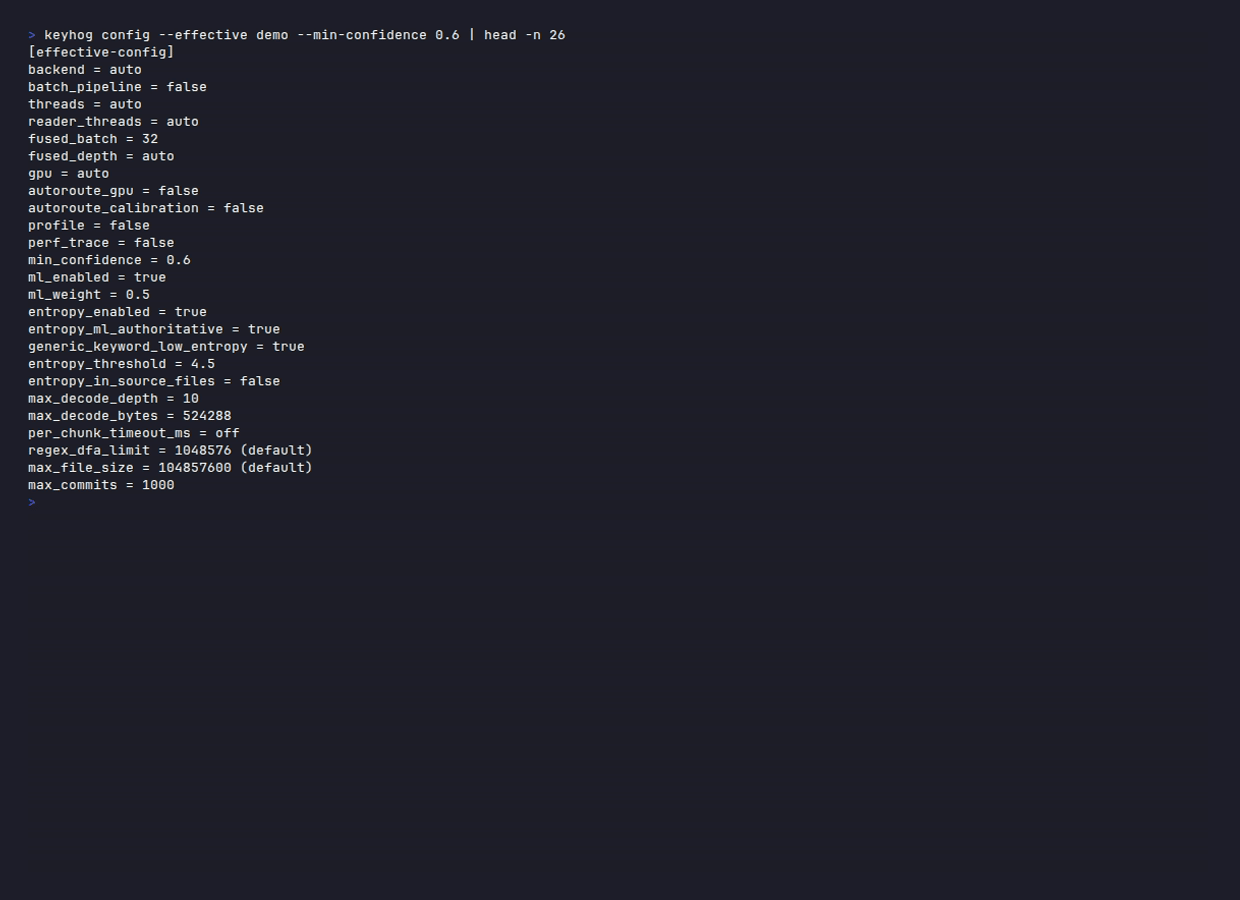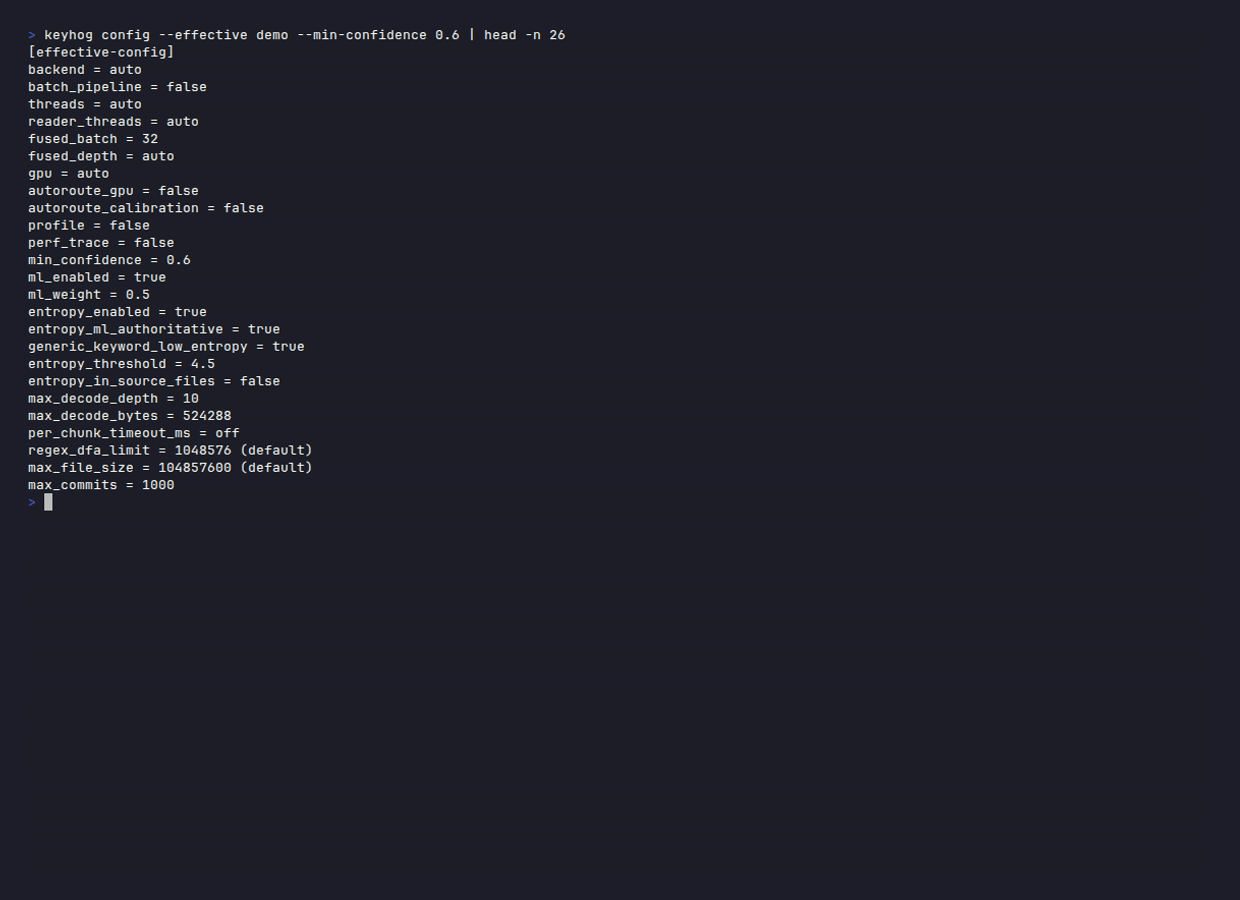 santhreal/keyhog
Open-source secret scanner in Rust
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.