
pharos
 cmu-sei/pharos
Automated static analysis tools for binary programs
binary-analysiseducationmalware-analysis+4
cmu-sei/pharosAutomated static analysis tools for binary programs
 cyberark/vulnhalla
Automated security analysis pipeline that runs CodeQL queries on GitHub repositories and uses LLMs to classify and filter true vulnerabilities from…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
 ejfkdev/dj
Extracts dynamically loaded JavaScript files by statically analyzing website HTML and JS, detecting webpack chunks, import() lazy loading, and source…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 spamscanner/spamscanner
Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…
 komimoe/arkari
Yet another llvm based obfuscator based on goron.
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 lilify-jp/squre
🛡️ Open-source binary protection toolkit for Windows PE. Nanomite, VM protection, anti-debug, and more.
 anerruption/logic.net
A free and open-source .NET obfuscator using dnlib.
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
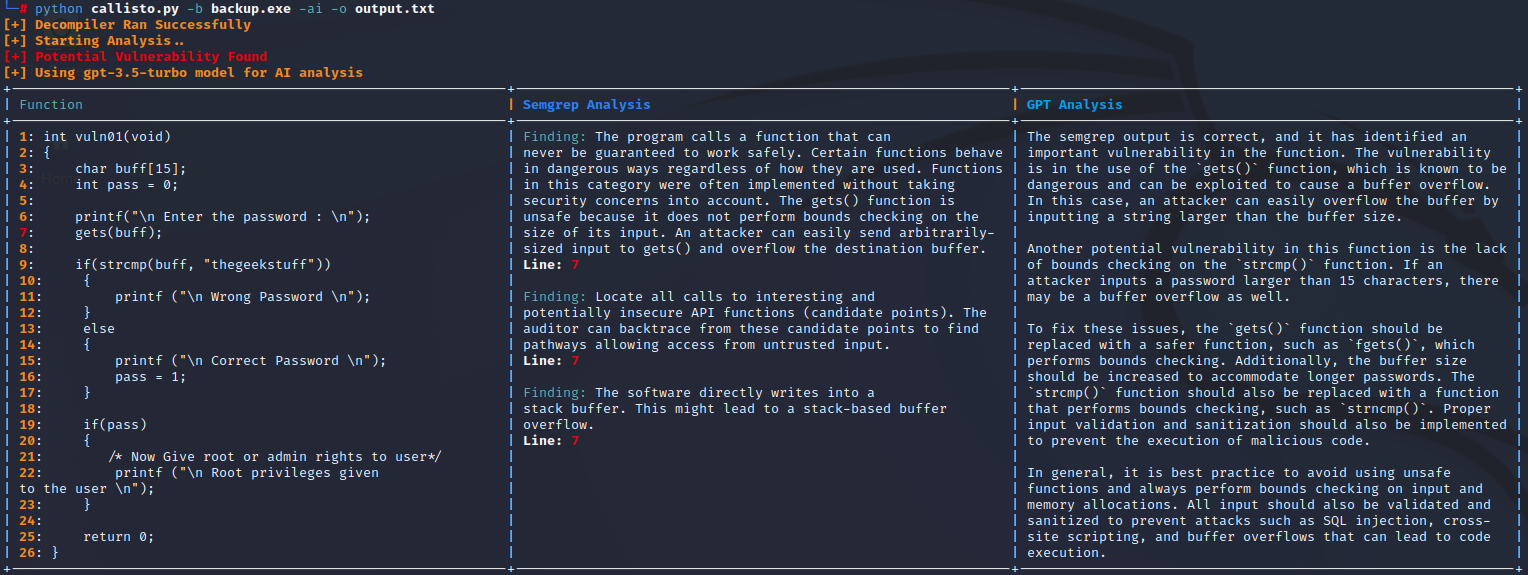 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis